

Scope: This assessment examines the transformation of cyber and operational risk across banking and financial infrastructure, with primary focus on the European Union and United Kingdom, specific lenses on Italy, France, Germany and the UK, and a five-year analytical horizon through 2031.
Executive Summary / BLUF
The central judgment is that banking cybersecurity has entered a structural transition in which the decisive contest is no longer simply between attackers attempting to penetrate networks and defenders attempting to exclude them, because artificial intelligence, compromised trusted identities, cloud concentration, software supply chains and increasingly automated financial processes are eroding the usefulness of the traditional distinction between an external cyberattack and an apparently legitimate action executed through authorised channels; consequently, the next generation of banking security must authenticate authority, intent, context and proportionality, rather than merely users, devices and network origins.
The regulatory evidence already reflects this change, because the European Central Bank has made operational resilience and robust ICT capabilities one of only two supervisory priorities for 2026-2028, while explicitly identifying recurring deficiencies in cybersecurity strategies, incident management and third-party risk frameworks and announcing cybersecurity inspections, threat-led penetration tests, cloud-dependency analysis and reviews of ICT change management. ECB Supervisory priorities 2026-28
The technological threat is simultaneously accelerating, because the European Banking Authority warned in its June 2026 risk assessment that increasingly capable frontier large-language models can improve the discovery and exploitation of software vulnerabilities, while the Bank of England concluded in July 2026 that frontier AI is beginning to alter the speed, scale and economics of cyber risk, potentially forcing institutions to discover, classify, test and remediate vulnerabilities at a tempo that existing human-intensive processes were not designed to sustain. EBA Risk Assessment Report – June 2026 Bank of England Financial Stability Report – July 2026
The strategic requirement is therefore not simply larger cybersecurity expenditure but a different allocation of capital, technology and governance: banks increasingly require AI-assisted vulnerability management, behavioural anomaly detection, continuous identity verification, independent verification of privileged or externally initiated requests, automated containment, rapid but controlled patch orchestration, immutable evidentiary logging, resilient recovery environments and much deeper visibility into software, cloud and data dependencies, while maintaining human authority over legally consequential decisions.
Europe has already moved cyber resilience from good practice into board-level regulatory responsibility through the Digital Operational Resilience Act, which requires financial entities to establish comprehensive ICT risk-management frameworks, allocate adequate resources, conduct resilience testing, manage ICT third-party risks and place ultimate responsibility for ICT risk with the management body. Regulation (EU) 2022/2554 — Digital Operational Resilience Act
The most dangerous systemic vulnerability is increasingly correlated failure rather than isolated institutional compromise, because banks share cloud providers, software libraries, telecommunications infrastructure, identity services, payment networks and cybersecurity suppliers; an AI-accelerated vulnerability affecting one common component can therefore propagate simultaneously through institutions whose individual control environments would previously have been considered independent.
The investment implication is correspondingly profound: cybersecurity expenditure must increasingly be treated as productive resilience capital comparable to liquidity management, redundancy and prudential infrastructure, rather than as a compliance overhead, because disruption to payments, trading, clearing, settlement, customer authentication or critical third parties can transmit an initially technological incident into liquidity stress, market dysfunction, reputational damage and ultimately financial-stability risk, a connection now explicitly recognised by both European and British authorities. HM Treasury — The Value of Resilience: Cyber Resilience in Financial Services
When the Attacker Does Not Breach the Bank: Revolut and the New Cybersecurity Failure
The Revolut incident disclosed on 15 September 2026 exposes a weakness that conventional bank cybersecurity is poorly designed to confront: criminals reportedly did not penetrate the fintech’s core infrastructure but instead used an email address associated with an authentic government domain to induce the company to release sensitive customer information. Around 700 customers were contacted after the initial investigation, while Revolut said its systems and customer funds were unaffected. The contradiction is the important part: technical infrastructure can remain uncompromised while institutional trust is successfully weaponised. For banks, this moves cybersecurity beyond malware, network intrusion and credential theft into the machinery through which lawful authority is recognised, validated and acted upon. The next investment cycle will therefore be judged not simply by how well institutions stop outsiders entering their systems, but by whether they can prevent trusted channels from being turned into instruments of disclosure.
The breach happened inside a legitimate process
Revolut described the event as a “sophisticated external impersonation scam” involving an unauthorised party using an email address associated with a genuine government agency domain, after which the company blocked the address and notified the relevant government agency, law-enforcement bodies, data-protection authorities and financial regulators. The bank has not publicly identified the government agency involved, nor established whether the underlying account had been externally compromised, misused by an authorised individual or exploited through another mechanism. That uncertainty matters because the failure occurred within a process that financial institutions are legally required to maintain: police forces, courts, regulators, tax authorities and other public bodies routinely request customer information through warrants, subpoenas, statutory notices or emergency powers. The attack therefore did not circumvent the process; it exploited the trust built into it.
That distinction creates a much harder security problem than ordinary spoofing. Technologies including SPF, DKIM and DMARC can establish whether an email was sent through authorised infrastructure, yet they cannot determine whether the person controlling a legitimate government mailbox is legally entitled to demand customer records. A compromised official account can therefore pass the technical tests an institution has spent years strengthening while still carrying a fraudulent instruction. The security perimeter is no longer only the bank’s network; it includes every trusted public authority, privileged mailbox, legal workflow and disclosure channel capable of triggering access to protected information.
Seven hundred customers reveal a much larger control problem
The number publicly identified is limited relative to Revolut’s scale: the company says it serves more than 80 million customers globally, including approximately 13 million in the United Kingdom, while around 700 individuals were contacted following the initial investigation. Numerically, the incident is small; structurally, it is not. The records reportedly disclosed depending on the customer included names, dates of birth, postal and email addresses, telephone numbers, account statements, IBANs, withdrawal records, verification photographs, passports, driving licences and detailed transaction histories, while some customers were warned that information concerning their Bitcoin activity might also have been released. The concentration of identity, financial and behavioural information held by a modern financial institution means that a successful request for records can deliver an attacker far more than access to a single account.
The economic value of such information does not disappear when passwords are reset or payment cards replaced. Passports, addresses, dates of birth, verification photographs and historical transaction records remain useful for impersonation long after the original incident, while precise knowledge of balances, withdrawals, transfers or cryptocurrency activity can make subsequent fraud materially more credible. The dossier records that former Mt. Gox chief executive Mark Karpelès said he was among those notified and that the notice he shared indicated potential disclosure of account statements, IBANs, withdrawal records and full transaction histories including Bitcoin activity. A breach of this kind therefore creates a durable secondary attack surface around the customer even when the bank’s core infrastructure remains intact.
Banks must stop treating official identity as sufficient authority
The central control failure raised by the incident is the assumption that authenticity of origin establishes legitimacy of instruction. It does not. The dossier states that an email sent from a genuine government domain can demonstrate where the communication originated while failing to prove that the sender is authorised, that an attached legal instrument is genuine or that the scope of the requested disclosure is proportionate to the underlying investigation. High-risk requests therefore require independent verification through a second channel using contact details obtained from an authoritative directory rather than from the incoming communication itself. Calling a telephone number supplied inside the suspicious request merely gives the attacker control of both sides of the verification process.
This has direct investment consequences. Banks need secure government-request portals where possible, pre-registered institutional contacts, cryptographic signatures, strict approval workflows, legal review, anomaly detection and explicit escalation when a request seeks unusually broad or sensitive information. They also need controls capable of asking whether the named official has submitted similar requests before, whether the jurisdiction is consistent with the customer or investigation, and whether the volume of information requested matches the stated purpose. These are not conventional perimeter controls; they are decision-integrity controls, designed to prevent an authentic channel from authorising an illegitimate outcome.
The attack method is established, not exceptional
The Revolut case sits inside a known pattern rather than representing an isolated innovation. In November 2024, the FBI warned of increased criminal discussion surrounding fraudulent emergency data requests, including the use of compromised government and police email accounts, stolen legal documents, official signatures and templates designed to make requests appear legitimate. Criminals were also discussing the purchase and sale of access to official government email accounts in the United States and other jurisdictions, turning trusted institutional identity into a tradable criminal commodity.
The mechanism had already produced consequences by 2022, when similar schemes reportedly led companies including Apple and Meta to disclose user information in response to forged emergency requests. Emergency procedures are particularly attractive because they are designed for circumstances involving imminent threats to life or serious physical harm, where the delay associated with an ordinary warrant or subpoena could be dangerous. Criminals can exploit that architecture by fabricating urgency around kidnapping, suicide threats, missing children or terrorism, pressuring employees to release records before every verification step has been completed. The challenge for banks is therefore institutional rather than simply technical: urgency must activate a specialised verification path, not suspend verification altogether.
Regulation will test the process, not merely the intrusion
The UK regulatory dimension is equally important because the Information Commissioner’s Office has reportedly opened an investigation after Revolut notified the privacy regulator, and the central issue is likely to concern the safeguards used to validate the requests rather than whether malware entered the bank’s network. Under the UK GDPR framework described in the dossier, disclosure of personal information to an unauthorised recipient constitutes a personal-data breach even when an employee deliberately sent the information after mistakenly believing that the recipient was entitled to receive it. Where a breach is likely to create a risk to individuals’ rights and freedoms, the ICO reporting framework requires notification without undue delay and, where feasible, within 72 hours of awareness.
The regulatory questions therefore reach directly into organisational design: how was the government representative authenticated, was the supporting legal authority independently verified, did legal or supervisory staff review the request, did the sensitivity of the requested information trigger additional approval, and was data minimisation applied so that only legally necessary information was released? The existence of the incident does not itself establish a violation of data-protection law, and the dossier explicitly notes that Revolut will have the opportunity to explain both its procedures and the sophistication of the deception, but the investigation will test whether the institution’s controls were proportionate to the sensitivity and volume of the information involved.
AI makes institutional impersonation cheaper and more scalable
The documented attack did not require compromise of Revolut’s core banking systems, and that is precisely why the strategic implications extend beyond this case. Once criminal groups possess legitimate government accounts, stolen documents, recognised signatures and knowledge of official disclosure procedures, artificial intelligence can reduce the cost of preparing persuasive requests, generating supporting correspondence, maintaining coherent identities and reproducing the language and administrative patterns expected by the recipient organisation. The dossier’s 2024 FBI warning already described a criminal market in official inboxes, templates and guidance; AI does not create that market, but it can industrialise the workflows operating inside it.
For banks, this changes the economics of defence. Security teams have historically concentrated capital on preventing unauthorised access to systems, yet the Revolut incident shows that criminals can sometimes obtain equivalent information by convincing authorised personnel to release it voluntarily. That means investment must increasingly move toward systems capable of evaluating the context of an instruction, not just the identity from which it originated, with machine-assisted anomaly detection used to flag requests whose timing, jurisdiction, scope or requested data categories depart materially from established patterns. The relevant contest is therefore between automated impersonation and automated verification, with human legal authority retained for decisions carrying significant consequences.
The next 12–24 months will price the cost of procedural weakness
Over the next 12–24 months, the cost of inaction will fall first on financial institutions that continue to treat government-domain authenticity as evidence of lawful authority and second on customers whose identity and transaction histories can be reused long after the original disclosure. Revolut has already stated that its systems and customer balances were unaffected, yet the company still faces regulatory scrutiny because the economically relevant asset was not only money inside the banking platform but the trusted information held around each customer. The distinction will become increasingly important as banks, fintechs and technology companies process larger volumes of official and emergency requests through digital channels.
The institutional cost will be paid through additional verification infrastructure, legal review, staff training, cryptographic authentication, request portals, anomaly detection and slower handling of exceptional disclosures; the alternative cost is larger, because a bank that perfects encryption, endpoint security and fraud detection while leaving trusted administrative processes vulnerable can still lose the very information those controls were designed to protect. Revolut’s 2026 incident therefore marks a more important boundary than the number of affected customers suggests: cybersecurity is moving from defending systems against illegitimate access toward defending institutions against legitimate-looking authority, and banks that fail to make that transition will continue to expose high-value information without any attacker needing to break through the front door.
Navigational Index
AI is collapsing the defensive time advantage
The principal technological problem is increasingly the compression of the interval between vulnerability discovery, exploitation and defensive remediation, which transforms patch management, identity verification, software assurance and incident containment from periodic administrative functions into near-continuous operational capabilities.
Cybersecurity is becoming a balance-sheet and systemic-resilience issue
The decisive exposure now extends beyond individual banks to common cloud platforms, software components, outsourced infrastructure and interconnected financial-market services, meaning that cyber events can produce correlated operational interruption and potentially propagate into liquidity, payments, clearing and market-confidence channels.
Europe now faces an investment and sovereignty decision
DORA, the ECB supervisory programme, national supervisory initiatives and the UK operational-resilience framework increasingly require financial institutions to strengthen cybersecurity while simultaneously confronting the strategic dependence created by concentrated cloud, AI and software providers, making security architecture, technological sovereignty and capital allocation inseparable policy questions.
Master Abstract
The security perimeter is disappearing
The historical architecture of bank cybersecurity was designed around a relatively intelligible model in which institutions possessed systems, employees possessed credentials, customers entered through controlled interfaces and hostile actors attempted to cross a technological perimeter, yet contemporary financial infrastructure increasingly operates through APIs, cloud services, remote workstations, automated workflows, outsourced software, digital identities, machine-to-machine communication and third-party decision systems, with the consequence that the most consequential attack may originate through technically valid credentials, legitimate infrastructure or an authorised business process rather than through an obviously malicious connection; the strategic problem therefore becomes not only whether an identity is authentic, but whether an authenticated action is authorised in substance, contextually credible, legally valid and proportionate to the information or capability being requested.
That distinction is fundamental because conventional email authentication, device authentication or access control can establish that a recognised account, certificate or system initiated an action without establishing that the human or machine controlling that identity possesses legitimate authority for the particular transaction, and the emerging defensive architecture must consequently incorporate contextual verification across identity, behaviour, device history, legal authority, transaction sensitivity, geography, organisational role and requested data scope, particularly where a request would release high-value financial or identity information.
This development is consistent with the European regulatory architecture rather than being a theoretical extension of it, because DORA requires financial institutions to maintain comprehensive ICT-risk frameworks, continuously monitor systems, preserve availability, authenticity, integrity and confidentiality, test operational resilience and manage third-party dependencies, while specifically placing ultimate ICT-risk responsibility on the management body and requiring appropriate budget allocation for digital operational resilience. Regulation (EU) 2022/2554 — European Parliament and Council
AI changes the economics of attack
Artificial intelligence matters to cybersecurity not principally because criminals can generate more convincing phishing messages, which is already operationally relevant but strategically secondary, but because advanced models increasingly possess capabilities that automate parts of vulnerability discovery, coding, reconnaissance, tool use and multi-stage software operations, thereby potentially increasing both the productivity of sophisticated attackers and the number of actors capable of performing technically demanding operations.
The European Banking Authority’s June 2026 Risk Assessment Report states that recent advances in highly capable frontier AI and large-language models, including their ability to discover and exploit software vulnerabilities, have increased concern among banks and supervisors, while operational risk continues to rise because of cyber risk, data security and fraud. Risk Assessment Report — June 2026 — European Banking Authority
The Bank of England has gone substantially further by treating frontier AI as a potential financial-stability variable, concluding in July 2026 that increasingly capable models can identify and exploit vulnerabilities at greater scale and across multiple stages while forcing financial institutions to discover, evaluate, patch and mitigate weaknesses faster and more frequently; critically, the Bank also identifies the defensive paradox generated by this acceleration, because faster patching and software modification can themselves produce outages when changes are inadequately tested or poorly coordinated across interconnected systems. Financial Stability Report — July 2026 — Bank of England
The resulting race is therefore not simply AI attacker versus AI defender, because the decisive variable becomes whether financial institutions can shorten the complete defensive cycle from detection through prioritisation, testing, remediation, deployment and validation without compromising the operational integrity of systems whose interruption can itself cause financial damage.
Recovery is becoming as important as prevention
The 2024 ECB cyber-resilience stress test is particularly significant because it deliberately assumed that preventive defences had already failed, forcing 109 directly supervised banks, including 28 institutions subjected to enhanced assessment and actual IT-recovery testing, to demonstrate their ability to respond to and recover from a severe but plausible cyber incident affecting core-system databases; the ECB concluded that institutions possessed response and recovery frameworks but that important areas for improvement remained, particularly around continuity, communication, data restoration, third-party collaboration and recovery planning. ECB concludes cyber resilience stress test — European Central Bank
This represents an important conceptual shift because a mature cyber programme can no longer be evaluated principally by whether penetration occurred; institutions must instead demonstrate that payments, liquidity operations, trading functions, customer access, data integrity and management control can survive degradation, isolation or compromise and can subsequently be reconstructed from trusted states without importing corrupted data back into restored systems.
The appropriate benchmark consequently resembles military resilience more than conventional corporate information security: assume penetration, contain blast radius, preserve command authority, maintain essential services, recover trusted operations and learn faster than the adversary adapts.
The next attack surface is institutional trust
One of the largest weaknesses remaining in financial infrastructure is not necessarily software code but the business process through which privileged actions are accepted, because financial institutions routinely process requests, instructions and data transfers originating from regulators, courts, police forces, counterparties, vendors, internal executives and other trusted parties, while technological systems frequently attribute disproportionate evidentiary weight to the recognised origin of those communications.
In an AI-intensive threat environment, that architecture becomes increasingly fragile because the combination of compromised legitimate credentials, synthetic identities, realistic voice and video generation, automated document fabrication and increasingly capable agentic systems reduces the cost of impersonating an authorised institution or individual, meaning that authenticity of origin can no longer serve as sufficient evidence of legitimacy of instruction.
Bank security architectures therefore require what can be described as transactional zero trust, under which high-consequence instructions are independently validated according to their requested action rather than merely according to the recognised identity of the sender, with separate verification channels, cryptographic signing where appropriate, predefined institutional directories, privilege segmentation, behavioural anomaly analysis and escalation rules for requests whose sensitivity or breadth exceeds ordinary historical patterns.
Third-party concentration turns cyber risk into systemic risk
Modern banking has reduced internal technological duplication by purchasing cloud capacity, security services, software platforms, data services and specialised infrastructure from external providers, which can strengthen security at the individual institution while simultaneously increasing concentration risk across the financial system; this creates the possibility that a single provider, common software library, authentication platform or cloud environment becomes an operational dependency for multiple institutions and therefore a transmission channel for correlated disruption.
The ECB’s 2026-28 supervisory priorities explicitly identify third-party risk, cloud dependency and cybersecurity as areas requiring intensified supervision, including dedicated on-site inspection campaigns, threat-led penetration testing and a deep dive into preparedness for service disruption at major cloud providers. ECB Supervisory priorities 2026-28
This concern is reinforced by Italy’s supervisory evidence, because Banca d’Italia reported in July 2026 that major ICT incidents notified during 2025 had increased compared with the previous year, that approximately one quarter were cybersecurity-related and that external ICT providers were significantly involved, strengthening the case for treating supplier resilience as part of the bank’s own security perimeter. Quadro segnaletico di Vigilanza dei gravi incidenti ICT — Banca d’Italia
Defensive AI is becoming infrastructure rather than experimentation
The logical response to machine-speed offensive capability cannot be a security architecture in which the majority of detection, prioritisation and response decisions remain sequentially dependent on human processing, because human governance remains essential but human reaction time cannot scale linearly with automated attack activity; the required architecture therefore increasingly combines human authority with machine-speed surveillance, prioritisation and containment.
AI investment inside banks should consequently concentrate on defensive use cases where machine processing offers measurable advantage: behavioural analytics across user and machine identities; detection of anomalous privileged activity; automated correlation across endpoint, cloud, identity and payment telemetry; vulnerability discovery and prioritisation; software-composition analysis; fraud-network detection; malware classification; phishing and synthetic-content detection; automated playbook execution; and continuous testing of security controls.
The United Kingdom already offers evidence of the scale of AI adoption, because a Bank of England and Financial Conduct Authority survey found 75% of surveyed financial firms already using AI and another 10% planning adoption within three years, while cybersecurity was identified among the leading perceived benefits but also as the greatest perceived systemic risk associated with AI; the same survey found that 33% of AI use cases depended on third parties, illustrating how defensive modernisation can simultaneously create new concentration and governance exposures. AI in UK financial services — Financial Conduct Authority
Investment must shift from cybersecurity products to security architecture
The capital question facing banks is therefore not whether cybersecurity budgets should increase in isolation, but whether institutions possess an investment architecture capable of transforming the entire operational environment, because buying additional detection products while retaining fragmented identity systems, poorly mapped software dependencies, slow vulnerability remediation, weak third-party visibility and unrehearsed recovery arrangements will increase technological complexity without proportionately increasing resilience.
The priority investment layers should increasingly include asset and dependency discovery; privileged-access redesign; identity security; security telemetry; AI-assisted security operations; automated vulnerability management; software supply-chain assurance; immutable logging; segmented backup and recovery infrastructure; third-party concentration intelligence; threat-led penetration testing; cryptographic agility; and post-quantum migration planning, with cyber expenditure evaluated according to measurable reductions in time-to-detect, time-to-contain, time-to-patch, recovery time and potential loss of critical financial services.
This direction is directly supported by DORA, which requires the management body of a financial entity to define, approve, oversee and remain responsible for the ICT-risk framework and specifically requires periodic review of the budget necessary to fulfil digital operational-resilience requirements, thereby making ICT resilience a board allocation decision rather than an exclusively technical function. Digital Operational Resilience Act — EUR-Lex
Italy
Italy’s immediate supervisory evidence indicates that the most relevant vulnerability is not a spectacular concentration of successful cyberattacks but the interaction between operational incidents, external ICT providers and increasingly interconnected digital services, because Banca d’Italia’s July 2026 horizontal analysis found that major ICT incidents increased during 2025, that operational failures remained the majority while roughly one quarter were cyber-related, and that third-party providers featured significantly in the reported incidents. Quadro segnaletico di Vigilanza dei gravi incidenti ICT — Analisi orizzontale 2025 — Banca d’Italia
For Italian institutions, this suggests that the highest-return security investment is likely to lie in reducing the boundary between internal operational-risk management and external supplier oversight, particularly through continuously updated inventories of outsourced applications, contractual recovery obligations, software dependencies, cloud concentration, privileged access and minimum recoverability requirements, because a bank cannot meaningfully calculate its own operational resilience while treating the failure probability and recovery architecture of critical suppliers as an external variable.
Italy also faces a structural asymmetry between major banking groups capable of sustaining sophisticated internal cyber capabilities and smaller institutions whose economic model makes dependence on shared software and service providers more pronounced, which means that sector-wide resilience cannot be achieved exclusively through higher expenditure by the largest banks and will increasingly depend on supervisory pressure, shared intelligence, testing standards and service-provider accountability.
France
France is moving particularly clearly toward treating cybersecurity, AI adoption and technological sovereignty as interdependent strategic questions, because the ACPR’s 2026 programme places implementation of DORA, cyber and operational risk, preparation for AI supervision and tokenisation among its principal supervisory workstreams, while the authority is simultaneously developing methodologies for assessing financial-sector AI systems. Programme de travail 2026 — Autorité de contrôle prudentiel et de résolution
The degree of adoption is already substantial, because the ACPR reported that its 2025 survey found that almost all surveyed banks and insurers had AI use cases in production, transforming model governance from an innovation question into an ordinary prudential and operational-control problem. Intelligence artificielle : les nouvelles frontières du risque — ACPR
The French strategic debate has additionally introduced the issue of technological dependence with unusual explicitness, because Denis Beau of the Banque de France and ACPR argued in September 2026 that digital transformation increases attack surfaces while dependence on hyperscale providers offering cloud and AI capabilities can create long-term technological and operational vulnerabilities, turning cybersecurity architecture into an issue of European strategic autonomy as well as institutional risk management. Cybersécurité : le secteur financier face aux risques de dépendance — ACPR/Banque de France
Germany
Germany’s banking architecture presents a different resilience problem because its comparatively fragmented financial system combines large internationally active institutions with numerous smaller banks and extensive reliance on shared technology and service infrastructures, making the quality and concentration of multi-client ICT providers particularly important to systemic resilience rather than merely to outsourcing compliance.
BaFin has repeatedly identified severe cyber incidents as a principal financial-sector risk and has emphasised that attacks against major multi-client technology providers can threaten not only individual institutions but the functioning and stability of the financial system, while DORA now gives the German supervisory architecture a more integrated framework for incident reporting, third-party risk and operational-resilience supervision. DORA — Bundesanstalt für Finanzdienstleistungsaufsicht
BaFin has also stated that it has not observed a dramatic numerical surge in attacks but has observed increasing professionalism and criminal capability, an important distinction because risk can rise even if incident counts remain stable when attackers become more capable, targets more interconnected and potential loss severity larger.
For Germany, therefore, the central investment requirement is less the indiscriminate expansion of individual security tools than the strengthening of sector-wide dependency mapping, common-provider resilience, automated detection, recovery testing and supervisory visibility into outsourced infrastructure, because fragmented ownership combined with concentrated technology can create hidden common points of failure.
United Kingdom
The United Kingdom currently provides the most explicit official analysis of the emerging AI-cyber interaction, because the Bank of England’s July 2026 Financial Stability Report concluded that rapid advances in frontier AI materially increase financial-stability risks through cyber and operational channels and specifically warned that financial institutions should not treat frontier AI as a marginal extension of traditional cyber risk. Financial Stability Report — July 2026 — Bank of England
The Bank’s analysis is especially important because it identifies a second-order danger frequently missed by conventional cyber strategies: if frontier AI substantially increases the rate at which vulnerabilities are discovered, financial institutions and their suppliers must patch systems more often, while every accelerated production change introduces its own possibility of outage, incompatibility or service interruption; cybersecurity therefore becomes inseparable from change-management capacity, meaning that organisations unable to automate testing, dependency analysis and safe deployment could face rising operational instability even while attempting to become more secure.
The UK policy response increasingly reflects this economic interpretation of resilience, because HM Treasury’s July 2026 report argues that cyber resilience should be regarded not merely as a compliance cost but as an enabler of continuity, investment and long-term financial performance. The Value of Resilience: Cyber Resilience in Financial Services — HM Treasury
European strategic implication
Europe has therefore reached a point at which banking cybersecurity policy can no longer be separated into independent discussions about cybercrime, AI regulation, cloud outsourcing, digital sovereignty and financial stability, because these domains increasingly describe different surfaces of the same system: financial institutions are becoming software-intensive infrastructures operating on increasingly concentrated external technology while adversaries acquire increasingly automated capabilities and governments simultaneously demand that banking services remain continuously available during geopolitical and technological disruption.
DORA establishes the common regulatory foundation by integrating ICT-risk governance, incident reporting, resilience testing, intelligence sharing and third-party risk into a single financial-sector framework, while the ECB has moved from establishing expectations toward deeper testing, inspection and remediation under its 2026-28 supervisory programme.
The policy objective should therefore not be technological self-sufficiency in every layer, which would be economically unrealistic and potentially reduce access to the strongest security technologies, but strategic substitutability, meaning that Europe should know where critical dependencies reside, prevent excessive single-provider concentration, establish credible migration and recovery capabilities and retain sufficient control over identity, cryptography, data and critical operational processes to continue functioning if a provider becomes unavailable, compromised or geopolitically inaccessible.
Key Evidence Table
| Indicator | Value/status | Reference date | Definition/scope | Issuer | Exact source |
|---|---|---|---|---|---|
| ECB cyber resilience exercise | 109 banks, including 28 enhanced assessments | 2024 | Directly supervised euro-area banks; scenario assumed preventive controls failed | European Central Bank | ECB concludes cyber resilience stress test |
| ECB supervisory direction | Operational resilience and robust ICT capabilities are one of two priorities for 2026-28 | 2026-28 | ECB Banking Supervision | European Central Bank | Supervisory priorities 2026-28 |
| EU legal framework | Management bodies bear ultimate responsibility for ICT risk and resource allocation | Applicable from 2025 framework | Financial entities within DORA scope | European Union | Regulation (EU) 2022/2554 |
| EU cyber exposure | Finance ranked among the most targeted European sectors in ENISA’s assessment | Data covering Jan. 2023-Jun. 2024 | EU financial sector | ENISA | ENISA Threat Landscape: Finance Sector |
| Italy ICT incidents | Incidents increased; roughly one quarter cyber-related; substantial third-party involvement | 2025 reports, published July 2026 | Major ICT incidents reported under DORA | Banca d’Italia | Supervisory ICT Incident Reporting Framework — Horizontal Analysis 2025 |
| French AI adoption | Almost all surveyed banks and insurers had AI use cases in production | ACPR 2025 survey, discussed Sep. 2026 | French supervised financial institutions | ACPR/Banque de France | Intelligence artificielle : les nouvelles frontières du risque |
| UK AI adoption | 75% of surveyed firms using AI; another 10% planning adoption within three years | Survey published by FCA/BoE | UK financial services respondents | FCA / Bank of England | AI in UK financial services |
| UK AI systemic assessment | Frontier AI judged capable of materially increasing cyber and operational vulnerabilities | July 2026 | UK financial stability assessment | Bank of England FPC | Financial Stability Report — July 2026 |
| German regulatory position | Cyber incidents with serious consequences treated as major financial-sector risk; provider concentration recognised as a systemic channel | Current supervisory framework | German financial system | BaFin | DORA — BaFin |
Principal Gaps and Watch Indicators
The first decisive indicator is the evolution of time-to-exploit compared with time-to-remediate, because a persistent reduction in the interval between public or machine-generated discovery of vulnerabilities and hostile exploitation would confirm that conventional human-centred patching processes are becoming structurally inadequate, whereas substantial deployment of automated defensive discovery, validation and safe remediation would weaken the assessment that attackers are gaining a durable speed advantage.
A second indicator is the frequency of multi-institution incidents originating from common technology providers, libraries, identity systems or cloud infrastructure, because increasing correlated disruption would validate the judgment that cyber risk is migrating from institution-specific operational risk toward systemic concentration risk; the ECB’s planned third-party inspections, cloud-disruption analysis and DORA critical-provider oversight are therefore particularly important observable measures.
A third indicator is the adoption rate of AI-enabled defensive systems inside security operations, particularly whether automated tools are permitted not merely to identify anomalous activity but to isolate systems, revoke credentials, prioritise vulnerabilities, initiate rollback procedures and coordinate response under predefined human-approved policies, because the distinction between AI-assisted analysis and machine-speed operational defence will become increasingly material if offensive systems continue to accelerate.
A fourth indicator is whether regulators begin measuring cyber resilience through service-loss tolerances and recovery performance rather than primarily through control inventories and compliance attestations, because that would demonstrate a further transition from prevention-oriented supervision toward an assumption-of-compromise framework already foreshadowed by the ECB cyber stress exercise.
A fifth indicator concerns cryptographic transition, because rapid improvements in AI capability have reinforced wider concerns that technological discontinuities can arrive sooner than institutional investment cycles anticipate, while the Bank of England has explicitly linked AI-driven cyber preparedness with the long-term need to prepare for post-quantum cryptography; material progress in cryptographic inventorying and migration programmes would reduce the risk that institutions discover too late that critical authentication and confidentiality infrastructure cannot be replaced within operationally acceptable timelines.
The principal unresolved official record concerns comparable cross-country statistics for severe ICT incidents under the now-harmonised DORA reporting regime, because national publications remain uneven in granularity and reference periods, preventing a methodologically defensible ranking of Italy, France, Germany and other European banking systems according to actual cyber-incident rates or losses.
A second unresolved record concerns actual financial expenditure on cybersecurity and AI-enabled defensive capability across individual European banks, because public supervisory sources establish rising regulatory priority and documented weaknesses but do not yet provide sufficiently harmonised capital- and operating-expenditure data to establish a defensible Europe-wide cyber-investment requirement or return-on-investment benchmark.
A third unresolved record concerns concentration within AI security infrastructure itself, because widespread adoption of a small number of frontier-model, cloud, cybersecurity or identity providers could strengthen individual institutions while creating a new class of correlated systemic exposure whose magnitude cannot presently be quantified from the official public record.
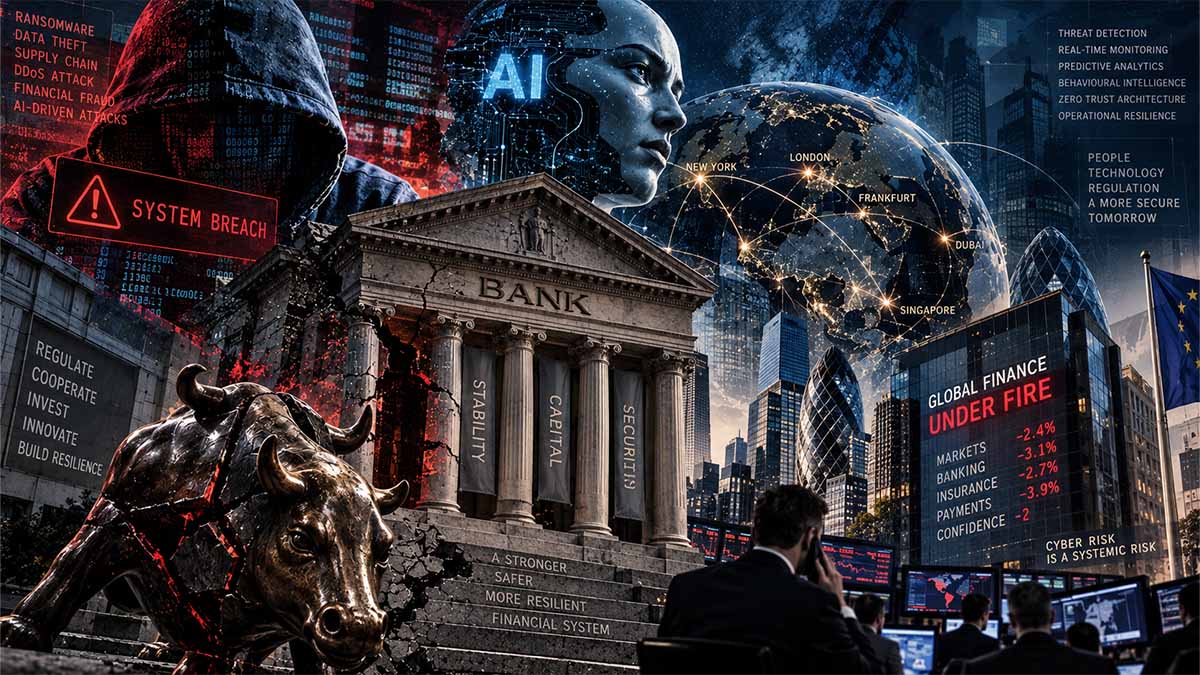
Banking System Under Fire: Why AI Is Forcing a New Cybersecurity Architecture for Global Finance
BLUF (Bottom Line Up Front): Banking cybersecurity has entered a structural transition where perimeter defence is obsolete. Artificial intelligence, compromised trusted identities, cloud concentration, and automated workflows are eroding the distinction between external attacks and authorized actions. Future security architecture must authenticate authority, intent, context, and proportionality rather than merely users, devices, and networks. With the ECB prioritizing operational resilience (2026–2028), DORA enforcing board-level accountability, and frontier AI accelerating vulnerability discovery, financial institutions must shift from compliance checklists to balance-sheet-level systemic resilience.
AI Attack Acceleration and the Disappearing Security Perimeter
Automated Vulnerability Exploitation
Frontier LLMs automate software vulnerability discovery, reconnaissance, and multi-stage exploit execution. As warned by the EBA (June 2026) and Bank of England (July 2026), AI compresses the time between vulnerability disclosure and hostile exploitation, forcing financial institutions to patch at unsustainable tempos.
Transactional Zero Trust
With APIs, cloud services, and machine-to-machine communications dominating finance, attacks routinely execute via valid credentials and authorized workflows. Traditional origin authentication is insufficient; security architecture must verify substantive authority, intent, and contextual credibility.
The Patching Paradox
Accelerated patching cycles generate secondary operational risk: hastily tested updates or uncoordinated changes across interconnected systems can trigger severe service outages, proving that change management is now a core stability variable.
Table 1: Key Audited Evidence & Regulatory Benchmarks
Controlling official findings from the ECB, EBA, Bank of England, ENISA, and European Union DORA framework.
| Indicator / Program | Verified Status / Value | Scope & Operating Context | Issuing Authority | Strategic Significance |
|---|---|---|---|---|
| ECB Cyber Stress Test | 109 banks; 28 enhanced assessments | 2024 exercise assuming preventive controls failed. | European Central Bank | Established assumption-of-compromise testing across euro-area institutions. |
| ECB Supervisory Priorities | Operational resilience & ICT core focus | Supervisory cycle 2026–2028; inspections & cloud analysis. | ECB Banking Supervision | Elevates cyber governance to top prudential supervisory level. |
| DORA Legal Framework | Mandatory board responsibility & ICT resilience | Applicable from 2025 across EU financial entities. | European Union | Transforms security into binding board-level regulatory duty. |
| ENISA Finance Sector Risk | Finance ranked among most targeted European sectors | Data covering Jan 2023 – Jun 2024. | ENISA | Confirms persistent targeting of financial institutions by malicious actors. |
| UK AI Adoption Survey | 75% firms using AI; 10% planning within 3 years | FCA / Bank of England financial services survey. | FCA / Bank of England | Shows widespread deployment while highlighting cyber risk as primary AI hazard. |
| Bank of England FSR | Frontier AI judged a financial-stability risk | July 2026 Financial Stability Report. | Bank of England (FPC) | Elevates AI cyber risk from IT concern to macroprudential stability threat. |
Table 2: National Jurisdictional Lenses (Italy, France, Germany, UK)
Supervisory focus, empirical findings, and systemic risk profiles across core European banking markets.
| Jurisdiction | Supervisory Body | Empirical Finding / Focus | Primary Systemic Vulnerability | Strategic Policy Priority |
|---|---|---|---|---|
| ITALY | Banca d’Italia | Major ICT incidents increased in 2025; ~25% cyber-related; heavy third-party involvement. | Asymmetry between major banking groups and smaller institutions reliant on shared IT providers. | Integrating external supplier oversight into internal operational risk management. |
| FRANCE | ACPR / Banque de France | Almost all surveyed banks/insurers have AI in production (2025 survey); DORA & AI supervision. | Cloud and hyperscaler dependency creating long-term operational and sovereign vulnerabilities. | Merging cyber resilience with European technological sovereignty and model governance. |
| GERMANY | BaFin | Increased attacker professionalism; multi-client technology provider concentration risks. | Fragmented financial system relying on shared multi-client ICT and service infrastructure. | Sector-wide dependency mapping and common-provider operational resilience. |
| UNITED KINGDOM | Bank of England / FCA / HM Treasury | Frontier AI accelerates vulnerability discovery and patching loops; 33% AI use via third parties. | Second-order instability from accelerated patching cycles triggering software incompatibilities. | Treating cyber resilience as productive capital and managing change-management velocity. |
Deep Structural Breakdown: Core Banking Cyber Vectors
Deconstructing the transition from perimeter defence to assumption-of-compromise and systemic concentration.
Assumption-of-Compromise (Recovery)
Following the ECB’s 2024 cyber stress test, traditional perimeter defence is no longer the sole metric. Banks must prove they can survive core database compromise, preserve command authority, maintain essential payments, and reconstruct clean operations without reintroducing corrupted data.
Institutional Trust & Synthetic Fraud
Attackers exploit institutional trust by weaponising communications from regulators, courts, and counterparties. Combined with compromised credentials, deepfakes, and synthetic documents, origin authentication fails; institutions require transactional zero trust to validate substance and context.
Concentration & Correlated Failure
Outsourcing to common cloud providers, software libraries, and payment platforms creates systemic concentration. An AI-accelerated vulnerability in a shared component propagates simultaneously across institutions, transforming technical flaws into macroprudential stability events.
Forensic Strategic Key Judgments
Definitive analytical conclusions derived from supervisory findings, regulatory mandates, and threat data.
Perimeter Defence is Structurally Obsolete
APIs, cloud workloads, and automated workflows mean attacks execute via authorised channels, requiring contextual verification of authority and intent.
Frontier AI Accelerates Vulnerability Exploitation
LLMs automate software reconnaissance and exploitation, forcing institutions to patch at unprecedented tempos while risking secondary change-management outages.
Resilience is Balance-Sheet Productive Capital
Cyber expenditure must be treated as core prudential infrastructure comparable to liquidity management, directly protecting financial stability.
DORA Mandates Board-Level Accountability
Ultimate responsibility for ICT risk rests with management bodies, converting cybersecurity into a binding legal duty with mandated budget allocation.
Concentration Risk Threatens Systemic Stability
Reliance on common cloud and software providers creates correlated failure pathways, turning individual IT failures into systemic financial crises.
Machine-Speed Defence is Mandatory
Human-centric security operations cannot scale against automated attacks; AI must be integrated into telemetry correlation, threat containment, and asset discovery.
Open Official Record Gaps
- Harmonised Incident Statistics: Absence of fully comparable cross-country severe ICT incident metrics under DORA due to varying national reporting granularities.
- Exact Cyber Capital Allocation: Lack of harmonised financial expenditure data to establish a definitive Europe-wide cyber investment benchmark across banks.
- AI Security Infrastructure Concentration: Unquantified systemic exposure resulting from widespread reliance on a small number of frontier AI and cloud security vendors.
- Post-Quantum Cryptographic Readiness: Incomplete public tracking of cryptographic inventorying and migration timelines across major European banking groups.
Observable Watch Indicators (Horizon 2026–2031)
AI is collapsing the defensive time advantage
Principal judgment
The decisive technological change confronting banks is not simply that artificial intelligence gives malicious actors another offensive instrument, but that increasingly capable AI systems are compressing the interval separating vulnerability discovery, exploit development, reconnaissance, attack execution and defensive remediation, thereby attacking one of the assumptions on which conventional financial-sector cybersecurity has historically depended: that defenders will have sufficient time after identifying a weakness to understand its significance, determine where the vulnerable software is deployed, prioritise remediation, test a patch, obtain operational approval, coordinate implementation with suppliers and business owners, deploy the change and verify that critical services remain stable before an adversary can exploit the same weakness at scale.
That assumption is becoming progressively less defensible, because the [European Banking Authority's June 2026 Risk Assessment Report] states that recent frontier large-language models have developed substantially enhanced capabilities to discover and exploit software vulnerabilities and warns that banks can become particularly vulnerable when they lack the operational capacity to respond at comparable speed, while the [Bank of England's July 2026 Financial Stability Report] reaches the more consequential systemic conclusion that frontier AI can materially alter the speed, scale and economics of cyber risk, increasing not only the rate at which vulnerabilities are identified and exploited but also the frequency with which financial institutions must modify production systems merely to remain secure.
The resulting problem is therefore better understood as a loss of defensive time advantage than as a conventional increase in cyberattack volume, because the strategic variable is becoming the difference between two operational clocks: the attacker's time from discovery to effective exploitation and the defender's time from discovery to verified remediation, with financial institutions remaining comparatively secure only when the second process can reliably remain ahead of, or sufficiently close to, the first without introducing unacceptable operational instability.
The next generation of banking cybersecurity must consequently operate much closer to continuous control than periodic administration, transforming vulnerability management, software assurance, privileged-access monitoring, identity verification, threat detection, configuration management and containment from activities conducted according to weekly, monthly or quarterly cycles into processes capable of accelerating dynamically when machine-generated threat activity requires it, while simultaneously preserving the governance, testing and safety standards demanded of institutions whose systems support deposits, payments, trading, clearing, settlement and access to liquidity.
The critical metric is moving from vulnerability count to exposure time
Traditional vulnerability-management programmes frequently organise their activity around inventories of discovered weaknesses, severity classifications, remediation deadlines and service-level agreements, yet an AI-accelerated environment makes the duration of exploitable exposure increasingly more important than the absolute number of vulnerabilities recorded, because a bank possessing thousands of known but low-value weaknesses can remain operationally safer than an institution containing a smaller number of externally reachable weaknesses that can be converted into reliable attack paths before remediation teams can act.
The distinction between discovery and exploitability is especially important because vulnerability databases already contain enormous numbers of technical weaknesses, whereas only a much smaller subset are observed being exploited in operational environments; the United Kingdom's National Cyber Security Centre noted in its May 2026 guidance that more than 40,000 vulnerabilities received CVE identifiers during 2025, while approximately 400 newly tracked vulnerabilities entered the US Cybersecurity and Infrastructure Security Agency's Known Exploited Vulnerabilities framework as being exploited and only around 40 were zero-days when initially exploited, demonstrating why a simple strategy of attempting to patch everything according to numerical severity is operationally inadequate and why exploitation evidence, asset criticality, exposure and attack-path relevance increasingly have to determine priority.
The [NCSC guidance on using AI for vulnerability discovery] consequently makes a point of considerable importance for financial institutions: discovering additional vulnerabilities does not itself improve security and can actually worsen operational conditions if the discovery system produces findings faster than engineering, security and operational teams can validate and remediate them, because the organisation then creates a rapidly expanding queue of unresolved weaknesses whose prioritisation itself becomes a resource problem.
This becomes particularly acute in banking environments because vulnerability remediation rarely consists of applying an isolated patch to an isolated computer, since critical financial applications can depend on databases, operating systems, middleware, authentication services, payment interfaces, market-data feeds, APIs, third-party libraries, hardware-security modules, cloud services and legacy applications whose interactions may not be fully visible to the team responsible for the affected component, meaning that the real defensive latency is determined not merely by whether a patch exists but by whether the institution can safely identify every affected dependency and deploy the correction without damaging the service it is trying to protect.
Frontier AI is changing the rate of vulnerability discovery
The evidence available in 2026 does not establish that frontier AI can already conduct reliable, autonomous and covert end-to-end attacks against highly defended major banks, and any such claim would exceed the public record, but official UK assessments do establish that current models have made unusually rapid progress in technically relevant components of offensive cyber operations, particularly vulnerability discovery, exploit development, tool use, sustained multi-step activity and reverse engineering.
The [National Cyber Security Centre's March 2026 assessment] reports that, in controlled testing conducted by the UK AI Security Institute, frontier models progressed in only eighteen months from making negligible progress on a realistic simulated enterprise attack to the strongest tested model averaging 15.6 completed steps out of a 32-step attack sequence when given extended processing time, corresponding to approximately six hours of work that the NCSC estimated would require a skilled human professional around fourteen hours to complete, while the estimated cost of a full automated attempt had fallen to roughly £65.
This evidence requires careful interpretation, because the NCSC expressly notes that models tested before March 2026 had not completed that enterprise scenario end-to-end and continued to exhibit weaknesses in specialist knowledge, long-duration coordination, reliability and stealth, while the Bank of England similarly cautions that success in simulated cyber environments does not demonstrate that frontier systems can already perform reliable attacks against well-defended real-world institutions; nevertheless, the relevant strategic signal is the rate of capability improvement, because systems that previously struggled with isolated cyber tasks are increasingly able to sustain longer sequences, use tools, recover from mistakes and perform parts of complex operations with progressively less human intervention.
The Bank of England's July 2026 assessment provides an especially striking indicator of this progression, reporting that frontier systems are increasingly capable of completing longer software tasks and citing AI Security Institute testing in which one advanced model completed a reverse-engineering challenge in 10 minutes and 22 seconds compared with approximately twelve hours for a human expert, while the Bank also records evidence that frontier systems were being used to identify vulnerabilities in widely deployed open-source and commercial software at volumes significantly above historical discovery rates.
The implication is not that every newly discovered weakness immediately becomes exploitable or systemically important, but rather that the economics of searching enormous software estates for weaknesses are changing because machine systems can examine code, configurations and attack paths continuously and in parallel, which means that software defects that might previously have remained undiscovered for years can increasingly become visible to both defensive and offensive actors within much shorter periods.
The “patch wave” changes the operational problem
The UK's technical cyber authority has therefore begun warning not merely about increased attacks but about what it explicitly describes as a “vulnerability patch wave”, because AI-assisted discovery can expose decades of accumulated technical debt across commercial software, open-source components, proprietary platforms and software-as-a-service environments, creating a forced correction in which organisations must absorb much higher volumes of security updates than their historical operating models were designed to process.
The [NCSC's May 2026 guidance on preparing for a vulnerability patch wave] advises organisations to prepare to deploy updates quickly, more frequently and at scale, recommending secure hot-patching where available, automatic updates where appropriate and risk-prioritised deployment mechanisms when neither approach is possible, while simultaneously recognising that rapid updating becomes substantially more difficult in safety-critical or operationally sensitive systems where a poorly tested change can itself interrupt essential services.
For banking systems, this represents a fundamental alteration of operational doctrine because a vulnerability programme historically optimised for scheduled maintenance windows can become structurally inadequate if the discovery rate increases by an order of magnitude while the production-change architecture remains unchanged, and the institution can therefore reach a point at which its greatest security weakness is not the absence of patches but the inability to consume patches safely at the rate at which vulnerabilities are being generated.
The Bank of England identifies precisely this problem when it warns that a higher frequency of vulnerability discovery forces firms to patch and mitigate weaknesses more rapidly while faster change itself increases the probability of configuration mistakes, compatibility failures and operational outages, producing a defensive paradox in which insufficient patching increases compromise risk but uncontrolled patching increases service-disruption risk.
For banks, whose systems frequently have stringent availability requirements, this means that software change management is becoming part of cybersecurity in a much deeper sense than previously recognised, because vulnerability remediation cannot be accelerated sustainably unless the institution can simultaneously accelerate software testing, dependency analysis, rollback, business validation, production monitoring and recovery.
The defensive pipeline must become an engineered system
The traditional model in which security teams discover vulnerabilities, generate tickets and transfer responsibility to application owners will progressively become insufficient in a machine-speed threat environment, because every human hand-off introduces latency while every disconnected inventory creates uncertainty about whether a discovered weakness is actually present in the production estate.
An effective future banking architecture therefore requires a continuous defensive pipeline capable of linking asset discovery, software composition, vulnerability intelligence, exploitability assessment, business-service mapping, attack-path analysis, remediation development, automated testing, controlled deployment and post-change verification, so that vulnerability management operates as an engineered lifecycle rather than a sequence of loosely connected administrative processes.
The [joint May 2026 statement by the Bank of England, Financial Conduct Authority and HM Treasury] explicitly moves in this direction by stating that financial firms should be capable of triaging, prioritising, assessing and remediating vulnerabilities more quickly, more frequently and at scale, including through automation where appropriate, while also requiring institutions to understand external applications, libraries and services integrated into their networks and to prepare for large-scale remediation of vulnerabilities originating in third-party components.
This requirement has particularly important implications for older banking estates because legacy systems, end-of-life platforms, proprietary applications and unsupported software can create remediation bottlenecks that AI cannot solve merely by detecting vulnerabilities faster, and the same UK authorities therefore explicitly state that investment and resource-allocation decisions should reflect exposure created by systems that have reached end of life or lost vendor support.
In practical terms, an institution whose security tooling can identify a critical weakness within minutes but whose architecture requires several weeks to determine ownership, locate dependencies, obtain vendor confirmation, construct a regression environment, secure business approval and identify a maintenance window has not achieved machine-speed defence, because artificial intelligence has accelerated only the first stage of a much longer organisational process.
AI therefore exposes organisational latency as a cyber vulnerability
The emerging strategic weakness is consequently not exclusively technical debt but decision latency, because banks frequently operate complex governance arrangements designed to prevent uncontrolled changes to highly sensitive systems, yet those arrangements can become exploitable disadvantages when approval chains, fragmented responsibilities and poor data about system dependencies cause critical security decisions to move substantially slower than the threat.
This does not mean that banks should eliminate human control, regulatory review or software-change governance, because high-speed automated remediation capable of modifying production banking systems without robust safeguards could generate operational failures with consequences comparable to the attacks it is intended to prevent; instead, institutions increasingly need pre-authorised response envelopes in which management bodies establish in advance which classes of security action can be executed automatically, which require rapid human validation, which systems require enhanced testing and which business services must never be modified without explicit senior approval.
Such an architecture converts governance from a serial bottleneck into a predefined control system, because decision rights, rollback conditions, testing requirements and escalation thresholds are established before the emergency rather than negotiated after vulnerability discovery, allowing the institution to accelerate response without abandoning accountability.
This direction is consistent with the legal structure established by the [EU Digital Operational Resilience Act, Regulation (EU) 2022/2554] , which requires financial entities to maintain comprehensive ICT-risk frameworks and specifically requires documented ICT change-management policies under which modifications to software, hardware, firmware, systems and security parameters are recorded, assessed, tested, approved, implemented and verified in a controlled manner, while additionally requiring comprehensive policies governing patches and updates.
The regulatory objective is therefore not maximum patch speed irrespective of consequences, but maximum safe remediation velocity, because operational resilience depends on reducing the attacker's usable window while preserving the integrity and availability of the financial service.
Identity verification is entering the same time-compression problem
The reduction in defensive time extends beyond software vulnerabilities because AI-assisted impersonation, synthetic content and automated social engineering can simultaneously increase the rate at which apparently credible privileged requests are generated, forcing identity systems to evaluate not merely who appears to be initiating an action but whether the requested action is consistent with that identity's authority, historical behaviour and operational context.
Traditional identity and access management has been heavily oriented toward authentication events, credentials, devices and assigned privileges, but a valid credential does not establish that every action executed through the credential is legitimate, particularly where a privileged account has been compromised or where an authenticated user has been manipulated into initiating an otherwise valid transaction.
DORA already establishes the regulatory foundation for stronger control by requiring financial entities to limit physical and logical access to what is necessary for legitimate and approved functions and to implement strong authentication mechanisms together with appropriate administration of access rights.
The next defensive layer must extend beyond static authentication into continuous contextual authorisation, meaning that high-consequence actions should be evaluated against the sensitivity of the requested information, normal behavioural patterns, transaction history, device condition, network context, business purpose and the relationship between the requesting identity and the affected asset, because machine-generated deception increasingly weakens the historical assumption that an apparently legitimate communication or credential is itself sufficient evidence of legitimate authority.
This is particularly significant for privileged accounts, security administrators, payment operators, treasury staff and personnel authorised to access customer information, where a compromise can bypass perimeter controls entirely and transform the attacker's problem from entering the system into persuading an already trusted component of the system to perform the desired action.
Detection without machine-speed containment will increasingly be insufficient
Financial institutions have invested heavily in security monitoring, security-information and event-management systems, endpoint telemetry and fraud analytics, but the compression of attacker timelines creates a growing distinction between seeing an attack quickly and stopping it quickly, because detection produces operational advantage only when institutions can transform an alert into containment before the attacker completes the relevant stage of the operation.
The [NCSC's March 2026 frontier-AI assessment] argues that defenders continue to possess an important structural advantage because they can shape and instrument their own environments, correlate signals across systems, understand intended behaviour and force attackers to remain concealed continuously, while attackers need only make one sufficiently valuable mistake by defenders exploitable; nevertheless, the NCSC expressly warns that this advantage is not guaranteed and can erode when attackers adopt AI more effectively than defenders or when weak baseline security degrades the quality of defensive information.
This means that future security operations centres will increasingly require automated containment functions capable of operating under defined policies, including session termination, credential revocation, endpoint isolation, workload quarantine, malicious-process suppression, network segmentation and enforcement of temporary restrictions on suspicious accounts, because routing every actionable event to a human analyst before any defensive intervention recreates precisely the time disadvantage that machine-speed attacks are capable of exploiting.
DORA explicitly anticipates part of this architecture by permitting automated mechanisms to isolate affected information assets during cyberattacks within the ICT-risk framework required of regulated financial entities.
The governance challenge is therefore to determine which responses are sufficiently reversible and low-risk to automate, which actions require human confirmation and which interventions carry such significant potential consequences for customers or financial-market functioning that they must remain under direct operational control, because the optimal architecture is not unrestricted autonomous defence but bounded automation operating under predetermined authority.
The attacker's asymmetry remains important
Even in an AI-enabled environment, attackers and defenders do not face symmetrical objectives, because attackers can choose their target, tolerate failed attempts, exploit different institutions sequentially and concentrate resources on a single weakness, whereas banks must defend large and heterogeneous estates continuously while maintaining availability, satisfying regulatory requirements and avoiding changes that disrupt customers or market infrastructure.
This asymmetric burden becomes more consequential when AI increases attack scalability, because a malicious actor capable of cheaply testing the same vulnerability or social-engineering technique against thousands of endpoints gains value even when the probability of success against each individual target remains low, whereas the defender must detect and respond to every consequential intrusion attempt across all critical systems.
Defenders nevertheless retain substantial structural advantages when their environments are well engineered, including privileged access to internal telemetry, authoritative knowledge of intended system behaviour, the ability to redesign vulnerable architecture, control access, revoke identities, segment networks and modify software, which is why the NCSC concludes that AI can strengthen defenders disproportionately when they maintain accurate inventories, robust access controls, secure configurations and comprehensive logging.
The implication for banking strategy is therefore not that AI inevitably gives attackers a permanent advantage, but that AI magnifies the quality of the underlying security architecture, accelerating capable defenders while simultaneously making organisations with fragmented inventories, legacy software, weak access controls and slow remediation processes progressively easier to exploit.
Vulnerability abundance creates a prioritisation crisis
One of the most counterintuitive consequences of AI-assisted vulnerability discovery is that the financial system can become less secure even while discovering far more weaknesses, because remediation capacity is finite and an excessive flow of undifferentiated findings can consume engineering resources that should instead be concentrated on vulnerabilities that are reachable, exploitable and capable of affecting critical services.
The NCSC's May 2026 guidance therefore emphasises that organisations using AI for vulnerability discovery need an established process capable of receiving, prioritising and fixing findings without overwhelming security teams, while the Bank of England similarly warns that a persistent increase in vulnerability volume could impose a sustained burden of triage, patching, testing and recovery across firms and suppliers.
Banks consequently require risk-based prioritisation architectures that combine technical severity with evidence of exploitation, internet exposure, business-service importance, privilege requirements, attack-path connectivity, compensating controls and the potential consequences of compromise, because treating all vulnerabilities as equivalent will consume scarce remediation capacity without meaningfully minimising financial risk.
The US Cybersecurity and Infrastructure Security Agency's [Known Exploited Vulnerabilities Catalog] illustrates this principle by maintaining an authoritative list of vulnerabilities for which evidence of active exploitation exists and urging organisations to use exploitation evidence as an input into vulnerability-management prioritisation, a methodology that becomes increasingly important as AI raises the number of technically valid discoveries faster than institutions can remediate them.
Third parties can determine the bank's remediation speed
A bank can redesign its internal vulnerability programme and still remain slower than the threat if critical software suppliers, cloud providers or outsourced technology operators cannot remediate their components at comparable speed, because the financial institution cannot patch software that it does not control and cannot safely alter a managed service whose internal dependencies are invisible to it.
This is one reason the EBA's first DORA-wide report on major ICT incidents, published in June 2026, describes ICT risk as increasingly borderless and interconnected and explicitly links the evolution of highly capable AI-driven tools to the need for stronger financial-sector cybersecurity.
The [DORA technical standards governing ICT third-party services] require financial institutions to retain effective control of operational risk, information security and business continuity throughout third-party contractual relationships and to assess subcontracting chains supporting critical or important functions, reflecting the regulatory recognition that technological responsibility cannot be outsourced merely because technological execution has been outsourced.
In the accelerated environment, supplier contracts therefore require a different resilience logic, including sufficiently rapid vulnerability notification, vulnerability-remediation obligations, coordinated testing, emergency change procedures, evidence of software dependencies, incident cooperation and credible exit or substitution arrangements, because a contractual service-level agreement measured in days can become irrelevant when an exploitable weakness is being weaponised in hours.
The dangerous threshold is when attacker speed exceeds institutional change capacity
The principal systemic threshold will be crossed not when AI discovers its first vulnerability or performs its first automated attack sequence, because those events have already occurred in controlled or limited settings, but when the volume and speed of exploitable discoveries persistently exceed the financial sector's ability to absorb them through safe remediation.
The Bank of England's July 2026 scenarios are particularly important because they identify this differential explicitly: in the favourable pathway, defenders use frontier AI sufficiently effectively to keep the backlog of unfixed vulnerabilities broadly stable, whereas in the adverse pathway malicious actors gain capabilities faster than institutions adapt, causing the population of known but unresolved weaknesses to rise and increasing the probability of common vulnerabilities being exploited simultaneously across firms or suppliers.
This provides a more useful strategic indicator than raw attack counts, because the relevant question for supervisors and boards becomes whether the stock of materially exploitable vulnerabilities is shrinking, stable or increasing after accounting for the rate of new discovery, and whether remediation capacity can surge during periods when major suppliers disclose unusually large numbers of weaknesses simultaneously.
A banking system experiencing more discovered vulnerabilities but a declining exposure window can become safer, whereas a system reporting stable incident numbers while accumulating an expanding backlog of exploitable weaknesses can become progressively more fragile without that deterioration being visible in conventional cyberattack statistics.
The software-change paradox becomes a financial-stability issue
The most important second-order consequence of this transition is that the cybersecurity problem becomes inseparable from operational resilience, because the institution must simultaneously defend itself against malicious modification and conduct a much greater volume of legitimate modification in response to discovered weaknesses.
If patching becomes continuous while testing remains predominantly manual, institutions can either delay remediation and preserve operational stability at the price of a longer attack window or accelerate changes and accept a growing probability that defensive actions themselves interrupt business services, which is why the Bank of England identifies faster patching as a potential source of disruption rather than assuming that every increase in remediation speed automatically improves resilience.
This has direct implications for payments, trading, clearing and settlement because common software or infrastructure vulnerabilities can cause many institutions to implement emergency changes within the same narrow time window, potentially producing correlated failures even when no attacker succeeds in compromising the underlying systems; a sufficiently serious vulnerability can therefore generate systemic pressure through the defensive reaction itself, particularly when multiple banks and infrastructures depend on the same provider or component.
The future resilience architecture consequently requires not simply faster patching but automated regression testing, digital replicas of critical environments where feasible, reliable configuration baselines, rehearsed rollback procedures, service dependency mapping, continuous observability and segregated recovery environments, because institutions must become capable of changing rapidly without losing confidence in the integrity of the resulting system.
AI-enabled defence is necessary, but autonomous defence requires boundaries
The [Bank of England, FCA and HM Treasury joint statement of 15 May 2026] expressly advises financial institutions to consider automated and AI-enabled defensive systems capable of operating at speeds comparable to AI-driven attacks, marking an important policy shift because machine-speed defence is increasingly being treated as an operational-resilience requirement rather than as an experimental cybersecurity capability.
The strongest use cases are those in which AI reduces informational or procedural latency without independently determining irreversible financial outcomes, including analysing vulnerability disclosures, correlating security telemetry, mapping software dependencies, enriching alerts, identifying anomalous privilege use, generating candidate patches, prioritising remediation queues and recommending containment actions, whereas actions capable of materially affecting customer assets, market infrastructure or legally protected information require considerably stronger governance.
The NCSC accordingly warns that AI-enhanced security systems create their own dependencies and failure modes and should themselves be treated as part of the attack surface, while separately emphasising that vulnerability-discovery models require careful control over access to source code, production systems, sensitive data and organisational infrastructure.
Banks therefore require a security architecture in which defensive AI is extensively used but not implicitly trusted, with model outputs treated as evidence requiring validation according to consequence, model access segregated, actions logged immutably, privileges minimised and automated remediation constrained by predefined authority boundaries.
Board governance must move from cyber budget to cyber throughput
The management question changes substantially under this model because boards can no longer evaluate cybersecurity primarily by asking whether expenditure increased, whether regulatory findings were closed or whether the organisation purchased contemporary security tools, since the relevant operational question is whether the institution possesses sufficient defensive throughput to identify, prioritise, remediate and recover faster than the threat environment generates material exposure.
A credible board-level dashboard should therefore increasingly track measurements such as the time from vulnerability disclosure to organisational identification, the time from identification to exploitability assessment, the percentage of externally exposed critical vulnerabilities remediated inside defined windows, the proportion of critical assets mapped to complete dependency inventories, the ability to implement emergency changes without service interruption, the percentage of privileged actions subjected to contextual monitoring, supplier remediation latency and tested recovery times for critical business services.
This governance transformation is already consistent with European law because [DORA] places ultimate responsibility for ICT risk management with the financial entity's management body, requires it to define and approve digital operational-resilience strategy and requires ICT-risk management to form an integral component of the institution's overall risk-management system, meaning that the capacity to respond to compressed cyber timelines cannot legitimately remain confined to the chief information security officer.
The relevant board question is therefore becoming not “How much are we spending on cybersecurity?” but “Can this institution change, contain and recover at the speed at which material cyber risk is now being generated?”, because a large budget attached to a slow operational model can remain strategically inferior to a smaller but highly automated security architecture capable of reducing exposure time without compromising business continuity.
Banking architecture now requires continuous defensive readiness
The evidence therefore supports a strong but bounded conclusion: frontier AI has not yet publicly demonstrated reliable autonomous compromise of hardened global banking systems, and it would be analytically irresponsible to describe such a capability as established, but official assessments from the EBA, Bank of England and NCSC collectively establish that the speed, affordability and complexity of AI-assisted vulnerability discovery and cyber operations have improved sufficiently to require immediate adaptation by financial institutions rather than observation from the sidelines.
The central strategic transformation is consequently temporal rather than merely technological, because banks that historically measured vulnerability response in weeks or scheduled maintenance cycles increasingly need architectures capable of acting in hours or, for narrowly defined defensive functions, minutes, while simultaneously preserving controlled deployment, legal accountability and operational safety.
This requires a progression from periodic vulnerability scanning toward continuous exposure management; from static authentication toward contextual authorisation; from human-only security operations toward bounded machine-speed containment; from manually assembled software inventories toward continuously maintained dependency intelligence; from scheduled patching toward safe high-frequency change; from supplier oversight conducted primarily through contractual documentation toward observable third-party resilience; and from cyber incident response plans toward tested operational recovery capable of restoring trusted financial services under conditions in which compromise must be assumed rather than treated as exceptional.
The institutions that retain the defensive advantage will therefore not necessarily be those with the largest security budgets or the greatest number of cybersecurity products, but those capable of converting intelligence into controlled action faster than an adversary converts vulnerability into exploitation, because in the emerging environment time itself is becoming a security control, and institutional latency is becoming an attack surface.
Key judgments
The evidence supports the judgment that AI is compressing the defensive time advantage, although the degree and pace of that compression remain uncertain because current frontier systems still exhibit reliability, stealth and coordination limitations in complex real-world attacks; nevertheless, waiting for fully autonomous offensive capability before restructuring defensive operations would leave banks attempting to redesign critical systems after the relevant speed differential has already emerged.
The most immediate banking vulnerability is therefore not a hypothetical super-intelligent cyber adversary but the interaction between rapidly increasing vulnerability-discovery capability and slow institutional processes for asset identification, prioritisation, testing, approval, deployment and recovery, which is why the EBA and UK authorities increasingly emphasise operational capacity rather than vulnerability discovery alone.
The principal defensive investment requirement is consequently an end-to-end increase in safe remediation velocity, integrating AI-assisted discovery with asset intelligence, exploitability prioritisation, automated testing, controlled patch deployment, contextual identity monitoring and rapid containment, because accelerating only detection would increase the volume of known exposure without necessarily reducing risk.
The most serious systemic pathway arises where the same vulnerabilities or emergency fixes affect widely shared software, cloud infrastructure or technology providers, because the reduction of remediation time can then produce simultaneous defensive activity across institutions and create correlated operational disruption even where direct compromise remains limited.
The regulatory direction already supports this transformation through DORA's requirements for ICT risk governance, change management, patch policies, third-party oversight and operational resilience, while the Bank of England, FCA and HM Treasury have now explicitly recommended consideration of automated and AI-enabled defences capable of responding at speeds comparable to AI-assisted attacks.
What would change the assessment
The assessment would weaken materially if independent official evaluations showed that frontier cyber capabilities had plateaued for a sustained period, that exploitation remained substantially dependent on specialist human operators despite further model improvements, and that financial institutions were reducing critical remediation times rapidly enough to prevent growth in their stock of exploitable vulnerabilities, because those developments would indicate that defenders were retaining or rebuilding their temporal advantage.
The assessment would strengthen materially if frontier models demonstrated reliable end-to-end compromise of defended enterprise networks under realistic monitoring conditions, if open-weight models approached the cyber capabilities currently concentrated in restricted frontier systems, if inference costs continued to fall sufficiently to support inexpensive mass exploitation, or if supervisors documented persistent growth in the backlog of known but unresolved vulnerabilities across major banks and shared technology providers.
A particularly important threshold would be evidence that multiple financial institutions were being affected simultaneously by the same newly discovered weakness before validated remediation became available, because such an event would demonstrate that the theoretical connection between accelerated discovery, common technology dependencies and systemic financial disruption had moved from a prospective risk pathway to an observed operational phenomenon.
Open official record
Comparable public statistics showing the actual median interval between vulnerability disclosure, internal detection, patch availability and verified deployment across major European banks remain unavailable, preventing a defensible quantitative comparison of defensive latency between Italy, France, Germany and the United Kingdom.
Public supervisory reporting likewise does not yet provide sufficiently harmonised evidence on the proportion of bank production environments capable of automated patching, hot-patching, automated rollback, AI-assisted remediation or machine-speed containment, meaning that the degree to which the European banking sector has already adapted to the compressed defensive cycle cannot be established from the official record.
Finally, the public record does not establish how rapidly advanced offensive cyber capabilities will diffuse from restricted frontier systems into cheaper or open-weight models, and this diffusion rate remains one of the most consequential variables determining whether the present challenge develops primarily into a sustained operational burden or into a materially larger systemic cyber threat.
Cybersecurity is Becoming a Balance-Sheet and Systemic-Resilience Issue
BLUF (Bottom Line Up Front): Financial-sector cybersecurity has transcended IT compliance to become a core balance-sheet and systemic-stability variable. Digital interdependence creates transmission channels where operational disruption migrates into liquidity stress, payment gridlocks, and capital degradation. Operational risk capital requirements reached 13.4% of total bank capital in late 2025, while the first DORA dataset recorded 3,383 major ICT incidents (~33% cross-border impact, ~10% cyber-related). Coupled with cloud concentration (AWS, Google, Microsoft, IBM) and IMF loss estimates reaching up to $2.2B–$2.5B in severe outcomes, cyber resilience now demands integrated prudential oversight, ecosystem-wide dependency mapping, and continuous operational recovery.
Operational Risk Capital Architecture and Prudential Weightings
Op Risk Capital Weightings
Operational-risk capital requirements reached 13.4% of total capital requirements at the end of 2025 (up from 10.6% in Dec 2024), making operational risk the second-largest component of banks' risk weightings after credit risk, directly embedding digital resilience into prudential architecture.
DORA Cross-Border Propagation
The first DORA dataset recorded 3,383 major ICT incidents, with ~33% exhibiting cross-border impact. Only ~10% were malicious cyber incidents, proving that software failures, cloud outages, and configuration errors generate systemic risks equal to cyberattacks.
Liquidity Stress & Cyber Runs
A major cyber incident can trigger liquidity stress before solvency is threatened. IMF findings reveal persistent deposit outflows after cyber events, with 25% wholesale withdrawals pushing ~20% of global banks below LCR thresholds.
Table 1: Prudential Transmission Channels & Empirical Data
Controlling quantitative findings from the EBA, ESAs DORA Report, IMF Global Financial Stability Report, and ECB Target Incident Post-Mortem.
| Transmission Channel | Verified Empirical Metric | Operating Scope & Context | Controlling Authority | Prudential Significance |
|---|---|---|---|---|
| Op Risk Capital Share | 13.4% of total capital (End 2025; up from 10.6% in 2024) | EBA Risk Assessment Report (June 2026). | European Banking Authority | Makes operational risk the second-largest risk weighting after credit risk. |
| DORA Major Incidents | 3,383 major incidents (~33% cross-border; ~10% cyber) | First annual DORA report (June 2026). | EBA / EIOPA / ESMA | Proves system failures and operational outages drive systemic disruption alongside cyber. |
| IMF Severe Cyber Loss | Up to $2.5 billion in severe-event models | Global Financial Stability Report (April 2024). | International Monetary Fund | Demonstrates that extreme losses can threaten bank liquidity and solvency. |
| Critical Third-Party List | Designated providers (AWS, Google, Microsoft, IBM, etc.) | ESA designation under DORA (November 2025). | European Supervisory Authorities | Extends direct European regulatory oversight to non-bank technology infrastructure. |
| Italy Third-Party Share | 70% cyber / 48% op incidents involved third parties (H1 2025) | Banca d'Italia Financial Stability Report No. 1 (2026). | Banca d'Italia | Empirically establishes heavy external supplier involvement in Italian bank incidents. |
| UK Systemic Risk Survey | 82% ranked cyber among top 5 systemic risks; 26% as largest | 2026 H1 Systemic Risk Survey. | Bank of England | Reflects market consensus viewing cyber as second only to geopolitics in systemic threat. |
Table 2: National Supervisory Lenses & Systemic Surveillance (IT, FR, DE, UK)
Comparing regulatory approaches, supervisory priorities, and institutional coordination across core European markets.
| Jurisdiction | Key Supervisory Body | Supervisory Focus & Initiatives | Empirical Evidence / Finding | Systemic Policy Objective |
|---|---|---|---|---|
| ITALY | Banca d'Italia | Strategic Plan 2026–2028; cyber resilience of central bank, payments, and market infrastructure. | 70% of cyber incidents involved third-party providers in H1 2025. | Bridging internal operational risk with external supplier oversight. |
| FRANCE | ACPR / Banque de France / ANSSI | Work Programme 2026; DORA compliance, outsourcing, AI supervision, July 2026 ANSSI agreement. | Almost all supervised banks and insurers have AI in production. | Integrating cyber risk with European technological sovereignty and macro supervision. |
| GERMANY | BaFin / Deutsche Bundesbank | National supervisory programme 2026–2028; multi-client provider concentration reviews. | High reliance on shared multi-client ICT and service infrastructure across decentralized banking sector. | Mapping hidden fourth-party dependencies and shared multi-client risks. |
| UNITED KINGDOM | Bank of England / FCA / HM Treasury | Operational resilience framework; HM Treasury report on cyber resilience as productive capital. | 82% of survey respondents rank cyber among top 5 systemic financial risks. | Treating resilience as balance-sheet capital and addressing critical infrastructure risks. |
Deep Structural Breakdown: Core Systemic Transmission Vectors
Deconstructing how operational disruption migrates across payment networks, settlement infrastructure, and cloud dependencies.
The Cyber Run & Liquidity Stress
An institution can remain solvent while suffering severe liquidity drainage if depositors or institutional counterparties lose confidence in transaction execution. IMF modeling shows 25% wholesale withdrawals push ~20% of sampled banks below LCR thresholds, bridging cyber with treasury management.
Infrastructure Coupling (T2 / T2S)
The February 2025 TARGET outage demonstrated that cash payments, securities settlement, and collateral transfers are operationally coupled. Interruption of one platform simultaneously halts connected financial functions, creating systemic gridlock across otherwise sound institutions.
Micro-Macro Divergence (Cloud)
Individual banks reduce operational risk by migrating to major cloud providers (AWS, Google, Microsoft), but collectively the banking system becomes dangerously concentrated. This microprudential-macroprudential divergence necessitates direct EU-level oversight of critical ICT providers via DORA.
Forensic Strategic Key Judgments
Definitive analytical assessments derived from prudential data, DORA supervisory filings, and financial stability reports.
Cyber Risk is Now Embedded in Prudential Capital
Operational risk capital requirements reached 13.4% of total capital in 2025, confirming that digital resilience directly governs bank loss absorption and capital allocation.
Operational Outages Drive Systemic Disruption
With only ~10% of DORA's 3,383 major incidents categorised as malicious cyber, software failure and cloud outages are proven primary drivers of systemic risk.
Liquidity Vulnerability Precedes Solvency Risk
Cyber incidents trigger rapid deposit outflows ("cyber runs") that can drain liquidity buffers and breach LCR requirements before capital solvency is threatened.
DORA Extends Oversight to Technology Infrastructure
Designating critical third-party providers (AWS, Microsoft, Google, Bloomberg) brings non-bank technology suppliers directly into European prudential oversight.
Capital Alone Cannot Resolve Operational Failure
Financial buffers cannot restore corrupted databases or broken cloud connections; operational substitutability and technical continuity are mandatory.
Cybersecurity is a System-Wide Public Good
Individual banks underinvest in contagion prevention because they capture only private benefits, justifying prudential mandates that internalize systemic stability.
Open Official Record Gaps
- Concentration Topology Maps: Absence of fully public Union-wide maps detailing which specific banks depend on particular cloud regions and fourth-party suppliers.
- Incident-to-Balance-Sheet Linkage: Lack of harmonized official data linking major ICT incidents directly to intraday liquidity usage and emergency central bank lending.
- Cyber Insurance Risk Transfer: Incomplete public data on the degree to which insured recovery genuinely offsets extreme operational losses across European banking groups.
- Substitutability Metrics: Unquantified official metrics measuring how quickly critical financial functions can migrate away from a failed major cloud provider.
Observable Watch Indicators (Horizon 2026–2031)
Cybersecurity is becoming a balance-sheet and systemic-resilience issue
Principal judgment
The most consequential change in financial-sector cybersecurity is no longer confined to the probability that an individual bank suffers a direct technological loss, because digital interdependence has created transmission mechanisms through which a severe ICT or cyber event can migrate from an operational disturbance into funding pressure, liquidity stress, interrupted payment and securities settlement, collateral-management disruption, operational losses, regulatory capital consequences, depositor concern and wider deterioration in confidence, meaning that cybersecurity increasingly belongs inside the same strategic discussion as capital adequacy, liquidity management, recovery planning and financial stability rather than remaining principally within the information-security function.
The scale of this transition is becoming visible in prudential data, because the European Banking Authority's Risk Assessment Report — June 2026 states that operational-resilience risks have become increasingly systemic and reports that operational-risk capital requirements represented 13.4% of total capital requirements at the end of 2025, compared with 10.6% in December 2024, making operational risk the second-largest component of banks' risk weightings after credit risk; this does not mean that the entire increase was caused by cyber incidents, because operational risk incorporates a substantially broader universe of events, but it demonstrates that technology-dependent operational resilience is now embedded inside the prudential architecture through which banks absorb losses and allocate scarce capital.
The emerging systemic issue is therefore not simply whether a particular institution can withstand a cyberattack, but whether the financial system can continue transferring money, securities and collateral when multiple institutions depend simultaneously on the same cloud platforms, telecommunications networks, software products, data providers, cybersecurity services, payment infrastructures or outsourced technology operators, because failures affecting such common dependencies can generate correlated operational losses that diversification across banks does not eliminate.
That distinction matters for financial stability because conventional prudential architecture is primarily designed around financial contagion transmitted through credit exposures, funding structures, market prices and liquidity positions, whereas technology creates another topology of contagion in which institutions that possess no substantial financial exposure to one another can nevertheless fail simultaneously because they depend on the same external digital infrastructure.
The first European DORA dataset confirms that operational disruption is already cross-border
The first comprehensive EU-wide evidence produced under the Digital Operational Resilience Act materially strengthens the case for analysing digital risk at system level, because the European Supervisory Authorities' first annual report on major ICT-related incidents — June 2026 records 3,383 major ICT-related incidents reported by financial entities under the harmonised DORA framework and states that approximately one third had cross-border impact, illustrating that digital incidents already propagate across national and organisational boundaries rather than remaining confined to the institution at which they originate.
The same dataset is analytically important because only approximately 10% of the reported major ICT incidents were categorised as cybersecurity-related, while system failures and external events constituted the principal drivers, which means that systemic digital resilience cannot rationally be constructed around malicious intrusion alone and must instead address the broader possibility that software failure, infrastructure outage, provider malfunction, configuration error or dependency failure produces economic consequences similar to those of a deliberate attack. ESAs publish the first report on DORA major ICT-related incidents — EBA/EIOPA/ESMA — Jun 2026
This distinction fundamentally changes how bank boards should understand cyber resilience, because the economically relevant variable is not the intent of the originating event but whether the event removes access to a critical service, corrupts data, prevents transactions from settling, interrupts liquidity transfers, disables customer authentication or renders a financial institution unable to determine with confidence which transactions remain valid.
The systemic risk therefore resides in functional interruption, not exclusively in hostile penetration, which explains why modern prudential frameworks increasingly use the broader language of digital operational resilience rather than relying on cybersecurity as the sole organising concept.
Cyber losses can reach the income statement before they reach the solvency ratio
Cybersecurity becomes a balance-sheet issue through several distinct channels, beginning with direct operational losses such as theft, fraud, system reconstruction, forensic investigation, customer compensation, legal expenditure, regulatory penalties and emergency technology procurement, before extending into indirect losses generated by interrupted business activity, higher funding costs, reputational deterioration and accelerated investment requirements.
The IMF Global Financial Stability Report — April 2024, Chapter 3 estimated that financial firms had reported almost US$12 billion in direct cyber losses since 2004, including approximately US$2.5 billion between 2020 and 2023, while explicitly warning that reported figures materially understate total economic damage because indirect losses such as lost business, reputational harm and subsequent security expenditure are much more difficult to observe and are frequently excluded from incident-loss datasets.
The IMF's extreme-loss analysis is more important for prudential purposes than the average event because the distribution of cyber losses is highly skewed, with the April 2024 Global Financial Stability Report estimating maximum annual losses for financial firms of approximately US$152 million in a median year and as much as US$2.2 billion in a one-in-ten-year outcome, while its broader cross-sector modelling produces a severe-event estimate of approximately US$2.5 billion, a scale that the IMF notes can threaten the liquidity or solvency of an affected firm depending on its size and financial condition.
These figures should not be interpreted as forecasts for any particular European bank, because the estimates derive from historical cross-country incident data and extreme-value modelling rather than institution-specific scenarios, but they demonstrate why treating cyber expenditure purely as administrative overhead misclassifies the economic nature of the exposure: a major cyber event can generate losses large enough to influence earnings, provisioning, capital planning and in extreme circumstances solvency itself.
Operational risk is already inside the prudential capital architecture
The connection between digital disruption and prudential capital is not merely conceptual because the Basel framework defines operational risk as the risk of loss resulting from inadequate or failed internal processes, people and systems or from external events, explicitly including legal risk, which places many financially measurable consequences of severe cyber or ICT incidents within the operational-risk perimeter used for bank capital purposes. Basel Framework — OPE10 Definitions and application — Bank for International Settlements
Under the Basel standardised approach, operational-risk capital requirements are calculated using a financial-statement-based Business Indicator together with the applicable regulatory methodology, while operational-risk risk-weighted assets equal 12.5 times the operational-risk capital requirement, which means that significant operational losses and the underlying scale of a bank's business are linked directly to the prudential framework rather than existing outside the balance-sheet architecture. Basel Framework — Calculation of RWA for operational risk — Bank for International Settlements
The strategic implication is that the economic cost of inadequate digital resilience cannot be assessed solely through annual cybersecurity expenditure, because operational failures can influence a bank through several simultaneous channels, including immediate P&L losses, future remediation expenditure, supervisory measures, litigation, customer compensation, increased liquidity requirements and capital allocation, while indirect effects can impair revenues or increase the cost of funding without appearing initially under a narrow technology-loss category.
Cyber resilience therefore increasingly resembles loss-absorbing infrastructure, because investment made before an incident is economically analogous to expenditure intended to reduce the frequency or severity of future operational losses, while failure to invest can crystallise simultaneously through accounting, liquidity and capital channels after a severe event.
A cyber incident can become a liquidity event before it becomes a solvency event
The most important bridge between cybersecurity and conventional banking stability is depositor behaviour, because a financial institution can remain economically solvent while experiencing severe liquidity pressure if customers or institutional counterparties become uncertain about whether they can access funds, execute payments or trust account information following a major operational or cyber incident.
The IMF Global Financial Stability Report — April 2024 identifies precisely this transmission mechanism, concluding that a severe cyber event can produce a “cyber run” when depositors withdraw funds because they fear interruption of transactions, loss of access or deterioration in the viability of the targeted institution, and the IMF's empirical work found modest but persistent deposit outflows after cyber incidents at US banks, with smaller institutions experiencing cumulative retail and wholesale deposit declines of approximately 5% over six quarters following an incident.
The IMF also tested how much deposit outflow would be required to push large banks below the 100% Liquidity Coverage Ratio requirement, finding substantial variation across a sample of 80 global banks and estimating that a 25% wholesale-deposit outflow would push roughly 20% of the sampled institutions below the threshold, while an equivalent retail-deposit outflow would do so for approximately 60%, although these are scenario calculations rather than observations of actual cyber-induced runs and therefore should be interpreted as measures of sensitivity rather than expected outcomes. Global Financial Stability Report, Chapter 3 — IMF — Apr 2024
The mechanism becomes especially powerful in digital banking because deposits can move rapidly while information about an incident can spread almost instantly, meaning that a cyber event capable of disrupting transactions or creating uncertainty around account integrity can potentially generate a liability-side response much faster than the affected institution can explain the underlying technical problem to the market.
Cyber resilience consequently intersects directly with treasury and liquidity management, because the institution must prepare not only to restore technology but also to maintain adequate liquidity under circumstances in which operational disruption and confidence deterioration occur simultaneously.
Market confidence can transmit operational uncertainty faster than verified losses
A severe digital incident does not need to destroy financial assets in order to generate systemic consequences, because uncertainty concerning the integrity of balances, payments, securities positions or customer information can itself cause market participants to reduce exposures, delay transactions or move liquidity toward institutions perceived as safer.
The IMF Global Financial Stability Report — April 2024 identifies loss of confidence, disruption of critical services and technological and financial interconnectedness as the three principal transmission channels through which a sufficiently severe cyber incident could threaten macrofinancial stability, while emphasising that no cyber incident observed in its historical dataset had yet become fully systemic; this qualification remains important because systemic cyber risk is supported by identifiable transmission mechanisms even though the extreme outcome has not yet been observed at the scale contemplated in supervisory scenarios.
The practical implication is that communications capacity becomes part of financial resilience, because markets and customers need credible information about whether deposits remain accessible, transaction records remain accurate, payments are being queued or rejected, liquidity positions are known and critical services are recoverable, with ambiguity itself potentially increasing defensive withdrawals or market disengagement.
This produces a distinctive cyber-financial feedback loop in which technological uncertainty can generate financial behaviour, financial behaviour can increase liquidity pressure, and the resulting liquidity pressure can make a technically manageable incident economically more difficult to contain.
Payments transform local disruption into network disruption
Payment systems are the most direct mechanism through which an operational event at one institution can affect numerous unrelated counterparties, because payments represent both a financial obligation and an information message whose successful settlement depends on several interconnected technological and institutional layers operating correctly.
The European Central Bank explicitly characterises T2 as a systemically important payment system and warns that, because of its cross-system and cross-participant interdependencies, failure in T2 can spread across financial markets and potentially produce systemic implications beyond the euro area, which is why the service is supported by a multi-region, multi-site continuity architecture rather than treated as an ordinary technology platform. T2 business continuity management — European Central Bank
The systemic significance of these dependencies was demonstrated by an operational rather than cyber event on 27 February 2025, when a hardware failure caused T2 to become unavailable for approximately 10 hours, T2S for approximately eight hours, and TIPS to experience partial disruption for roughly one hour, suspending payment processing, securities settlement instructions, ancillary-system settlement and liquidity transfers between TARGET Services for several hours. TARGET Services incident of 27 February 2025 — Post-mortem Report — European Central Bank
The incident was not publicly attributed to malicious cyber activity and should not be represented as such, yet analytically it is highly valuable because it demonstrates the transmission geometry that a successful cyber event affecting equivalent infrastructure could exploit: interruption of one technical component can simultaneously stop cash payments, securities settlement and liquidity transfers even when individual participating banks remain financially sound.
The ECB subsequently identified 20 corrective measures following the incident, including replacement of the failed component, review of business-continuity and IT-service-continuity arrangements and assessment of how effectively extended cut-off times protected market participants during a prolonged outage, demonstrating that resilience of financial infrastructure is evaluated not only according to whether failure occurs but according to whether the surrounding financial system possesses credible mechanisms to absorb the resulting delay. ECB Annual Report 2025 — European Central Bank
Securities settlement creates a second transmission channel through collateral and market positions
The systemic consequences of an ICT failure become more complex when securities settlement is interrupted because securities transactions affect not only ownership transfer but also collateral availability, funding arrangements, margin obligations and the capacity of institutions to complete other transactions whose settlement depends on receipt of cash or securities earlier in the chain.
The February 2025 TARGET incident therefore illustrates more than payment interruption, because simultaneous unavailability of T2 and T2S temporarily suspended both high-value payments and securities settlement together with liquidity transfers between TARGET Services, demonstrating how apparently separate financial functions can become operationally coupled through shared infrastructure. TARGET Services incident of 27 February 2025 — Post-mortem Report — ECB
This interdependence means that cyber resilience at financial-market infrastructures must be understood in terms of transaction chains rather than individual platforms, because the economic consequence of disabling one settlement process depends on the downstream obligations that cannot be completed when the expected cash, collateral or securities movement fails to occur.
An institution can therefore experience liquidity pressure without suffering a direct cyber compromise if a critical counterparty, central securities depository, payment system or common service provider becomes unavailable, making digital operational resilience a network characteristic rather than a property that any one bank can achieve independently.
Clearing infrastructure concentrates operational consequences
Central counterparties constitute another important concentration point because they stand between large numbers of buyers and sellers, manage collateral and margin flows, and increasingly support markets in which centrally cleared transactions represent a large share of overall activity, meaning that their operational continuity has direct implications for market liquidity and counterparty-risk management.
The Bank for International Settlements' August 2026 assessment of central counterparties states that CCPs are increasingly dependent on a relatively limited population of critical third-party technology providers, including cloud services, cybersecurity companies and specialised software vendors, and warns that this dependence can create single points of failure for the financial system when multiple infrastructures rely on the same provider.
The systemic importance of these dependencies arises from their timing characteristics, because a service interruption during a period of market stress can interfere with the calculation, communication or settlement of margin obligations precisely when collateral movements and liquidity transfers are most urgent, potentially forcing market participants to conserve liquidity or reduce activity at the same moment that the financial system requires them to continue intermediating risk.
Cyber risk therefore interacts with market risk through operational infrastructure: an event that begins with data or technology can ultimately affect margining, liquidity demand, asset sales and trading behaviour even when no underlying financial asset has been directly destroyed.
Cloud concentration creates a form of common exposure that traditional bank ratios do not show
Perhaps the most important structural development is the migration of critical financial workloads toward a relatively concentrated group of external technology providers, because this produces an exposure that does not appear naturally in conventional balance-sheet ratios yet can affect multiple institutions simultaneously.
The Basel Committee has explicitly described this as a new supervisory problem, noting that many institutions increasingly depend on the same core service providers, cloud platforms, payment rails, data vendors and cybersecurity tools, thereby creating common exposures whose significance must be assessed at ecosystem level rather than solely institution by institution. Issues and challenges in banking supervision in the digital era — BIS — Mar 2026
This type of concentration differs fundamentally from an ordinary bilateral outsourcing relationship because each individual bank may rationally conclude that purchasing services from a major cloud or technology provider improves its own resilience, cost efficiency and technological quality, while the financial system collectively becomes more dependent on the continued functioning of the same supplier.
The result is a microprudential–macroprudential divergence in which a decision that reduces operational risk for one bank can increase common-mode risk for the system when many institutions make the same decision, making third-party concentration one of the clearest examples of why cybersecurity investment cannot be evaluated solely from the perspective of the individual financial institution.
DORA has converted technology suppliers into objects of systemic oversight
The European Union has begun responding directly to this problem through DORA's critical ICT third-party provider framework, under which technology companies considered sufficiently important to the financial sector can be subjected to direct European oversight even though they are not banks, insurers or investment firms.
On 18 November 2025, the European Supervisory Authorities published the first Union-level list of designated critical ICT third-party providers after collecting financial institutions' registers of contractual ICT arrangements and conducting a criticality assessment based on systemic importance, support for critical or important financial functions and substitutability. The European Supervisory Authorities designate critical ICT third-party providers under DORA — EBA/EIOPA/ESMA — Nov 2025
The resulting official list includes major infrastructure, cloud, software, data and technology providers such as Amazon Web Services EMEA, Google Cloud EMEA, Microsoft Ireland Operations, IBM, Oracle Nederland, SAP, Deutsche Telekom, Orange, Equinix, Accenture, Capgemini, Kyndryl, LSEG Data and Risk and Bloomberg, among others, demonstrating that the European supervisory perimeter now explicitly extends toward the non-bank technology infrastructure on which financial services increasingly depend. List of designated Critical ICT Third-Party Providers — European Supervisory Authorities — Nov 2025
Under the DORA oversight framework, the European Supervisory Authorities acting as Lead Overseers can request information, conduct investigations and on-site inspections, issue recommendations and apply the dedicated oversight architecture through Joint Examination Teams, which represents a significant institutional shift because systemic resilience is no longer pursued only by regulating the financial institution purchasing the technology but also by examining the technology provider creating the concentration. DORA oversight — European Banking Authority
Concentration risk can exist several layers below the contractual relationship
Direct provider concentration is only the visible part of the problem because a bank can diversify its immediate technology vendors while those vendors themselves rely on the same cloud platform, data centre, telecommunications operator, authentication provider or software component, creating hidden concentration below the contractual layer that the financial institution directly manages.
The Deutsche Bundesbank has explicitly warned that actual third-party concentration risk can be greater than it initially appears because ICT providers themselves can subcontract to the same critical providers and because technology supply chains are not always sufficiently visible, meaning that a diversified procurement strategy can produce illusory diversification when several apparently independent vendors share the same underlying infrastructure. DORA from the perspective of on-site inspections — Deutsche Bundesbank
This creates a major analytical challenge because conventional vendor-management systems are usually structured around contractual counterparties rather than full technical dependency graphs, while the economic transmission of an outage follows the underlying infrastructure rather than the legal contract.
Systemic resilience therefore increasingly depends on identifying fourth-party and nth-party dependencies, particularly where services supporting payments, market connectivity, identity, cybersecurity, data processing or core banking applications ultimately converge on the same infrastructure provider.
Cybersecurity expenditure possesses characteristics of a system-wide public good
A further reason market incentives alone may produce insufficient investment is that security expenditure by one institution can benefit other institutions connected to it, while the investing bank does not capture the entire value generated by the reduction in contagion risk.
A Bank for International Settlements working paper published in May 2026 examining evidence from the ECB's 2024 cyber-resilience stress test characterises cybersecurity investment within financial networks as possessing features of a public good, because stronger protection by an individual bank improves not only that institution's resilience but also the resilience of institutions connected to it, creating a theoretical possibility of system-wide underinvestment when banks evaluate expenditure exclusively according to private costs and benefits.
This observation gives prudential intervention an economic justification beyond ordinary consumer protection, because supervisory requirements can compel institutions to internalise part of the systemic benefit that private budgeting processes might otherwise undervalue.
Cybersecurity investment therefore belongs partly within macroprudential policy because the social cost of a severe technology failure can exceed the loss absorbed by the institution where the failure originated, particularly when payments, market infrastructure or common service providers transmit disruption to other firms.
The banking sector can import cyber risk from outside finance
An additional source of systemic vulnerability arises because financial institutions depend heavily on critical infrastructure sectors whose resilience lies partly outside financial supervision, particularly telecommunications, energy, internet infrastructure and large technology platforms.
The Bank of England's July 2026 Financial Stability Report explicitly identifies this channel, warning that disruption at telecommunications providers, common software components, managed service providers or other critical sectors can transmit operational stress simultaneously to multiple financial institutions even when those banks themselves have not been directly compromised.
This cross-sector exposure complicates traditional prudential planning because a bank can maintain strong capital, liquidity and internal security controls while remaining dependent on electrical power, telecommunications connectivity, digital identity services or cloud capacity that it cannot restore independently.
Cyber systemic risk must consequently be treated partly as critical-infrastructure risk, requiring coordination between financial supervisors, national cybersecurity authorities, central banks, telecommunications authorities and technology providers rather than reliance exclusively on bilateral supervision of banks.
The real systemic event may be a simultaneous loss of access rather than a simultaneous financial loss
Financial contagion is traditionally imagined as institutions suffering financial losses at roughly the same time, yet digital concentration creates another systemic scenario in which many institutions remain economically solvent but temporarily lose the ability to transact, reconcile positions, access market infrastructure or prove the integrity of critical information.
This distinction is important because financial buffers cannot repair corrupted databases, restore telecommunications connectivity or recreate an unavailable cloud service, an observation explicitly made by the Deutsche Bundesbank, which notes that while liquidity or solvency stress can be mitigated with financial buffers or established sector mechanisms, ICT disruption cannot be resolved through capital alone and instead requires technical and organisational continuity measures capable of restoring operations. DORA from the perspective of on-site inspections — Deutsche Bundesbank
Capital therefore remains necessary but becomes insufficient, because an institution can satisfy every prudential capital ratio while being operationally incapable of processing a payment, accessing collateral information or confirming customer balances.
The conceptual shift is profound: systemic resilience in digital finance increasingly requires operational substitutability alongside financial loss absorption, because economic continuity depends on whether critical functions can move to alternative systems, providers, sites or communication channels when the primary infrastructure fails.
Italy: third-party involvement is already visible in supervisory incident data
Italy provides unusually useful official evidence of the third-party transmission problem because the Banca d'Italia Financial Stability Report No. 1 — 2026 presents granular supervisory incident data showing substantial third-party involvement across both cyber and operational events, while explicitly identifying technological supply chains and dependencies on global IT and cloud providers as a principal area of systemic operational analysis.
During the first half of 2025, according to the Bank's supervisory reporting data, 70% of major cyber incidents involved third-party service providers, while the corresponding share for operational incidents was 48%; during the second half of 2025 the figures were 36% and 65% respectively, with the Bank cautioning that the 2025 data are reported under the new DORA framework and therefore are not perfectly comparable with earlier periods. Financial Stability Report No. 1 — Banca d'Italia — Apr 2026
These figures do not establish that outsourcing is inherently less secure than internal operation, nor do they measure the severity of every provider-related incident, but they demonstrate empirically that a large share of material Italian financial-sector disruption now involves infrastructure outside the immediate organisational perimeter of the affected intermediary.
Banca d'Italia accordingly describes cybersecurity as a financial-stability issue arising from dense technological interdependence and dependence on suppliers from other sectors, while its 2026-2028 Strategic Plan explicitly includes strengthening the cyber resilience of the central bank itself together with payment and market infrastructures. Cybersecurity for financial stability — Banca d'Italia Strategic Plan 2026-2028 — Banca d'Italia
France: cyber risk is being integrated with outsourcing, liquidity and system-wide supervision
France's supervisory response similarly indicates that operational resilience is being absorbed into the wider prudential framework rather than treated as an isolated technical discipline, because the ACPR Work Programme for 2026 places DORA implementation, cyber and operational risk, outsourcing oversight and business-model resilience within the same supervisory agenda that examines market risk, sovereign exposure, profitability, solvency and liquidity.
The ACPR has identified incident management, ICT-risk frameworks and contractual compliance with technology providers as the three principal ICT supervisory priorities for 2026 and has stated that institutions most exposed to these risks will be targeted through strengthened supervision and on-site inspections, while outsourced functions and technological dependencies will also be examined through the broader lens of business-model sustainability. ACPR Work Programme 2026 — Autorité de contrôle prudentiel et de résolution
France has additionally strengthened institutional coordination through the agreement signed on 3 July 2026 between ANSSI, the Banque de France and the ACPR to reinforce information exchange and cooperation in information-system security, illustrating the growing recognition that systemic financial cyber risk cannot be managed entirely inside the prudential-supervision perimeter. ANSSI, ACPR and Banque de France cooperation agreement — ACPR — Jul 2026
Germany: concentration among multi-client service providers is an explicit supervisory priority
Germany's 2026 supervisory programme is especially explicit about the structural concentration problem because BaFin and the Deutsche Bundesbank identify growing technological dependence on a limited number of service providers and the increasing outsourcing of material IT activities as major supervisory concerns, with particular attention directed toward concentrations involving cloud providers and multi-client technology suppliers. National supervisory programme 2026-28 — Deutsche Bundesbank
This is particularly important in the German banking structure, where many institutions can rely on shared or multi-client technology environments, meaning that a supplier can become economically systemic even without appearing on any bank's balance sheet as a large conventional counterparty.
The German supervisory position therefore emphasises identification of cyber and IT risk together with concentration at third-party providers, thematic DORA reviews at selected institutions and technology suppliers, and risk-oriented remediation of identified weaknesses, indicating that supervisory attention is moving toward the network architecture surrounding banks rather than examining only the security controls located within each regulated entity. Nationales Aufsichtsprogramm 2026-2028 — Deutsche Bundesbank/BaFin
United Kingdom: market participants already classify cyberattack as a leading systemic risk
The United Kingdom offers unusually direct evidence that cyber risk is already perceived by financial-market participants in systemic rather than merely institutional terms, because the Bank of England's 2026 H1 Systemic Risk Survey found that 82% of respondents identified cyberattack among the five risks they believed would have the greatest impact on the UK financial system if realised, while 26% identified cyberattack as the single largest risk, making it second only to geopolitical risk in the survey.
Operational risk was separately identified among the top five risks by 35% of respondents, while risks associated with artificial intelligence were cited by 32%, indicating that market participants increasingly distinguish several technologically mediated threat categories rather than subsuming them into a single cybersecurity label. Systemic Risk Survey Results — 2026 H1 — Bank of England
The Bank of England's policy analysis therefore places increasing emphasis on correlated disruption across common providers, software and critical infrastructure rather than considering severe cyber losses exclusively at individual firms, because a system dominated by shared dependencies can experience simultaneous interruption even when every institution individually maintains substantial capital and sophisticated internal controls. Financial Stability Report — July 2026 — Bank of England
Europe is moving from entity supervision toward ecosystem supervision
The cumulative regulatory response suggests that Europe is gradually moving beyond an institution-by-institution conception of financial cybersecurity toward what can reasonably be described as ecosystem supervision, in which authorities attempt to understand how critical financial functions depend on technology providers, market infrastructures, subcontractors, cloud platforms and other sectors whose failure can affect multiple regulated entities simultaneously.
DORA provides the clearest institutional embodiment of this change through harmonised major-incident reporting, mandatory registers of ICT contractual relationships, critical-provider designation and direct European oversight of systemically important technology suppliers, while national supervisors are increasingly using those mechanisms to construct dependency maps rather than merely reviewing individual outsourcing contracts. Digital Operational Resilience Act — European Banking Authority
The significance of this approach is that systemic cyber risk becomes observable in ways traditional prudential reporting cannot capture, because two banks may appear independently diversified according to assets, liabilities and counterparties while remaining operationally concentrated on the same cloud region, software vendor or managed-service platform.
A future macroprudential cyber framework will therefore increasingly need to measure common digital dependencies alongside common financial exposures, because concentration that cannot be seen cannot be subjected to credible stress testing, substitution planning or crisis management.
The balance sheet must be considered together with the service map
Traditional bank resilience starts from the balance sheet because capital absorbs losses and liquidity enables obligations to be met, yet digital operational risk introduces a complementary requirement: supervisors and boards also need a precise map of the services whose continued functioning gives economic meaning to those financial resources.
A bank can possess adequate capital but remain unable to transfer money; it can possess adequate liquid assets but be unable to mobilise collateral; it can retain customer deposits but temporarily prevent customers from accessing them; and it can hold complete transaction records while lacking confidence that those records have not been altered, meaning that the solvency of the legal entity and the operational availability of the banking service are related but no longer interchangeable concepts.
The Basel Committee's consolidated Operational Risk and Resilience guidelines, published in 2026, reflect this distinction by treating operational resilience, operational-risk management and third-party risk as interconnected but separately governed prudential disciplines, illustrating that future banking stability requires both sufficient financial buffers and credible continuation of critical operations. Operational risk and resilience — Basel Committee on Banking Supervision — 2026
This means that a meaningful bank stress test increasingly requires two simultaneous questions: whether the institution can absorb the financial loss generated by a severe incident, and whether it can continue delivering economically critical services during the incident itself.
The decisive systemic vulnerability is common-mode failure
The evidence therefore supports a conclusion materially different from the earlier discussion of attack speed: the principal financial-stability threat is not simply that individual banks face more sophisticated cyber adversaries, but that the architecture of modern finance has created shared technological dependencies capable of disabling several institutions, infrastructures or markets through a single operational locus.
The European DORA incident dataset already shows meaningful cross-border propagation; Italian supervisory data demonstrate substantial third-party involvement in reported major incidents; German supervision identifies cloud and multi-client provider concentration as a priority; French supervision is integrating outsourcing and ICT risk into prudential governance; UK market participants already rank cyberattack among the most important systemic threats; and European authorities have formally placed major technology providers inside a direct oversight architecture. ESAs annual overview of DORA major ICT incidents — Jun 2026 National supervisory programme 2026-28 — Deutsche Bundesbank Systemic Risk Survey 2026 H1 — Bank of England
The economic implication is that cybersecurity investment cannot be judged exclusively according to whether it reduces expected direct losses at the individual institution, because resilience spending also reduces the probability that one institution transmits disruption to counterparties and infrastructures, while investment in redundancy, provider substitution and service continuity generates benefits extending beyond the bank financing those controls.
The prudential implication is equally important: capital absorbs financial losses, liquidity absorbs funding stress, but neither can substitute for the continued availability and integrity of the digital infrastructure through which modern banking operates, which means that cybersecurity, operational resilience and financial resilience must increasingly be designed as one integrated stability architecture.
Key judgments
The strongest new evidence is that cyber and ICT risk have already entered the prudential domain quantitatively rather than rhetorically, because operational-risk capital requirements accounted for 13.4% of total bank capital requirements at the end of 2025, while EU authorities received 3,383 reports of major ICT incidents under the first DORA-wide annual reporting cycle and approximately one third of those incidents produced cross-border effects. Risk Assessment Report — EBA — Jun 2026 ESAs annual report on major ICT incidents — Jun 2026
The most consequential transmission channel is likely to arise from common dependencies rather than simultaneous direct compromise, because many banks, market infrastructures and service providers depend on overlapping cloud, software, telecommunications and technology ecosystems that can convert one technical failure into simultaneous loss of functionality across otherwise financially independent institutions.
The principal balance-sheet channel is liquidity rather than immediate solvency, because evidence from the IMF indicates that cyber incidents can produce persistent deposit outflows and that significant deposit withdrawal scenarios can materially weaken Liquidity Coverage Ratios before an institution suffers losses large enough to threaten its capital position. Global Financial Stability Report — IMF — Apr 2024
The principal infrastructure channel runs through payments, settlement, collateral and clearing, because interruption of these services can transmit operational stress between institutions regardless of whether the initial event originates inside the regulated banking perimeter, as demonstrated by the February 2025 TARGET operational outage even though that particular event was not cyber-induced. TARGET Services incident post-mortem — ECB — Nov 2025
The principal policy development is the shift from supervising banks toward supervising financial technology ecosystems, with DORA's designation and direct oversight of critical ICT providers representing the clearest European institutional recognition that operational concentration outside regulated banks can nevertheless create systemic financial risk. DORA oversight — European Banking Authority
What would change the assessment
The assessment would weaken if several years of harmonised DORA data demonstrated that major ICT disruptions remained consistently local, that cross-border incidents rarely affected critical financial functions, that common-provider incidents produced negligible simultaneous disruption across clients, and that depositor and market behaviour remained largely insensitive to major technology outages, because those observations would indicate that current operational interdependence creates less systemic amplification than the institutional architecture presently assumes.
The assessment would strengthen substantially if DORA reporting identified an increasing proportion of incidents affecting multiple financial entities through the same supplier, if a major cloud, telecommunications or managed-service provider simultaneously interrupted critical functions at several banks, if payment or securities infrastructure suffered a cyber-induced outage comparable in duration or scope to the February 2025 TARGET operational disruption, or if a cyber incident at a significant institution produced measurable deposit withdrawal or wholesale-funding pressure.
A particularly important threshold would be a severe event in which institutions remained economically solvent yet became unable to process payments, settle securities or mobilise collateral for a sustained period, because such an event would demonstrate conclusively that modern systemic resilience can fail operationally even where traditional capital and liquidity metrics remain initially sound.
Open official record
The European public record still lacks a sufficiently granular Union-wide map showing which individual financial entities depend on which critical cloud regions, software platforms, identity providers, telecommunications networks and fourth-party suppliers, because DORA registers of information are primarily supervisory instruments rather than fully public datasets and therefore do not permit independent measurement of the complete European concentration topology.
The public record also lacks harmonised data linking major ICT incidents directly to deposit outflows, intraday liquidity usage, emergency central-bank liquidity, collateral mobilisation, payment delays, market spreads and capital impacts, preventing reliable estimation of how frequently a technological incident translates into measurable balance-sheet stress across European institutions.
Comparable European information on cyber insurance coverage, exclusions, deductibles, aggregate exposure and the degree to which insured recovery actually offsets severe operational losses remains similarly incomplete, making it impossible to determine from official public sources how much extreme cyber-loss risk has genuinely been transferred outside individual bank balance sheets.
Finally, authorities do not presently publish sufficiently detailed system-wide substitution metrics showing how quickly critical financial services could migrate away from a failed major cloud, communications or technology provider, meaning that substitutability rather than nominal provider count remains one of the most important unresolved variables in assessing the true systemic concentration of European digital finance.
Cybersecurity is Becoming a Balance-Sheet and Systemic-Resilience Issue
BLUF (Bottom Line Up Front): Financial-sector cybersecurity has transcended IT compliance to become a core balance-sheet and systemic-stability variable. Digital interdependence creates transmission channels where operational disruption migrates into liquidity stress, payment gridlocks, and capital degradation. Operational risk capital requirements reached 13.4% of total bank capital in late 2025, while the first DORA dataset recorded 3,383 major ICT incidents (~33% cross-border impact, ~10% cyber-related). Coupled with cloud concentration (AWS, Google, Microsoft, IBM) and IMF loss estimates reaching up to $2.2B–$2.5B in severe outcomes, cyber resilience now demands integrated prudential oversight, ecosystem-wide dependency mapping, and continuous operational recovery.
Operational Risk Capital Architecture and Prudential Weightings
Op Risk Capital Weightings
Operational-risk capital requirements reached 13.4% of total capital requirements at the end of 2025 (up from 10.6% in Dec 2024), making operational risk the second-largest component of banks' risk weightings after credit risk, directly embedding digital resilience into prudential architecture.
DORA Cross-Border Propagation
The first DORA dataset recorded 3,383 major ICT incidents, with ~33% exhibiting cross-border impact. Only ~10% were malicious cyber incidents, proving that software failures, cloud outages, and configuration errors generate systemic risks equal to cyberattacks.
Liquidity Stress & Cyber Runs
A major cyber incident can trigger liquidity stress before solvency is threatened. IMF findings reveal persistent deposit outflows after cyber events, with 25% wholesale withdrawals pushing ~20% of global banks below LCR thresholds.
Table 1: Prudential Transmission Channels & Empirical Data
Controlling quantitative findings from the EBA, ESAs DORA Report, IMF Global Financial Stability Report, and ECB Target Incident Post-Mortem.
| Transmission Channel | Verified Empirical Metric | Operating Scope & Context | Controlling Authority | Prudential Significance |
|---|---|---|---|---|
| Op Risk Capital Share | 13.4% of total capital (End 2025; up from 10.6% in 2024) | EBA Risk Assessment Report (June 2026). | European Banking Authority | Makes operational risk the second-largest risk weighting after credit risk. |
| DORA Major Incidents | 3,383 major incidents (~33% cross-border; ~10% cyber) | First annual DORA report (June 2026). | EBA / EIOPA / ESMA | Proves system failures and operational outages drive systemic disruption alongside cyber. |
| IMF Severe Cyber Loss | Up to $2.5 billion in severe-event models | Global Financial Stability Report (April 2024). | International Monetary Fund | Demonstrates that extreme losses can threaten bank liquidity and solvency. |
| Critical Third-Party List | Designated providers (AWS, Google, Microsoft, IBM, etc.) | ESA designation under DORA (November 2025). | European Supervisory Authorities | Extends direct European regulatory oversight to non-bank technology infrastructure. |
| Italy Third-Party Share | 70% cyber / 48% op incidents involved third parties (H1 2025) | Banca d'Italia Financial Stability Report No. 1 (2026). | Banca d'Italia | Empirically establishes heavy external supplier involvement in Italian bank incidents. |
| UK Systemic Risk Survey | 82% ranked cyber among top 5 systemic risks; 26% as largest | 2026 H1 Systemic Risk Survey. | Bank of England | Reflects market consensus viewing cyber as second only to geopolitics in systemic threat. |
Table 2: National Supervisory Lenses & Systemic Surveillance (IT, FR, DE, UK)
Comparing regulatory approaches, supervisory priorities, and institutional coordination across core European markets.
| Jurisdiction | Key Supervisory Body | Supervisory Focus & Initiatives | Empirical Evidence / Finding | Systemic Policy Objective |
|---|---|---|---|---|
| ITALY | Banca d'Italia | Strategic Plan 2026–2028; cyber resilience of central bank, payments, and market infrastructure. | 70% of cyber incidents involved third-party providers in H1 2025. | Bridging internal operational risk with external supplier oversight. |
| FRANCE | ACPR / Banque de France / ANSSI | Work Programme 2026; DORA compliance, outsourcing, AI supervision, July 2026 ANSSI agreement. | Almost all supervised banks and insurers have AI in production. | Integrating cyber risk with European technological sovereignty and macro supervision. |
| GERMANY | BaFin / Deutsche Bundesbank | National supervisory programme 2026–2028; multi-client provider concentration reviews. | High reliance on shared multi-client ICT and service infrastructure across decentralized banking sector. | Mapping hidden fourth-party dependencies and shared multi-client risks. |
| UNITED KINGDOM | Bank of England / FCA / HM Treasury | Operational resilience framework; HM Treasury report on cyber resilience as productive capital. | 82% of survey respondents rank cyber among top 5 systemic financial risks. | Treating resilience as balance-sheet capital and addressing critical infrastructure risks. |
Deep Structural Breakdown: Core Systemic Transmission Vectors
Deconstructing how operational disruption migrates across payment networks, settlement infrastructure, and cloud dependencies.
The Cyber Run & Liquidity Stress
An institution can remain solvent while suffering severe liquidity drainage if depositors or institutional counterparties lose confidence in transaction execution. IMF modeling shows 25% wholesale withdrawals push ~20% of sampled banks below LCR thresholds, bridging cyber with treasury management.
Infrastructure Coupling (T2 / T2S)
The February 2025 TARGET outage demonstrated that cash payments, securities settlement, and collateral transfers are operationally coupled. Interruption of one platform simultaneously halts connected financial functions, creating systemic gridlock across otherwise sound institutions.
Micro-Macro Divergence (Cloud)
Individual banks reduce operational risk by migrating to major cloud providers (AWS, Google, Microsoft), but collectively the banking system becomes dangerously concentrated. This microprudential-macroprudential divergence necessitates direct EU-level oversight of critical ICT providers via DORA.
Forensic Strategic Key Judgments
Definitive analytical assessments derived from prudential data, DORA supervisory filings, and financial stability reports.
Cyber Risk is Now Embedded in Prudential Capital
Operational risk capital requirements reached 13.4% of total capital in 2025, confirming that digital resilience directly governs bank loss absorption and capital allocation.
Operational Outages Drive Systemic Disruption
With only ~10% of DORA's 3,383 major incidents categorised as malicious cyber, software failure and cloud outages are proven primary drivers of systemic risk.
Liquidity Vulnerability Precedes Solvency Risk
Cyber incidents trigger rapid deposit outflows ("cyber runs") that can drain liquidity buffers and breach LCR requirements before capital solvency is threatened.
DORA Extends Oversight to Technology Infrastructure
Designating critical third-party providers (AWS, Microsoft, Google, Bloomberg) brings non-bank technology suppliers directly into European prudential oversight.
Capital Alone Cannot Resolve Operational Failure
Financial buffers cannot restore corrupted databases or broken cloud connections; operational substitutability and technical continuity are mandatory.
Cybersecurity is a System-Wide Public Good
Individual banks underinvest in contagion prevention because they capture only private benefits, justifying prudential mandates that internalize systemic stability.
Open Official Record Gaps
- Concentration Topology Maps: Absence of fully public Union-wide maps detailing which specific banks depend on particular cloud regions and fourth-party suppliers.
- Incident-to-Balance-Sheet Linkage: Lack of harmonized official data linking major ICT incidents directly to intraday liquidity usage and emergency central bank lending.
- Cyber Insurance Risk Transfer: Incomplete public data on the degree to which insured recovery genuinely offsets extreme operational losses across European banking groups.
- Substitutability Metrics: Unquantified official metrics measuring how quickly critical financial functions can migrate away from a failed major cloud provider.
Observable Watch Indicators (Horizon 2026–2031)
Europe now faces an investment and sovereignty decision
Principal judgment
Europe's next financial-security decision is fundamentally about capital allocation under conditions of strategic technological dependence, because banks and financial infrastructures are being required to digitalise more rapidly, deploy artificial intelligence, satisfy materially stronger resilience requirements and compete with technology-intensive global institutions while much of the computing capacity, cloud infrastructure, advanced processors, foundation-model ecosystem and enterprise software on which that transformation depends remains concentrated outside European strategic control; consequently, neither an indiscriminate retreat from non-European technology nor unrestricted technological dependence provides a sustainable solution, and the relevant objective is becoming controlled dependency through substitutability, portability, European capacity and credible exit options.
The policy environment has changed decisively during 2026, because the European Commission no longer describes technological sovereignty merely as an industrial aspiration but explicitly defines it as Europe's capacity to act independently in the digital sphere by developing and controlling critical technologies, data and infrastructure while reducing excessive reliance on non-EU suppliers, and on 3 June 2026 it placed that objective at the centre of a new technology-sovereignty package comprising the proposed Cloud and AI Development Act, the Chips Act 2.0, an EU Open Source Strategy and complementary initiatives intended to strengthen European digital capacity. Strengthening Europe’s Tech Sovereignty — European Commission
For the banking sector, however, sovereignty cannot sensibly mean technological autarky, because restricting institutions to European suppliers irrespective of security, performance, scale or functionality could weaken competitiveness and potentially reduce resilience, while continued dependence on a small number of externally controlled technology stacks without credible substitution creates strategic exposure to service interruption, extraterritorial legal requirements, contractual repricing, software discontinuation and geopolitical coercion; the decision facing Europe is therefore not foreign technology versus European technology, but which digital capabilities must remain under European control, which dependencies can safely remain international, and which critical services require technically and economically credible alternatives.
The investment problem is equally immediate because the opportunity to finance this transition exists at a moment when the euro-area banking sector remains comparatively profitable and well capitalised: statistics released by ECB Banking Supervision on 15 September 2026 show that significant institutions recorded an aggregate annualised return on equity of 10.73% in the second quarter of 2026, the highest value since the ECB series began in 2015, alongside a 16.00% Common Equity Tier 1 ratio and a cost-to-income ratio of 53.06%, its lowest recorded level in that series. ECB publishes supervisory banking statistics on significant institutions for the second quarter of 2026 — ECB Banking Supervision
Europe is therefore confronting the issue from a position in which many major banks possess the financial capacity to invest, making the strategic question less whether the sector can afford resilience investment than whether it will allocate current profitability toward architectures that remain controllable over a ten- or fifteen-year technological cycle rather than maximising short-term efficiency while accumulating dependencies whose future cost cannot easily be reversed.
Technological sovereignty must be defined as control rather than nationality
The concept of technological sovereignty becomes analytically useful only when separated from economic nationalism, because a technology does not automatically become resilient merely because its supplier is European, while a non-European technology does not automatically become unsuitable merely because ownership resides elsewhere; what matters for financial stability is whether the institution retains effective control over its data, cryptographic keys, workloads, interfaces, software dependencies, operational procedures and exit pathways under both ordinary and stressed conditions.
The proposed Cloud and AI Development Act — European Commission, June 2026 represents an important development precisely because it attempts to operationalise sovereignty rather than leave the concept undefined, establishing a proposed four-level assurance structure under which cloud and AI services would be evaluated according to increasingly demanding conditions concerning location, independence from third-country influence, ownership and control, transparency over software supply chains and freedom from external interference.
Under the Commission's proposed structure, the lowest level would establish that data are processed and stored inside the Union, while progressively stronger levels introduce requirements relating to independence from third countries, transparency across the software supply chain, EU ownership and control and, at the highest level, full supply-chain transparency combined with protection against third-country interference; the significance of this model is not that every financial workload should be placed at the highest sovereignty level, but that Europe is moving toward risk-proportionate sovereignty, in which the sensitivity and systemic significance of a workload determine the degree of autonomy required. Cloud and AI Development Act — European Commission
For banks, such an approach offers a more credible architecture than blanket localisation, because ordinary productivity applications could remain within internationally supplied environments while prudential data, cryptographic infrastructure, privileged security functions, transaction-critical workloads or strategic supervisory datasets could be subjected to progressively stronger requirements concerning control, reversibility and jurisdiction.
The key principle is therefore sovereignty by function, under which Europe identifies which capabilities cannot be allowed to depend on a single external point of control and designs investment accordingly.
Europe remains structurally dependent in the technologies it is asking banks to adopt
The urgency of the issue becomes clearer when Europe’s digitalisation objectives are compared with its industrial position, because the State of the Digital Decade 2026 acknowledges that substantial dependencies on non-EU providers persist across cloud services, cybersecurity and other strategic technologies, while the Union's share of the global semiconductor market remains approximately 9%, less than half the Digital Decade objective of 20%.
At the same time, European dependence on digital infrastructure is expanding rapidly rather than stabilising, with the same Commission assessment reporting that 46.7% of EU enterprises used cloud computing in 2026, 39.9% used data analytics, and nearly 20% had deployed AI, while AI adoption rose by approximately 48% during 2025 compared with the previous year. 2026 State of the Digital Decade package — European Commission
This creates a strategic contradiction at the centre of European digital policy: the Union needs faster adoption of AI and cloud technology to improve productivity and competitiveness, but every acceleration of adoption potentially deepens dependence on infrastructure in which European suppliers remain comparatively weak, meaning that digitalisation without industrial-capacity policy can increase strategic exposure at precisely the moment when regulation demands greater operational control.
For banks, the consequence is particularly acute because financial institutions cannot simply defer technology adoption without incurring competitive costs, yet deploying large-scale AI models, cloud-native infrastructure and advanced analytics frequently requires access to hardware, platforms and software stacks controlled by a small group of global suppliers, making procurement policy an increasingly important component of risk management.
Europe is beginning to spend at industrial rather than regulatory scale
The European response is no longer limited to imposing standards on private institutions because public policy has begun moving toward the creation of indigenous computing and AI capacity at a scale intended to influence the structure of the market itself.
The Commission's InvestAI initiative, launched in February 2025, is intended to mobilise €200 billion of investment in artificial intelligence, including a dedicated €20 billion facility for AI gigafactories, representing one of the largest coordinated attempts yet made to expand European AI infrastructure rather than merely regulate applications developed elsewhere. EU launches InvestAI initiative to mobilise €200 billion of investment in artificial intelligence — European Commission
That programme has moved beyond announcement, because on 30 July 2026 the Commission launched a call for up to seven AI Gigafactories, supported by as much as €10 billion in EU and national public funding and designed to unlock at least €20 billion of private investment, with each facility expected to combine advanced AI processors, software, cloud technology, high-speed connectivity and energy-efficient data-centre infrastructure. EU launches AI Gigafactories call — European Commission — Jul 2026
The scale of these facilities matters because the Commission describes AI gigafactories as infrastructure incorporating more than 100,000 advanced AI processors, placing the initiative in a category materially different from ordinary research funding and closer to industrial infrastructure policy. AI Factories — European Commission
The proposed Cloud and AI Development Act complements this approach with an objective of dramatically increasing European data-centre capacity, while the AI Continent Action Plan envisages tripling EU data-centre capacity over approximately five to seven years, illustrating that sovereignty is increasingly being pursued through physical computing capacity rather than through legal requirements alone. AI Continent Action Plan — European Commission
For the financial sector, this matters because a European AI and cloud ecosystem cannot become strategically credible unless it possesses sufficient scale to offer the performance, availability and economic efficiency required by banks, insurers and market infrastructures, meaning that the sovereignty debate ultimately turns on whether Europe can build alternatives that institutions choose because they are technologically competitive rather than because regulation obliges them to accept inferior solutions.
Public investment cannot substitute for private financial mobilisation
The scale of Europe's wider digital programme also reveals why banking and capital-market mobilisation is unavoidable, because Member States' updated Digital Decade roadmaps now contain 1,934 measures valued at approximately €289.3 billion, of which €205.9 billion derives from public budgets, yet the Commission warns that almost half of the public funding embedded in those roadmaps is expected to phase out by the end of 2026. 2026 State of the Digital Decade package — European Commission
This creates a financing transition in which Europe cannot expect Recovery and Resilience Facility-era public expenditure to sustain the digital transformation indefinitely, making bank lending, institutional investment, venture capital and deeper European capital markets increasingly important to financing data centres, cybersecurity companies, semiconductor projects, AI infrastructure and software firms.
The European Central Bank has connected these issues directly, with Christine Lagarde arguing on 14 September 2026 that artificial intelligence represents precisely the type of transformative project capable of driving European capital-market development because its financing requirements are too large to be met through public budgets or bank lending alone and require capital markets capable of allocating European savings toward high-risk, long-duration technological investment. A new age of capital: growth, sovereignty and AI — Christine Lagarde, ECB — Sep 2026
The sovereignty challenge is consequently also a financial-architecture challenge, because Europe cannot plausibly reduce dependence on foreign technology while leaving its own high-growth technology companies dependent on foreign capital markets for scale-up financing.
Bank cybersecurity expenditure must become strategic capital expenditure
The distinction between ordinary IT expenditure and resilience investment is increasingly artificial because the infrastructure choices that determine efficiency simultaneously determine strategic dependence, recoverability, portability and the institution's future bargaining power against suppliers.
Denis Beau of the Banque de France stated in September 2026 that European banks' IT budgets were estimated at close to 3% of net banking income in 2024, illustrating that technology already represents a material recurring allocation within banking economics even before the investment demands of large-scale AI adoption and intensified resilience requirements are fully reflected. Cybersécurité : le secteur financier face aux risques de dépendance — Banque de France — Sep 2026
The strategic question is therefore not merely whether those budgets increase, but what they purchase, because spending more on proprietary managed services can improve immediate functionality while making future migration harder, whereas investments in open interfaces, internal engineering competence, data portability, independent security monitoring and multi-environment deployment can initially cost more while preserving longer-term strategic options.
ECB Banking Supervision has made the investment requirement unusually explicit, arguing in June and July 2026 that operational resilience requires sustained multi-year expenditure across people, systems and governance and that current banking profitability creates an opportunity to make those investments rather than postpone them until economic conditions deteriorate. Strengthening operational resilience for the age of AI — ECB Banking Supervision — Jun 2026 Hearing of the Committee on Economic and Monetary Affairs — ECB Banking Supervision — Jul 2026
The implication for bank boards is that technology expenditure increasingly requires capital-allocation discipline comparable to other strategic investments, with projects evaluated not only according to near-term cost reduction but also according to dependency concentration, portability, exit cost, recoverability, regulatory alignment, data control and the preservation of internal expertise.
Europe should distinguish efficiency from irreversibility
Large global technology providers can offer security investment, geographic redundancy, specialised talent and economies of scale that individual European financial institutions could not economically reproduce, meaning that sovereignty policy which mechanically penalises external suppliers risks sacrificing genuine resilience in pursuit of nominal autonomy.
The more defensible approach is therefore to distinguish use from dependence: a bank may use a foreign cloud provider extensively without becoming strategically dependent if workloads are portable, data formats interoperable, cryptographic control remains independent, architectural documentation is complete, alternative environments have been tested and the institution retains the technical expertise necessary to migrate essential functions.
Conversely, an institution can become strategically dependent even while using several providers if its applications rely on proprietary services, APIs or operational processes that cannot be replicated elsewhere without prolonged redevelopment, meaning that nominal multi-cloud deployment does not necessarily constitute genuine substitutability.
The proposed CADA framework is important in this respect because its emphasis on sovereignty assurance levels moves European policy away from the simplistic proposition that physical data location is sufficient, recognising that legal control, software supply chains and exposure to third-country influence remain material even where servers are geographically located within the Union. Cloud and AI Development Act — European Commission
True sovereignty should therefore be measured through ability to continue operating when a supplier relationship changes unexpectedly, rather than by the flag under which the supplier operates.
Open source is becoming an instrument of strategic resilience
One of the less visible components of the June 2026 European technology-sovereignty package is the new EU Open Source Strategy, which reflects the recognition that control over software cannot be reduced to ownership of data centres or chips because financial and governmental infrastructure depends on enormous quantities of software whose continuity can be threatened by vendor discontinuation, licensing changes, supply-chain compromise or loss of maintenance capability.
The Commission explicitly links open-source development with the Cloud and AI Development Act and Chips Act 2.0 as part of the effort to construct a more competitive and resilient European digital economy, while CADA itself identifies open-source solutions as a mechanism capable of reinforcing resilience and reducing strategic dependency. Proposal for the Cloud and AI Development Act — European Commission
For banks, the strategic value of open source does not mean indiscriminately replacing supported commercial platforms, because security depends heavily on governance, maintenance and expertise, but it does create an important option where open interfaces and auditable code can reduce vendor lock-in and allow institutions or European service providers to maintain critical software independently if commercial relationships deteriorate.
Software sovereignty therefore depends partly on the ability to inspect, modify, maintain and migrate critical components rather than merely on where the software vendor is headquartered.
Cybersecurity itself is becoming an industrial-policy sector
Europe also faces the possibility of becoming dependent on external suppliers for the defensive technologies intended to protect it from dependency-related risk, which would create a strategic circularity in which financial institutions satisfy stronger cybersecurity requirements by purchasing an increasingly concentrated portfolio of non-European security platforms.
The EU has therefore begun using industrial-policy instruments to strengthen the European cybersecurity ecosystem, with the Digital Europe Programme operating with an overall budget of approximately €8.1 billion for 2021-2027, including approximately €1.4 billion dedicated to cybersecurity, covering deployment of cybersecurity capabilities, infrastructure coordination and support for adoption across the economy. Digital Europe Programme — European Commission Funding & Tenders Portal
The European Cybersecurity Competence Centre has additionally become an investment vehicle rather than merely a coordination institution, with responsibility for pooling EU, Member State and industry resources, supporting cybersecurity start-ups and deploying advanced cybersecurity technology, while four ECCC calls opened in late 2025 allocated €50 million specifically toward AI-powered cybersecurity, SME uptake, preparedness testing and regional cable-hub resilience. European Cybersecurity Competence Network and Centre — European Commission New European Cybersecurity Competence Centre calls — European Commission
On 10 July 2026, the Commission further adopted an EU Action Plan on Cybersecurity and Artificial Intelligence, explicitly linking AI-enabled defence with sovereign European AI capability and announcing an EU Grand Challenge intended to accelerate AI-powered cybersecurity solutions.
This marks an important policy shift because Europe is no longer attempting merely to regulate cybersecurity demand; it is beginning to intervene on the supply side, recognising that durable resilience requires a domestic industrial base capable of producing at least part of the technology on which critical sectors depend.
The sovereignty problem extends to models, not merely cloud infrastructure
The financial sector's AI dependencies differ from traditional cloud outsourcing because the institution can become dependent not only on infrastructure but simultaneously on foundation models, inference APIs, specialised accelerators, orchestration frameworks, proprietary data interfaces and model-monitoring tools, producing several layers of dependence inside a single application.
This matters because an institution can technically retain ownership of its data while losing operational autonomy if a critical process has been redesigned around a proprietary model whose behaviour, pricing or availability is controlled externally, particularly when employee workflows, fraud systems, compliance tools or customer-service processes become deeply integrated with the model.
The Banque de France has articulated an unusually clear sovereignty principle for its own AI architecture, stating that the more sensitive the information, the stronger the requirement that it remain within internal infrastructure or a trusted European cloud, while every AI solution should remain reversible and replaceable and should avoid technological lock-in that could expose the central bank to third-country law, unilateral price changes or discontinuation of an essential service. The challenges posed by AI from the perspective of the central bank — Banque de France
That principle can reasonably be generalised to financial institutions: model sovereignty does not require every bank to train its own frontier model, but it does require institutions to understand whether a material business process can continue if its preferred model provider becomes unavailable or economically unattractive.
Data sovereignty is more important than model sovereignty
An institution can change models more easily than it can recreate decades of proprietary transaction, risk and customer data, making control over data architecture arguably more strategically important than ownership of any individual AI system.
Future banking investment should therefore distinguish between replaceable intelligence and irreplaceable institutional data, ensuring that proprietary information remains stored in portable formats, that training and inference pipelines do not create undocumented dependencies, that data provenance remains traceable and that contractual terms prevent external technology providers from acquiring effective control over information that cannot realistically be reconstructed.
This perspective is consistent with the emerging European architecture because the Digital Decade programme identifies cloud, AI, secure data infrastructure and cybersecurity as mutually reinforcing foundations of technological sovereignty rather than independent policy domains. State of the Digital Decade 2026 — European Commission
For banks, sovereignty therefore begins with a relatively simple proposition: applications can be replaceable; core institutional data cannot.
Payment sovereignty demonstrates what technological dependency ultimately means
The sovereignty question becomes most concrete in payments because control of payment technology influences not only cybersecurity but also monetary autonomy and Europe's capacity to maintain commerce under geopolitical stress.
ECB Executive Board member Piero Cipollone argued in February 2026 that Europe's dependencies in payments and finance have become excessive and that strategic autonomy requires Europe to stop outsourcing functions critical to its security and prosperity, connecting digital infrastructure directly with monetary sovereignty rather than treating payment technology as an ordinary commercial service. Europe and monetary sovereignty — ECB — Feb 2026
The Banque de France has reached a similar conclusion, stating in April 2026 that the increasing role of non-European actors and technologies within euro-denominated payment systems generates interconnected risks to financial stability and strategic autonomy. Les systèmes de paiement en euro, un enjeu de souveraineté pour la France et l'Europe — Banque de France — Apr 2026
The importance of payment sovereignty is that it demonstrates the ultimate meaning of dependency: a service can be commercially efficient and technologically sophisticated yet still represent a strategic vulnerability if political or legal developments outside Europe can influence whether Europeans retain uninterrupted access to it.
This is why technological sovereignty cannot be evaluated solely through procurement costs; it requires analysis of who retains ultimate control under exceptional conditions.
Italy: the investment challenge is scale, integration and finance for domestic innovation
Italy's strategic problem differs from that of the largest European technology ecosystems because the central challenge is not merely technological adoption but the ability to mobilise sufficient long-term capital to convert research, specialist companies and innovative financial applications into industrial-scale capabilities.
Banca d'Italia Governor Fabio Panetta argued in July 2026 that many of the investments required by artificial intelligence are intangible — including software, data, skills, research and organisational transformation — and therefore difficult for traditional finance to value because their returns are uncertain and often materialise over long periods, making patient capital, equity finance and deeper markets critical to turning technological innovation into productivity. Finance for innovation and artificial intelligence as drivers of development — Banca d’Italia — Jul 2026
The same reasoning applies to cybersecurity and sovereign infrastructure because investments in internal expertise, architecture portability or secure European technology stacks may produce limited immediate revenue while preserving strategic options whose economic value becomes visible only under conditions of disruption or geopolitical stress.
Banca d'Italia's Strategic Plan 2026-2028 accordingly places responsible AI adoption, cyber resilience, payment-infrastructure modernisation and advanced digital technologies inside the central bank's own investment strategy, while explicitly linking these programmes to the broader requirement to respond proactively to external shocks and technological transformation. Strategic Plan for 2026-2028 — Banca d’Italia
For Italy, the strategic opportunity therefore lies in combining financial-sector demand with domestic and European technology development, using regulated financial institutions not merely as customers of imported digital infrastructure but as anchor buyers, investors and development partners for specialised European cybersecurity, financial-data and AI capabilities.
The principal constraint remains scale: fragmented domestic procurement can sustain pilots but rarely creates suppliers capable of competing internationally, making European interoperability and common procurement significantly more important for Italy than purely national technological autonomy.
France: sovereignty is becoming a procurement criterion
France has moved furthest among the four countries considered here toward explicitly integrating sovereignty into technology procurement and supervisory thinking, with Banque de France officials increasingly describing cybersecurity and sovereignty as two dimensions of the same problem: control over critical digital infrastructure.
Denis Beau stated on 9 September 2026 that reliance on a limited number of indispensable technology providers can reduce financial institutions' ability to evaluate, control and reproduce outsourced functions internally, creating strategic vulnerability even where the supplier itself maintains strong technical security. Cybersécurité : le secteur financier face aux risques de dépendance — Banque de France — Sep 2026
The Banque de France is applying the principle internally rather than limiting it to supervisory rhetoric, because its AI policy requires sensitive information to remain on internal infrastructure or a trusted European cloud, demands reversibility and replaceability from technological solutions and treats avoidance of supplier lock-in as a condition of central-bank autonomy. Les enjeux de l’IA du point de vue de la Banque Centrale — Banque de France
This makes France an important test case for whether sovereignty criteria can be introduced without undermining innovation, because the challenge is to establish sufficient procurement discipline to preserve strategic control while avoiding a regime in which nationality becomes a substitute for objective evaluation of security, performance and resilience.
The French model suggests that the relevant principle should be progressive sovereignty according to sensitivity, rather than universal localisation.
Germany: digital sovereignty is being treated as economic capability
Germany's emerging framework places particular emphasis on industrial capacity, because the Bundesbank, the Federal Office for Information Security and the State of Hesse jointly published 37 implementation-oriented measures for digital sovereignty in July 2026 covering semiconductors, cloud computing, artificial intelligence, robotics and quantum technologies, explicitly arguing that digital sovereignty will influence both where future economic value is created and whether Germany and Europe retain the capability to shape technological development rather than merely consume it. 37 implementation-oriented measures for digital sovereignty in Germany and Europe — Deutsche Bundesbank — Jul 2026
This is strategically significant for banking because Germany combines a large financial sector with a major industrial base, meaning that domestic demand for cloud, cybersecurity and AI infrastructure can potentially support broader technology ecosystems rather than remaining exclusively a cost centre for banks.
Germany has also developed collaborative approaches to supplier oversight, including initiatives through which major financial institutions jointly audit important cloud providers, a model cited by Banque de France as an example of how financial entities can increase negotiating leverage and reduce duplication when dealing with technology companies whose scale exceeds that of many individual banks. Cybersécurité : le secteur financier face aux risques de dépendance — Banque de France — Sep 2026
The broader German policy implication is that sovereignty does not necessarily require every institution to internalise every capability; collective purchasing, shared audits, interoperable standards and coordinated infrastructure can increase European bargaining power while preserving access to global suppliers.
United Kingdom: resilience without an explicit autonomy doctrine
The United Kingdom has pursued a somewhat different strategic model because its policy framework concentrates more heavily on direct oversight and resilience of global technology providers than on constructing a European-style sovereignty doctrine.
That distinction became operational on 13 July 2026, when the Bank of England, Prudential Regulation Authority and Financial Conduct Authority began direct joint oversight of the first four technology companies designated by HM Treasury as Critical Third Parties to the UK financial system: Amazon Web Services EMEA, Google Cloud EMEA, Microsoft Ireland Operations and Oracle Corporation UK. UK financial regulators to begin overseeing Critical Third Parties — Bank of England — Jul 2026
The British approach therefore accepts that globally supplied infrastructure will remain deeply embedded within the financial sector while attempting to reduce the systemic risk created by that dependence through regulatory access, testing, resilience requirements and supervisory engagement with the provider itself.
This represents an important alternative to stronger autonomy policies because it assumes that governability of dependency can substitute in part for domestic ownership, provided regulators possess sufficient visibility and leverage over the critical services concerned.
The UK model is therefore likely to become an important comparator for continental Europe: if direct supervision of external technology suppliers proves capable of ensuring continuity without materially constraining innovation, it will strengthen the case for open technological ecosystems combined with strong regulatory control; if geopolitical, legal or commercial developments reveal limits to supervisory influence over foreign-controlled technology, the European argument for stronger domestic capacity will become correspondingly more persuasive.
The investment decision should be organised around strategic layers
The most defensible architecture is therefore neither complete technological self-sufficiency nor unrestricted global sourcing, but a differentiated investment structure in which banks and governments decide which layers justify higher expenditure for strategic control.
At the data layer, institutions should preserve direct control over critical datasets, cryptographic material, provenance and portability because loss of control over historical financial data creates an exposure that cannot quickly be reversed.
At the application layer, institutions should favour open interfaces, documented portability and modular architectures capable of changing underlying providers without rebuilding complete business processes.
At the cloud layer, resilience should be evaluated according to actual workload substitutability, contractual exit capability and tested migration rather than nominal numbers of suppliers.
At the AI layer, model providers should be treated as replaceable components wherever technically possible, while highly sensitive use cases should operate within controlled infrastructure capable of preserving confidentiality and institutional autonomy.
At the cybersecurity layer, Europe requires enough domestic capability to avoid a scenario in which the tools responsible for observing and defending critical infrastructure themselves become an irreplaceable external dependency.
At the hardware layer, complete European self-sufficiency is unrealistic in the relevant horizon, but diversified sourcing, strategic inventories, European semiconductor capability and access to shared high-performance computing can reduce the consequences of disruption.
The investment logic is therefore hierarchical: spend most aggressively where irreversibility and systemic consequence intersect.
Sovereignty has a price, but dependence has an option value that is often ignored
European institutions should acknowledge explicitly that greater strategic autonomy can increase short-term costs because maintaining multiple compatible environments, avoiding proprietary lock-in, sustaining internal technical expertise and financing alternative infrastructure creates duplication that pure efficiency analysis may classify as unnecessary.
The error would be to compare this duplication with the cost of normal operation rather than with the cost of losing strategic options during abnormal conditions, because resilience is economically valuable precisely when the primary system cannot be relied upon.
The same principle already underlies capital buffers, liquidity reserves, backup sites and insurance: assets or capabilities that appear inefficient during normal periods become valuable when ordinary assumptions fail.
Technological substitutability should therefore be understood as a form of real option, because investment made today purchases the future ability to change providers, jurisdictions or architectures when circumstances make continuation of the existing relationship economically or politically undesirable.
Banks that optimise technology solely for current operating cost can unknowingly sell this option without recording the transaction anywhere on their balance sheets.
European sovereignty ultimately requires a market, not a protected enclave
No sovereignty strategy can succeed permanently if European cloud, AI and cybersecurity solutions remain economically dependent on protection from competition, because banks will ultimately require the best available security, performance and functionality if they are to compete globally.
The strategic objective must therefore be to create sufficient demand, financing, computing infrastructure, talent and common standards for European suppliers to scale until choosing them becomes commercially rational rather than politically symbolic.
The Commission's 2026 Digital Decade assessment demonstrates that this is fundamentally an execution problem because Member States have already committed nearly €290 billion of digital measures while Europe continues to retain significant structural dependencies, indicating that the next phase cannot be judged by the number of programmes launched but by whether those programmes create internationally competitive technology companies and infrastructure. State of the Digital Decade 2026 — European Commission
Europe therefore needs procurement aggregation, scale-up finance, common technical standards and deeper capital markets at least as much as it needs additional regulation, because fragmented national demand can produce compliant national projects without creating suppliers capable of competing at continental or global scale.
The current profitability window should be treated as strategically temporary
The latest banking statistics make the investment decision unusually consequential because European significant institutions are entering this technological transition from a comparatively strong earnings position, with the 10.73% aggregate annualised return on equity reported for the second quarter of 2026 representing the highest level in the ECB series, while aggregate capital remains substantial. ECB supervisory banking statistics — Second quarter 2026
There is no guarantee that this profitability environment will persist across the investment cycle, which is why ECB supervisors have repeatedly argued that current earnings provide banks with an opportunity to finance resilience before weaker economic conditions reduce discretionary investment capacity. Interview with Milano Finanza — Claudia Buch, ECB Banking Supervision — Jan 2026
For boards, postponing strategic technology investment can therefore create a double disadvantage: the architecture becomes progressively more difficult to change as dependencies deepen, while the financial capacity available to fund transformation may be lower when migration eventually becomes unavoidable.
The relevant decision is not simply whether to spend more in 2026 or 2027, but whether current profitability is used to purchase future technological freedom of action.
Europe should avoid confusing sovereignty with fragmentation
A final strategic danger is that technological sovereignty pursued through twenty-seven divergent national approaches could weaken precisely the European companies intended to benefit, because cloud providers, cybersecurity firms and AI developers require a sufficiently large market to amortise infrastructure and research expenditure.
Banca d'Italia has explicitly warned that divergence in rules, data standards and supervisory approaches can increase compliance costs and prevent financial institutions from scaling AI applications across borders, while a coherent European framework would support both safer adoption and deeper integration of the Single Market. From Analysis to Action: AI in Financial Markets — Banca d’Italia — Apr 2026
Technological sovereignty therefore requires more European integration, not less, because the economically relevant unit for competing in cloud, semiconductors, cybersecurity and frontier AI is continental rather than national.
A fragmented collection of nationally sovereign systems can remain globally dependent, while an integrated European market possessing shared infrastructure, portable standards and competitive suppliers can remain strategically autonomous even while trading extensively with the rest of the world.
The decision facing Europe
Europe now has to decide whether the next wave of financial-sector digitalisation will reproduce the dependency architecture of the previous decade or deliberately create greater freedom of action, and the answer cannot be delivered through regulation alone because regulation can require resilience but cannot manufacture semiconductors, build data centres, train engineers, finance scale-ups or create competitive cloud and AI companies.
The emerging policy architecture nevertheless represents the beginning of a coherent response: DORA establishes operational accountability; the proposed CADA introduces a graduated sovereignty framework for cloud and AI; InvestAI and the AI Gigafactory programme attempt to build computational capacity; the EU Open Source Strategy addresses software dependency; Digital Europe and the European Cybersecurity Competence Centre support security capability; and the broader capital-market agenda seeks to mobilise European savings toward strategic technology.
The decisive variable will be whether these initiatives converge into an integrated industrial and financial ecosystem rather than remaining separate programmes administered by separate institutions.
For banks themselves, the implication is more immediate: every major cloud contract, AI-platform deployment, cybersecurity procurement and core-system transformation now contains a strategic option embedded inside a technology decision, because it determines not only what the institution can do today but how easily it can change direction tomorrow.
The relevant objective should therefore be neither maximal localisation nor maximal outsourcing, but maximum strategic freedom consistent with global technological competitiveness, achieved by investing in portability, internal capability, European alternatives, data control, open standards and realistic substitution pathways while continuing to use international technology where it offers genuine advantages.
Europe's sovereignty problem is therefore ultimately an investment problem, and its investment problem is ultimately a question of whether governments, banks and capital markets are prepared to pay today for technological choices that preserve autonomy under conditions that cannot yet be predicted.
Key judgments
Europe's strategic vulnerability derives not from the use of foreign technology itself but from irreversible dependence, particularly where critical financial functions cannot be migrated, replicated or operated independently if commercial, technological, legal or geopolitical conditions change.
The strongest new development in 2026 is that the European Union has begun converting technological sovereignty from a political concept into an investable architecture through the proposed Cloud and AI Development Act, AI Gigafactories, InvestAI, the EU Open Source Strategy and dedicated cybersecurity programmes, while explicitly recognising that cloud, AI, semiconductors and cybersecurity represent interconnected components of strategic autonomy. Strengthening Europe’s Tech Sovereignty — European Commission
The financing requirement cannot be met predominantly through public expenditure because national Digital Decade programmes already represent approximately €289.3 billion of measures while a substantial share of their present public financing is approaching expiry, making mobilisation of bank finance and European capital markets increasingly necessary. 2026 State of the Digital Decade package — European Commission
The present profitability of major euro-area banks creates an unusually favourable but potentially temporary period for strategic technology investment, meaning that institutions which postpone architecture modernisation may confront both deeper technological lock-in and weaker future financing capacity.
European sovereignty should therefore be measured principally through control of critical data, portability of workloads, substitutability of providers, software transparency, preservation of internal expertise and continuity under geopolitical stress, rather than through supplier nationality alone.
The United Kingdom is pursuing a partially different experiment by directly supervising globally controlled critical technology providers rather than embedding technological autonomy as explicitly within its policy framework, creating an important comparative test of whether regulatory control can provide sufficient strategic resilience without larger-scale domestic technological substitution. UK financial regulators to begin overseeing Critical Third Parties — Bank of England
What would change the assessment
The assessment that Europe requires substantially greater indigenous digital capability would weaken if global cloud, AI and software markets became materially more diversified, interoperability improved sufficiently to make supplier migration inexpensive and rapid, European financial institutions demonstrated routine portability of critical workloads between unrelated providers, and geopolitical arrangements provided durable legal guarantees against discriminatory withdrawal of strategically important technology services.
The judgment would strengthen if European adoption of cloud and AI continued accelerating while market concentration remained high, if material workloads became progressively dependent on proprietary APIs or model ecosystems that were difficult to replace, if foreign legal or geopolitical measures restricted European access to critical technology, or if the cost of switching major providers proved materially higher than current institutional risk assessments assume.
A particularly important signpost will be implementation of the proposed Cloud and AI Development Act, because the practical meaning of its sovereignty assurance levels, the willingness of providers to undergo the required assessments and the extent to which financial institutions incorporate those classifications into procurement will reveal whether technological sovereignty becomes an operational market discipline or remains predominantly a public-sector policy objective. Proposal for the Cloud and AI Development Act — European Commission
The second decisive indicator will be whether the AI Gigafactory programme succeeds in mobilising the private investment envisioned by the Commission and producing commercially usable European computing capacity at competitive cost, because infrastructure that exists only through subsidy but is not adopted by demanding private-sector users would provide limited strategic autonomy.
The third will be whether European technology companies begin retaining a greater share of their scale-up financing inside European capital markets, since infrastructure sovereignty cannot be separated indefinitely from ownership, financing and corporate scale.
Open official record
The public record does not presently provide a sufficiently complete mapping of how much of European banks' critical workloads, AI inference, cybersecurity telemetry or core data processing is hosted on European-controlled infrastructure compared with subsidiaries of non-European technology groups, making the actual scale of strategic dependence impossible to quantify precisely.
No harmonised public metric currently establishes the switching cost or migration time required for a major European bank to move a critical workload from one cloud or AI provider to another, even though that variable is arguably more informative for sovereignty than nominal supplier diversification.
Similarly, official sources do not yet provide a standardised measure of how much financial-sector AI expenditure ultimately flows toward European models, computing infrastructure and software providers, preventing a reliable assessment of whether rapid financial-sector AI adoption is strengthening Europe's technology ecosystem or increasing dependence on external platforms.
The economic return from sovereignty-enhancing duplication also remains imperfectly observable because the value of maintaining alternative infrastructure, internal expertise or portable architecture becomes most visible only when the dominant provider fails or becomes unavailable, making traditional short-term return-on-investment analysis structurally biased against resilience.
The central unresolved question is therefore not whether Europe has identified the problem, because the policy architecture adopted and proposed during 2026 demonstrates that it has, but whether European institutions can convert regulation, public investment, private capital and procurement demand into globally competitive technological capacity before their dependence on the next generation of cloud and AI infrastructure becomes substantially harder to reverse.
Europe Now Faces an Investment and Sovereignty Decision
BLUF (Bottom Line Up Front): Europe's financial-security and tech-sovereignty challenge centers on capital allocation under strategic technological dependence. While euro-area banks record strong profitability (RoE 10.73%, CET1 16.00% in Q2 2026), much of the underlying cloud infrastructure, AI foundation models, and advanced processors remain controlled outside Europe. To avoid passive reliance or autarky, Europe is deploying industrial-scale instruments—the proposed Cloud and AI Development Act, the €200B InvestAI initiative, AI Gigafactories, and Chips Act 2.0—to achieve controlled dependency through substitutability, portability, and domestic capacity.
The CADA 4-Level Assurance Model: Sovereignty by Function
Risk-Proportionate Assurance
Rather than imposing blanket localization, the proposed Cloud and AI Development Act (CADA) establishes a 4-level assurance framework. Level 1 secures EU data storage/processing, while higher levels introduce third-country immunity, software transparency, and EU ownership control.
Banking Profitability Window
Significant institutions recorded a Q2 2026 RoE of 10.73% and a CET1 ratio of 16.00% (ECB data). This strong profitability provides banks with a temporary financial window to fund strategic resilience and portable architecture before economic conditions tighten.
Industrial Compute Scaling
The Commission's €200B InvestAI initiative and AI Gigafactory calls (up to €10B public funding unlocking €20B private investment for facilities featuring >100,000 advanced processors) aim to build indigenous compute scale to compete globally.
Table 1: European Sovereignty Policy Package & Industrial Instruments
Controlling official European Commission, ECB, and Digital Decade benchmarks.
| Policy Instrument | Verified Financial / Scale Value | Operational Scope & Target | Issuing Authority | Strategic Significance |
|---|---|---|---|---|
| Cloud & AI Development Act (CADA) | 4-level assurance framework | Evaluation of cloud/AI on location, third-country immunity, and software transparency. | European Commission (June 2026) | Operationalizes sovereignty through risk-proportionate functional requirements. |
| InvestAI Initiative | €200 billion total mobilisation | Includes €20bn dedicated facility for AI gigafactories (launched Feb 2025). | European Commission | Expands European AI compute infrastructure at industrial scale. |
| AI Gigafactories Call | Up to €10B public / €20B private (up to 7 facilities) | Launched 30 July 2026; facilities incorporating >100,000 advanced AI processors. | European Commission | Creates physical computing infrastructure to reduce external AI dependency. |
| Digital Decade Roadmaps | €289.3 billion across 1,934 measures (€205.9B public) | 2026 State of the Digital Decade package. | Member States / Commission | Highlights financing transition as RRF-era public funds phase out by end of 2026. |
| ECB Banking Statistics | 10.73% RoE (Q2 2026); 16.00% CET1; 53.06% C/I | Significant euro-area banking institutions (ECB Sept 2026 release). | ECB Banking Supervision | Provides banking sector with financial capacity to invest in strategic resilience. |
| Cybersecurity Competence Centre | €50 million across 4 late-2025 calls | AI cybersecurity, SME uptake, preparedness testing, and cable-hub resilience. | ECCC / European Commission | Strengthens domestic European cybersecurity industrial base and supply-side capabilities. |
Table 2: National Jurisdictional Approaches (Italy, France, Germany, UK)
Contrasting sovereign procurement criteria, industrial measures, and direct supervisory models across core markets.
| Jurisdiction | Key Supervisory / Policy Body | Strategic Position & Doctrine | Key Initiatives / Statements | Core Strategic Approach |
|---|---|---|---|---|
| ITALY | Banca d'Italia | Mobilising long-term patient capital for intangible tech investments; Strategic Plan 2026–2028. | Governor Fabio Panetta (July 2026) on patient capital for AI and intangible innovation. | Anchor Buyer & Long-Term Capital Mobilisation |
| FRANCE | Banque de France / ACPR | Integrating sovereignty directly into procurement and central-bank AI architecture. | Denis Beau (Sept 2026) on dependency risks; internal C-B AI policy requiring EU cloud. | Sovereignty as Procurement Criterion |
| GERMANY | Deutsche Bundesbank / BSI / Hesse | Industrial capacity focus; joint financial institution cloud audits. | 37 implementation measures for digital sovereignty (July 2026); joint bank cloud audits. | Industrial Capability & Collective Auditing |
| UNITED KINGDOM | Bank of England / PRA / FCA / HM Treasury | Direct joint oversight of global technology providers rather than explicit sovereignty doctrine. | Critical Third Party oversight beginning July 2026 for AWS, Google, Microsoft, Oracle. | Governability of Dependency via Direct Supervision |
Deep Structural Breakdown: Core Sovereignty & Investment Vectors
Deconstructing the shift from legal standards to industrial compute capacity, workload portability, and open-source resilience.
Workload Portability over Localisation
True sovereignty is measured by operational replaceability and exit pathways rather than supplier flag. A bank may use international cloud services safely if workloads are portable, data formats interoperable, and independent cryptographic control is preserved.
Data Sovereignty vs. Model Sovereignty
Models are replaceable intelligence, whereas decades of proprietary transaction and risk data are irreplaceable institutional assets. Banking architecture must prioritize data provenance, portable storage formats, and independent training/inference pipelines.
Open Source as Strategic Resilience
The EU Open Source Strategy and CADA recognise that software control requires auditable code and open interfaces. Auditable software prevents vendor lock-in and allows financial institutions to maintain critical applications independently if commercial relationships deteriorate.
Forensic Strategic Key Judgments
Definitive analytical assessments derived from ECB banking statistics, Digital Decade roadmaps, and European Commission sovereignty instruments.
Sovereignty is Control, Not Autarky
Restricting banks to European suppliers regardless of performance would harm competitiveness; sovereignty requires controlled dependency via substitutability and portability.
Strong Bank Profitability Funds the Transition
Q2 2026 significant institution RoE of 10.73% and CET1 of 16.00% provide an unusually strong financial window to fund resilience and portable architectures.
Industrial Scale Replaces Pure Regulation
The €200B InvestAI program and AI Gigafactories call (>100k processors per facility) move EU policy from compliance mandates to physical computing infrastructure.
Public Funding Phase-Out Requires Capital Markets
With RRF-era public funds phasing out by end of 2026, deepening European capital markets is essential to finance long-term technology and AI infrastructure.
Data Control Trumps Model Ownership
Foundation models are swappable intelligence, whereas proprietary transaction and risk data are irreplaceable institutional assets requiring rigorous portability.
UK Direct Supervision vs. EU Sovereignty Doctrine
The UK relies on direct joint oversight of global tech providers (AWS, Microsoft, Google, Oracle), creating a vital comparative test against continental autonomy.
Open Official Record Gaps
- Workload Hosting Mapping: Absence of public statistics detailing exact proportions of bank workloads hosted on European vs. non-European infrastructure.
- Migration Switching Costs: Lack of standardized metrics measuring the time and financial cost required to migrate bank workloads between major cloud providers.
- AI Expenditure Flow Tracking: Unquantified official tracking on whether European banking AI expenditure benefits domestic European technology platforms.
- CADA Implementation Uptake: Unobserved market adoption of CADA sovereignty assurance levels by financial institutions post-legislation.