



Scope: This dossier assesses whether Europe possesses a functioning, genuinely European digital ecosystem across cloud infrastructure, cybersecurity, operational software and AI computing, distinguishing the European Union from the United Kingdom, examining evidence available by 16 November 2026 and adopting an outlook to November 2031.
Executive Summary / BLUF
Europe possesses a real digital supply base, including commercially operating cloud providers, cross-border service partnerships, public computing infrastructure and deployed alternatives to proprietary software. It does not follow that these capabilities form an autonomous ecosystem across the entire technology stack.
The Commission’s April 2026 procurement established access to sovereign cloud services for up to €180 million over six years, with different sovereignty levels among successful providers; this is a procurement ceiling, not demonstrated expenditure or universal technological independence. commission.europa.eu
OVHcloud reported €1,145.1 million in FY2026 revenue, while EuroHPC documents substantial European-operated computing infrastructure that incorporates non-European processors. [Sources: OVHcloud, October 2026; EuroHPC JU, June 2026, detailed below.] corporate.ovhcloud.com
The defensible judgment is partial, operationally meaningful autonomy, uneven across services, countries and dependencies.
Procurement should reward verifiable control, continuity and substitutability; European branding alone cannot establish those properties.
The decisive uncertainty is whether bounded sovereign services can scale into interoperable alternatives that remain maintainable, affordable and usable during a serious supplier disruption.
Europe’s Digital Sovereignty Must Be Bought as a Capability
The European Commission’s sovereign-cloud procurement exposes the contradiction at the centre of Europe’s digital policy: institutions can purchase services under European control while remaining dependent on technologies, maintenance and operating relationships they cannot readily replace. The governing test should therefore be whether public spending buys demonstrable freedom to operate, recover and change supplier. The Data Act and the Digital Operational Resilience Act give customers stronger instruments to govern dependence, but neither creates an alternative platform or supplies the engineers needed to migrate an application. Europe already possesses operating providers and public computing infrastructure. Its industrial and security interests now depend on converting that supply base into services that institutions can sustain under pressure. Spending that enlarges capacity without improving those choices can leave the underlying dependence intact.
The figures measure different things—and policy must preserve the distinction
The Commission’s April 2026 sovereign-cloud award allows Union entities to procure services for up to €180 million over six years. That is purchasing capacity, not expenditure already incurred or guaranteed supplier revenue. The IPCEI Next Generation Cloud Infrastructure and Services authorises up to €1.2 billion in public funding, expected to unlock €1.4 billion in private investment, for research, development and first industrial deployment. TechEU identifies €70 billion in EIB Group financing over 2025–2027, intended to mobilise at least €250 billion in investment across several innovation domains. Adding these figures would manufacture an industrial result from incompatible accounting categories. Commission procurement decision; IPCEI framework; TechEU financing structure.
Commercial scale presents a separate constraint. AWS reported $128.7 billion in global segment sales and $45.6 billion in operating income for calendar 2025. OVHcloud reported €480.5 million in adjusted EBITDA, €77.8 million in operating results and €9.4 million in net income for FY2026. Different currencies, periods, portfolios and accounting measures prevent a simple competitive ratio. They nevertheless identify the economic problem: European suppliers must finance renewal, specialised support and product development while customers compare them with platforms supported by substantial recurring demand. A funding envelope cannot substitute for that demand.
National delivery figures require equal discipline. PSN reported more than 280 migrated public administrations in July 2026; ZenDiS reported 100,000 openDesk-equipped public-sector workplaces in October 2026; the Health Data Hub described more than 350 technical requirements in its selection of Scaleway. These are evidence of implementation, distribution and purchasing complexity respectively. They do not establish complete application migration, uniform daily use or accepted delivery. Their policy value lies in the next question each makes answerable: what function has become more controllable, and what evidence demonstrates it?
Procurement can create a market—or consolidate the incumbent
The Health Data Hub’s selection of Scaleway shows how public demand can influence industrial capability. A demanding customer can specify security, scalability and operating requirements that encourage a supplier to extend its offer. The announcement also acknowledged that participating offers covered parts of the requirement and that some security options remained to be implemented. Selection therefore established a delivery relationship, not a completed sovereign capability. The industrial benefit depends on whether the resulting functions are accepted, maintained and made useful beyond the original customer. Health Data Hub selection announcement.
The UK’s proposed National Cloud Infrastructure Programme creates a related tension. Central purchasing can improve negotiating leverage and give suppliers investment visibility. A contract too broad for additional providers to contest can also concentrate demand and make later switching harder. The Government Digital Service expects procurement to launch in early 2027, subject to design and approvals; its engagement horizon is not an awarded contract term. The eventual structure will determine whether aggregation supports competing providers or gives government a better price for a deeper dependence. Cloud Challenge Book clarification.
Directive 2014/24/EU permits evaluation through cost-effectiveness and life-cycle costing, subject to verifiable criteria linked to the contract. That gives authorities room to examine transition effort, maintenance and service quality. The purchasing requirement must connect these characteristics to delivery: a portability advantage used to select an offer loses value if the contract does not preserve the corresponding interfaces, assistance and evidence. Procurement shapes the market through the obligations suppliers must continue fulfilling.
Stronger rights do not perform the migration
The Data Act makes switching a more explicit contractual process, while the Commission’s non-binding cloud clauses provide tools for planning, testing and termination. Neither establishes that exported information will reproduce a working application at its destination. Identity, configuration, historical records and application behaviour must remain usable together. A customer that has never tested that reconstruction possesses a legal option whose operational value remains uncertain. The distinction matters at renewal, when an untested alternative offers weaker protection against price changes or deterioration in service. Commission Recommendation (EU) 2026/2394.
The Digital Operational Resilience Act keeps responsibility with financial entities using external ICT services. Registers, concentration assessments and exit plans must therefore support actual decisions. A supplier can satisfy a defined assurance requirement while the customer remains unable to recover a critical function within its approved conditions. Likewise, qualification of infrastructure does not automatically establish the security or qualification of an application running on it. Institutions must purchase the service they have assessed and preserve the capacity to verify it throughout the relationship.
European operation does not complete the supply chain
LUMI-AI demonstrates how institutional integration and technological dependence can advance together. European organisations have arranged funding, hosting, procurement and access for an expansion built on AMD processors and accelerators. That can increase European control over who receives computing resources without creating an indigenous component supply chain. DARE addresses a different part of the problem through processor, accelerator and software development. Its contribution must be credited through technical and production milestones, rather than treating a research objective as an available replacement.
ASML’s supplier disclosures show that European industrial strength can itself contain concentrated vulnerabilities. Its dependence on Carl Zeiss SMT for critical optical components is a different problem from external jurisdiction, but it still matters to continuity. Industrial policy must identify the constraint it intends to reduce: access to technology, production concentration, maintenance competence or exposure to another authority. A measure that improves one can leave the others unchanged. “European content” is too coarse a purchasing metric to reveal that difference.
Oversight can manage concentration without removing it
The UK’s critical-third-party regime and DORA recognise that some dependencies extend beyond individual customers. A shared provider failure can create competing recovery demands across institutions, while one customer’s contract reveals little about the wider system’s priorities. The memorandum between European supervisory authorities and British financial regulators supplies a mechanism for cooperation and information sharing across distinct jurisdictions. Its value lies in improving the understanding and management of common exposure; it does not give each institution an executable substitute. EU–UK oversight memorandum announcement.
The FCA’s November 2026 observations sharpen the standard: institutions should demonstrate what they can deliver during severe disruption, challenge supplier assumptions and consider cumulative harm across interconnected services. That is also a useful discipline for European industrial policy. A programme should establish which essential outcome becomes achievable after investment and how that result was tested. Future capacity cannot serve as evidence that a present recovery weakness has been resolved. FCA resilience observations.
The next two years will allocate the cost of untested dependence
Over the next 12–24 months, the Health Data Hub migration, Italy’s continuing PSN implementation, Germany’s reusable-software programmes and the UK’s planned procurement will face different acceptance tests. The decisive evidence will concern usable services, supported configurations and the ability to change arrangements without losing essential functions. Institutions should commission representative recovery and transition exercises before extending their reliance. Where a gap appears, investment should address its demonstrated cause rather than default to another infrastructure announcement.
The cost of inaction will fall first on customers and public budgets. Under DORA, financial entities retain responsibility; under public-service contracts, administrations still have to sustain delivery when a supplier relationship fails. Without tested alternatives, they may have to pay for parallel operation, emergency integration or a difficult renewal. European suppliers also bear a cost when public programmes fund development without creating durable demand. By 2031, Europe’s stronger position would be measured in services it can operate, maintain and replace under adverse conditions. The purchasing decisions made over the next two years will determine how much of that freedom becomes real.
Navigational Index
Pillar I — What Europe Actually Controls
- Chapter 1 — Defining a European Ecosystem: Ownership, Authority and Operational Control
- Chapter 2 — Delivered Capabilities: Cloud, Cybersecurity, Software and AI Computing
- Chapter 3 — Dependency Architecture: Chips, Platforms, Maintenance and Infrastructure
Pillar II — Institutions, Markets and National Implementation
- Chapter 4 — Legal Sovereignty: Jurisdiction, Qualification, Procurement and Exit
- Chapter 5 — Industrial Economics: Scale, Investment, Demand and Sustainable Supply
- Chapter 6 — National Realities: Italy, France, Germany, the United Kingdom and EU Coordination
Pillar III — Strategic Resilience and Decisions
- Chapter 7 — Disruption Pathways, Competing Futures and the Outlook to 2031
- Chapter 8 — Courses of Action, Decision Thresholds and Final Net Assessment
Master Abstract
A genuine ecosystem requires functioning relationships
The primary question is whether European organisations can obtain, combine, operate and replace essential digital capabilities under effective European authority. For this assessment, a functioning ecosystem requires more than the presence of European suppliers: it requires durable relationships between infrastructure operators, software developers, security providers, maintainers, customers and financing institutions. Its sovereignty depends on the particular activity being assessed. European ownership can strengthen corporate accountability without establishing control over an underlying software platform. European hosting can establish location without proving that administration, diagnostics or technical support remain within the same perimeter. Conversely, reliance on an imported component does not by itself establish foreign access to customer information. The appropriate unit of analysis is therefore the specific service and its dependency chain, rather than the nationality attached to a company or data centre.
The Commission’s cloud procurement provides a concrete demonstration of both capability and limits. Its successful suppliers included the Post Telecom–OVHcloud–Clever Cloud partnership, STACKIT, Scaleway and a Proximus-led partnership using S3NS, Clarence and Mistral. The Commission reported different sovereignty levels, including a lower level for the Proximus/S3NS offering than for the other successful providers. Its award therefore supports the existence of competing European delivery arrangements, while preserving a distinction between European-developed technology and European-operated services incorporating external technology. Commission advances cloud sovereignty through strategic procurement — European Commission — Apr 2026. commission.europa.eu
Commercial existence is established; comprehensive substitutability is not
Commercial reporting supplies evidence that European cloud activity extends beyond publicly financed experimentation. OVHcloud reported FY2026 revenue of €1,145.1 million, including €255.1 million from Public Cloud, for the financial year ended 31 August 2026. These are company-reported results covering its own business segments and international operations; they cannot be treated as the size of the European sovereign-cloud market. Nevertheless, recurring commercial revenue establishes a materially stronger foundation than a memorandum, funding announcement or proposed facility. The strategic question concerns the breadth of services that customers can adopt and sustain, rather than whether a European supplier exists at all. All 2026 targets achieved, excellence in execution, focus on value creation — OVHcloud — Oct 2026. corporate.ovhcloud.com
Cybersecurity partnerships also demonstrate an emerging division of labour between European infrastructure and application providers. In its September 2026 announcement, Bitdefender described hosting GravityZone on Aruba infrastructure while retaining operational control of the platform, and committed to an EU perimeter for customer and configuration data, security events and telemetry. This is an attributable supplier commitment. It establishes the announced architecture and commercial proposition; it does not independently establish compliance across every enabled feature, privileged-access event or emergency support workflow. The appropriate next evidence consists of applicable contracts, service configurations and audit findings. Such arrangements can strengthen a European ecosystem when their respective responsibilities are enforceable and technically observable. Bitdefender and Aruba Partner to Deliver Sovereign European Cybersecurity to Italian Businesses — Bitdefender — Sep 2026. bitdefender.com
Computing capacity and industrial autonomy remain distinct
Europe’s public computing infrastructure demonstrates the difference between possessing a capability and controlling every technology required to reproduce it. EuroHPC’s June 2026 account describes JUPITER as built on BullSequana XH3000 architecture and equipped with approximately 24,000 NVIDIA GH200 Grace Hopper Superchips. European institutions can therefore operate substantial computing resources while retaining dependencies on external semiconductor suppliers. Those dependencies require separate assessment for maintenance, replacement, software compatibility and future expansion. The installed system establishes capacity; it does not establish an indigenous accelerator supply chain. Two New EuroHPC Systems Join the TOP500 as JUPITER Remains Among the World’s Fastest Supercomputers — EuroHPC JU — Jun 2026. eurohpc-ju.europa.eu
The European Court of Auditors’ 2025 semiconductor assessment provides a further constraint on expansive sovereignty claims. It found that the Chips Act had generated momentum but was highly unlikely to deliver the 20% Digital Decade target. Its accompanying factsheet presented a 2030 projection of 11.7% of global semiconductor value-chain share, compared with the 20% objective. That projection is an assessment published in 2025, not an observed 2026 outcome or a measure of Europe’s ability to produce particular AI accelerators. Its strategic significance is the gap between declared ambition and the industrial trajectory then assessed. The EU’s strategy for microchips: Key facts and findings, Special Report 12/2025 — European Court of Auditors — 2025. The EU’s strategy for microchips
Legal protection must be matched by operational control
European law supplies meaningful authority over data processing, but legal authority and technical independence answer different questions. The European Data Protection Board’s final Article 48 guidelines explain that third-country judgments and administrative decisions cannot automatically and directly be recognised or enforced in an EU Member State. A disclosure responding to a foreign authority must satisfy the applicable GDPR requirements, including an Article 6 legal basis and Chapter V conditions. This constrains lawful disclosure; it does not certify the security architecture of a provider or establish immunity from every competing legal demand. Guidelines 02/2024 on Article 48 GDPR, Version 2.1, executive summary and sections 3–5 — EDPB — Jun 2025. edpb.europa.eu
The Commission’s procurement framework makes a related distinction between levels of sovereignty. Its June 2026 clarification identifies data sovereignty, technological autonomy and full sovereignty as different assurance levels, alongside an assessment containing 48 criteria in eight categories. These are the Commission’s defined procurement measures, rather than a universal certification that automatically applies to all services sold by a successful company. The analytical implication is substantial: a service can meet a specified sovereignty requirement while retaining dependencies that would matter under a different threat model. A defensible procurement decision must identify the required level, the exact assessed service and the disruption against which the customer expects protection. Sovereign Cloud Framework explained — European Commission — Jun 2026. commission.europa.eu
Italy: qualification provides a basis for scrutiny
Italy’s framework offers an institutional mechanism for distinguishing infrastructure from the services delivered through it. Cloud Italia explains that the ACN catalogue identifies qualified SaaS, PaaS and IaaS services, their providers and qualification levels. It also distinguishes the qualification of privately supplied cloud services, involving an assessment before catalogue publication, from the compliance process for infrastructure and publicly operated services. The resulting analytical discipline is clear: the status of an underlying infrastructure cannot be used as a substitute for checking the status and scope of the purchased application service. Come usare il catalogo dei servizi qualificati — Cloud Italia, Department for Digital Transformation and ACN — undated; consulted Nov 2026. Cloud Italia
Italy’s opportunity is to turn qualification into informed demand for services whose responsibilities, continuity arrangements and exit conditions are contractually clear. The limitation is that catalogue eligibility answers a defined regulatory question, whereas technological substitutability requires additional operational evidence. For strategic users, the relevant purchasing decision must connect the classification of the workload to the exact service, contractual entity, administration model and recovery arrangements. This assessment therefore treats Italian qualification as an important governance instrument, while reserving judgments about broader autonomy for evidence concerning the service’s actual dependencies and tested behaviour.
France: stringent assurance coexists with implementation constraints
France provides a developed assurance model, alongside official evidence that adoption remains difficult. ANSSI explains that SecNumCloud assesses resilience against specified threats, including certain extraterritorial demands, and explicitly warns that qualification of a cloud offering does not determine the security of a customer’s digital service hosted upon it. Its explanation of qualification by composition also requires an application provider to enter the qualification process rather than simply inherit the status of its infrastructure supplier. FAQ avant de se lancer dans la qualification SecNumCloud — ANSSI — undated; consulted Nov 2026. ANSSI
The Cour des comptes reported in October 2025 that sovereign-cloud adoption by administrations remained limited, internal state clouds struggled to achieve sufficient scale, and government lacked a ministry-by-ministry map of sensitive data. These findings establish a documented implementation gap at the time of the audit; they should not be silently represented as a fresh measurement for every administration in November 2026. They nevertheless identify the practical requirements against which subsequent progress must be tested: data classification, migration execution, sufficient service scale and acceptable performance. France demonstrates that a demanding assurance doctrine can coexist with continued dependence in actual government systems. Les enjeux de souveraineté des systèmes d’information civils de l’État — Cour des comptes — Oct 2025. Cour des comptes
Germany: deployed alternatives reveal both feasibility and residual dependence
Germany supplies a particularly useful implementation example because the official record identifies completed migration, remaining exceptions and support provision. Schleswig-Holstein reported on 19 September 2026 that more than 200 State Chancellery employees were working on Linux, while approximately 20 workstations remained unmigrated because of technical dependencies, including specialist applications. The same announcement identified a completed Linux-support procurement involving Dataport and Gonicus, and described further rollout to other ministries and authorities as subsequent work. Staatskanzlei nutzt Linux – nächster Meilenstein auf dem Weg zur digitalen Unabhängigkeit in Schleswig-Holstein — Schleswig-Holstein State Government — Sep 2026. schleswig-holstein.de
This is stronger evidence of autonomy than a general commitment to open source: it identifies an operating environment and the maintenance relationship needed to sustain it. The exceptions are equally consequential. They show how specialist applications can preserve dependence after the general desktop environment has changed. The national lesson is therefore workload-specific. Migration can reduce particular dependencies, provided integration, user support and application compatibility are funded. The documented result concerns one administration; it cannot establish the migration status of Germany’s public sector as a whole.
United Kingdom: competition policy addresses dependence through customer choice
The United Kingdom requires separate treatment because its regulatory authorities and policy instruments differ from those of the EU. In its October 2026 cloud update, the Competition and Markets Authority reported that Amazon and Microsoft had taken steps to reduce switching and multi-cloud barriers, while customers continued to face material obstacles. It identified identity and access management across clouds and Kubernetes portability as areas for further work. It also described a provisional proposal to designate Microsoft’s business software ecosystem under the strategic market status regime; that procedural position must remain distinct from a final designation. Update on Cloud actions: Covering March–October 2026, summary, pp. 3–5 — CMA — Oct 2026. assets.publishing.service.gov.uk
The British evidence strengthens the report’s central distinction between supplier availability and effective freedom of action. Alternative providers create limited practical choice when identity systems, application licensing and migration engineering make switching prohibitively difficult. Competition measures can improve bargaining power and reduce dependence without creating domestic ownership of the underlying platform. Their success should consequently be measured through usable alternatives, completed transfers and reduced contractual or technical barriers.
European coordination is advancing; delivery remains the test
At EU level, the Commission adopted its Cloud and AI Development Act proposal on 3 June 2026, addressing research and innovation, capacity and autonomy. The European Parliament’s procedure record remained at “Awaiting committee decision” when consulted for this assessment. The proposal is therefore evidence of a legislative initiative, rather than an operative regulation whose intended effects have already occurred. Proposal for the Cloud and AI Development Act — European Commission — Jun 2026; Procedure 2026/0138(COD): Cloud and AI Development Act — European Parliament — current record consulted Nov 2026. Shaping Europe’s digital future
The Commission’s June 2026 Open Source Strategy also recognises that sustainable autonomy requires maintained assets, supporting communities and governance over technology choices. That combination identifies the mechanism through which a collection of suppliers could become a stronger ecosystem: common assets reduce duplication, maintenance capacity sustains them, and procurement creates recurring demand. The countervailing risk is fragmentation into nationally bounded projects with incompatible requirements and insufficient demand to support continued development. The principal judgment would strengthen if European buyers demonstrated repeatable migration, continued operation during supplier disruption and viable maintenance across borders. It would weaken if sovereign-labelled services expanded while their decisive control points remained technically or contractually inaccessible. Commission boosts open and interoperable digital ecosystems for public administrations — European Commission — Jun 2026. commission.europa.eu
Key Evidence Table
Monetary values below retain the currencies and reporting bases used by their issuers. Procurement ceilings, company revenue, installed equipment and policy projections are different measures and are not aggregated.
| Indicator | Value/status | Reference date | Definition/scope | Issuer | Exact source |
|---|---|---|---|---|---|
| EU sovereign-cloud procurement | Up to €180 million over six years; four contracts | April 2026 | Maximum procurement access for Union entities; not expenditure already incurred | European Commission | Commission advances cloud sovereignty through strategic procurement |
| Sovereignty assessment | 48 criteria in eight categories; distinct assurance levels | June 2026 | Commission procurement framework | European Commission | Sovereign Cloud Framework explained |
| OVHcloud commercial activity | €1,145.1 million total revenue; €255.1 million Public Cloud revenue | FY ended 31 August 2026 | Company-reported global group and segment revenue; nominal euros | OVHcloud | FY2026 results |
| JUPITER accelerator equipment | Approximately 24,000 NVIDIA GH200 Superchips | June 2026 account | Equipment in a European-operated computing system | EuroHPC JU | June 2026 systems update |
| Semiconductor ambition versus projection | 20% objective; 11.7% projection for 2030 | Assessment published 2025 | Share of global semiconductor value chain; projection is not an observed outcome | European Court of Auditors | Special Report 12/2025: Key facts and findings |
| Deployed Linux migration | More than 200 employees using Linux; approximately 20 workstations awaiting migration | September 2026 | Schleswig-Holstein State Chancellery; not statewide completion | Schleswig-Holstein Government | Staatskanzlei nutzt Linux |
| Cloud switching charges | Prohibited from 12 January 2027 under Article 29(1) | Prospective at dossier cut-off | Charges covered by the Data Act’s switching provisions; distinct from all migration-related customer expenditure | Bundesnetzagentur, explaining EU law | Data processing services and provider switching |
| Cloud and AI Development Act | Legislative proposal awaiting committee decision | Record consulted 16 November 2026 | Ongoing ordinary legislative procedure | European Parliament | Procedure 2026/0138(COD) |
The Data Act’s prohibition on switching charges is a consequential legal milestone, but it does not establish that applications, integrations and operational procedures can move without customer engineering work. The Bundesnetzagentur’s guidance distinguishes contractual switching requirements, technical transition arrangements and the withdrawal of provider switching charges. Data processing services and provider switching — Bundesnetzagentur — undated; consulted Nov 2026. Data processing services and provider switching
Competing Explanations
These hypotheses are competing accounts of Europe’s present position. Different services can exhibit different characteristics; the assessment does not force every workload into a single category.
| Hypothesis | Diagnostic support | Disconfirming evidence | Indicators | Current standing |
|---|---|---|---|---|
| A substantially autonomous ecosystem already exists across the essential stack. | Commercial providers, public procurement and deployed software alternatives demonstrate substantial capability. | Imported computing components, continuing switching barriers and differentiated sovereignty levels contradict a general claim of autonomy. | Demonstrated maintenance, replacement and continued operation across critical dependencies. | Too broad for the verified record. |
| A functioning European ecosystem exists, with bounded autonomy and uneven external dependence. | Commercial revenue, cross-border delivery arrangements and completed migrations establish operational substance. | Comprehensive replacement capability and disruption tolerance remain insufficiently established. | Repeatable exits, interoperable services, durable maintenance and diversified supply. | Best-supported explanation. |
| European digital sovereignty remains predominantly a commercial and political label. | Some claims rely on announcements, planned legislation or location-based assurances. | Operating services, recorded revenue, awarded procurement and completed migrations contradict a blanket dismissal. | Persistent failure to produce contractual controls, deployed results or usable alternatives. | Relevant to individual claims; inadequate as an overall explanation. |
Principal Gaps and Watch Indicators
Independent evidence of service control. Public announcements often describe intended processing boundaries without publishing the complete operational evidence. The decisive records are service-specific audit scopes, privileged-access logs, subprocessor schedules and documented emergency-access procedures. A substantiated discrepancy between contracted boundaries and actual administration would weaken the assessment of that service.
Continuity under upstream disruption. Installed capacity does not establish how long a provider can operate safely without external updates, replacement equipment or specialist support. Relevant evidence includes exercised continuity plans, maintenance rights, spare-parts arrangements and observed recovery results. Tolerance must be judged against the workload’s required operating period.
Portability demonstrated through completed transfers. The next test is successful reconstruction of a representative service elsewhere, including its identities, policies, configurations and necessary records. Relevant observations are elapsed transition time, internal labour, interruption, retained functionality and continuing security coverage. These are proposed assessment measures, not results already established.
Qualification scope and exceptions. Buyers should monitor the exact service record, its validity, covered operating model and dependencies on other qualified services. A material change in provider, administration or underlying service requires renewed assessment rather than continued reliance on an earlier label.
Economic sustainability. Evidence should distinguish recurring customer demand from grants, procurement ceilings and announced investment. Sustained maintenance and product development require durable financing; rapid capacity growth without sufficient demand can create a different continuity risk.
Implementation after legislative milestones. Adoption of new rules should be followed through implementing measures, procurement changes and observed customer outcomes. The Commission’s CADA proposal remains a legislative pathway at the cut-off, while the January 2027 switching-charge deadline supplies a defined near-term milestone.
Security performance alongside sovereignty. Geographic and jurisdictional control must be assessed alongside detection, recovery and resistance to supply-chain compromise. ENISA’s September 2026 threat assessment, covering events observed during 2025, identifies dependencies and third-party attacks as mechanisms through which incidents can spread. Sovereignty measures should therefore be evaluated for their contribution to resilience, without treating them as a substitute for effective security. Exploring the evolution of the cyber threat landscape: How dependencies weaken our digital resilience — ENISA — Sep 2026. ENISA
Visualisation — Testing a Sovereignty Claim
The following component presents an analytical verification sequence. Its branches distinguish separate findings; they do not assign a numerical sovereignty score or reproduce a certification scheme.
What does the sovereignty claim establish?
Assessment date: 16 November 2026. Qualitative decision sequence; no numerical scale. Apply each test to the exact purchased service.
Test 1 · Location and scope
Is the processing perimeter documented?
Identify production, recovery, administration and support.
Documented: proceed to the control test.
Missing: the claimed processing perimeter remains unestablished.
Test 2 · Authority and access
Who can administer or disclose information?
Examine legal entities, privileged access, subcontractors and procedures for authority requests.
Supported controls: proceed to continuity.
Location alone leaves operational and jurisdictional questions open.
Test 3 · Dependency and continuity
Can the service survive upstream disruption?
Examine maintenance rights, updates, replacement components and exercised recovery arrangements.
Demonstrated resilience: assess its duration and workload coverage.
Untested arrangements leave disruption tolerance unresolved.
Test 4 · Effective choice
Can the customer reconstruct the service elsewhere?
Test export, usable formats, identity migration, application operation and transition effort.
Successful transfer supports autonomy for the tested scope.
Export rights alone leave practical substitutability unresolved.
Interpretation: Record the demonstrated scope and remaining dependencies. A completed test supports a bounded finding, not universal independence.
Documentary basis: European Commission sovereignty framework, June 2026; EDPB Article 48 guidelines, June 2025; Bundesnetzagentur switching guidance, consulted November 2026. Verification questions are analytical recommendations.
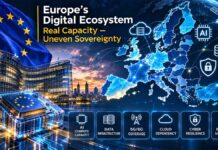
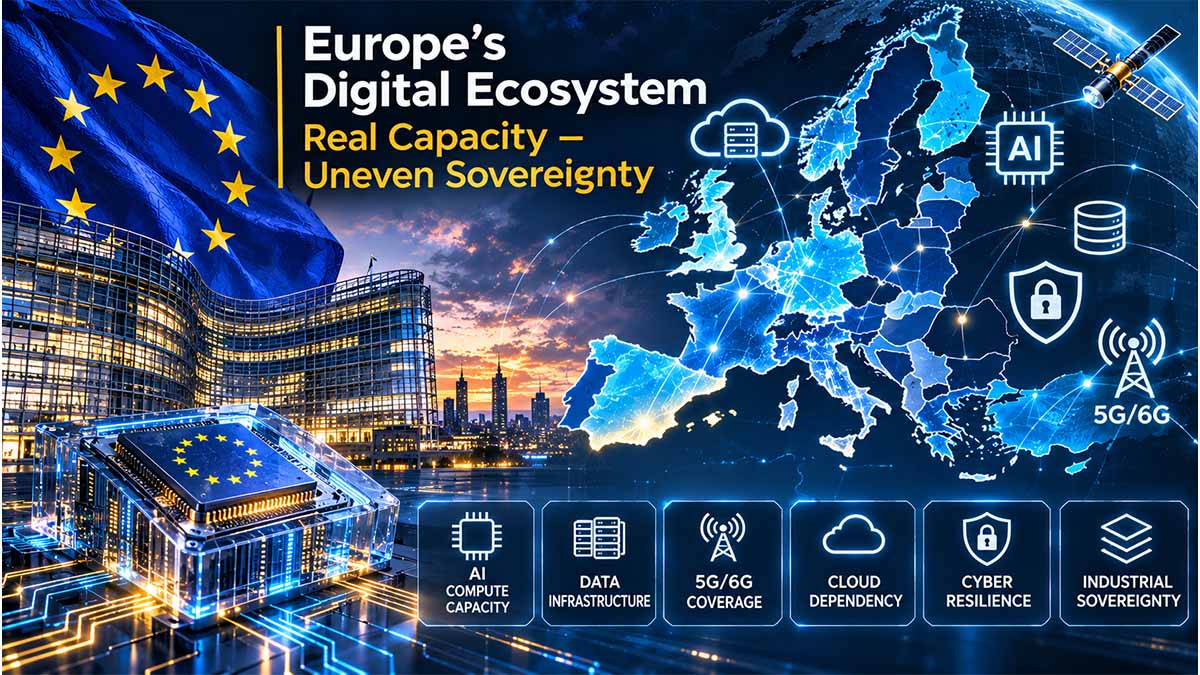
Europe’s Digital Ecosystem
Real capacity. Uneven sovereignty.
Evidence baseline: 16 November 2026. Europe has operating digital capabilities, but autonomy varies across services and dependencies.
| EU sovereign-cloud procurement | Up to €180 million over six years |
|---|---|
| OVHcloud FY2026 revenue | €1,145.1 million |
| JUPITER equipment | Approximately 24,000 NVIDIA GH200 Superchips |
The interactive dashboard requires JavaScript.
Pillar I — What Europe Actually Controls
Chapter 1 — Defining a European Ecosystem: Ownership, Authority and Operational Control
Europe’s capacity to govern a digital service must be established through the distribution of decision rights, technical privileges and maintenance responsibilities across that service. Corporate nationality provides an initial point of inquiry, but a strategic assessment must establish who can authorise changes, administer production systems, approve exceptional access, distribute software updates, retain essential intellectual property and sustain operation when a commercial or geopolitical relationship deteriorates. These powers can belong to different organisations operating under different jurisdictions. Consequently, an infrastructure provider can exercise effective control over buildings, networks and virtual machines while another entity controls application administration, a third supplies identity services and a fourth determines the availability of critical software updates. The analytical task is to establish the relationship between these authorities and the workload being protected. The resulting finding should specify the activity over which European control is demonstrable, the conditions under which that control can be exercised and the dependencies that remain outside the assessed perimeter.
Corporate location and corporate control answer different questions
Arm illustrates why European technological heritage, legal establishment and ultimate ownership require separate treatment. Its FY2026 annual filing states that, as of 21 May 2026, SoftBank Group beneficially owned approximately 86.4% of its issued and outstanding share capital, representing a majority of voting power. The filing explains the resulting controlled-company status and the shareholder’s ability, subject to the stated legal qualifications, to determine matters submitted to shareholder votes. This does not diminish the technical importance of Arm’s activities or establish that every customer relationship creates a particular security exposure. It establishes that an assessment of European corporate control cannot rely on British location or historical origin alone. For a strategic customer, ownership analysis should therefore identify voting rights, board appointment powers and contractual rights relevant to the supplied technology, while separately examining the jurisdiction and operational privileges of the entities involved. Annual Report on Form 20-F, sections on controlled-company status and major shareholders — Arm Holdings — May 2026. Arm®
A comparable distinction applies to joint ventures, licensed platforms and locally incorporated subsidiaries. Local incorporation identifies a legal entity; it does not establish the complete allocation of rights between that entity, its shareholders and its technology suppliers. A defensible examination should identify whether an upstream organisation can terminate a licence, withhold an update, veto a material change, appoint administrators or require access to systems. These are separate propositions requiring separate evidence. Equally, foreign shareholding should not be converted automatically into a claim of unrestricted technical access. A shareholder may possess extensive corporate influence without holding production credentials, while a small specialist subcontractor may hold operational privileges capable of affecting a sensitive workload. The meaningful distinction is between corporate influence and executable authority: the first concerns governance over the organisation, while the second concerns actions that particular people or systems can perform within the service. Neither can safely be inferred from the other.
| Dimension | Question that must be answered | Evidence capable of supporting the answer | Conclusion the evidence cannot establish alone |
|---|---|---|---|
| Legal establishment | Which entity contracts with the customer? | Registered entity, executed agreement, applicable terms | Ultimate ownership or production access |
| Corporate control | Who determines strategic decisions? | Voting rights, board powers, shareholder agreements where available | Access to customer information |
| Technology rights | Who can maintain, modify and redistribute essential components? | Licences, intellectual-property rights, maintenance agreements | Continued access to hardware or competent staff |
| Operational authority | Who can change the running service? | Privilege assignments, administrative procedures, change records | Lawfulness of every possible disclosure |
| Information access | Who can obtain intelligible customer information? | Architecture, access logs, key-management arrangements | Resistance to every future vulnerability |
| Continuity authority | Who can restore or continue the service? | Exercised recovery plans, dependency contracts, recovery credentials | Performance of an untested replacement |
| Exit capability | Who can reconstruct the workload elsewhere? | Completed migration, usable exports, verified replacement operation | Universal portability across all applications |
The table defines analytical requirements; it does not attribute these characteristics to any supplier without service-specific evidence.
Jurisdiction follows authority and control, not simply server location
The relevant United States statutory provision demonstrates why geographic hosting claims cannot settle the jurisdictional question. 18 U.S.C. §2713 requires providers within the provision’s scope to comply with the chapter’s preservation, backup and disclosure obligations for information within their possession, custody or control, whether that information is located inside or outside the United States. The provision is not a statement that every foreign-owned data centre is accessible to United States authorities, nor does it create an unlimited power to obtain information from any organisation anywhere. It makes possession, custody or control central to the specified obligations and removes physical location as a sufficient answer. A service assessment must therefore identify the relevant provider, the applicable legal process and the information that the provider can actually obtain. Required preservation and disclosure of communications and records, 18 U.S.C. §2713 — United States Code, text current through 10 November 2026. uscode.house.gov
For European customers, the practical consequence is that jurisdictional mapping should follow actual service relationships rather than stop at a hosting address. Production information, diagnostic packages, support tickets, administrative records and security telemetry may be governed through different processing relationships. Their treatment should be assessed according to the entities receiving them and the privileges required to perform the relevant task. A restriction covering production storage may leave a separate support workflow unresolved; a contractual commitment covering ordinary administration may require additional provisions for exceptional intervention. These are questions of scope and implementation. The purpose of the assessment is to identify whether the customer’s required boundary survives routine operation, incident response and service evolution. A supplier should receive credit for a boundary it can document and enforce, while a broader claim should remain unestablished until the corresponding evidence is available.
Encryption must be evaluated against the processing task
The decisive issue in encryption is whether an actor whose access is being restricted can obtain the information in intelligible form during the activity the customer has authorised. The EDPB’s supplementary-measures recommendations distinguish storage that does not require access to clear data from processing that does. Under its specified conditions, strong encryption with appropriately controlled keys can provide an effective supplementary measure for storage. In its separate clear-processing scenario, the Board explains that transport encryption and encryption at rest do not solve the identified problem where the importer holds the keys and must access unencrypted information. These findings concern the transfer scenarios and conditions described in the recommendations; they should not be generalised into a claim that every cloud service is unlawful or that later technical approaches are incapable of improving protection. Recommendations 01/2020, Annex 2, Use Cases 1 and 6, paragraphs 84 and 94–95 — EDPB — June 2021. edpb.europa.eu
A strategically useful assessment therefore distinguishes custody of keys from authority to cause their use, and both from access to the application after decryption. Customer-controlled keys can strengthen control over particular storage or disclosure scenarios, but the assessment must establish whether privileged operators can invoke decryption, impersonate an authorised application or retrieve information through an approved diagnostic process. The same discipline applies to claims that infrastructure operators cannot read application data: the claim may be well founded for a particular architecture, but its validity depends on the boundary between infrastructure administration and the application’s trusted computing environment. Procurement should consequently ask which actors can obtain intelligible information through normal operation, exceptional intervention and recovery. The evidentiary requirement is a description of the actual processing path and associated privileges, supported by the controls and records needed to verify it.
Qualification has a defined perimeter
France’s 12 August 2026 order, published on 14 August, formally approved version 3.2 of the SecNumCloud requirements under the specified national legal framework. Its stated scope concerns commercial cloud services supplied to the identified public bodies for processing particularly sensitive information whose compromise would have the consequences described in the instrument. The order demonstrates a concrete legal implementation step, rather than a general political endorsement of sovereign cloud. It does not mean that every service supplied by a qualified company falls within an identical assessed perimeter. Arrêté du 12 août 2026 portant approbation du référentiel d’exigences relatif aux prestataires de services d’informatique en nuage — French Government, Journal officiel — Aug 2026.
ANSSI’s explanation of qualification by composition is particularly relevant to layered services: using a qualified infrastructure can reduce duplicated evaluation, but an application supplier must still enter the qualification process to obtain its own relevant qualification. ANSSI also states that qualification of a cloud offering does not determine the security of a customer application hosted on it. These distinctions prevent assurance from being extended automatically across commercial packaging. FAQ avant de se lancer dans la qualification SecNumCloud, sections on composition and customer-service security — ANSSI — undated, consulted November 2026.
The decision consequence is that assurance should be represented as a chain of scoped findings rather than as a label attached to an entire corporate group. The customer must establish which service was assessed, which operating model was included, which underlying services support it and which responsibilities remain with the customer. Where several services are combined, their individual qualifications do not by themselves demonstrate that the combined configuration preserves the necessary boundary. Integration may introduce new administrative relationships, data flows or recovery dependencies. A credible ecosystem is therefore one in which assurance can be traced across these interfaces without assuming that an assessment of one layer automatically validates another.
Control assessment: verify corporate authority, operational privileges, access to intelligible information and continuity rights separately.
Key judgments
A European ecosystem should be assessed through the rights and operational powers available for the particular service. Ownership, jurisdiction, access and continuity contribute different forms of control, and deficiencies in one cannot automatically be compensated by strength in another. Qualification provides valuable scoped assurance, while its extension to additional applications or operating models requires a corresponding assessment.
What would change the assessment
The assessment of a service would strengthen with documented limits on upstream intervention, verified administrative separation, demonstrable rights to maintain essential components and recovery exercises covering the relevant disruption. It would weaken where a claimed European boundary excludes decisive support, update or recovery relationships, or where an assurance claim extends beyond the service actually assessed.
Open official record
The consequential records are service-specific qualification decisions and annexes, applicable public procurement specifications, corporate disclosures identifying control rights and published audit findings where available. Detailed privilege assignments, shareholder arrangements and maintenance contracts may be non-public; their absence from the public record limits the conclusion that can be drawn without establishing that the corresponding safeguards do not exist.
Chapter 2 — Delivered Capabilities: Cloud, Cybersecurity, Software and AI Computing
Europe’s delivered capability is most accurately understood as a portfolio of operating services, deployed software, allocated computing resources and projects at different stages of completion. The strategic assessment must preserve those stages because they establish different kinds of freedom of action. A commercially operating service demonstrates an ability to serve customers; an accepted computing system demonstrates installed capability; a signed procurement contract establishes obligations concerning future delivery; and a research programme establishes an organised attempt to develop technology. Each can contribute to an ecosystem, but their contribution cannot be measured by counting announcements as though they were equivalent assets. The following evidence therefore concentrates on the composition of operating activity, the service mechanisms surrounding computing infrastructure and the distinction between capabilities available to users and capacity expected later.
Commercial cloud is a differentiated business
OVHcloud’s FY2026 segment disclosure shows why total cloud-provider revenue should not be interpreted as a uniform measure of hyperscale substitution. The company reported €690.4 million in Private Cloud revenue, €255.1 million in Public Cloud and €199.7 million in Webcloud, representing 60.3%, 22.3% and 17.4% of its reported business respectively. Public Cloud revenue increased 18.9% on a like-for-like basis. These categories demonstrate different sources of commercial demand and capability; they do not establish an equivalent portfolio to every service offered by a larger global platform. All 2026 targets achieved, excellence in execution, focus on value creation, revenue by product segment — OVHcloud — Oct 2026.
Germany’s IONOS provides a second commercial reference. Its Q3 2026 results presentation reported €1,054.6 million in revenue from continuing operations for the first nine months of 2026, compared with €980.2 million in the comparable 2025 period, an increase of 7.6% as reported and 8.4% excluding currency effects. The presentation separately reported 16.9% constant-currency growth in Cloud Solutions. These figures establish business activity and growth within the company’s reporting definitions, rather than a market share for sovereign cloud. Q3 2026 Results Webcast, financial overview and guidance comparison — IONOS Group — Nov 2026. corporate.ovhcloud.com
The industrial implication is that European commercial capability should be evaluated by service category, customer requirement and operational maturity. A provider with a substantial dedicated-server business can offer a credible foundation for workloads that benefit from that model without demonstrating the same depth in managed analytics, application integration or specialised development services. Conversely, a smaller provider may supply a sufficiently mature alternative for a defined workload even where it cannot reproduce the complete catalogue of a global platform. Strategic procurement should therefore establish the functions actually required and the service levels needed to sustain them. The decisive comparison concerns the ability to run the customer’s application with acceptable security, performance, support and continuity. A catalogue-wide comparison can obscure workable alternatives by treating every unused proprietary feature as a mandatory requirement, while an excessively narrow infrastructure comparison can understate the integration work required to replace a managed platform.
Cybersecurity capability includes the service organisation around the software
Bitdefender’s Sovereign Acceleration Program extends its declared EU boundary to customer and configuration data, events, telemetry and information collected for customer support. This wider scope is consequential because it addresses processing associated with operating and supporting the security service, rather than describing hosting alone. The announcement also identifies partnerships involving OVHcloud and secunet. These are supplier statements establishing the declared programme and its intended service perimeter; they do not constitute an independent measurement of detection performance, incident-response quality or every customer configuration. Bitdefender Launches Sovereign Acceleration Program to Advance European Data Sovereignty Initiatives — Bitdefender — 2026.
The relevant capability extends beyond possession of a detection engine. A security service must sustain rule updates, investigate ambiguous events, maintain trained personnel, manage false positives and execute authorised containment without losing visibility into the affected environment. A European processing boundary can make these relationships easier to govern, but it does not establish their effectiveness. The appropriate examination should connect a representative incident to the records produced during collection, analysis, escalation and response, while distinguishing routine operations from exceptional specialist intervention. The ecosystem contribution is strongest when infrastructure, security technology and managed operations can be combined under responsibilities that a customer can audit and exercise. It is weaker where a nominally integrated offer leaves uncertainty over which party owns the incident decision, which organisation can access the evidence or how protection continues during a contractual transition. These are proposed operational tests; the public announcements do not establish their results.
AI software requires deployment-specific analysis
Mistral’s documentation offers a useful technical distinction between where code executes and where the wider platform operates. Its deployment guide describes self-hosted workers running on customer infrastructure while Mistral provides orchestration, and explicitly states that self-hosting a deployment is different from running the whole Studio platform on the customer’s premises. The documentation therefore supports several deployment arrangements rather than a single general sovereignty claim. An assessment must identify which arrangement the customer is purchasing and which platform functions remain external to the local workers. Deployments, sections on deployment modes and on-premises distinction — Mistral documentation — undated, consulted November 2026. Mistral Docs
This distinction matters because an AI application may execute tools close to its data while relying on another environment for routing, scheduling, observation, secrets or model inference. Local execution of one component can therefore provide meaningful control without establishing independence of the complete application. The assessment should identify the inference endpoint, execution environment, orchestration service and operational records separately, then establish which connections are essential to continue processing. A European model developer can contribute valuable technology under several delivery models, each with different implications for customer control. The service’s actual architecture and applicable licences determine whether a customer can continue inference, retain operational records, modify its application or replace an upstream function. Corporate origin remains relevant, but it cannot replace this deployment-specific analysis.
Public computing becomes an ecosystem through access and support
EuroHPC’s AI Factory service catalogue demonstrates that the intended institutional capability includes user guidance, access mechanisms, technical support, data and software services, training and project assistance. Its descriptions identify different sectoral and service emphases: HammerHAI focuses on industrial users including engineering and automotive applications; the BSC AI Factory includes training and access support; and Italy’s IT4LIA combines the existing Leonardo environment with a forthcoming AI-optimised system at Bologna. These are programme descriptions and must retain their respective implementation status. They establish the service model being assembled around computing infrastructure, rather than a common audited maturity level across all sites. AI Factories Services — EuroHPC JU — undated, consulted November 2026.
The strategic significance of this service layer is that computing ownership and computing usability are different capabilities. An organisation may possess a technically suitable application and still lack the expertise to prepare data, optimise execution, manage distributed workloads or validate results. Support institutions can reduce those barriers and make infrastructure accessible to a wider industrial base. Their contribution should be assessed through completed onboarding, accepted projects, delivered assistance and sustained use, rather than through installed equipment alone. Access conditions also matter: research allocations, startup programmes and commercial production services can serve different purposes and impose different constraints. A public computing network can therefore expand Europe’s capacity to develop applications without necessarily replacing the contractual, availability and support arrangements required for every production workload.
Existing LUMI services and future LUMI-AI capacity are separate assets
EuroHPC’s 31 August 2026 announcement states that the LUMI AI Factory had been providing computing resources and services to European SMEs and startups since April 2025 using the existing LUMI system. The same announcement records a procurement contract with Bull for a new LUMI-AI supercomputer, with a €387.8 million budget covering acquisition, delivery, installation and maintenance, funded 50% by EuroHPC and 50% by the consortium. Installation and user availability were expected in 2027. The planned system uses AMD processors and accelerators. These facts establish operating services alongside contracted expansion, while preserving an external component dependency. EuroHPC JU Signs Contract to Deploy the LUMI-AI Supercomputer — EuroHPC JU — Aug 2026. eurohpc-ju.europa.eu
The distinction matters for policy timing. Existing services can support present projects, while contracted equipment contributes to a future capacity assessment subject to delivery, acceptance and operational integration. Neither the investment value nor the processor specification proves the amount of useful capacity a particular customer will receive. That requires access allocations, workload performance and service arrangements. The European ecosystem’s strength in this case lies partly in the coordination of funding, hosting, procurement and user support across several countries. Its technological autonomy remains a separate question determined by component availability, software support and maintenance rights. This is a concrete example of institutional integration advancing faster than comprehensive independence across the underlying technology stack.
British delivery adds capacity without removing external component reliance
A ministerial answer published by the UK Parliament on 27 April 2026 states that AIRR became operational in July 2025, with approximately 5,448 NVIDIA accelerator chips at Isambard-AI and 1,024 Intel accelerator chips at Dawn, with those counts unchanged in April 2026. The University of Bristol’s June 2026 technical account identifies Isambard-AI’s HPE Cray EX platform, NVIDIA GH200 architecture and HPE Slingshot interconnect. These records establish a publicly accessible national capability with identifiable external technology suppliers. Artificial Intelligence: Infrastructure, written answer — UK Department for Science, Innovation and Technology / Parliament — Apr 2026; Inside the UK’s most powerful AI supercomputer — University of Bristol — Jun 2026.
The British example should be incorporated into a geographically European capability assessment while remaining institutionally distinct from EU programmes. Its existence expands the region’s research and industrial computing base, but access rights and allocation mechanisms must be established under the applicable British arrangements. It also demonstrates why hardware counts should not be used as a common performance ranking across different systems: accelerator generations, interconnects, software environments and workloads affect useful output. The relevant comparison concerns what a user can obtain, under what conditions and with what support. A system can deliver important national freedom of action through domestic allocation and operation while retaining substantial dependence on imported processors, network technology and software.
Capability status: distinguish operating services, contracted delivery, procurement calls and research objectives.
Key judgments
Europe can demonstrate commercial delivery, public computing access and service organisations capable of supporting users. Its capability portfolio nevertheless contains operating assets, contracted expansion and development programmes that must remain distinct. The strongest evidence of an ecosystem concerns the combination of technology with procurement, maintenance, access and user support; the weakest generalisations arise when those relationships are inferred from investment announcements or hardware ownership.
What would change the assessment
The assessment would strengthen with accepted deliveries, published access results, completed industrial projects and evidence that applications can move between supported European environments without losing essential functionality. It would weaken if new equipment remained inaccessible to intended users, service support proved insufficient or nominal alternatives required continued dependence on an unexamined external platform.
Open official record
Priority records include acceptance notices, access-call outcomes, service catalogues identifying availability, published utilisation measures with clear denominators and procurement amendments affecting delivery. The public record should distinguish installed infrastructure from allocated customer capacity and development access from production-service commitments.
Chapter 3 — Dependency Architecture: Chips, Platforms, Maintenance and Infrastructure
Europe’s most consequential digital dependencies are the upstream capabilities whose interruption would prevent a service from being repaired, secured, expanded or replaced within the customer’s required operating period. Their significance cannot be established by counting foreign components or calculating an unsupported percentage of European content. An imported component may remain usable for an extended period without external intervention, while a comparatively small licensing, identity or maintenance dependency may affect service availability much sooner. The relevant assessment therefore combines the dependency’s function, concentration, legal and technical rights, replacement difficulty and time to operational consequence. This chapter examines the mechanisms that connect hardware, software, maintenance and physical infrastructure, while preserving the distinction between exposure, a plausible disruption pathway and an observed interruption.
Semiconductor strength can coexist with concentrated vulnerability
ASML’s 2025 IFRS annual report identifies reliance on critical single-source components and describes Carl Zeiss SMT as its sole supplier of specified essential optical components. It states that a prolonged inability to maintain that supply could prevent ASML from continuing its business. The report also identifies manufacturing activities across the Netherlands, Germany, the United States, South Korea and Taiwan, and warns that alternative production capacity may be unavailable after a major disruption. These are company-disclosed risks, rather than evidence that such a disruption is occurring. Annual Report 2025, risk factors concerning critical suppliers and manufacturing facilities, pp. 68–69 — ASML — 2026. ourbrand.asml.com
This evidence has two strategic implications. First, Europe’s possession of an important position within the semiconductor industry does not establish control over all the activities needed to deliver finished computing systems. Second, dependencies within Europe can be strategically concentrated even where they do not create an external-jurisdiction problem. A European supplier can strengthen regional industrial capability and simultaneously constitute a single point of industrial vulnerability. The policy objective should therefore identify the specific dependency being addressed: reducing exposure to external authority, increasing supply resilience, preserving technical competence or securing production capacity. These objectives overlap but are not interchangeable. A procurement or industrial-policy measure that improves one may leave another unchanged, and additional geographic concentration can create new exposure even while increasing the European share of an activity.
Processor design autonomy requires a complete route to usable systems
EuroHPC’s DARE programme addresses part of the processor problem through a RISC-V-based hardware and software initiative. The project record describes a six-year framework partnership running to 2030, with development objectives including one general-purpose processor and two accelerators, alongside a supporting HPC and AI software stack. The record specifies design, development and tape-out objectives; it does not establish that these components are already available as production replacements in European computing facilities. DARE, project objectives and framework partnership — EuroHPC JU — undated, consulted November 2026.
The programme’s strategic contribution should be evaluated along the route from architectural freedom to deployable systems. An open instruction set can improve the freedom to implement a design, but the finished capability still requires verified processor implementations, manufacturing, packaging, memory integration, boards, firmware, compilers, libraries and system support. A successful design milestone therefore resolves a narrower question than reliable production availability. The ecosystem becomes materially stronger when European organisations can integrate those activities, maintain the resulting software and deliver systems that meet user requirements. Conversely, a programme can generate important intellectual property and engineering competence without yet providing a practical substitute for an installed accelerator platform. The appropriate indicators are successful technical milestones, independently checkable performance under defined workloads, production commitments and accepted integration into supported systems.
Software dependencies can survive infrastructure diversification
The UK CMA’s October 2026 cloud update identifies identity and access management across clouds and Kubernetes portability as areas requiring further work. Its discussion shows why adding providers or moving data does not necessarily remove the controls that constrain operational choice. A workload can be distributed across several infrastructures while still depending on a common identity service, licensing arrangement or application interface. The regulator’s findings concern the assessed UK cloud market and should not be converted into a measured dependency rate for the EU. Update on Cloud actions: Covering March–October 2026, summary and next areas of work — CMA — Oct 2026.
The analytical consequence is that supplier diversification must be examined at the level of shared dependencies. Two infrastructure contracts do not necessarily provide independent recovery if both environments rely on the same authentication authority, administrative workstation, backup-management service or software distribution channel. Equally, shared technology does not automatically invalidate diversification: its significance depends on whether the relevant failure could affect both environments and whether independent recovery remains possible. A credible continuity assessment should therefore identify common control points and establish how credentials, configuration and required software would be recovered if the normal administration path were unavailable. The proposed test is functional: demonstrate that the alternative environment can be administered and restored under the disruption being considered. Merely listing several suppliers establishes commercial diversity, while operational independence requires evidence about their common dependencies.
| Dependency layer | Potential interruption mechanism | Immediate question | Evidence needed to assess resilience |
|---|---|---|---|
| Processor and accelerator supply | Replacement or expansion becomes unavailable | Can the existing workload continue, and for how long? | Installed condition, spares, maintenance coverage, compatible alternatives |
| Firmware and essential updates | Security or compatibility maintenance is interrupted | Who can approve, validate and distribute updates? | Update rights, signing arrangements, supported lifecycle |
| Identity and privileged access | Normal authentication or administration becomes unavailable | Can recovery proceed through an independent authority? | Exercised emergency access and protected recovery credentials |
| Managed application interfaces | A replacement cannot reproduce required behaviour | Which functions must be rebuilt or adapted? | Application inventory and completed compatibility testing |
| Software maintenance | Required expertise or dependencies cease to be available | Can the organisation sustain a supported version? | Maintainer capacity, build process, component inventory |
| Physical infrastructure | Power, cooling, connectivity or replacement equipment is constrained | Which service commitments remain achievable? | Site-specific arrangements and exercised recovery |
| Operational knowledge | Critical procedures depend on unavailable specialists | Can another authorised team operate the system? | Documentation, cross-training and observed handover |
These are disruption mechanisms and assessment requirements, not claims that every listed failure has occurred.
Maintenance determines how long autonomy lasts
The distinction between deployment and sustainment is central to strategic autonomy. A service may continue functioning after access to an upstream supplier is interrupted, yet gradually lose the ability to correct vulnerabilities, replace failed equipment or support new application requirements. The relevant assessment must therefore identify several time horizons: continued operation in the existing configuration, secure operation as vulnerabilities emerge, restoration after a failure and adaptation to changing demand. These are analytical categories rather than standardised durations. Their practical value is that they prevent a successful short-duration demonstration from being represented as indefinite independence. A disconnected system that processes a test workload establishes a specific result; it does not prove that the operator can maintain the software, validate future patches or rebuild the environment after equipment loss.
Open software can improve this position by making inspection, adaptation and maintenance possible under the applicable licence, but those rights require competent organisations capable of exercising them. The Commission’s June 2026 Open Source Strategy accordingly identifies maintained assets, supporting communities and governance as mutually reinforcing requirements. Its significance is the recognition that the availability of code and the existence of an operational maintenance ecosystem are different conditions. Commission boosts open and interoperable digital ecosystems for public administrations — European Commission — Jun 2026.
For a strategic customer, the maintenance question should establish whether the organisation or its authorised suppliers can reproduce builds, track essential components, validate changes and sustain supported operation. A nominal right to modify code is of limited practical value if no competent team can exercise it within the required time. Conversely, a commercially supplied maintenance service can provide substantial operational resilience where it offers durable rights, effective handover and workable alternatives. The quality of the ecosystem is therefore demonstrated partly by the depth of organisations capable of assuming responsibility when an existing supplier withdraws. This is a more demanding test than identifying the original author or the licence attached to a repository.
Physical infrastructure constrains digital freedom of action
The IEA’s 2026 update projects global data-centre electricity consumption increasing from 485 TWh in 2025 to approximately 950 TWh in 2030, and identifies bottlenecks across the value chain as constraints on more aggressive near-term growth. These are global estimates and projections, not measurements of European sovereign infrastructure or a forecast of shortages at a specific European site. They establish that computing expansion must be assessed against physical delivery constraints. Key Questions on Energy and AI, executive summary — International Energy Agency — 2026. IEA
OVHcloud’s FY2026 disclosure provides a narrower company example: it reported 250 MW of connected power capacity, of which 140 MW was in operation. These measures should remain separate. Connected capacity describes an infrastructure position, while the operating figure describes a different state of use; neither directly measures available application output for an individual customer. All 2026 targets achieved, excellence in execution, focus on value creation, infrastructure capacity discussion — OVHcloud — Oct 2026.
The strategic mechanism is that a legally autonomous provider cannot deliver additional useful computing without the required electrical, thermal, network and equipment conditions. Likewise, spare capacity at one site may not be an immediate substitute for a constrained site if the workload requires particular connectivity, contractual arrangements or data-handling conditions. Physical diversification should therefore be tested against the service’s actual recovery requirements. The relevant evidence is site-specific: power availability, recovery capability, independent connectivity where required and the ability to obtain compatible replacement equipment. A regional capacity aggregate may be useful for industrial planning, but it cannot establish whether a particular organisation can recover a critical service within its required period.
Announced infrastructure must not be counted as delivered independence
EuroHPC launched its AI Gigafactories call on 30 July 2026 to select consortia for facilities combining computing, storage, networks, cloud access and specialised support. The published call stated a submission deadline of 12 November 2026, followed by competitive evaluation. At this dossier’s cut-off, that launch record establishes a procurement pathway and intended service model; it does not establish completed facilities or accepted customer capacity. The EuroHPC Joint Undertaking launches the AI Gigafactories Call — EuroHPC JU — Jul 2026.
The programme should consequently be tracked through successive commitments: selection, financing, enforceable delivery obligations, physical completion, acceptance and service availability. Each step can reduce a particular uncertainty, but none should be skipped in the assessment. The same discipline applies to autonomy: a facility built and operated in Europe establishes an important geographic and operational position, while the rights and dependencies associated with its processors, software and maintenance determine additional aspects of control. A genuinely stronger ecosystem would connect these infrastructure projects to domestic and cross-border users, competent maintenance organisations and development pathways capable of reducing specific dependencies over time. The appropriate measure is the expansion of demonstrated options available to European customers, with the residual constraints made explicit.
Upstream disruption can affect immediate operation, secure maintenance and future expansion differently. Each requires a separate recovery test.
Key judgments
The dependency that matters most is the one capable of preventing required operation, maintenance or recovery within the relevant period. European industrial strengths can coexist with concentrated suppliers, external components and shared software controls. Research and infrastructure programmes can reduce these constraints, but their contribution must be assessed through delivered milestones and usable operational alternatives.
What would change the assessment
The assessment would strengthen with qualified replacement components, accepted European processor systems, independently maintainable software environments and recovery exercises that remove shared control points. It would weaken if nominally diversified services relied on the same inaccessible administration, update or recovery path, or if infrastructure expansion lacked the physical resources and support required to become operational.
Open official record
The decisive records include accepted procurement deliveries, processor integration results, supported-component lifecycles, published supplier-risk disclosures and site-specific infrastructure commitments. Operational recovery exercises and detailed maintenance rights are frequently non-public. Public investment totals cannot resolve those gaps; they establish the resources committed to a pathway, while the pathway’s effect on customer freedom of action requires subsequent evidence.
Pillar II — Institutions, Markets and National Implementation
Chapter 4 — Legal Sovereignty: Jurisdiction, Qualification, Procurement and Exit
European legal sovereignty becomes operationally meaningful when institutions can translate their authority into enforceable purchasing conditions, continuing supervision and an executable ability to change service arrangements. The central institutional question is therefore how a public administration, regulated enterprise or supervisory authority converts a legal requirement into observable conduct throughout the life of a digital service. A purchasing organisation must determine which rules apply to its activities, distinguish mandatory obligations from voluntary assurance, allocate responsibilities among the parties and preserve sufficient evidence to demonstrate compliance after the initial purchase. These functions require administrative and technical competence within the customer organisation. They also require contracts that remain effective when a provider changes its operating model, introduces a subcontractor, modifies a service or encounters financial difficulty. The existence of European legislation provides a framework for exercising authority; the effectiveness of that authority depends on whether institutions can specify, verify and enforce the relevant conditions.
Sectoral regulation preserves responsibility within the customer
The Digital Operational Resilience Act establishes a particularly clear allocation of responsibility in the financial sector. Article 28(1)(a) provides that financial entities remain responsible for their applicable obligations when using third-party ICT services; Article 28 also requires relevant contractual registers and, for services supporting critical or important functions, documented exit arrangements. Article 29 addresses concentration and substitutability, while Article 30 specifies contractual requirements, including service descriptions, processing locations and provisions concerning access, recovery and termination. These obligations establish a governance relationship between the financial entity and its providers rather than transferring regulatory responsibility to a supplier. Regulation (EU) 2022/2554, Articles 28–30 — European Parliament and Council — Dec 2022. eur-lex.europa.eu
The practical consequence is that a provider’s European establishment, security certification or sovereign-service designation cannot complete the financial entity’s own assessment. The institution must connect the purchased service to the business function it supports, establish how disruption would affect customers and identify whether the proposed arrangement increases a concentration that is difficult to reverse. A register that lists contractual counterparties without identifying the functions they support can satisfy an administrative need while providing limited operational insight. Conversely, a technically detailed architecture that is disconnected from contractual rights may leave the institution unable to obtain information or assistance when it needs them. Effective supervision requires these records to converge: the contractual service, its operational dependencies, its business significance and the authority to inspect or exit must refer to the same arrangement. This creates a substantive institutional demand for European suppliers able to provide transparent service boundaries and usable evidence, while imposing comparable responsibilities on customers selecting them.
NIS2 introduces a different, broader framework whose obligations must be understood through its scope and national implementation. The Commission describes requirements addressing cybersecurity risk management, incident reporting, national strategies and supply-chain security across an expanded range of sectors. Its institutional effect is to make the security of supplier relationships part of organisational governance, rather than an issue confined to the technical performance of individual products. A claim that a service supports NIS2 compliance should consequently identify the controls and evidence it supplies to the customer’s applicable responsibilities. It should not imply that purchasing the service establishes compliance for the organisation as a whole. NIS2 Directive: securing network and information systems — European Commission — current guidance consulted November 2026.
Public procurement can evaluate strategic value within legal constraints
European public procurement law provides mechanisms for evaluating more than the initial invoice. Under Articles 67 and 68 of Directive 2014/24/EU, award evaluation can use cost-effectiveness and life-cycle costing, while qualitative criteria must remain linked to the subject matter and capable of effective verification. The authority must disclose the relevant criteria and, where applicable, the method used to assess life-cycle costs. These provisions provide a basis for examining measurable service characteristics and lifecycle consequences; they do not create an unrestricted entitlement to select a supplier according to an undefined political preference. Directive 2014/24/EU, Articles 67–68, consolidated text of 1 January 2024 — European Parliament and Council. eur-lex.europa.eu
For a strategic digital procurement, the important distinction is between an eligibility requirement, an award criterion and a contract-performance obligation. An eligibility requirement determines whether an offer can be considered; an award criterion differentiates compliant offers; a performance obligation determines what the successful provider must continue doing after selection. Institutions weaken their position when these functions are confused. A continuity property that is essential to the workload should not depend solely on a small discretionary award advantage, while a characteristic assessed during competition may lose practical value if the contract permits its subsequent removal without an effective remedy. Similarly, a supplier’s general qualification should not replace evaluation of the exact service configuration. Procurement design should therefore identify which requirements are indispensable, how additional value will be evaluated and which evidence must remain available throughout delivery. The objective is an auditable relationship between the public need and the purchased capability.
Italy’s procurement practice supplies a concrete example of this relationship. In pre-litigation opinion No. 103 of 24 March 2026, ANAC examined cloud-service requirements and treated the relevant ACN framework as part of a binding body of rules. In the circumstances examined, it considered that required certifications could operate as participation conditions where the contracting authority had demanded possession at the tender stage. The opinion concerns that dispute and should not be represented as a universal finding that every qualification must always be held at the same procedural moment. Its significance is that cloud-assurance requirements can have substantive procurement consequences rather than serving only as descriptive catalogue information. Parere di precontenzioso n. 103 del 24 marzo 2026 — Autorità Nazionale Anticorruzione — Mar 2026.
| Contract function | Institutional purpose | Evidence to specify | Consequence of an incomplete requirement |
|---|---|---|---|
| Service identification | Establish what is actually being purchased | Service name, operating model, included features and contractual entity | Assurance may refer to a different configuration |
| Continuing qualification | Preserve the required assurance perimeter | Applicable record, validity, change notification and consequences of loss | A compliant award can evolve into an unsuitable service |
| Audit and inspection | Permit continuing verification | Relevant records, access arrangements, audit scope and response obligations | The customer may retain responsibility without sufficient visibility |
| Subcontracting control | Govern changes in the delivery chain | Permitted activities, material changes, notification and applicable remedies | Important processing relationships can change after selection |
| Incident cooperation | Connect technical response with institutional authority | Escalation responsibilities, assistance and evidence availability | Delayed decisions or incomplete incident records |
| Exit preparation | Preserve future choice | Export scope, interfaces, assistance and transition responsibilities | A contractual right may remain difficult to exercise |
| Termination and residual data | Complete the relationship safely | Retrieval, deletion, retained copies and applicable retention obligations | Information or operational dependence can persist after termination |
This matrix is an analytical specification framework. Applicable legal requirements depend on the procurement, service and sector concerned.
Exit law establishes a process with defined qualifications
The Data Act gives switching a more explicit contractual structure. Article 25 requires written provisions covering the relevant rights and obligations, establishes a maximum notice period of two months and ordinarily a maximum transitional period of 30 calendar days. Where the latter is technically unfeasible, the provider must notify the customer within 14 working days, justify the difficulty and identify an alternative period not exceeding seven months. The Article also provides for a customer-requested extension and a minimum retrieval period after transition. These provisions should be read with their statutory scope and exceptions; they do not establish a universal guarantee that every complex application can be reconstructed elsewhere within 30 days. Regulation (EU) 2023/2854, Article 25 — European Parliament and Council — Dec 2023. eur-lex.europa.eu
The institutional advance is that exit becomes a service-governance process with responsibilities before, during and after the transfer. The customer must identify the information and digital assets required for continuity, the destination environment and the functions that must remain available during transition. A successful transfer of files is insufficient where the receiving environment cannot interpret the exported records or reproduce the required application behaviour. Conversely, a complex transition should not be used to obscure information that can be transferred promptly or to leave responsibilities undefined. Public bodies and regulated enterprises should therefore distinguish the legal entitlement to switch, the provider’s required cooperation and the customer’s own engineering responsibilities. This distinction also improves competition: suppliers can compete on the quality of their transition support and the usability of their exports, provided those characteristics are specified in a manner that customers can verify.
A recent implementation instrument makes this more concrete. Commission Recommendation (EU) 2026/2394 of 29 October 2026, published on 6 November, contains non-binding model terms and cloud contractual clauses, including provisions on switching and exit and a separate annex on termination. The switching material addresses planning, testing, data and digital assets, timing and responsibilities. Its legal status matters: the recommendation provides optional contractual tools, while the applicable obligations derive from the legislation and the parties’ binding arrangements. Its clauses must not be confused with the GDPR standard contractual clauses used for international personal-data transfers. Commission Recommendation (EU) 2026/2394, Annexes VI–VII — European Commission — Oct 2026, published Nov 2026.
Contract governance: define requirements, verify delivery, monitor changes and prepare exit before dependence becomes difficult to reverse.
Key judgments
Legal sovereignty requires institutional capacity to exercise rights throughout service delivery. Procurement, qualification, supervision and exit perform different functions and should be connected explicitly. A customer can remain legally responsible while lacking the information or technical preparation needed to discharge that responsibility; a credible European service ecosystem must help close that gap through transparent and usable contractual arrangements.
What would change the assessment
The assessment would strengthen where contracting authorities publish verifiable requirements, monitor material changes and demonstrate workable transitions. It would weaken where assurance is assessed only at award, responsibilities remain divided across inconsistent documents or exit provisions have no corresponding operational preparation.
Open official record
The most consequential records are procurement specifications, contract-performance conditions, published qualification decisions, supervisory findings and documented transition outcomes. Where contracts or audit reports are non-public, a public claim of compliance should remain limited to the evidence actually disclosed.
Chapter 5 — Industrial Economics: Scale, Investment, Demand and Sustainable Supply
The economic test of a European digital ecosystem is whether suppliers can fund continuing product development, infrastructure renewal and reliable service from a durable combination of customer demand and appropriately structured finance. Investment announcements establish an intention to allocate resources, but industrial autonomy requires organisations that can sustain the resulting capability after construction, initial deployment or public support. This distinction is particularly important in cloud and AI infrastructure because the economic burden includes equipment replacement, software development, specialist personnel, energy, network operation and the cost of keeping capacity available before demand fully materialises. A strategic assessment must therefore examine the relationship between demand, utilisation, margins, financing and reinvestment. It should also distinguish the activities public intervention is intended to support: research, first industrial deployment, customer adoption and recurring service delivery have different economic mechanisms and should not be treated as interchangeable forms of expenditure.
Scale affects the resources available for continuous development
Amazon reported $128.7 billion in AWS segment sales and $45.6 billion in AWS operating income for calendar year 2025. These figures describe a global business and are neither European cloud expenditure nor a sovereign-cloud market estimate. Their relevance is the scale of recurring commercial activity available to support a broad platform. They should not be converted into a simple ratio against European providers reporting different product portfolios, fiscal periods and currencies. Amazon.com Announces Fourth Quarter Results, full-year 2025 segment results — Amazon — Feb 2026.
The competitive mechanism is cumulative. A provider serving a large recurring demand base can distribute product-development and operating costs across more customers, invest in specialised functions and sustain a wider range of integrations. Customers can then obtain additional functions within an established commercial relationship, reinforcing the appeal of the platform. Smaller suppliers can compete successfully within particular service categories, but expanding beyond those categories requires finance and credible demand for the additional capability. The consequence for European industrial policy is that the existence of technically competent suppliers does not resolve the scale problem. The relevant question is which combinations of services and customers can support sustainable expansion, and which forms of coordination reduce the cost of building and maintaining alternatives. A strategy that requires every supplier to reproduce an entire global platform risks dispersing resources across functions for which it cannot establish sufficient demand.
Operating profitability and reinvestment are separate measures
OVHcloud’s FY2026 disclosure reported €480.5 million in adjusted EBITDA, a 42% adjusted EBITDA margin, €77.8 million in operating results and €9.4 million in net income. It also reported €1,157 million in consolidated net debt excluding lease liabilities at 31 August 2026 and €49.5 million of advance component investment intended for 2027. These company-reported measures illuminate different parts of the business; adjusted EBITDA does not represent cash freely available after equipment renewal, financing and other obligations. All 2026 targets achieved, excellence in execution, focus on value creation, operating results and funding sections — OVHcloud — Oct 2026. Amazon.com Announces Fourth Quarter Results
The strategic issue is the ability to maintain the service and invest through changes in component prices, customer demand and financing conditions. Infrastructure businesses can report substantial operating earnings while committing significant resources to replacement and expansion. For customers purchasing critical services, supplier resilience should therefore be assessed through the relationship between recurring revenue, maintenance needs, financial obligations and the timing of future investment. A high margin on one accounting measure cannot establish indefinite financial resilience, while debt does not by itself establish fragility where financing terms and cash generation are appropriate. The useful inquiry is whether the business can sustain its contractual service commitments through plausible conditions without relying on an unsupported assumption that additional capital will always arrive. This also explains why the quality and duration of demand matter: predictable commitments can improve investment planning, but poorly designed commitments can transfer excessive demand risk to customers or protect suppliers from competitive discipline.
| Financial or programme measure | What it establishes | What should not be inferred |
|---|---|---|
| Recognised revenue | Recorded customer activity under the issuer’s accounting definitions | Equivalent product breadth or strategic independence |
| Adjusted EBITDA | Earnings under a company-defined adjusted operating measure | Cash remaining after renewal and financing |
| Operating income | Profitability after the expenses included in that measure | Future financing availability |
| Net debt | A financing position at a specified date and definition | Inability to meet obligations without further analysis |
| Approved public aid | Permission and programme scope for support | Full disbursement or completed capability |
| Financing envelope | Resources intended to support eligible transactions | Funding already received by digital suppliers |
| Mobilised-investment objective | Intended broader investment effect | An additional amount that can be added without checking overlap |
| Procurement ceiling | Maximum purchasing capacity under an arrangement | Guaranteed revenue for participating suppliers |
European funding instruments address different industrial failures
The Commission’s approved IPCEI Next Generation Cloud Infrastructure and Services involves 19 companies from seven Member States, with up to €1.2 billion in public funding expected to unlock a further €1.4 billion in private investment. Its stated purpose concerns research, development and first industrial deployment of interoperable cloud-to-edge technologies. These are programme commitments and expected investment effects, rather than a consolidated record of expenditure or completed services. Approved IPCEI Next Generation Cloud Infrastructure and Services — European Commission — approved Dec 2023.
The EIB Group’s TechEU framework is much broader. Its published financing structure identifies €70 billion in equity, quasi-equity, loans and guarantees over 2025–2027, intended to mobilise at least €250 billion in investment across several innovation domains. It is not a dedicated cloud budget, and the mobilisation objective must not be added to the financing envelope as though both represented separate public expenditure. Europe’s innovative companies get boost as EIB Group launches TechEU Platform to simplify financing — European Investment Bank — Aug 2025. European Commission
These instruments can support complementary stages of industrial development, but their economic effects depend on how projects move from financed activity to maintained services. Research support can create technology that would otherwise be underfunded; investment finance can help a supplier expand; purchasing commitments can establish demand; and adoption assistance can reduce customer transition costs. None automatically performs the others’ role. A technically successful project may still lack a sustainable customer base, while a profitable service may depend on components whose development requires a different funding model. The assessment should therefore follow each intervention to its intended output and subsequent commercial position. The strongest evidence of a functioning ecosystem is the formation of durable relationships between developers, maintainers, providers and users. The weakest accounting is the addition of heterogeneous funding announcements into a single total labelled European capacity.
Demand should be examined through its composition
Eurostat’s 2025 enterprise survey provides a demand baseline with explicit coverage: enterprises with at least ten employees or self-employed persons in the surveyed economic activities. Its data show substantial differences by size, with paid-cloud adoption of 49.30% among small enterprises, 66.78% among medium enterprises and 84.67% among large enterprises. These figures measure adoption, not supplier ownership, expenditure or sovereignty. Cloud computing — statistics on the use by enterprises, Figure 3 and methodological notes — Eurostat — data extracted Jan 2026.
The economic interpretation is that European suppliers face several markets rather than a homogeneous pool of demand. Smaller enterprises may value integrated services, predictable costs and limited administrative effort; larger organisations can require extensive integration, assurance and specialist support. These differences affect the services providers can scale and the channels through which they reach customers. Public policy should consequently distinguish a shortage of purchasing power from a shortage of implementation capability. A subsidy can lower the purchase price without resolving the customer’s lack of expertise, while technical assistance can make an existing service usable without reducing its underlying operating cost. Aggregated demand can improve bargaining power and provide investment visibility, but it can also favour suppliers able to serve a very large contract immediately. Contract packaging and support arrangements therefore influence whether public purchasing creates opportunities for multiple providers or concentrates demand among a few established organisations.
Italy’s Cloud and Cybersecurity Voucher illustrates a demand-side instrument with a defined scale. MIMIT describes support for eligible SMEs and self-employed workers through grants covering up to 50% of eligible expenditure, capped at €20,000, with eligible products and services supplied through the programme’s specified listing arrangements. These are programme conditions, not evidence of the number of successful beneficiaries or the strategic independence of the purchased services. Sostegno alla domanda di servizi di cloud computing e cyber security — Ministry of Enterprises and Made in Italy — current programme information consulted Nov 2026.
EU paid-cloud adoption, 2025: small enterprises 49.30%; medium enterprises 66.78%; large enterprises 84.67%.
Sustainable supply requires an economically viable exit
The ability to change provider has an economic value even when the customer never exercises it: a credible alternative can influence renewal negotiations, constrain unilateral changes and reduce the cost of adapting to new requirements. That value depends on preparation and must be weighed against its cost. Maintaining a second fully operational environment may be disproportionate for some workloads, while documented export procedures, portable application design and periodic transition tests may preserve useful options at lower cost. The appropriate level of preparation depends on the function, its criticality and the consequences of disruption. Strategic purchasing should therefore evaluate the total cost of the service relationship, including implementation, operation, assurance, adaptation and eventual transition. An initially inexpensive service can become costly if essential changes are difficult, while a more expensive offer can justify its price only where the claimed lifecycle advantages are sufficiently specific and verifiable. This is an analytical evaluation framework, not a finding that European or non-European suppliers systematically occupy either position.
Key judgments
A sustainable ecosystem requires more than financing supply: it requires services that customers can adopt, maintain and renew on economically defensible terms. Public aid, investment finance and purchasing power address different constraints. Their effectiveness should be measured through delivered capability, recurring demand, maintainable services and demonstrable customer choice, rather than through the aggregate value of announcements.
What would change the assessment
The assessment would strengthen where European suppliers sustain product development and service renewal from durable demand, where financed projects achieve supported commercial deployment and where customers can adopt alternatives without disproportionate integration costs. It would weaken where capacity expands without sufficient utilisation, public support repeatedly substitutes for a viable service model or procurement concentration prevents smaller competent providers from reaching demand.
Open official record
Priority records include programme-level disbursements, project milestones, procurement call-offs, supplier financial disclosures and service-specific pricing and transition terms. Aggregate financing objectives cannot establish how much investment reaches cloud, cybersecurity or particular European suppliers without transaction-level or programme-specific evidence.
Chapter 6 — National Realities: Italy, France, Germany, the United Kingdom and EU Coordination
National implementation demonstrates several distinct routes towards greater digital control, each with different institutional strengths and different limits. Italy has combined central infrastructure and migration mechanisms with qualification and adoption support; France is using demanding workload requirements and public purchasing to steer sensitive-service migration; Germany is developing reusable software and shared administrative components across a federal system; and the United Kingdom is preparing a more coordinated cloud-purchasing approach while pursuing competition and legacy-modernisation objectives. These approaches should be compared through the functions they perform and the evidence of delivery, rather than through a single unsupported ranking of national sovereignty. A programme can be effective at consolidating infrastructure while leaving application dependence unresolved, or successful at distributing software while still requiring extensive integration and support. The relevant national assessment must identify what has changed for public institutions and industrial users, which changes are independently or officially documented and which remain prospective.
Italy: migration scale creates an opportunity for deeper service governance
Polo Strategico Nazionale reported on 21 July 2026 that more than 280 public administrations, including central administrations and health organisations, had migrated data, services and information systems to its infrastructure. This is an attributable operator report of programme delivery. Its count should not be interpreted as proof that every application, dataset or dependency of each participating administration had been fully transferred, independently audited or replaced. The useful next level of evidence is workload coverage and the operating state of the migrated services. Centrato il target PNRR: oltre 280 Pubbliche Amministrazioni migrate al cloud sovrano di Polo Strategico Nazionale — PSN — Jul 2026.
The Department for Digital Transformation separately extended the deadline for eligible administrations to join the PSN convention to 23 February 2027, specifying the distinction for administrations not bound by PNRR deadlines. This makes the administrative horizon different from the timetable attached to particular recovery-plan commitments. Polo Strategico Nazionale: prorogato il termine di adesione alla Convenzione — Department for Digital Transformation — Sep 2025.
Italy’s implementation challenge now concerns the depth and continuing governance of migration. Consolidation can improve the ability to establish consistent service requirements, but it can also make shared operational and contractual dependencies more consequential. The national framework must therefore connect migration records to data classification, service responsibilities, recovery arrangements and continuing qualification. The 2026 update to the Three-Year ICT Plan explicitly links acquisition to qualified or compliant services, requires updates to data and service classification when the perimeter changes and provides for monitoring qualifications valid for up to 36 months. These provisions establish an ongoing administrative task rather than a once-only migration event. Piano triennale per l’informatica nella Pubblica Amministrazione 2024–2026, aggiornamento 2026, Chapter 6 — AgID. polostrategiconazionale.it
The industrial opportunity is to convert a substantial migration programme into predictable demand for maintainable services and qualified specialist support. The corresponding risk is that progress becomes measured mainly through organisational counts while important differences in migrated scope remain obscured. A central administration moving a limited service and a health organisation transferring a large operational environment can both contribute to a programme count while presenting very different continuity and implementation requirements. Italy’s next analytical threshold is therefore the connection between programme delivery and observed service outcomes: whether the migrated applications can be supported, whether responsibilities are exercised during incidents and whether future changes remain feasible. These questions should be answered through service-level evidence rather than by inferring comprehensive autonomy from the national infrastructure’s identity.
France: demanding public workloads can develop the supplier base
The Health Data Hub announced on 23 April 2026 that it had selected Scaleway as the future host of its technology platform. It described a selection process lasting two and a half months and involving more than 350 technical requirements. The announcement also stated that participating offers covered parts of its needs and that some required security options remained to be implemented. It anticipated managing a copy of the principal SNDS database between the end of 2026 and the beginning of 2027. These statements establish selection, technical requirements and an implementation trajectory; they do not establish that the migration was complete at the dossier cut-off. La Plateforme des données de santé engage sa migration vers un cloud souverain avec Scaleway — Health Data Hub — Apr 2026. Health Data Hub
The strategic significance is the relationship between a demanding public user and the evolution of a supplier’s offer. A specialised workload can help define features whose development would be difficult to justify through fragmented demand alone. The public customer then contributes to industrial capability through a structured requirement and a credible service relationship, while retaining responsibility for determining whether the resulting environment meets its needs. This mechanism can strengthen an ecosystem if newly developed capabilities become maintainable and useful to additional customers. It can also create expensive bespoke environments if requirements diverge excessively or if the customer lacks the capacity to manage delivery. The appropriate assessment follows implementation, acceptance and subsequent service operation. Supplier selection is an important milestone, but the industrial result depends on the functionality delivered and the ability to sustain it beyond the initial migration.
France’s position therefore cannot be reduced either to the strength of its assurance doctrine or to earlier evidence of implementation difficulty. A credible assessment must track the sequence from requirement to procurement, implementation and operation. For sensitive public services, a supplier’s qualification and the customer’s specific configuration must converge at the point of delivery. Subsequent changes must preserve that relationship. The national advantage lies in the possibility of aligning security requirements, public demand and domestic technical development; the constraint is the institutional effort required to manage complex transitions without interrupting the functions those services support. France’s contribution to a broader European ecosystem will be stronger where this effort produces reusable services and transparent interfaces that can support additional public and industrial users across borders.
Germany: reusable software requires coordination across administrative levels
ZenDiS stated in its 9 October 2026 release that 100,000 public-administration workplaces were equipped with openDesk. In the same communication, it distinguished proposed agentic-AI and air-gapped operating scenarios as proof-of-concept work and roadmap developments. The deployment count is therefore evidence of reported software distribution, while the new operating scenarios require separate maturity judgments. It does not establish uniform daily use, the same configuration at every workplace or completed nationwide withdrawal from other collaboration platforms. Agentische KI und air-gapped-Betrieb: ZenDiS zeigt Proof-of-Concepts für neue openDesk-Szenarien auf der SCCON 2026 — ZenDiS — Oct 2026.
At a broader architectural level, the Federal Ministry for Digital Transformation and Government Modernisation describes the Deutschland-Stack as a framework for interoperable components serving federal, state and local administration, with iterative work towards concrete offers through 2028. Its description emphasises open standards, reusable components and integration of existing national and European building blocks. This is evidence of a coordinated development direction, not a claim that the complete platform has already been delivered. Der Deutschland-Stack — BMDS — current programme description consulted Nov 2026. Zentrum Digitale Souveränität
Germany’s institutional challenge is to make reuse operational across organisations that retain different application estates, responsibilities and implementation capacities. A common component reduces duplication only where its interfaces, support and governance permit institutions to adopt it without creating a new set of incompatible local versions. The maintenance organisation is consequently as important as the initial code. The ecosystem gains depth when several competent suppliers can integrate, support and extend a shared component while preserving compatibility and a clear route for security updates. It gains less where nominal reuse produces extensive customisation that only one contractor can sustain. The national assessment should therefore examine deployment quality, supported configurations, user outcomes and the ability to transfer maintenance responsibility. Germany’s federal structure makes coordination demanding, while also creating a substantial potential demand base for components that solve recurring administrative requirements.
United Kingdom: central purchasing could reshape demand, subject to delivery
The Government Digital Service’s clarification of the Cloud Challenge Book 2026 states that the anticipated National Cloud Infrastructure Programme procurement is expected to launch in early 2027, subject to continuing design and approvals. It asks suppliers to consider a five-to-ten-year planning horizon for engagement, while explicitly stating that future contract terms, structures and commitments have not been decided. These qualifications are material: the planning horizon is not an awarded contract term, and the anticipated procurement is not established supplier revenue. Clarifications on the Cloud Challenge Book 2026 — Government Digital Service — 2026.
The CMA’s October 2026 update describes engagement with government on the ability of national cloud procurement to influence market conditions, alongside its work on switching and interoperability. This connects the purchasing question to competition, rather than treating public buying solely as an exercise in obtaining a lower immediate price. Update on Cloud actions: Covering March–October 2026, public procurement discussion — CMA — Oct 2026.
The British strategic choice concerns how central purchasing will distribute opportunity and risk. Larger commitments can provide investment visibility and improve the government’s negotiating position, but a highly concentrated purchasing arrangement can also deepen dependence if entry, interoperability and transition are insufficiently protected. A demand-led programme should therefore be assessed through its eventual contract structure, the treatment of smaller providers, the services included and the continuing ability to alter the supplier mix. Its contribution to the wider European digital economy will depend on the practical terms under which providers can participate and customers can combine services. Geographical investment in the United Kingdom can strengthen regional capability without establishing EU jurisdiction or access rights, so cross-border cooperation requires explicit commercial and legal arrangements.
National adoption does not measure national sovereignty
The following comparison uses the same Eurostat enterprise-adoption measure for the EU and three Member States. It does not insert a British value from a different survey.
| Geography | Enterprises buying paid cloud services, 2025 |
|---|---|
| European Union | 52.74% |
| Italy | 75.60% |
| Germany | 53.91% |
| France | 40.41% |
The denominator is enterprises within the survey’s covered activities and size threshold. The figures measure adoption, not the share purchased from European providers, the sophistication of each workload or control over the underlying technology. Cloud computing — statistics on the use by enterprises, Table 1 and methodological notes — Eurostat — data extracted Jan 2026.
National comparison: Italy—reported migration; France—supplier selection; Germany—reported deployment; United Kingdom—procurement preparation. These are different implementation stages.
EU coordination must connect national demand without erasing material differences
The comparative record supports a European coordination problem that is more specific than a general shortage of ambition. Institutions are purchasing, migrating, developing shared software and preparing infrastructure programmes, but their units of progress differ. An administration count, a workstation count, a selected provider and an anticipated procurement cannot be combined into a common capacity total. Coordination should instead establish whether national activities produce services and components that other institutions can adopt under compatible requirements. This requires common descriptions of scope, interfaces, assurance evidence and transition responsibilities, while preserving legitimate differences in workload sensitivity and national authority. An excessively uniform approach could impose unnecessary requirements on ordinary services; an excessively fragmented approach could force suppliers to reproduce similar assurance and integration work for each market. The strategic objective is therefore compatibility of evidence and service relationships, with requirements proportionate to the function being protected.
The economic and institutional effects reinforce each other. Where national customers can reuse services and components across borders, suppliers gain a broader demand base and users gain additional options. Where requirements are opaque or tied to highly specific implementations, national spending can sustain isolated markets that remain dependent on external platforms for the functions they cannot develop economically. The quality of European coordination should consequently be judged through completed cross-border adoption, reusable procurement specifications, maintainable interfaces and the ability to change suppliers without reconstructing every institutional relationship. These are proposed measures of ecosystem integration. They preserve a distinction between increased European spending and increased European freedom of action: the former can support the latter, but the relationship must be demonstrated through the capabilities and choices available to actual users.
Key judgments
Italy, France, Germany and the United Kingdom are advancing through different institutional mechanisms, and the evidence establishes materially different stages of implementation. Reported migration and deployment demonstrate substance, while supplier selection and planned procurement establish future pathways. European coordination will add the most value where it converts national demand into reusable, maintainable services with compatible assurance and practical opportunities for additional suppliers.
What would change the assessment
The assessment would strengthen with accepted French migration milestones, deeper Italian workload evidence, demonstrated German interoperability and maintenance portability, and British procurement structures that preserve competition and future choice. It would weaken where national programmes produce isolated configurations, where reported deployment obscures limited operational use or where public purchasing increases concentration without workable transition arrangements.
Open official record
The consequential records are workload-level migration and acceptance evidence, deployment definitions, service-use measures, published procurement conditions and cross-border adoption outcomes. National expenditure and programme counts remain useful indicators, but their contribution to a genuinely European ecosystem requires evidence that the resulting services can be used, maintained and replaced beyond the boundaries of the original project.
Pillar III — Strategic Resilience and Decisions
Chapter 7 — Disruption Pathways, Competing Futures and the Outlook to 2031
Europe’s digital autonomy should be judged by the essential functions its institutions can preserve during disruption, the alternatives they can activate and the dependencies they can repair within an acceptable operating period. This requires a different assessment from counting suppliers, facilities or qualified services. A functioning service can remain strategically fragile if its recovery depends on an unavailable authority, an overstretched specialist organisation or information whose integrity cannot be established. Conversely, an organisation can retain meaningful freedom of action while using external technology if it can maintain essential operations, protect its information and activate a tested alternative. The central resilience question is therefore how dependencies behave together under stress. The most consequential pathways involve combinations of technical failure, impaired decision-making, scarce recovery resources and competing institutional priorities. Their effects depend on the workload and its users, which makes a universal numerical sovereignty score less useful than an explicit account of the functions that remain available, the conditions under which they deteriorate and the decisions required before disruption becomes intolerable.
Documented threats establish exposure, not a forecast of inevitable failure
CERT-EU’s April 2026 assessment of activity observed during 2025 provides evidence relevant to European institutional exposure. Its findings distinguish tracked malicious activity, significant incidents, affected partners and targeted software. These categories cannot be combined into an incident total. The report also explains that expanded monitoring affected year-to-year visibility, while expressly cautioning against interpreting fewer significant incidents as proof of reduced threats or improved defences. Threat Landscape Report 2025: A Year in Review, key findings and methodology, pp. 4–6 — CERT-EU — Apr 2026. cert.europa.eu
| Observation | Recorded value | Reference period and scope | Interpretation limit |
|---|---|---|---|
| Distinct threat actors identified | At least 174 | 2025; Union entities and their ecosystem | Reflects collection and attribution coverage |
| Significant incidents to which CERT-EU responded | 9 | 2025; CERT-EU constituency | Not the total number of European incidents |
| Significant incidents initially involving vulnerability exploitation | 7 | Subset of those 9 incidents | Not a general European intrusion rate |
| Targeted or exploited software products used by Union entities | 198 | 2025; report’s observation scope | Products, not organisations or incidents |
| Recorded malicious-activity cases affecting partners | 178 | 2025; partner observations | Different unit from significant incidents |
| Partner organisations concerned | 90 | 2025; report’s partner scope | Does not establish identical impact |
The strategic implication concerns the relationship between institutional boundaries and operational exposure. An organisation can strengthen its direct environment while remaining exposed through a trusted partner, a widely used product or an authorised service connection. This does not establish that every shared service is unsuitable; it establishes the need to assess how an incident can cross an otherwise well-defined perimeter. In a European ecosystem, interconnection is simultaneously a source of capability and a transmission mechanism. Reusable components and shared providers can improve access to expertise, but their compromise can affect several customers through a common dependency. Resilience therefore requires an account of how compromised trust is withdrawn, how legitimate operation is restored and how essential activity continues while the affected relationship remains unavailable. Supplier nationality does not answer these operational questions, although jurisdiction, contractual authority and maintenance rights influence the options available to resolve them.
The decisive disruption is often a combination of failures
A severe disruption becomes strategically significant when the ordinary recovery assumptions cease to hold together. A provider outage may coincide with impaired customer authentication; an application restoration may depend on specialist staff already supporting other affected clients; or backup data may remain available while its reliability is uncertain. These are analytical stress conditions, rather than assertions that the same sequence has occurred across Europe. They matter because organisations frequently evaluate individual controls under conditions in which the surrounding environment remains available. A backup restoration performed with normal credentials, functioning communications and immediate specialist support establishes a narrower capability than recovery during a shared-provider incident. The relevant exercise should identify which surrounding conditions are essential, remove those that the scenario makes unavailable and observe the resulting service outcome. Where an essential function cannot be restored, the assessment should continue to examine minimum service, user protection and the handling of accumulated work.
The FCA’s 11 November 2026 observations provide a current supervisory foundation for this approach. Drawing on firms’ 2025–2026 self-assessments, it identifies the need for stronger evidence of present capability, challenged supplier assumptions, severe-but-plausible testing and attention to cumulative harm when interconnected services are disrupted. It also distinguishes useful measures beyond elapsed time, including affected customers, transaction volumes and outstanding work. These are observations for the relevant financial-sector framework, not new requirements automatically applicable to every European organisation. Operational resilience: demonstrating resilience in practice — Financial Conduct Authority — Nov 2026. FCA
| Stress pathway | Combination to examine | Consequence requiring a decision | Evidence that would support resilience |
|---|---|---|---|
| Shared-provider disruption | Several institutions lose access while drawing on the same recovery resources | Recovery priorities compete across customers | Contracted assistance and an exercise reflecting concurrent demand |
| Compromised administration | Production failure coincides with untrusted privileged credentials | Normal restoration authority cannot be assumed safe | Independently controlled recovery access and observed credential replacement |
| Uncertain data integrity | Applications can restart, but restored records cannot yet be trusted | Availability may conceal incorrect decisions or transactions | Integrity validation and reconciliation before full service restoration |
| Support overload | A regional incident affects both customers and their specialist providers | Nominal support entitlement may not produce timely assistance | Capacity commitments, escalation arrangements and exercised alternatives |
| Legal-operational conflict | A disputed request or restriction affects a necessary service relationship | The institution must preserve lawful operation while resolving the conflict | A defined decision authority and a technically workable contingency |
| Prolonged degraded operation | Essential functions continue below normal throughput | Backlogs, vulnerable users and deferred obligations accumulate | Tested minimum service and measured backlog-reduction capability |
These are proposed stress pathways. They are not assigned frequencies or probabilities.
Continuity must include integrity, prioritisation and backlog recovery
A service should not be declared recovered solely because its application responds or its infrastructure returns to operation. For many institutional functions, the decisive condition is whether the service produces trustworthy results, preserves the required sequence of work and supports the users whose needs cannot be deferred. This requires a distinction between technical restoration, functional restoration and the clearance of accumulated obligations. A system can regain access while retaining inconsistent records; a minimum service can protect urgent users while ordinary work accumulates; and a restored processing environment can remain below the throughput needed to clear that backlog. The appropriate recovery judgment must identify which state has been reached and what consequences remain. This is particularly important for public services, healthcare, financial operations and industrial coordination, where delayed or incorrect decisions can persist after the original infrastructure failure has ended.
A proposed measurement framework should therefore connect the institution’s tolerance to the actual service outcome. The maximum acceptable disruption is a management judgment informed by the affected function, applicable obligations and user harm; the observed recovery time is an exercise or incident result. They must not be confused. An organisation should also establish the maximum acceptable data loss, the evidence required to trust restored records, the throughput necessary for minimum service and the resources needed to reduce accumulated work. No common numerical value can be assigned defensibly across all workloads from the public record. The decision threshold is whether the tested arrangement meets the organisation’s documented requirements under the stated conditions. Where it does not, the response should distinguish a remediable weakness, a temporary and explicitly governed exposure and a service arrangement unsuitable for the function concerned.
Mutual assistance reduces exposure only within its demonstrated capacity
The EU Cybersecurity Reserve provides a mechanism for requesting specialist assistance beyond an affected organisation’s immediate resources. ENISA describes services from trusted managed-security providers supporting incident response and initial recovery, with requests channelled through the specified authorities. Its FAQ identifies €36 million over three years under the Commission–ENISA contribution agreement and explains that unused pre-committed response services may be converted into preparedness services under the relevant contract. These provisions establish a funded assistance mechanism; they do not establish unlimited simultaneous response capacity, a guaranteed arrival time for every affected entity or replacement of national responsibilities. The EU Cybersecurity Reserve — FAQ — ENISA — current description consulted Nov 2026.
The strategic value of such arrangements depends on the relationship between demand, eligibility, activation and available personnel during a shared incident. A reserve can reduce the disadvantage faced by institutions lacking specialist expertise, while also improving preparation through services delivered before an incident. Its contribution should be assessed through activation exercises, actual assistance records and evidence of coordination with national response structures. It should not become an assumption used to defer the institution’s own recovery preparation. A major event can create demand across several countries at once, making prioritisation and the availability of independent expertise central to effectiveness. The relevant planning question is therefore which functions the institution must preserve with its own arrangements, which assistance it can legitimately request and how it will operate while that assistance is being allocated.
Competing pathways to 2031
The outlook is best expressed through three conditional pathways that can coexist across sectors. Integrated selective autonomy would emerge where European services become easier to combine, maintain and replace, supported by reusable assurance and recurring demand. Managed external dependence would persist where institutions continue using global platforms but strengthen oversight, continuity and contractual options. Fragmented protection would develop where national restrictions and bespoke configurations grow faster than interoperable alternatives, increasing costs without resolving the shared dependencies that matter. The present record supports elements of the first two pathways and provides reasons to monitor the third. It does not support numerical probabilities or a claim that one pathway will encompass every country and workload. The distinguishing observations concern completed transfers, supported maintenance, cross-border adoption and the institutional capacity to preserve essential functions during disruption.
The Commission’s proposed Cloud and AI Development Act supplies a policy pathway for coordination, but its intended effects remain conditional on legislation, implementation and delivery. The Parliament’s June 2026 summary describes proposed measures addressing deployment, sovereignty assessment and common procurement, including an ambition to triple EU data-centre capacity over five to seven years. That ambition cannot be treated as capacity already delivered or as a guarantee that technological dependence will fall at the same rate. Cloud and AI Development Act, document summary for procedure 2026/0138(COD) — European Parliament — Jun 2026.
| Pathway to 2031 | Mechanism | Evidence that would strengthen it | Evidence that would weaken it | Present analytical standing |
|---|---|---|---|---|
| Integrated selective autonomy | Reusable services, maintenance capability and interoperable demand expand practical alternatives | Repeatable cross-border adoption and successful transitions across critical workloads | Persistent bespoke integration and inaccessible upstream maintenance | Credible pathway; delivery remains uneven |
| Managed external dependence | Oversight and tested contingencies reduce exposure while external platforms remain important | Demonstrated recovery, enforceable assistance and usable replacement options | Assurance that relies on untested supplier commitments | Consistent with an important part of the current record |
| Fragmented protection | National requirements produce isolated service environments and duplicated effort | Repeated incompatibility, limited competition and high transition costs | Mutual acceptance of evidence and reusable implementations | Material downside pathway; not an established universal outcome |
Resilience assessment: examine simultaneous provider disruption, uncertain data integrity and prolonged degraded operation. These are analytical scenarios, not forecasts.
Watch indicators and the five-year assessment horizon
The most informative near-term indicators concern the quality of evidence produced after a procurement, migration or exercise. During 2027, a stronger position would be demonstrated by accepted service transitions, explicit residual-risk records and recovery results that include shared dependencies. During 2028–2029, the more demanding question is whether these results can be repeated across institutions and national boundaries without rebuilding the arrangement each time. By 2030–2031, the strategic test becomes whether Europe possesses a deeper pool of suppliers and maintainers capable of sustaining essential services when a major commercial relationship is impaired. These are assessment checkpoints, not predicted completion dates. A single successful project can establish a useful capability, while an ecosystem-level judgment requires evidence of repeatability, scale and transfer of responsibility. Conversely, failures should be examined for their mechanism: an isolated implementation defect does not invalidate an entire industrial strategy, but repeated failures at the same interface can identify a structural constraint.
Key judgments
Resilience depends on service outcomes under combined stress, including trustworthy information, prioritised delivery and recovery of accumulated work. External assistance and supervisory arrangements can reduce exposure, but their scope and capacity must remain explicit. Through 2031, the most defensible outlook is a differentiated combination of selective European autonomy and managed external dependence, with fragmentation remaining a consequential downside if national initiatives fail to produce reusable alternatives.
What would change the assessment
The assessment would strengthen with repeated exercises demonstrating independent recovery, trusted data restoration and manageable backlogs across shared-service incidents. It would weaken where continuity depends on the same unavailable personnel, credentials or platform as the affected production environment, or where future investment is used as evidence of present resilience.
Open official record
Priority evidence includes anonymised cross-institution exercise findings, activation and assistance records, observed recovery under concurrent demand, service-integrity results and documented failures to meet agreed tolerances. Public threat observations establish exposure; they do not supply a probability model for European digital-system failure.
Chapter 8 — Courses of Action, Decision Thresholds and Final Net Assessment
The recommended course is to purchase and develop measurable freedom of action for essential workloads, while directing industrial support towards the dependencies that demonstrably constrain it. This approach requires institutions to decide what they must preserve, establish how the proposed service performs under relevant disruption and allocate investment to the gaps that remain. It avoids treating every imported component as equally consequential or every European service as equally suitable. It also prevents public intervention from being evaluated solely through expenditure and deployment counts. The decision standard should connect public authority, industrial capability and user outcomes: an institution should know who can act, what can continue, which alternatives are usable and how long those arrangements remain adequate. Where evidence is incomplete, the immediate task is to narrow the service claim and obtain the missing proof, rather than to assign an unsupported assurance score.
Separate decisions about operation, renewal, migration and industrial investment
These decisions occur at different levels and should use different evidence. An operational decision concerns whether an existing arrangement can continue supporting the required function within its approved conditions. A renewal decision concerns whether those conditions remain acceptable over the next contractual period. A migration decision concerns whether the destination environment can meet the requirement and whether the transition itself is manageable. An industrial-investment decision concerns whether financing a new capability will reduce a specified constraint and produce a service that can be sustained. Combining these questions can create avoidable error. An institution may need to continue an existing service temporarily while developing a better alternative; the temporary decision should not be represented as approval of indefinite dependence. Equally, a promising domestic technology programme should not be treated as an operational replacement before it has met the relevant delivery and acceptance conditions.
The existence of oversight mechanisms reinforces this distinction. The European Supervisory Authorities’ DORA guide describes an oversight framework for designated critical ICT providers, using criteria including systemic impact, interconnectedness and limited substitutability. Its purpose includes identifying risks and formalising recommendations within the framework’s scope. Such oversight supplies a mechanism for managing concentrated dependencies; it does not establish that a customer can replace the service or that all activities of the provider are covered. Guide on DORA oversight activities, sections 3.1–3.2 — European Supervisory Authorities — Jul 2025.
Use decision thresholds tied to the workload
The following thresholds are proposed analytical gates. They do not introduce universal legal limits, statutory deadlines or numerical probabilities. Each institution must define its own acceptable service conditions through the relevant authority and applicable framework.
| Gate | Evidence required | Threshold for proceeding | Response where the threshold is not met |
|---|---|---|---|
| Authority | Identified contractual and operational decision-makers | Required actions can be authorised and executed within the assessed arrangement | Resolve authority and escalation gaps before extending the service claim |
| Access boundary | Documented privileged and support access for the purchased configuration | Access conforms to the approved processing and security requirements | Restrict affected functions, remediate or select another arrangement |
| Minimum service | Exercise results under the relevant disruption | Essential outcomes remain within approved harm tolerances | Fund remediation or a tested alternative; record interim exposure |
| Information integrity | Validation and reconciliation results | Restored information meets the standard required for operational decisions | Withhold full restoration until reliability is established |
| Transition | Representative export, import and application operation | The destination supports the required function with an acceptable transition burden | Revise the design or avoid increasing the affected dependency |
| Sustainment | Maintenance capability, rights and required resources | The service remains supportable over the assessed period | Narrow the operating period or invest in a viable maintenance alternative |
| Shared failure | Mapping and testing of common dependencies | Claimed alternatives remain usable under the specified common disruption | Remove the shared failure or revise the diversification claim |
The purpose of these gates is to make the decision consequence explicit. Evidence can justify proceeding within a limited scope, proceeding subject to a funded correction, maintaining a temporary arrangement under documented conditions or declining additional dependence. These outcomes should not be collapsed into a binary label applied to an entire provider. A service may meet the requirement for one workload while failing another because the consequences of interruption, information exposure or delayed transition differ. The same principle applies over time: a configuration can cease to meet the requirement after a material change even where the supplier’s identity remains unchanged. Decision records should therefore identify the service, the tested conditions, the evidence date and the authority accepting any residual exposure. This creates a usable connection between assurance and institutional accountability.
Compare feasible courses of action
The options below are complementary where their functions differ. Implementation windows are proposed planning periods after a competent decision, not forecasts of supplier delivery or statutory deadlines. A test result, accepted milestone or completed procurement remains necessary before an outcome can be claimed.
| Course of action | Competent authority | Expected effect | Implementation burden | Proposed time to initial effect |
|---|---|---|---|---|
| Establish a workload-level evidence register | Service owner, accountable management and relevant security or procurement functions | Connects requirements, dependencies, evidence and accepted gaps | Inventory reconciliation and continuing ownership | Initial priority-workload register within 90 days |
| Exercise one representative transition | Contracting customer with its source and destination providers | Tests whether a claimed alternative is operationally usable | Test environment, engineering, contractual assistance and validation | First exercise within 3–6 months where access and resources permit |
| Reserve minimum-service and recovery capability | Service owner and continuity authority | Protects essential outcomes during prolonged disruption | Staffing, procedures, independent access and realistic exercises | Initial arrangements in 3–6 months; assurance follows testing |
| Procure reusable assurance and interfaces | Contracting authorities within applicable procurement rules | Reduces duplicated evaluation and integration barriers | Specification design, supplier engagement and lifecycle governance | Through the next suitable procurement cycle |
| Finance a specific maintenance or replacement gap | Competent funding body, investor or industrial programme | Reduces a demonstrated constraint in support or substitution | Technical due diligence, milestone design and sustained funding | Milestone-dependent; no capability credited before acceptance |
| Coordinate exercises and dependency information | Relevant supervisory, cyber-response and public-service authorities | Identifies shared failure and competing recovery demand | Confidentiality arrangements, scenario design and cross-organisation participation | Design within 6 months; delivery depends on agreed scope |
| Course of action | Reversibility | Second-order consequence | Principal risk |
|---|---|---|---|
| Workload evidence register | High; scope can be adjusted | Makes previously unowned dependencies visible | Administrative collection without operational use |
| Representative transition | High before production cutover | Reveals integration costs and can improve negotiating leverage | A narrow demonstration is misrepresented as universal portability |
| Minimum-service capability | Generally high for procedures; lower for dedicated investment | Requires explicit prioritisation of users and functions | A manual or reduced service cannot scale under prolonged disruption |
| Reusable assurance and interfaces | Medium; changes must preserve contract and service stability | Can broaden the addressable market for additional suppliers | Common specifications become tied to one implementation |
| Targeted gap financing | Lower after substantial capital commitment | Can build specialist capability and create future competition | Funding sustains a bespoke capability without durable demand |
| Coordinated exercises | High for exercise design | Exposes system-wide priorities and information-sharing needs | Institutions disclose plans without testing executable recovery |
The recommended sequence begins with the evidence register and a representative exercise because these improve the quality of subsequent purchasing and investment decisions. Their value is diagnostic: they identify whether the binding constraint is contractual, technical, organisational or industrial. Where the problem is unclear access authority, new infrastructure may contribute little. Where the problem is an absent maintenance capability, repeated migration documentation will not supply the missing expertise. Where the alternative already exists but the customer cannot adopt it, implementation assistance may be more useful than financing another platform. This sequencing preserves resources by connecting the intervention to an observed constraint. It also allows institutions to maintain proportionate arrangements: a low-impact workload may require a lighter transition preparation than an essential service whose interruption would rapidly cause serious harm.
Concentration requires collective supervision as well as individual preparation
The United Kingdom’s first critical-third-party designations took effect on 13 July 2026, covering four providers: Amazon Web Services EMEA SARL, Google Cloud EMEA Limited, Microsoft Ireland Operations Ltd and Oracle Corporation UK Limited. The FCA states that the regime addresses system-level risks in critical services supplied to the financial sector and complements the responsibilities of regulated firms. It also specifies that designation is not the same as regulatory authorisation. This supplies a concrete example of authorities addressing shared dependency through oversight rather than assuming that each customer can independently resolve a system-wide concentration. UK financial regulators to begin overseeing Critical Third Parties announced by Treasury — FCA — Jul 2026. FCA
European coordination can also operate across distinct jurisdictions without treating them as a single legal system. The 14 January 2026 memorandum between the European Supervisory Authorities and the Bank of England, PRA and FCA establishes principles and procedures for cooperation, information sharing and coordination concerning critical ICT-provider oversight. This is an institutional cooperation mechanism; its existence does not merge the regimes or establish that every cross-border dependency has been resolved. The European Supervisory Authorities and UK financial regulators sign Memorandum of Understanding on oversight of critical ICT third-party service providers under DORA — ESMA — Jan 2026. esma.europa.eu
The decision consequence is that customer-level resilience and collective oversight should reinforce each other. Individual institutions can test recovery and preserve alternatives, while public authorities can identify dependencies whose effects extend across several customers or markets. Neither level is sufficient alone. Collective supervision cannot reconstruct every customer application, and an individual organisation cannot reliably assess the recovery priorities of an entire sector from its own contract. Coordination should therefore produce information and exercises that improve both levels of decision-making, while respecting confidentiality and legal competence. The practical output should be a clearer account of shared exposure, available assistance and conflicting recovery assumptions. A concentration becomes more manageable when these relationships are visible and exercised; it remains strategically consequential even after it is formally designated or supervised.
National priorities should follow the remaining implementation constraint
For Italy, the next resilience decision is to connect migrated workloads to tested service outcomes and continuing responsibility, rather than extending an organisational migration count into a claim about every dependent application. For France, the priority is to follow sensitive-service procurement through implementation and acceptance, establishing which new capabilities become reusable beyond the original workload. For Germany, the decisive question is whether shared software and administrative components can be supported and maintained across organisations without recreating a dependence on one integration or support arrangement. For the United Kingdom, the central purchasing and oversight mechanisms should be assessed together: future contracts can improve bargaining power, but their structure must preserve competition, adaptability and continuity. These are analytical priorities derived from the national implementation evidence in Pillar II, not additional claims of completed programmes. Their common purpose is to identify the next proof needed before a broader claim of autonomy is justified.
At EU level, the corresponding task is to make evidence and service relationships reusable across borders. Common assurance descriptions should help institutions understand what has been assessed without implying that every workload requires the same restrictions. Industrial programmes should identify which dependency they reduce and how their output will be supported. Procurement cooperation should broaden practical access to suppliers rather than assume that aggregation alone improves competition. Cyber-response coordination should identify assistance that can be requested and the essential capability that must remain locally available. These functions are mutually supportive, but they operate through different authorities and timescales. Their integration should be evaluated through observable results: accepted services, usable alternatives, supported maintenance and recovery under shared stress. A European ecosystem becomes strategically stronger when another institution can adopt those results without repeating the entire development and assurance process.
Decision sequence: establish evidence, test the required service outcome, address the binding gap and reassess after material change.
Implementation milestones and accountability
The first implementation period should produce a narrower but more defensible assurance position. Within the proposed initial 90-day planning window, institutions should identify priority workloads, assign ownership of evidence and record the most consequential untested assumptions. The subsequent exercise period should concentrate on one representative recovery or transition whose result can change a real purchasing or investment decision. Where a gap is identified, the remediation record should state the responsible authority, resources, acceptance condition and the circumstances requiring renewed testing. Over a longer period, programmes should be evaluated for repeatability: whether additional institutions can use the capability, whether maintenance responsibility can move and whether the same evidence remains meaningful across configurations. These milestones are management proposals rather than predictions. They deliberately require an observed result before a capability is credited, so that completion of an administrative action is not confused with improvement in resilience.
| Proposed checkpoint | Deliverable | Acceptance question |
|---|---|---|
| Initial 90-day planning period | Priority-workload evidence register | Does each material dependency have an owner and a stated evidentiary position? |
| First representative exercise | Observed recovery or transition result | Can the required function operate under the selected disruption? |
| Remediation acceptance | Validated correction | Has the binding gap been removed, rather than merely assigned an action? |
| Procurement or renewal decision | Updated service-specific assessment | Does the evidence support the intended period and scope of reliance? |
| Programme review | Reuse and sustainment evidence | Can other institutions adopt and maintain the output on viable terms? |
| 2031 strategic reassessment | Cross-sector account of demonstrated options | Has Europe increased its ability to operate, maintain and replace essential services? |
Final net assessment
A genuinely European digital ecosystem exists, but its strategic autonomy is bounded, differentiated and dependent on the functions being assessed. The dossier’s evidence supports the existence of operating suppliers, public computing and service institutions, deployed alternatives, procurement mechanisms and an expanding framework for oversight and coordination. It does not establish comprehensive independence across the technology stack or a common level of resilience across countries and sectors. The strongest conclusion concerns demonstrated capacity within defined service boundaries; the broader conclusion depends on whether that capacity can be maintained, combined and substituted under adverse conditions. The evidence is therefore sufficient to reject a blanket claim that European digital sovereignty is merely promotional language, while also rejecting the assumption that European ownership, hosting or qualification establishes autonomous operation by itself.
The most defensible objective to 2031 is an increase in demonstrated options: more essential workloads that can continue under disruption, more services whose maintenance can be assumed by another competent organisation, more transitions that succeed in practice and fewer decisions constrained by an inaccessible upstream control point. This objective permits selective use of global technology while requiring the resulting dependence to remain explicit and proportionate. It also gives industrial policy a concrete test: investment should reduce a specified constraint and produce a capability that users can sustain. Europe’s strategic position will improve where public authority, commercial demand, technical competence and recovery capacity reinforce one another. It will remain weaker where assurance rests on labels, investment substitutes for acceptance evidence or national projects cannot become reusable services. The decisive measure is the freedom European institutions and enterprises can actually exercise when normal conditions no longer hold.


