

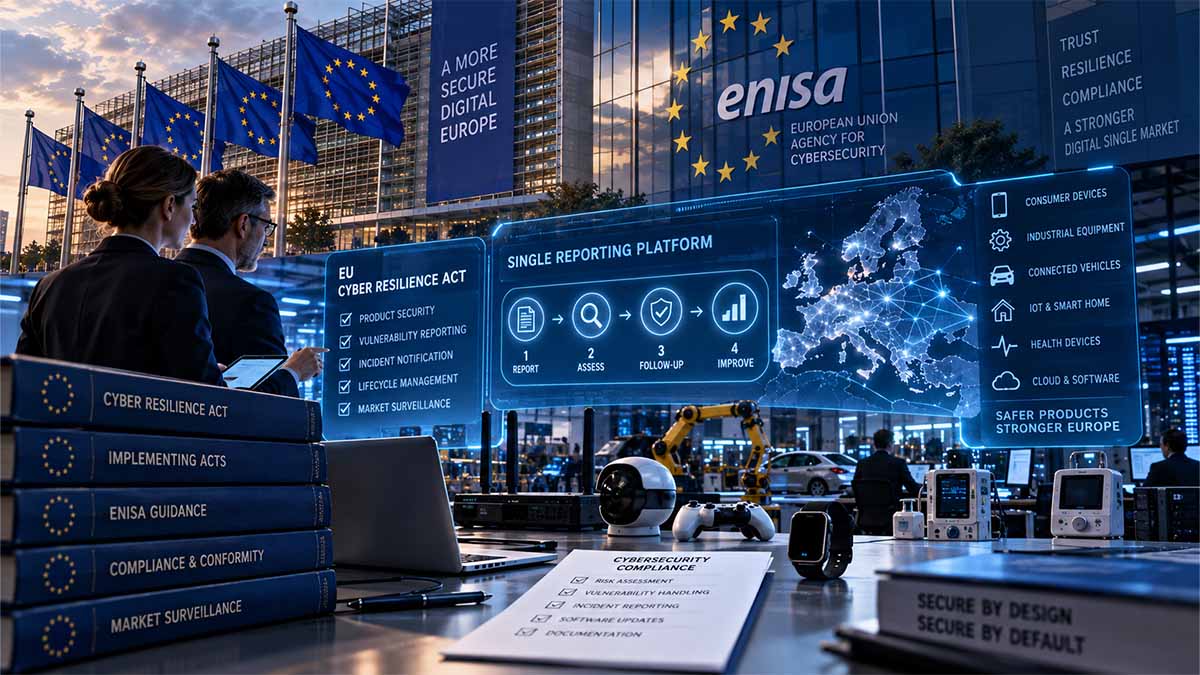
Scope: This assessment examines the Cyber Resilience Act reporting regime now applicable across the European Union, the operational launch of European Union Agency for Cybersecurity (ENISA)’s Single Reporting Platform, the resulting obligations for manufacturers and technology suppliers, the interaction with adjacent EU cyber-reporting regimes, and the implications for corporate boards, national governments, regulators and cybersecurity authorities through the 2027 full-application date and the subsequent implementation period.
Executive Summary / BLUF
The decisive change is that Cyber Resilience Act reporting has moved from regulatory preparation into a legally applicable operational regime, because Article 14 of Regulation (EU) 2024/2847 has applied since 11 September 2026, even though the CRA as a whole does not become applicable until 11 December 2027; manufacturers therefore already need the organisational capacity to recognise a potentially reportable event, determine whether it satisfies the statutory threshold, identify the responsible Computer Security Incident Response Team (CSIRT) endpoint and transmit the first notification within a period measured in hours rather than days. The CRA expressly provides that Article 14 applies from 11 September 2026, while the remainder of the Regulation is generally scheduled for application from December 2027.
The regulatory trigger is deliberately narrower than the existence of an ordinary software vulnerability but broader than many conventional corporate concepts of a “major breach”: mandatory vulnerability reporting concerns an “actively exploited vulnerability”, defined as a vulnerability for which reliable evidence exists that a malicious actor has exploited it without the system owner’s permission, while a reportable severe incident includes an event that negatively affects, or is capable of negatively affecting, the product’s ability to protect important or sensitive data or functions, or that has led or is capable of leading to malicious-code execution in the product or a user’s systems.
The operating clock is severe: manufacturers must provide an early warning within 24 hours after becoming aware of a reportable exploited vulnerability or severe incident and a fuller notification within 72 hours; an exploited-vulnerability case subsequently requires a final report no later than 14 days after a corrective or mitigating measure becomes available, whereas a severe-incident final report is due within one month after the 72-hour incident notification, creating a compliance model in which technical detection, product identification, legal classification, executive escalation, external reporting and customer communication have to function as one integrated process.
ENISA’s Single Reporting Platform, or SRP, entered operational service on 11 September 2026 and is intended to permit a manufacturer to report once through a common European infrastructure rather than separately notifying every potentially affected Member State; the notification is routed to the CSIRT designated as coordinator in the relevant Member State while becoming available to ENISA and, subject to narrowly defined security exceptions, being disseminated to other affected Computer Security Incident Response Team (CSIRTs) .
For companies, the central governance problem is therefore no longer merely whether cybersecurity controls are technically adequate, but whether the organisation can transform incomplete technical evidence into a legally defensible reporting decision inside a 24-hour statutory window, while preserving privilege, confidentiality, coordinated-vulnerability-disclosure requirements, customer communications and parallel notification obligations under other regulatory regimes; the base material supplied for this assessment correctly identifies that the first operational consequence is the need for an integrated process connecting product security, incident response, legal, compliance and customer-facing functions.
For governments, the SRP represents something more consequential than a compliance portal because, if reporting quality and CSIRT processing are sufficiently consistent, it can become a Union-wide sensor for identifying exploitation of common products across several jurisdictions, correlating campaigns and recognising supply-chain or software-distribution compromises before individual national authorities would necessarily connect them; ENISA may also transmit relevant information to EU-CyCLONe where notifications bear on coordinated management of large-scale cybersecurity incidents and crises.
The principal policy limitation is that single reporting under the CRA does not create a single European cyber-notification regime, because the legal trigger, competent authority, timing and reporting content can differ under NIS2, DORA, GDPR and national rules; financial entities, for example, operate under DORA’s separate major ICT-incident framework, while NIS2 establishes its own notification architecture for essential and important entities, meaning that one cyber event can generate several legally distinct reporting assessments even where the technical facts are identical.
A further legal distinction is particularly important for board papers and public-policy documents: although the uploaded base text associates CRA reporting failures with the Regulation’s maximum administrative fines of €15 million or 2.5% of worldwide annual turnover, Article 64 indeed establishes that ceiling for specified Article 13 and Article 14 infringements, but Article 71 places the Regulation’s general application date at 11 December 2027 while expressly accelerating Article 14 itself to September 2026; accordingly, current reporting obligations should not be described simplistically as if every element of the CRA’s later penalty architecture had necessarily become applicable on the same September 2026 date. The legal duty is already operational, while the enforcement architecture requires more precise treatment than a headline fine figure alone.
The strategic conclusion for both companies and policymakers is consequently that the period between September 2026 and December 2027 should be treated as a live operational transition rather than a grace period: manufacturers already face Article 14 reporting duties, European Union Agency for Cybersecurity (ENISA) and national CSIRTs are already receiving structured vulnerability and incident intelligence, older products within CRA scope are expressly brought within Article 14 reporting even when they were placed on the market before December 2027, and the Commission is required to evaluate the effectiveness of the platform by 11 September 2028, making the next two years critical for establishing reporting practice, national coordination, confidentiality safeguards and evidence standards that will shape the mature CRA enforcement environment.
EU Cyber Resilience Act Reporting Has Gone Live — Europe Now Has to Make the Information Move Faster Than the Attack
The Cyber Resilience Act crossed from preparation into operation on 11 September 2026, when manufacturers became subject to mandatory reporting for actively exploited vulnerabilities and severe incidents affecting products with digital elements through ENISA’s Single Reporting Platform. The legal change is narrower than full CRA application, which is scheduled for 11 December 2027, but its immediate effect is larger than the timetable suggests: product-security intelligence that once remained inside vendors now enters a European reporting chain linking manufacturers, national CSIRTs, ENISA, market-surveillance authorities and, in large-scale cases, EU-CyCLONe. The fiscal cost falls first on companies building 24-hour reporting capacity; the security return depends on whether Europe can turn those reports into cross-border warning before exploitation outruns administration.
The clock now belongs to the regulator, not the incident team
Article 14 makes timing the first hard constraint. A manufacturer must provide an early warning within 24 hours of becoming aware of an actively exploited vulnerability or a severe incident, followed by a more detailed notification within 72 hours. For actively exploited vulnerabilities, the final report is due no later than 14 days after a corrective or mitigating measure becomes available; for severe incidents, the final report is due within one month after the 72-hour notification. These are not investigation windows. They are reporting windows built around incomplete information, which means internal escalation, legal classification and technical evidence have to run in parallel rather than sequentially.
The threshold is equally important. The CRA does not require every vulnerability to be reported. Mandatory vulnerability reporting is limited to actively exploited vulnerabilities for which reliable evidence exists that a malicious actor has exploited the flaw without the system owner’s permission. A proof of concept, laboratory demonstration or vulnerability discovered in code review does not automatically satisfy that test. At the same time, a manufacturer cannot safely wait for complete attribution or a reconstructed intrusion if the available evidence already establishes malicious exploitation. The compliance problem is therefore evidentiary discipline under time pressure, not simply faster form-filling.
A single platform does not mean a single authority
The Single Reporting Platform is centralised in user experience but distributed in institutional effect. The manufacturer submits through the endpoint associated with the CSIRT designated as coordinator for the relevant Member State, while ENISA also receives access through the common architecture. Where the affected product has been made available in other Member States, the receiving CSIRT is expected to disseminate the notification to the relevant national CSIRTs without delay. The platform therefore converts one manufacturer report into a potential cross-border warning mechanism.
That design matters because the object of regulation is the product, not only the victim. A compromised router, operating system, enterprise application or connected device may be deployed simultaneously across many jurisdictions. The first observed exploitation in one Member State can therefore carry defensive value for authorities elsewhere before they see an incident of their own. The strategic value of the platform lies in correlation: repeated reports concerning the same product, component, update channel or exploitation pattern can reveal a campaign that would remain fragmented if each national authority saw only its domestic cases.
The numbers define an operating model, not a compliance checklist
The CRA timetable now creates four operational markers that companies must design around: 24 hours for the early warning, 72 hours for the fuller notification, 14 days after a corrective measure becomes available for the final actively exploited vulnerability report, and one month after the 72-hour notification for the final severe-incident report. Those figures change staffing, authority delegation and supplier contracts because any function holding relevant evidence can consume the statutory clock before the legal team becomes involved.
The platform itself also introduces concrete resilience requirements. ENISA allows one Primary Assigned Representative and up to 20 Secondary Assigned Representatives for a manufacturer, with access through EU Login and multi-factor authentication. At launch, no API is available for automated submission. That means large companies can automate evidence collection, incident records and form preparation internally, but the final reporting workflow still depends on authenticated human operators. A reporting process built around one individual or one headquarters time zone is therefore a governance weakness created by design, not by chance.
The supply chain now transmits legal exposure as well as technical risk
The CRA changes the value of supplier information because a manufacturer can depend on a cloud provider, software component supplier, managed security provider, external developer or vulnerability researcher for the first reliable evidence that exploitation is occurring. If that information moves under a contract requiring notice only after several business days, the supplier can consume most of the manufacturer’s 24-hour regulatory window before the manufacturer even begins its own assessment.
The same logic applies to product inventories and customer records. A manufacturer must know which versions are affected, where products have been made available and which users may need warning. The dossier establishes that affected users must be informed of the vulnerability or incident and of available mitigation or corrective measures, with machine-readable information where appropriate. Product distribution, software-bill-of-materials data and customer-support records therefore become part of cyber-regulatory infrastructure. Weak inventory is no longer only an operational inconvenience; it can directly degrade reporting quality and user protection.
Confidentiality is managed, not absolute
The most sensitive part of the architecture concerns information that could make exploitation easier if circulated too quickly. The CRA permits a manufacturer to identify information as sensitive, and the receiving CSIRT can delay dissemination to other national CSIRTs where cybersecurity-related grounds justify doing so and only for as long as strictly necessary. In particularly exceptional cases, ENISA may initially receive only limited information where exploitation is confined to one Member State and wider dissemination could expose essential national interests or create an imminent high cybersecurity risk.
This is not a confidentiality veto for manufacturers. The system is designed around a trade-off between the defensive value of rapid sharing and the offensive value of detailed technical information before remediation is available. If ENISA determines that a restricted case presents a systemic risk to the internal market, it may recommend wider dissemination of the full notification. The governance question is therefore not whether information is sensitive, but whether withholding it reduces more risk than it creates elsewhere in the Union.
Europe has centralised CRA reporting, not cyber regulation
The largest structural weakness is that the SRP sits beside rather than above Europe’s other cyber-reporting regimes. NIS2 imposes its own incident-management and notification duties on essential and important entities; DORA imposes a separate regime on financial entities; GDPR can independently require reporting of personal-data breaches. The same attack can therefore generate several legal assessments, several competent authorities and several deadlines, even when the underlying facts are identical.
This is not duplication by accident. The legal triggers are different. CRA asks whether a product has an actively exploited vulnerability or has suffered a severe security incident. NIS2 asks whether a regulated entity has suffered a significant incident affecting service provision. DORA focuses on major ICT-related incidents in the financial sector. GDPR asks whether a personal-data breach creates risk to the rights and freedoms of individuals. The practical burden arises because the same chronology, technical indicators and mitigation measures may have to be repackaged several times for different authorities.
The dossier’s national comparisons show why the next phase will be uneven. Italy has concentrated major national cyber functions around ACN and CSIRT Italia. Germany has developed a BSI portal model and already uses authority-to-authority forwarding in parts of its reporting architecture to avoid duplicate submissions. France remained under EU infringement pressure in 2026 because full NIS2 transposition had not yet been completed. The United Kingdom is outside the EU framework and operates its separate PSTI product-security regime, which has applied since 29 April 2024 and uses different obligations and enforcement mechanisms. For multinational manufacturers, “European compliance” therefore means a portfolio of legal and institutional systems, not a single operating environment.
The next 24 months will decide whether SRP becomes intelligence infrastructure
The European Commission is required to assess the effectiveness of the Single Reporting Platform by 11 September 2028, giving the Union two years to establish whether the system improves warning speed, cross-border correlation and supervisory action. The decisive metrics will not be the number of forms submitted. They will be the time between manufacturer awareness and national dissemination, the number of multi-country cases correlated through the platform, the frequency and duration of delayed dissemination, the number of cases escalated toward EU-CyCLONe, and the extent to which market-surveillance authorities use incident information in product enforcement.
The cost of inaction over the next 12–24 months will be distributed unevenly. Manufacturers will pay through duplicate reporting teams, emergency legal reviews and remediation delays if internal data remain fragmented; national CSIRTs will pay through higher analytical workload if submissions are inconsistent; regulators will pay through parallel systems that collect the same facts without sharing them efficiently; and users will pay when warning, patching and mitigation lag behind exploitation. The policy choice is therefore not whether Europe should create more reporting. That decision has already been made. The choice is whether the SRP remains a compliant intake channel or becomes the common information layer capable of making several existing cyber regimes work at operational speed.
Navigational Index
Corporate reporting becomes an operational control system
The first pillar examines the legal reporting thresholds, the 24-hour and 72-hour decision clocks, the meaning of manufacturer “awareness”, jurisdiction and CSIRT selection, customer-warning obligations, supply-chain information flows, governance requirements and the operational architecture companies require to demonstrate that reportability decisions were timely, reasoned and reproducible.
ENISA’s platform creates a new European cybersecurity information layer
The second pillar examines how the SRP links manufacturers, national CSIRTs, ENISA, market-surveillance authorities and potentially EU-CyCLONe, including the mechanisms governing cross-border dissemination, confidentiality, temporary withholding of highly sensitive vulnerability information and the emerging value of aggregated product-level reporting for European threat intelligence and crisis management.
Regulatory convergence remains incomplete despite centralised reporting
The third pillar examines the interaction between the CRA and NIS2, DORA, GDPR, national cybersecurity frameworks and the United Kingdom’s separate product-security regime, with particular attention to duplicated reporting, diverging legal thresholds, multinational manufacturers, enforcement architecture and the policy question of whether the SRP should eventually become part of a more integrated European incident-reporting framework.
Master Abstract
The application of Article 14 of the Cyber Resilience Act on 11 September 2026 marks a structural change in European cybersecurity regulation because the EU is moving responsibility for product-security intelligence closer to the manufacturer and attaching legally defined reporting clocks to information that historically remained within vulnerability-management, product-security or incident-response teams until the company itself decided that external disclosure was appropriate. The CRA now requires manufacturers to notify actively exploited vulnerabilities and severe incidents affecting products with digital elements, while ENISA’s newly operational Single Reporting Platform provides the common technical infrastructure through which those notifications reach the designated national CSIRT and ENISA. The statutory design therefore turns product telemetry, threat intelligence, vulnerability research, customer incident reports and supply-chain observations into potential regulatory evidence, making information architecture and escalation governance inseparable from legal compliance.
This change does not mean that every CVE, proof-of-concept exploit or internally discovered security defect becomes reportable, because Regulation (EU) 2024/2847 distinguishes an ordinary vulnerability, an exploitable vulnerability and an actively exploited vulnerability, with the last category requiring reliable evidence that malicious exploitation has occurred in a system without authorisation; the Regulation’s recitals further distinguish good-faith vulnerability discovery from the malicious exploitation contemplated by mandatory reporting. This distinction is central for corporate compliance because an excessively broad interpretation would overwhelm reporting systems and expose sensitive vulnerability information unnecessarily, whereas an excessively narrow interpretation could cause a manufacturer to lose critical hours while demanding forensic certainty that the statutory concept of “reliable evidence” does not necessarily require.
The severe-incident branch creates a different challenge because the statutory threshold is tied to the security properties and potential consequences of an incident rather than simply to the manufacturer’s internal severity label: a security event can qualify when it negatively affects, or is capable of negatively affecting, protection of the availability, authenticity, integrity or confidentiality of important or sensitive data or functions, or where malicious code has been or can be introduced or executed in the product or the user’s network and information systems. The Regulation specifically contemplates the compromise of development, production, maintenance or software-update channels as the kind of event capable of creating wider cybersecurity risk, meaning that product-security teams must monitor not merely customer-facing product vulnerabilities but also compromise of build pipelines, signing infrastructure, update distribution and other trust mechanisms through which software reaches users.
The significance of the 24-hour early warning is therefore organisational rather than clerical, because the requirement compresses several traditionally sequential corporate processes into a concurrent response: security operations must establish enough reliable evidence to identify the event; product teams must determine which versions and products are implicated; legal and compliance teams must classify the event against the CRA threshold; regulatory specialists must determine the appropriate CSIRT endpoint; senior decision-makers must have delegated authority sufficient to permit submission without a lengthy hierarchy of approvals; and communications teams must prepare the separate user information that Article 14 requires manufacturers to provide after becoming aware of an actively exploited vulnerability or severe incident. The Regulation expressly provides for user information, including risk-mitigation and corrective measures and, where appropriate, a structured machine-readable format, reinforcing the conclusion that CRA compliance depends directly on product inventories, version mapping and customer-location data.
The SRP simultaneously changes the governmental side of the equation because Article 16 requires ENISA to establish and operate the common reporting infrastructure while permitting Member States and ENISA to maintain electronic notification endpoints within that architecture; once the coordinator CSIRT receives a notification, the default rule is dissemination without delay to coordinator CSIRTs in Member States where the manufacturer indicates that the relevant product has been made available. The architecture therefore creates the basis for European authorities to correlate vulnerabilities affecting commercially distributed products across borders without requiring each national authority to discover the same exploitation independently.
That centralisation is intentionally constrained because vulnerability intelligence can itself create security risk, particularly before remediation becomes available, and Article 16 consequently permits delayed dissemination in exceptional circumstances where cybersecurity-related grounds justify withholding the notification for the period strictly necessary; the Regulation also creates a still narrower mechanism for particularly exceptional circumstances in which ENISA initially receives only limited information where broader dissemination could prejudice essential national interests or create an imminent high cybersecurity risk. The Commission states that a delegated act adopted on 11 December 2025 further specifies the conditions governing these cybersecurity-related grounds, illustrating that the EU has attempted to reconcile two competing objectives that cannot be eliminated by regulation: rapid multinational warning and controlled handling of exploit information whose premature disclosure could increase attack capability.
For policymakers, the principal opportunity lies in the information externality created by mandatory reporting, because individual manufacturers possess product telemetry and vulnerability information that national governments cannot independently reproduce at comparable speed or scale; central routing through ENISA and the CSIRT network can therefore produce cross-market situational awareness, while the connection to national market-surveillance authorities links cybersecurity incident intelligence to product regulation rather than leaving it exclusively within cyber-response organisations. Article 16 specifically requires coordinator CSIRTs to provide market-surveillance authorities with the information necessary for their CRA duties, while Article 17 permits ENISA to provide relevant information to EU-CyCLONe when required for operational coordination of large-scale cyber incidents and crises.
The principal weakness lies in the dependence of the system on manufacturer recognition and classification, because the SRP can only provide early warning when the manufacturer receives or generates sufficiently reliable evidence, correctly identifies the legal threshold and moves that information through its internal governance process before the deadline; weaknesses in telemetry, customer visibility, component inventories, contractual incident notification, vulnerability intake or cross-border product records can therefore become regulatory weaknesses even when the underlying technical security controls are otherwise mature. This is why the transition should be interpreted as a governance reform affecting procurement, software-development lifecycle management, third-party contracts, asset mapping, vulnerability disclosure and customer-service data rather than as a narrowly defined regulatory reporting project.
The broader European policy problem remains fragmentation, because centralising CRA notifications does not eliminate separate obligations created by entity-based, sector-based and data-protection legislation: DORA requires financial entities to report major ICT-related incidents through their sectoral competent-authority architecture and now uses detailed initial, intermediate and final reporting requirements, while other incidents can simultaneously trigger NIS2 or personal-data-breach obligations under the GDPR. The policy objective should therefore not be confused with legal unification: the CRA creates a single reporting mechanism for CRA product-security notifications, not a universal European cyber incident gateway.
The international dimension is equally important because the CRA regulates products made available on the EU market rather than merely companies headquartered inside the Union, meaning that technology groups in the United Kingdom, United States, Israel, Asia and elsewhere must structure European reporting arrangements when their products fall within scope; this is particularly relevant for UK companies, which already operate under the United Kingdom’s separate Product Security and Telecommunications Infrastructure regime for consumer connectable products, effective since 29 April 2024, and therefore increasingly face two distinct European product-security compliance environments rather than a single post-Brexit standard. The UK regime imposes requirements concerning matters including passwords, vulnerability-reporting channels and security-update transparency, but it does not replicate the CRA architecture, confirming that multinational manufacturers require jurisdiction-specific compliance mapping rather than an assumption of regulatory equivalence.
The resulting policy judgment is that the real strategic asset created by the CRA is not the reporting form but the information network surrounding it: if manufacturers provide high-quality information rapidly, CSIRTs correlate it effectively, ENISA protects and analyses it securely, national market-surveillance authorities use it consistently and overlaps with other reporting frameworks are progressively rationalised, the EU will gain a cybersecurity visibility layer covering commercial hardware and software that did not previously exist in this form; if those links remain fragmented, however, the SRP risks becoming an efficient submission mechanism sitting above inconsistent classification practices and parallel national processes rather than the genuinely integrated product-security intelligence system envisaged by the legislation.
Key Evidence Table
| Indicator | Value/status | Reference date | Definition/scope | Issuer | Exact source |
|---|---|---|---|---|---|
| CRA Article 14 reporting obligations | Applicable | 11 Sep 2026 | Manufacturers of products with digital elements within CRA scope | European Parliament / Council | Regulation (EU) 2024/2847, Article 71 |
| General CRA application | 11 Dec 2027 | Future general application date | Most CRA substantive obligations | European Parliament / Council | Regulation (EU) 2024/2847, Article 71 |
| Single Reporting Platform | Operational | 11 Sep 2026 | Mandatory CRA reporting infrastructure operated by ENISA | ENISA | Single Reporting Platform; ENISA launch notice |
| Early warning | ≤24 hours | From manufacturer awareness | Actively exploited vulnerability or severe incident | European Parliament / Council | Regulation (EU) 2024/2847, Article 14 |
| Detailed notification | ≤72 hours | From manufacturer awareness | Additional technical and contextual information | European Parliament / Council | Regulation (EU) 2024/2847, Article 14 |
| Vulnerability final report | ≤14 days after corrective/mitigating measure is available | Event-dependent | Actively exploited vulnerability | European Commission | CRA Reporting Obligations guidance |
| Severe-incident final report | ≤1 month after 72-hour notification | Event-dependent | Severe incident affecting product security | European Parliament / Council | Regulation (EU) 2024/2847, Article 14(4)(c) |
| Active exploitation threshold | Reliable evidence of malicious exploitation without system-owner permission | Current statutory definition | Distinct from theoretical exploitability or good-faith research | European Parliament / Council | Regulation (EU) 2024/2847, Article 3(42) |
| Existing products | Article 14 reporting also covers qualifying products placed on market before Dec 2027 | Transitional regime | Products otherwise within CRA scope | European Parliament / Council | Regulation (EU) 2024/2847, Article 69(3) |
| SRP assessment | Commission report required | 11 Sep 2028 | Effectiveness of SRP and delayed-dissemination mechanism | European Commission | Regulation (EU) 2024/2847, Article 70(2) |
| CRA maximum Article 13/14 fine ceiling | Up to €15m or 2.5% worldwide annual turnover, whichever is higher | Article 64 framework | Subject to the Regulation’s application and national penalty architecture | European Parliament / Council | Regulation (EU) 2024/2847, Article 64 |
| UK product-security regime | In force | 29 Apr 2024 | Consumer connectable products supplied in the UK | UK Government / OPSS / DSIT | UK PSTI product-security guidance |
What the 24-Hour Rule Changes Inside a Company
The deepest corporate consequence is that cybersecurity evidence has acquired a statutory time value, because information that remains unclassified or trapped inside an engineering, SOC, cloud, customer-support or third-party-provider workflow can consume a material portion of the reporting period before legal teams even know that a CRA decision is required; this means that compliance maturity will increasingly depend on the speed with which evidence travels through the organisation rather than solely on whether a formal incident-response policy exists.
The manufacturer therefore requires an internal decision structure capable of distinguishing at least four states without waiting for complete forensic reconstruction: an ordinary vulnerability that does not trigger Article 14; an exploitable vulnerability for which malicious exploitation has not been reliably established; an actively exploited vulnerability satisfying the CRA definition; and a severe product-security incident meeting Article 14’s separate impact criteria. The legal distinction is especially important because the Regulation itself differentiates “vulnerability,” “exploitable vulnerability” and “actively exploited vulnerability,” while recital 68 indicates that good-faith testing, investigation, correction or disclosure should not itself create mandatory notification.
A mature corporate control model should consequently preserve not merely the final answer but the evidence trail behind it: what information was first received, when the organisation became aware of it, whether the evidence suggested malicious exploitation, which product versions were involved, which jurisdictions contained affected customers, what additional intelligence was sought, who made the reportability determination and why the early-warning submission was or was not triggered. Such a record is important because the most consequential future regulatory dispute may concern not the technical existence of a vulnerability but when corporate knowledge became sufficient to begin the statutory clock.
The SRP Changes the Government Intelligence Picture
The architecture created by Article 16 is institutionally significant because it provides a mechanism through which commercial product-security information can move from individual manufacturers into national and Union-level cyber authorities while preserving Member-State coordination: manufacturers submit through the relevant electronic endpoint, coordinator CSIRTs disseminate the notification to other affected coordinator CSIRTs, ENISA participates in the platform architecture, and market-surveillance authorities receive the information needed to perform their responsibilities under the CRA.
The resulting dataset has potential strategic value that extends beyond individual compliance cases, particularly where the same operating system, network appliance, library, industrial controller, cloud-connected application or update mechanism is deployed across several Member States, because simultaneous reports concerning the same technology can reveal campaign patterns or systemic exposure that remain invisible when incidents are treated as independent national events. ENISA’s own launch material describes the SRP as part of a coordinated European approach to handling cybersecurity risks affecting products with digital elements, while Article 70 requires the Commission to assess the system’s effectiveness by September 2028 rather than assuming that centralisation itself guarantees useful intelligence.
For governments, the key performance measure should consequently not be the raw number of notifications but the decision latency between manufacturer awareness, SRP submission, cross-CSIRT dissemination, identification of common exposure and protective action, because a reporting system that collects accurate information but does not translate that information rapidly into warnings, prioritisation or market-surveillance action would satisfy the procedural objective without delivering the full resilience benefit.
The Regulatory Stack Remains the Principal Complexity
European companies should not interpret “single reporting platform” as “single regulatory report,” because the CRA is product-centred whereas adjacent regimes can be organisation-centred, sector-centred or data-centred, which means that one compromise can generate several legally distinct obligations based on different factual predicates; DORA, for example, requires financial entities to record ICT-related incidents and report major ICT-related incidents through its competent-authority framework, including an initial notification, intermediate report and final report, with more detailed timing rules established in Commission Delegated Regulation (EU) 2025/301.
The practical consequence is that a vendor whose compromised software update affects a regulated bank can confront one CRA analysis as manufacturer while the bank performs a DORA analysis as financial entity and potentially separate NIS2 or GDPR assessments depending upon the incident’s effects; the technical event is singular, but the legal relationships are not, which makes the quality of contractual information-sharing between vendors, customers, managed-service providers and cloud providers increasingly important to regulatory resilience.
The policy problem for the European Union is therefore no longer whether incident reporting should be mandatory, because that decision has already been embedded across several legal instruments, but whether the Union can progressively reduce duplicated information collection without collapsing legally distinct thresholds into an artificial common denominator; the CRA SRP provides a practical laboratory for that question because it centralises product-security reporting while preserving the separate legal competences of national CSIRTs, market-surveillance authorities and other sectoral regulators.
Italy, France, Germany and the United Kingdom: Initial Strategic Lens
For Italy, France and Germany, the immediate government task is not to create separate CRA substantive rules, because the Regulation is directly applicable, but to ensure that national CSIRT coordination, market-surveillance functions, industry guidance and enforcement interfaces are capable of processing a volume of reports that will increasingly reflect multinational products rather than geographically contained incidents; the cross-border architecture means that differences in national administrative capacity can become European externalities because a report initially handled in one Member State can contain security intelligence relevant to users and critical organisations across several others. Regulation (EU) 2024/2847 requires dissemination among affected coordinator CSIRTs and explicitly connects those CSIRTs with national market-surveillance authorities.
For the United Kingdom, the issue is different because the country is outside the EU regulatory architecture while UK manufacturers can nevertheless face CRA obligations when placing qualifying products on the EU market; at the same time, the domestic PSTI regime has applied since April 2024 to relevant consumer connectable products and imposes its own security requirements on manufacturers, importers and distributors. The result is not straightforward duplication but regulatory divergence, because the UK’s current product-security framework focuses on defined baseline product-security requirements including password practices, vulnerability-reporting mechanisms and transparency around minimum security-update periods, whereas the CRA establishes a substantially broader lifecycle and incident-reporting architecture for products with digital elements.
A full country comparison therefore requires examination not merely of statutory text but of the designated CSIRT coordinator, national market-surveillance authorities, reporting guidance, supervisory practice, enforcement resources and implementation choices in each jurisdiction, because those institutional variables will determine whether a formally harmonised EU regulation produces operationally consistent outcomes.
Principal Gaps and Watch Indicators
The most important unresolved question is how consistently manufacturers and national authorities will interpret “reliable evidence” of active exploitation and the severity threshold during the first year of implementation, because divergence at that classification stage would create substantial differences in reporting volume and could weaken the comparability of information flowing through the SRP even though the legal text itself is uniform. The Commission and ENISA guidance available at launch establishes the basic architecture, while practical interpretive consistency will depend on operating experience and future guidance.
A second watch indicator is the frequency with which coordinator CSIRTs invoke the Article 16 mechanism permitting delayed dissemination of particularly sensitive vulnerability information, because excessive withholding would reduce the early-warning value of the European system while indiscriminate dissemination could create precisely the vulnerability-exposure risks the safeguard was designed to prevent; the Commission’s legally mandated 2028 evaluation explicitly includes the impact of these cybersecurity-related grounds on timely dissemination.
A third indicator is the degree of operational integration between the CRA SRP and other EU reporting structures, because persistent duplication would impose substantial transaction costs on companies and regulators while increasing the risk that inconsistent descriptions of the same incident reach different authorities; convergence in templates, data dictionaries, secure channels or authority-to-authority information sharing would therefore be more consequential than superficial convergence in statutory deadlines.
A fourth indicator concerns supply-chain intelligence, because manufacturers often depend upon cloud providers, open-source components, embedded software, security researchers, managed service providers and customers to discover active exploitation; the capacity of contractual arrangements and technical telemetry to move that information rapidly enough for a 24-hour reporting decision will determine whether the legal deadline is supported by actual information flows rather than by nominal governance documents.
A fifth indicator is the evolution of enforcement after the CRA reaches full application on 11 December 2027, particularly the way national authorities interpret proportionality, repeated non-compliance, failures of organisational process and the relationship between late reporting and wider product-security deficiencies; headline maximum fines are therefore less analytically useful than the eventual enforcement pattern, especially because the CRA itself requires national penalty rules to be effective, proportionate and dissuasive.
Decision Thresholds for Corporate Leadership
A board or executive committee should regard the CRA programme as operationally inadequate when the company cannot establish, within minutes rather than days, which products and versions are affected by a security event, whether those products were made available in the European Union, which entity is legally the manufacturer, which national CSIRT endpoint is applicable, which customers or users may require notification and which parallel regulatory regimes require assessment.
A chief information security officer should regard the organisation’s detection architecture as incomplete for CRA purposes when evidence of exploitation can remain inside customer support, product engineering, cloud telemetry, fraud teams, third-party security providers or vulnerability researchers without triggering a centralised product-security escalation, because the statutory reporting clock is tied to manufacturer awareness rather than to the point at which an incident-management committee formally declares an emergency.
A general counsel should regard the governance model as insufficient when the company requires several layers of executive approval before an incomplete but legally required 24-hour early warning can be submitted, because Article 14 deliberately contemplates staged reporting: the early warning establishes the event rapidly, while the 72-hour notification and later final report permit the factual record to mature.
A government should regard implementation as institutionally weak when national authorities can receive CRA notifications but cannot correlate them rapidly with reports received by other CSIRTs, market-surveillance information, national vulnerability-management processes and crisis-management structures, because the strategic purpose of the platform is not fulfilled merely by successful electronic submission.
CRA Mandatory Reporting Clock
Awareness
Early warning
Detailed notification
Final reporting
| Stage | Deadline | Principal purpose |
|---|---|---|
| Early warning | 24 hours | Rapid regulatory awareness |
| Detailed notification | 72 hours | Initial technical and mitigation picture |
| Vulnerability final report | 14 days after corrective measure becomes available | Severity, impact, threat information and remediation |
| Severe-incident final report | One month after incident notification | Detailed incident, root cause and mitigation record |
EU Cyber Resilience Act Reporting Rules Go Live as ENISA’s Single Reporting Platform Changes the Operating Model for Product Cybersecurity
The decisive change is operational rather than merely legislative. Article 14 reporting obligations have applied since 11 September 2026, while most of the Cyber Resilience Act becomes applicable on 11 December 2027. Manufacturers must therefore already be able to recognise potentially reportable exploitation or severe product-security incidents, determine jurisdiction, preserve a defensible evidence trail and submit an early warning within 24 hours. ENISA’s Single Reporting Platform now transforms those corporate decisions into a Union-wide stream of product-security intelligence capable of feeding national CSIRTs, market-surveillance authorities and, where appropriate, EU-level crisis coordination.
The 24-hour rule turns reporting into a corporate control system
Cybersecurity evidence now has statutory time value. Evidence that remains inside engineering, SOC, cloud, customer-support or third-party workflows can consume the reporting window before legal and compliance functions even know that an Article 14 decision is required.
CRA operational benchmarks
| Indicator | Value / Status | Reference Date | Definition / Scope | Issuer | Primary Source |
|---|---|---|---|---|---|
| CRA Article 14 reporting | APPLICABLE | 11 Sep 2026 | Manufacturers of products with digital elements within CRA scope | EU Parliament / Council | Regulation (EU) 2024/2847, Article 71 |
| General CRA application | 11 DEC 2027 | Future application | Most substantive CRA obligations | EU Parliament / Council | Article 71 |
| ENISA Single Reporting Platform | OPERATIONAL | 11 Sep 2026 | Common infrastructure for CRA reporting | ENISA | Single Reporting Platform |
| Early warning | ≤24 HOURS | From manufacturer awareness | Actively exploited vulnerability or severe incident | EU Parliament / Council | Article 14 |
| Detailed notification | ≤72 HOURS | From manufacturer awareness | Additional technical and contextual information | EU Parliament / Council | Article 14 |
| Vulnerability final report | ≤14 DAYS | After corrective / mitigating measure available | Actively exploited vulnerability | European Commission | CRA reporting guidance |
| Severe-incident final report | ≤1 MONTH | After 72-hour notification | Severe product-security incident | EU Parliament / Council | Article 14(4)(c) |
| Active exploitation threshold | Reliable evidence of malicious exploitation | Current statutory definition | Distinct from theoretical exploitability or good-faith research | EU Parliament / Council | Article 3(42) |
| Existing products | ARTICLE 14 COVERAGE | Transitional regime | Qualifying products placed on market before Dec 2027 | EU Parliament / Council | Article 69(3) |
| SRP Commission assessment | 11 SEP 2028 | Mandated review date | Effectiveness of platform and delayed dissemination mechanism | European Commission | Article 70(2) |
| Article 13 / 14 fine ceiling | €15M OR 2.5% | Article 64 framework | Worldwide annual turnover; application depends on enforcement architecture | EU Parliament / Council | Article 64 |
| UK PSTI regime | IN FORCE | 29 Apr 2024 | Consumer connectable products supplied in UK | UK Government / OPSS / DSIT | PSTI product-security guidance |
Four structural layers of the new operating model
Evidence becomes regulatory infrastructure
Product telemetry, vulnerability research, customer reports, cloud logs and supplier intelligence can now determine when a statutory reporting clock begins. Evidence architecture is therefore inseparable from legal compliance.
SRP creates a European information layer
Manufacturer reporting can be distributed across coordinator CSIRTs and linked with market-surveillance functions. This creates a basis for identifying common product exposure across multiple Member States.
Centralisation does not equal legal unification
CRA, NIS2, DORA, GDPR and national requirements can still generate separate assessments from the same technical event. The SRP is a single channel for CRA notifications, not a universal EU cyber-reporting gateway.
Supply chains become part of reporting latency
Manufacturers may depend on open-source maintainers, cloud providers, managed services, security researchers and customers to detect exploitation. Contractual and technical information flows therefore become compliance controls.
One event, several legal relationships
| Regime | Regulatory Logic | Typical Trigger | Principal Actor | Operational Consequence |
|---|---|---|---|---|
| CRA | Product-centred | Actively exploited vulnerability / severe product-security incident | Manufacturer | SRP notification and user communication |
| NIS2 | Entity-centred | Significant incident affecting essential / important entity | Regulated entity | Separate national cyber notification assessment |
| DORA | Sector-centred | Major ICT-related incident | Financial entity | Initial, intermediate and final sectoral reporting |
| GDPR | Data-protection centred | Personal-data breach meeting notification threshold | Controller / processor architecture | Parallel supervisory and data-subject assessment |
| UK PSTI | Consumer product-security baseline | Product supplied in UK market | Manufacturer / importer / distributor | Separate post-Brexit compliance environment |
Italy, France, Germany and the United Kingdom
The immediate task is institutional rather than legislative: national CSIRT coordination, market-surveillance interfaces, industry guidance and enforcement workflows must be capable of processing reports concerning products distributed across several Member States. Weak processing capacity can become a European externality where information is relevant beyond the originating jurisdiction.
Operational consistency will depend on the interaction between national cyber-response capability, market-surveillance functions and the common SRP architecture. The critical policy variable is not the text of the Regulation, which is uniform, but the speed and consistency with which national institutions process cross-border product intelligence.
The German challenge is similarly operational: a highly industrialised market contains products, components and enterprise systems whose vulnerabilities can propagate across borders. Effective CRA implementation therefore requires rapid correlation between manufacturer reporting, national cyber authorities and product-supervision structures.
The UK sits outside the EU architecture but UK manufacturers placing qualifying products on the EU market can still face CRA obligations. Meanwhile the domestic PSTI framework has applied since 29 April 2024, creating regulatory divergence rather than simple duplication and requiring jurisdiction-specific compliance mapping.
Six decision-grade judgments
The CRA is already operational. The September 2026 start of Article 14 means the period before December 2027 is a live transition, not a grace period.
Decision latency is the core compliance variable. The decisive control is how rapidly uncertain technical evidence becomes a documented, legally defensible reporting decision.
SRP’s strategic value lies in information aggregation. Its importance is not merely electronic submission but the possibility of correlating common product exploitation across jurisdictions.
Single reporting is not single regulation. CRA reporting can coexist with NIS2, DORA, GDPR and national duties triggered by the same underlying event.
Supply-chain visibility becomes regulatory capacity. Contracts, component inventories, update infrastructure, customer mapping and third-party telemetry can determine whether a manufacturer can meet the 24-hour window.
The mature strategic asset is the information network. If manufacturers, CSIRTs, ENISA and market-surveillance authorities exchange high-quality information rapidly, Europe gains a product-security visibility layer that did not previously exist in this form.
- How consistently manufacturers and national authorities interpret “reliable evidence” of active exploitation.
- How consistently severe-incident thresholds are applied during the first year of operational reporting.
- How frequently coordinator CSIRTs invoke delayed dissemination under Article 16.
- How much operational duplication persists between CRA, NIS2, DORA, GDPR and national processes.
- How national enforcement practice will evolve after full CRA application in December 2027.
- Whether reporting volumes are comparable across Member States once implementation matures.
The programme is operationally inadequate if the organisation cannot rapidly identify affected products, versions, EU availability, manufacturer entity, jurisdiction, customer population and parallel notification obligations.
Detection is incomplete if exploitation evidence can remain in engineering, cloud telemetry, customer support, fraud teams or third-party channels without entering a central product-security escalation process.
Governance is insufficient if multiple executive approvals are needed before a legally required 24-hour early warning can be filed.
Implementation is institutionally weak if notifications are received but cannot be correlated rapidly with other CSIRT reports, market-surveillance intelligence and crisis-management processes.
Corporate Reporting Becomes an Operational Control System
Principal judgment
The application of Article 14 of the Cyber Resilience Act changes product-security reporting from a predominantly specialist cybersecurity activity into a time-critical corporate control function, because the legal obligation is triggered by what the manufacturer becomes aware of rather than by the completion of an internal investigation, the assignment of a CVE, the convening of an incident committee or the confirmation of attribution to a particular threat actor. Under Regulation (EU) 2024/2847 — Cyber Resilience Act, manufacturers must notify actively exploited vulnerabilities and severe incidents affecting the security of products with digital elements through the Single Reporting Platform, with an early warning required without undue delay and in any event within 24 hours after awareness, followed by the legally prescribed subsequent reporting stages. The European Commission’s current Cyber Resilience Act — Reporting obligations guidance confirms that these obligations have applied since 11 September 2026.
The resulting compliance problem is therefore fundamentally one of corporate information velocity. A manufacturer can possess technically capable security teams yet remain institutionally exposed when information concerning exploitation is fragmented between product engineering, a security operations centre, a cloud provider, an outsourced incident-response company, a customer-support organisation, an acquisition subsidiary or a researcher communicating through a vulnerability-disclosure channel. The CRA does not give manufacturers an additional internal investigation period before the reporting clock begins, and consequently the relevant governance question becomes whether material information can travel from whichever part of the organisation first receives it into a legally competent reporting process quickly enough to support a defensible Article 14 determination.
This makes the CRA reporting architecture materially different from a compliance model in which regulatory reporting begins only after a company has formally declared a major incident. The control objective must instead be designed around three linked questions: when did the manufacturer acquire information capable of establishing awareness; what did the available evidence demonstrate at that moment; and what governance process converted that evidence into the decision to report, defer reporting because the legal threshold had not yet been met, or escalate the case for immediate reassessment?
Awareness is the point at which cyber evidence becomes legally consequential
Article 14 repeatedly uses the formulation that a manufacturer must notify an actively exploited vulnerability or severe incident that it “becomes aware of”, which means that the chronology of information acquisition becomes central to compliance. The Cyber Resilience Act implementation FAQs, updated by the Commission on 4 September 2026, provide current implementation guidance on how manufacturers should understand the reporting regime, while ENISA’s CRA Single Reporting Platform FAQs explicitly states that the reporting clock for actively exploited vulnerabilities is triggered when the manufacturer becomes aware of the exploitation.
This does not mean that every unverified alert received anywhere in a multinational group automatically establishes Article 14 awareness; equally, however, it would be risky for manufacturers to define awareness solely as the moment at which a particular executive, legal department or central product-security team receives a formally validated incident report. The Regulation does not create a broad safe harbour allowing relevant information to remain operationally isolated within the corporate structure, and ENISA expressly states that, where a manufacturer operates through multiple branches or subsidiaries, the manufacturer remains responsible for coordinating internally across its corporate structure and ensuring that the required notification is submitted. ENISA’s Single Reporting Platform FAQ further confirms that only one notification is required for a given actively exploited vulnerability or severe incident, including where the manufacturer has multiple EU branches or a parent company headquartered outside the Union.
For compliance engineering, the prudent interpretation is therefore not to attempt to postpone the awareness moment administratively, but to build an internal process that records the first credible indication, distinguishes raw signals from reliable evidence, documents the subsequent analytical steps and escalates ambiguous cases rapidly enough that the statutory deadline remains achievable if the reporting threshold is reached.
Corporate awareness-control matrix
| Information source | Typical evidence received | CRA relevance | Required internal control | Principal governance failure |
|---|---|---|---|---|
| Security Operations Centre | Endpoint telemetry, anomalous execution, intrusion indicators | Can establish evidence of exploitation or malicious-code execution | Automatic escalation to PSIRT/product-security function when a covered product may be implicated | Alert remains treated as ordinary enterprise security event |
| Product Security Incident Response Team | Vulnerability reports, exploit samples, coordinated disclosure | Central to determining active exploitation | Formal Article 14 classification workflow and timestamping | Technical remediation proceeds without regulatory review |
| Customer support | Reports of compromise, abnormal product behaviour, security complaints | Can provide first external indication of exploitation | Security-trigger keywords and mandatory escalation pathway | Customer ticket remains within service organisation |
| Managed security provider | Detection alerts, incident investigation | Can provide third-party evidence of exploitation | Contractual notification SLA shorter than CRA internal decision window | Supplier reports after contractual monthly/weekly cycle |
| Cloud provider | Logs, infrastructure compromise information | Can expose attacks affecting cloud-dependent products | Real-time incident notification clause and shared evidence protocol | Vendor has evidence before manufacturer receives it |
| Vulnerability researcher | Exploit evidence, technical proof, victim observations | Potentially decisive depending on reliability and context | Coordinated vulnerability-disclosure intake linked to CRA process | Disclosure channel isolated from compliance team |
| CERT/CSIRT or public authority | Exploitation intelligence, victim reports, campaign information | Potentially high-confidence evidence | Immediate executive/product-security escalation | Information treated only as external intelligence |
| Sales/distributor network | Customer incident information and affected product geography | Relevant both to awareness and Member-State reporting data | Security escalation obligation for distributors and partners | Commercial teams lack incident-reporting duty |
| Software/component supplier | Notification of exploitation in integrated component | Can trigger assessment across multiple dependent products | SBOM/component dependency mapping plus immediate escalation | Manufacturer cannot identify affected downstream products |
| Threat-intelligence provider | Indicators, adversary campaigns, exploitation claims | Reliability varies; can trigger further verification | Evidence-grading model and product correlation | Intelligence collected but not tied to product inventory |
The central governance requirement is that these information channels must converge before the 24-hour legal deadline becomes operationally impossible to meet. This is why the Commission’s July 2026 Guidance on the application of the Cyber Resilience Act is particularly important for companies: the guidance was developed specifically to clarify practical implementation questions, including reporting obligations and risk assessment, rather than leaving manufacturers to treat the Regulation as an abstract legal text.
The reportability threshold must be separated from ordinary vulnerability management
One of the most important control failures would be to equate “vulnerability discovered” with “CRA report required”. The Regulation establishes a narrower category of mandatory vulnerability reporting by defining an actively exploited vulnerability around reliable evidence that a malicious actor has actually exploited the vulnerability without the permission of the system owner. Regulation (EU) 2024/2847 therefore creates an evidentiary threshold rather than requiring universal regulatory notification of every weakness identified during code review, penetration testing or vulnerability research.
At the same time, companies should not transform that threshold into a requirement for complete forensic certainty. Article 14 requires an early-warning structure precisely because the facts will frequently remain incomplete during the first 24 hours, while ENISA’s current Single Reporting Platform guidance differentiates the information required at the early-warning, 72-hour notification and final-report stages, with additional information becoming required or available as the investigation develops.
The operational standard should therefore be designed around progressive evidentiary confidence rather than binary forensic completion. The first question is whether reliable evidence demonstrates malicious exploitation; the second is whether the vulnerable code or component is contained in a product with digital elements for which the legal entity is the manufacturer; the third is whether the event fits the mandatory reporting category; and only thereafter does the completeness of attribution, impact assessment and remediation become relevant to the later reporting stages.
Reportability decision framework
| Situation | Evidence condition | Presumptive Article 14 treatment | Required corporate action |
|---|---|---|---|
| Vulnerability found in internal code review | No evidence of malicious exploitation | Not automatically reportable as an actively exploited vulnerability | Remediate through vulnerability-management process and monitor exploitation intelligence |
| Researcher provides proof-of-concept | Demonstrates technical exploitability but no evidence of real malicious exploitation | Not automatically an AEV | Validate vulnerability, assess external exploitation evidence, preserve chronology |
| Customer reports exploitation and provides credible logs | Evidence plausibly demonstrates unauthorised malicious use | Immediate Article 14 assessment | Begin awareness clock assessment and escalate |
| CSIRT warns manufacturer of exploitation in the wild | Competent external source reports malicious exploitation | Strong trigger for Article 14 review | Treat as priority reportability case |
| Vulnerable third-party component is exploited elsewhere | Exploitation established, but manufacturer’s products may or may not contain affected version | Dependency analysis required | Use SBOM/product dependency records to determine affected products |
| Compromise of software-update pipeline | Security of product distribution or customer systems affected | Potential severe incident even without conventional CVE | Assess Article 14 severe-incident criteria immediately |
| Malicious code reaches users through trusted product channel | Integrity/trust function compromised | Strong severe-incident indicator | Early-warning analysis should proceed without waiting for complete attribution |
| Security event affects only manufacturer’s corporate IT | No demonstrated impact on security of product with digital elements | CRA Article 14 may not apply on those facts alone | Assess other regimes separately and confirm whether product-security impact exists |
The distinction becomes particularly consequential for third-party components, because modern software products incorporate libraries, packages, firmware, open-source dependencies and externally supplied modules. ENISA’s CRA SRP FAQ specifically directs manufacturers dealing with an actively exploited vulnerability in a third-party component to the Commission’s implementation guidance, demonstrating that the regulator expects component-level exploitation to be assessed through the manufacturer’s own product context rather than mechanically generating identical notifications from every company that has ever used the component.
This is where a software bill of materials becomes operationally valuable even before the CRA’s wider December 2027 compliance architecture is fully applicable: the practical problem created by Article 14 is that a manufacturer receiving evidence of exploitation in a shared dependency must rapidly determine which products, versions and supported branches incorporate the affected code. A vulnerability inventory that cannot perform that mapping converts a technical dependency problem into a reporting-delay problem.
Severe incidents require a product-security lens rather than a corporate-severity label
The second Article 14 reporting category concerns severe incidents having an impact on the security of a product with digital elements. Under Article 14 of Regulation (EU) 2024/2847, an incident is severe where it negatively affects, or is capable of negatively affecting, the product’s ability to protect the availability, authenticity, integrity or confidentiality of important or sensitive data or functions, or where it has led, or is capable of leading, to the introduction or execution of malicious code in the product or in a user’s network and information systems.
This legal definition creates a material mismatch with many internal incident-ranking methodologies. A company may classify an incident as “medium” because the manufacturer itself experienced little downtime or financial loss, while the same event can be legally significant because the attack compromised the product’s security function or created a path for malicious execution inside customer environments. Conversely, a major corporate ransomware incident does not become a CRA severe incident merely because the internal business impact is large if there is no relevant effect on a product with digital elements.
Internal severity versus CRA severity
| Internal corporate metric | Why it may be insufficient | CRA-relevant additional question |
|---|---|---|
| Financial loss | Measures impact on manufacturer, not product-security consequence | Did the incident affect security functions or customer systems? |
| Corporate downtime | Can be low even where compromised code reaches users | Was product integrity, authenticity or confidentiality affected? |
| Number of corporate endpoints compromised | Does not necessarily map to product exposure | Did the affected infrastructure build, maintain, sign or distribute the product? |
| Number of known victims | Early incident counts can materially underestimate potential impact | Is the incident capable of creating broader security consequences? |
| CVSS score | Applies principally to vulnerability severity, not the entire incident architecture | Has malicious code been introduced or executed through the product? |
| Confirmed data theft | Data theft is only one possible consequence | Were important security functions compromised even without exfiltration? |
| Threat-actor attribution | Attribution can remain unknown for weeks or months | Is there sufficient evidence of malicious activity without knowing the actor? |
| Public disclosure status | Publication is not the statutory trigger | When did the manufacturer become aware of the qualifying event? |
The operational implication is that organisations should create a CRA-specific classification overlay rather than simply adding a “CRA yes/no” field to an existing enterprise incident-severity model. That overlay should test the legal properties of the product-security event independently from business-impact scoring.
The 24-hour period requires delegated authority rather than executive improvisation
The first reporting stage must be submitted without undue delay and in any event within 24 hours, meaning that the 24-hour period is a ceiling rather than an entitlement to wait until the end of the period. The same drafting applies to the 72-hour notification. The current European Commission reporting guidance and ENISA SRP FAQ both reproduce this staged structure.
A corporate workflow requiring sequential approval from the local CISO, global CISO, chief legal officer, business-unit president, CEO and communications director would therefore create a foreseeable control weakness. Governance should instead define advance authority thresholds determining who can authorise the early warning when evidence meets the reporting standard, with higher executive bodies informed concurrently rather than used as unavoidable serial bottlenecks.
Recommended internal decision-time budget
The following is an operational control model rather than a statutory allocation of the 24-hour period; its purpose is to preserve sufficient contingency inside the legal deadline rather than to redefine the legal requirement.
| Internal elapsed time from credible alert | Control objective | Responsible function | Required output |
|---|---|---|---|
| 0–1 hour | Preserve evidence and identify possible product connection | SOC / PSIRT / incident response | Incident record, source, first timestamp |
| 1–3 hours | Confirm product/version/dependency relevance | Product security + engineering | Product impact map |
| 1–4 hours | Determine whether evidence can meet AEV or severe-incident criteria | PSIRT + cyber legal | Preliminary reportability assessment |
| 2–6 hours | Establish manufacturer entity and relevant CSIRT | Legal/compliance | Jurisdiction determination |
| 3–8 hours | Determine Member States where product is known to be available | Product operations / sales / compliance | Geographic distribution data |
| 4–10 hours | Prepare statutory early-warning data | Assigned Representative + legal + PSIRT | Draft SRP submission |
| 6–12 hours | Approve and submit if threshold met | Delegated Article 14 authority | Submitted early warning |
| Remaining contingency | Resolve unexpected evidence or platform issues | Incident command | Deadline protection |
The value of this structure is not the specific hour allocation, which should differ according to organisational scale and product complexity, but the deliberate refusal to consume most of the statutory period before reporting personnel become involved.
SRP access itself has become an operational-resilience control
The production characteristics of the Single Reporting Platform create specific organisational requirements that boards and compliance teams should not treat as administrative details. ENISA states in its SRP Frequently Asked Questions that Assigned Representatives must use personal EU Login accounts with multifactor authentication; one Primary Assigned Representative can be associated with a manufacturer, while up to 20 Secondary Assigned Representatives can be established, and both Primary and Secondary Representatives can submit and update notifications within their permissions.
This matters because a compliance design based on one individual’s availability creates an avoidable single point of failure. The platform’s architecture permits redundancy, and corporate governance should exploit that redundancy by maintaining a controlled roster of trained representatives covering different time zones, absence scenarios and incident-response responsibilities.
ENISA further explains that the Assigned Representative–manufacturer relationship is validated by the relevant CSIRT, but the validation process operates in parallel with reporting and does not prevent submission while verification is pending; an unverified representative can currently submit up to 20 notifications for the manufacturer before verification becomes mandatory. The current platform also does not provide an API at initial release, although companies can automate their own internal reporting workflows, meaning that regulatory submission still includes a human platform-interaction step even where detection, case management and evidence preparation are heavily automated. ENISA — CRA SRP Frequently Asked Questions.
SRP operational readiness controls
| Control | Current ENISA platform position | Corporate implication |
|---|---|---|
| Authentication | EU Login with MFA | Accounts must exist and remain accessible during crisis conditions |
| Primary representative | One Primary AR | Avoid dependence on Primary AR for actual submission availability |
| Secondary representatives | Up to 20 | Create resilience across geography, time zones and absence |
| Submission authority | Primary and Secondary ARs can submit within permissions | Train multiple operational reporters |
| Entity verification | Performed by designated CSIRT | Maintain accurate manufacturer identity information |
| Pending verification | Does not block initial reporting within ENISA limits | Registration status should not be used as reason to miss deadline |
| API availability | No API at initial release | Human submission remains part of critical process |
| Internal automation | Permitted | Pre-populate case data and structured evidence internally |
| Wrong CSIRT selection | Notification can be invalidated and require resubmission | Jurisdiction determination must occur before crisis |
| Draft visibility | Drafts remain individual to the AR account | Avoid relying on personal drafts as shared case record |
The absence of an initial reporting API deserves particular attention for large manufacturers generating high volumes of security intelligence, because the optimal architecture becomes machine-assisted preparation with controlled human submission, rather than complete end-to-end automation. Internal systems can collect product identifiers, vulnerability data, evidence, affected geography, mitigation measures and legal classifications, but the organisation still requires human operational capacity to transpose or validate that information within the SRP interface.
Determining the correct CSIRT is a corporate-jurisdiction problem
The CRA does not allow multinational manufacturers simply to choose whichever national authority they regard as administratively convenient. Under Article 14(7), the notification uses the electronic endpoint of the CSIRT designated as coordinator in the Member State where the manufacturer has its main establishment in the Union, and the Regulation defines that concept specifically for CRA purposes as the Member State where decisions related to the cybersecurity of the manufacturer’s products with digital elements are predominantly taken. If that location cannot be established, the Regulation moves to the establishment with the highest number of employees in the Union. Regulation (EU) 2024/2847, Article 14(7).
For manufacturers without a main establishment in the Union, ENISA sets out the Article 14(7) hierarchy in its official SRP FAQ: first the Member State where the authorised representative acts for the highest number of products with digital elements; failing that, the Member State where an importer places the highest number of the manufacturer’s products on the market; failing that, the Member State where a distributor makes the highest number available; and finally, where none of those criteria resolves the question, the Member State containing the highest number of users of the manufacturer’s products.
CSIRT jurisdiction hierarchy
| Manufacturer structure | Primary test | Secondary/fallback test | Governance evidence that should exist |
|---|---|---|---|
| Manufacturer established in EU | Where product-cybersecurity decisions are predominantly taken | EU establishment with highest employee count if first test cannot determine location | Board mandates, PSIRT reporting structure, cybersecurity decision authority |
| Non-EU manufacturer with authorised representative | Member State where representative acts for highest number of products | Importer criterion if unavailable | Representative mandate and product portfolio |
| Non-EU manufacturer without determinative representative | Member State where importer places highest number of products on EU market | Distributor criterion | Import statistics and entity records |
| No determinative importer | Member State where distributor makes highest number of products available | User-location criterion | Distribution records |
| No preceding criterion resolves location | Member State with highest number of users | Final hierarchy stage | User/location records and methodology |
This hierarchy transforms corporate organisation data into regulatory evidence. Groups that have historically regarded the location of cybersecurity decision-making as an internal management matter should now be able to demonstrate where those decisions are predominantly taken, because that fact determines the legally relevant reporting endpoint.
ENISA also warns that selecting the wrong coordinator CSIRT can result in the notification being invalidated and requiring resubmission. ENISA — CRA SRP FAQ, “How do I know which national CSIRT I should report to?”. This makes pre-incident jurisdiction mapping essential for multinational companies; determining the correct authority at hour nineteen of a live exploitation case is an avoidable governance failure.
Customer and user notification becomes part of the incident architecture
Article 14 does not end with the report sent to ENISA and the coordinator CSIRT. After becoming aware of an actively exploited vulnerability or severe incident, the manufacturer must inform the impacted users and, where appropriate, all users, including information concerning risk-mitigation or corrective measures that users can deploy. The Regulation further envisages structured machine-readable communication where appropriate, while allowing designated CSIRTs to communicate information themselves when the manufacturer does not inform users in a timely manner and disclosure is considered proportionate and necessary to prevent or mitigate harm. Regulation (EU) 2024/2847, Article 14(8).
This creates a second information problem that differs from regulatory notification. Reporting authorities need legally structured incident information, while users need actionable instructions linked to the actual products and versions they operate. A manufacturer therefore requires sufficiently accurate records to determine not only that an exploited vulnerability exists but also who is exposed, which versions remain installed, which mitigations can safely be applied and through which channels affected users can be reached.
User-notification readiness
| Required capability | Operational purpose | Failure consequence |
|---|---|---|
| Product-version inventory | Identify precisely which builds are vulnerable | Over-notification or missed customers |
| Distribution geography | Determine relevant Member States and cross-border exposure | Incomplete SRP data and weak user targeting |
| Customer entitlement data | Identify organisations using affected products | Delayed communication |
| Device/update telemetry where lawful and available | Estimate actual deployment of vulnerable version | Poor exposure assessment |
| Machine-readable advisory capability | Enable automated vulnerability-management ingestion | Slow enterprise remediation |
| Multilingual communication workflow | Reach EU users effectively | Uneven risk mitigation |
| Secure advisory publication process | Prevent manipulation of remediation instructions | Secondary security risk |
| Support contact escalation | Manage user remediation questions | Operational overload |
| Version-specific mitigation testing | Ensure advice does not introduce additional failure | Remediation-induced disruption |
For enterprise manufacturers, this also changes the strategic value of customer and installed-base records. Data previously optimised for licensing, support and commercial account management now becomes part of the cybersecurity compliance architecture.
Supply-chain contracts must move faster than the statutory clock
The 24-hour legal structure can become ineffective if the manufacturer itself does not control the telemetry capable of revealing exploitation. Modern products increasingly depend on external cloud providers, managed security services, embedded components, open-source packages, software-development contractors, code-signing services and third-party infrastructure; information about active exploitation can therefore originate outside the reporting manufacturer.
The governance implication is straightforward: a supplier contract that requires notification of a cybersecurity incident “within a reasonable period” or within several business days may be structurally incompatible with the manufacturer’s own Article 14 decision window. The CRA does not transfer the manufacturer’s reporting deadline to its supplier simply because the decisive evidence was held externally.
Contractual controls for CRA-critical suppliers
| Contractual element | Governance objective | Suggested control logic |
|---|---|---|
| Security incident notification | Prevent supplier delay from consuming Article 14 window | Immediate notification on credible product-security impact |
| Evidence preservation | Support reportability determination | Preserve relevant logs, binaries, indicators and timestamps |
| Exploitation intelligence sharing | Detect active exploitation rapidly | Mandatory transfer of verified indicators and victim evidence |
| Dependency identification | Map component issue to manufacturer products | Version and build-level dependency information |
| Customer-impact support | Determine scope | Provide known affected deployments where legally permissible |
| Investigation cooperation | Populate 72-hour and final reports | Defined technical contact and escalation path |
| Continuous availability | Avoid business-hours delay | 24/7 security contact for CRA-relevant suppliers |
| Subcontractor flow-down | Prevent blind spots lower in supply chain | Equivalent notification requirements for critical subcontractors |
| Regulatory cooperation | Support lawful response | Assistance with factual records and competent-authority enquiries |
| Change notification | Maintain dependency visibility | Notify material changes to components and security architecture |
These controls should be concentrated on suppliers capable of generating material evidence rather than indiscriminately imposed on every vendor, because the decision-relevant question is whether delayed supplier information can prevent the manufacturer from determining Article 14 reportability.
Sensitive vulnerability information requires a separate disclosure decision
The reporting system is designed to distribute useful cyber intelligence across Member States, but the Regulation recognises that premature distribution of certain vulnerability information can itself increase risk. Article 16 allows dissemination of a notification to other coordinator CSIRTs to be delayed in exceptional circumstances on justified cybersecurity-related grounds for the period strictly necessary, including circumstances connected with coordinated vulnerability disclosure. The Commission subsequently adopted Commission Delegated Regulation (EU) 2026/881 of 11 December 2025, published in the Official Journal on 20 April 2026, specifically to establish the conditions governing such delays.
Manufacturers should therefore treat sensitivity designation as a controlled decision rather than as a default confidentiality request attached to every submission. The legal architecture attempts to balance dissemination with the danger that detailed exploitation information could expose unpatched systems, compromise a coordinated disclosure process or create an imminent cyber risk, and an organisation claiming heightened sensitivity should be able to explain the concrete cybersecurity basis for that position.
Sensitivity-assessment record
| Question | Purpose |
|---|---|
| Is a patch or mitigation already publicly available? | Determines whether wider technical disclosure increases exposure |
| Would the information materially improve an attacker’s ability to exploit the vulnerability? | Tests disclosure risk |
| Is exploitation geographically limited and still operationally contained? | Relevant to dissemination consequences |
| Is a coordinated vulnerability-disclosure process active? | Establishes legitimate timing considerations |
| Are critical or essential systems disproportionately exposed? | Assesses potential systemic consequence |
| Would delayed dissemination impair other Member States’ defensive capability? | Tests countervailing European interest |
| Which specific fields are sensitive? | Avoids treating whole report as uniformly sensitive |
| When should sensitivity be reassessed? | Prevents indefinite restriction |
The important corporate distinction is that sensitivity does not eliminate the underlying reporting obligation. It affects the handling and dissemination of information after submission, not the manufacturer’s ability to decide unilaterally that sensitive exploitation should remain outside the Article 14 system.
Evidence preservation becomes as important as notification speed
Because Article 14 creates explicit reporting stages, a manufacturer must expect the factual account to evolve. The 24-hour submission will frequently contain provisional information, the 72-hour notification will provide a more developed technical assessment, and the final report will contain considerably more complete information about vulnerability severity, effects, threat information, root cause and remediation. The European Commission reporting page and ENISA reporting FAQ expressly differentiate these reporting stages.
A robust corporate record should therefore preserve what was known at each reporting stage rather than rewriting the historical file using information learned later. This distinction is important for regulatory defensibility. A fact absent from the 24-hour report because it had not yet been discovered is fundamentally different from a fact that was known but omitted.
Minimum incident evidence ledger
| Evidence field | Why it matters |
|---|---|
| First signal timestamp | Establishes chronology |
| Source of information | Supports reliability assessment |
| First internal recipient | Documents information path |
| First indication of malicious exploitation | Supports AEV analysis |
| Product and versions potentially affected | Establishes CRA nexus |
| Legal manufacturer entity | Determines obligation holder |
| Member States where product is available | Supports cross-border dissemination |
| Evidence supporting severity | Supports severe-incident classification |
| Contradictory evidence | Prevents hindsight reconstruction |
| Internal decision timestamp | Shows escalation speed |
| Decision authority | Establishes governance accountability |
| SRP submission timestamp | Demonstrates deadline compliance |
| Subsequent factual changes | Explains differences between reports |
| Patch/mitigation availability timestamp | Determines vulnerability final-report timeline |
| User notification timestamp | Supports Article 14(8) compliance |
Governance should operate as one control chain rather than four departments
The CRA makes the traditional separation between technical security, legal, regulatory and customer functions increasingly difficult to maintain during product-security incidents. Product security owns the technical evidence; legal interprets the statutory threshold; compliance manages authority relationships; customer operations knows where the product is deployed; engineering develops remediation; communications manages external messaging; executive management controls material risk; and the Assigned Representative performs the actual SRP operation.
The system succeeds only when these activities operate as one chain.
CRA reporting RACI architecture
| Function | Detection | Reportability assessment | CSIRT jurisdiction | SRP submission | User notification | Remediation | Evidence record |
|---|---|---|---|---|---|---|---|
| SOC / incident response | R | C | I | I | I | C | R |
| PSIRT / product security | A/R | R | C | C | C | R | A/R |
| Product engineering | C | C | I | I | C | A/R | C |
| Cyber/legal | C | A/R | A/R | C | C | C | A |
| Regulatory compliance | I | C | R | A/R | C | I | R |
| Assigned Representative | I | I | C | R | I | I | C |
| Customer operations | C | I | C | I | A/R | C | C |
| Communications | I | I | I | I | R | I | C |
| Executive incident lead | A | A | I | A | A | A | A |
R = Responsible; A = Accountable; C = Consulted; I = Informed. The matrix is an analytical governance model rather than a statutory allocation of responsibilities and should be adapted to corporate structure.
For groups with hundreds of subsidiaries, the relevant design principle should be central legal interpretation with distributed detection, because decentralising the meaning of Article 14 creates inconsistent thresholds, while centralising all technical evidence before escalation can create delay. Local operations therefore need the authority to trigger escalation immediately, while a central product-security/legal function should preserve consistency in the ultimate reporting standard.
Control maturity can be tested quantitatively
A corporation should be able to measure whether its Article 14 architecture works rather than merely confirming that a policy exists. The most useful metrics concern information latency, mapping accuracy and operational continuity rather than the raw number of notifications submitted.
Board-level CRA reporting metrics
| Metric | What it measures | Decision significance |
|---|---|---|
| Median detection-to-PSIRT escalation time | Internal information velocity | Whether relevant evidence reaches competent function rapidly |
| 95th percentile escalation time | Tail-risk in workflow | Whether rare delays threaten statutory deadline |
| Percentage of products with current dependency map | Supply-chain visibility | Ability to identify exposure from third-party vulnerabilities |
| Percentage of EU products mapped to legal manufacturer | Entity governance | Ability to assign obligation correctly |
| Percentage of products mapped to relevant CSIRT | Jurisdiction readiness | Ability to submit without crisis-time legal analysis |
| Percentage of EU product portfolio with current distribution geography | Cross-border visibility | Ability to populate notification accurately |
| Number of trained Secondary ARs | Submission resilience | Protection against individual unavailability |
| Percentage of critical suppliers with rapid security-notification clauses | External evidence velocity | Protection against supplier-generated delay |
| Percentage of tabletop exercises completed inside internal submission target | Operational effectiveness | Tests end-to-end reporting control |
| Percentage of Article 14 decisions with complete evidence ledger | Auditability | Supports later regulatory review |
| User-notification preparation time | Communication resilience | Tests Article 14(8) capability |
| Patch availability-to-final-report timer control | Final-report governance | Prevents missed downstream deadlines |
A mature organisation should also distinguish false-negative risk from false-positive reporting risk. Excessively restrictive classification can lead to missed mandatory notifications, while indiscriminate reporting can overwhelm internal processes, unnecessarily disclose sensitive vulnerabilities and reduce the informational value of the European reporting system. The purpose of governance is therefore not to maximise the number of CRA reports but to maximise the consistency and defensibility of the reportability decision.
The first regulatory year should be treated as a control-calibration period
ENISA’s current platform guidance is unusually operationally specific for a newly applicable regime, describing Assigned Representative roles, registration, verification, notification stages, CSIRT selection, platform limitations and the information expected in different types of notification. The ENISA FAQ was updated on 17 September 2026, only days after the reporting obligations entered into application, which itself indicates that the implementation environment should be expected to evolve through updated guidance as operational experience accumulates.
Companies should therefore freeze neither their legal interpretation nor their technical workflow in September 2026. The governance architecture needs controlled versioning so that changes in Commission guidance, ENISA platform fields, CSIRT practice, delegated acts and eventual enforcement decisions can be incorporated without destroying the historical audit trail showing which rules and guidance applied when a previous incident occurred.
The Commission’s CRA implementation timetable also confirms that the reporting regime sits inside a much larger staged implementation programme extending to full CRA application on 11 December 2027, making the present period particularly important for integrating Article 14 reporting with the vulnerability-management, product-risk, technical-documentation and conformity processes that will subsequently become part of the broader regulatory system.
Corporate operating model for 2026–2027
For large manufacturers, the appropriate target architecture is an integrated CRA Product Security Reporting Control System with six permanent capabilities rather than an incident-specific emergency procedure.
| Control layer | Permanent capability | Decision-grade output |
|---|---|---|
| Detection layer | Continuous collection from SOC, PSIRT, customer support, suppliers, researchers and threat intelligence | Time-stamped candidate security events |
| Product intelligence layer | Product catalogue, supported versions, SBOM/dependency mapping, distribution geography | Rapid exposure determination |
| Legal classification layer | AEV/severe-incident decision rules, manufacturer-entity mapping, jurisdiction model | Documented Article 14 determination |
| Reporting layer | Trained Assigned Representatives, EU Login/MFA, SRP procedures, submission templates | Timely regulatory notification |
| User-protection layer | Customer mapping, advisory system, mitigation and machine-readable communications | Article 14(8) user notification |
| Assurance layer | Evidence ledger, audit trail, tabletop testing, KPI reporting, lessons learned | Demonstrable governance effectiveness |
This architecture makes the CRA reporting obligation inseparable from cyber resilience itself. A manufacturer unable to determine which products contain a compromised dependency will struggle to remediate rapidly; a manufacturer unable to identify its users will struggle to warn them; a manufacturer unable to determine where cybersecurity decisions are taken will struggle to identify the competent CSIRT; and a manufacturer unable to reconstruct when evidence entered the organisation will struggle to demonstrate why its reporting timeline was legally compliant.
Key judgments
The most important corporate effect of the CRA reporting regime is therefore not the creation of another regulatory form, but the conversion of technical awareness into a governed legal event, because the time at which evidence becomes sufficiently reliable to establish exploitation or a severe product-security incident can determine the start of a reporting clock that the organisation cannot subsequently reset through internal procedure.
The second judgment is that the highest-risk companies are not necessarily those with the weakest cybersecurity tools; organisations with strong detection but fragmented product ownership, complex subsidiary structures, poor dependency mapping or slow legal approval chains can generate high-quality technical intelligence while still failing to convert that intelligence into a compliant Article 14 response.
The third judgment is that CSIRT jurisdiction must be solved before an incident, because Article 14(7) establishes a specific hierarchy, ENISA places responsibility on the manufacturer for selecting the correct coordinator CSIRT, and an incorrect selection can require resubmission. ENISA — CRA Single Reporting Platform FAQ.
The fourth judgment is that the SRP’s current implementation model makes human operational resilience material: EU Login, MFA, Assigned Representative governance, the single Primary AR plus up to 20 Secondary ARs and the absence of an initial API mean that organisations should design reporting redundancy explicitly rather than assuming that their existing cyber automation will complete the regulatory submission. ENISA — CRA SRP Frequently Asked Questions.
The fifth judgment is that supplier-management, product inventory and customer records have become direct components of cybersecurity regulatory readiness, because Article 14 depends upon the manufacturer receiving exploitation intelligence quickly, understanding which products and jurisdictions are affected and communicating mitigation effectively to users.
What would change the assessment
The assessment would require revision if subsequent Commission guidance or controlling judicial interpretation established a materially narrower or broader standard for attributing employee, subsidiary or supplier knowledge to the manufacturer for the purpose of determining when Article 14 awareness occurs, because that issue directly affects the practical beginning of the 24-hour clock.
The assessment would also change if ENISA introduces a production API or substantially alters the Assigned Representative model, because large manufacturers could then move from machine-assisted human reporting toward much greater automation of the final regulatory submission; ENISA currently states that no API is available at initial release, while leaving open the possibility of API functionality in a future phase. ENISA — CRA SRP Frequently Asked Questions.
A further change would arise if national CSIRTs develop materially divergent validation, classification or enforcement practices despite the common legal framework, because that would transform what is presently a harmonised European reporting duty into an operational environment in which the same Article 14 facts generate meaningfully different supervisory outcomes depending upon the manufacturer’s designated coordinator.
Open official record
The official record still needs practical implementation evidence concerning how national authorities will evaluate disputed awareness timestamps, how frequently notifications are invalidated because the wrong coordinator CSIRT was selected, what evidentiary threshold authorities apply to borderline active-exploitation cases, how often manufacturers request delayed dissemination under Article 16, how frequently CSIRTs grant those requests, and whether recurring reporting failures become an important component of broader CRA market-surveillance enforcement after full application.
Those data will become increasingly important because the quality of the CRA reporting regime cannot ultimately be measured by the existence of a platform or the formal observance of deadlines alone; its institutional success will depend upon whether manufacturers consistently detect qualifying events early enough, whether authorities receive comparable and actionable information, whether users are warned quickly enough to reduce exposure and whether the resulting information can be transformed into European-level situational awareness without creating unnecessary vulnerability-disclosure risk.
Corporate Reporting Becomes an Operational Control System
Article 14 of the Cyber Resilience Act converts product-security reporting from a specialist cybersecurity activity into a time-critical corporate control function. The statutory trigger is manufacturer awareness, not completion of a forensic investigation, CVE assignment, executive incident declaration or confirmed threat-actor attribution. The central compliance variable is therefore corporate information velocity: whether technical evidence can move from SOC, PSIRT, engineering, suppliers, cloud providers, customer support or researchers into a legally competent reporting process before the 24-hour early-warning boundary becomes impossible to meet.
Awareness is the moment cyber evidence becomes legally consequential
Article 14 repeatedly uses the concept that the manufacturer “becomes aware of” an actively exploited vulnerability or severe incident. The chronology of information acquisition therefore becomes a compliance fact in its own right.
Corporate awareness-control matrix
| Information Source | Typical Evidence | CRA Relevance | Required Internal Control | Principal Governance Failure |
|---|---|---|---|---|
| Security Operations Centre | Endpoint telemetry, anomalous execution, intrusion indicators | Can establish evidence of exploitation or malicious-code execution | Automatic PSIRT escalation when a covered product may be involved | Alert remains an ordinary enterprise event |
| PSIRT / Product Security | Vulnerability reports, exploit samples, coordinated disclosure | Central to active-exploitation determination | Article 14 classification workflow and timestamping | Remediation occurs without regulatory review |
| Customer Support | Compromise reports, abnormal product behaviour, security complaints | May provide first external evidence of exploitation | Security-trigger keywords and mandatory escalation route | Ticket remains inside service workflow |
| Managed Security Provider | Detection alerts, investigation findings | Third-party exploitation evidence | Notification SLA materially shorter than CRA decision window | Weekly or monthly reporting delay |
| Cloud Provider | Logs, infrastructure compromise data | Can expose attacks affecting cloud-dependent products | Real-time incident notification and evidence protocol | Provider has evidence before manufacturer receives it |
| Vulnerability Researcher | Exploit evidence, technical proof, victim observations | Potentially decisive depending on reliability | CVD intake linked directly to CRA workflow | Research channel isolated from compliance |
| CERT / CSIRT | Campaign intelligence, victim reports, exploitation data | Potentially high-confidence evidence | Immediate executive / PSIRT escalation | Treated only as external intelligence |
| Supplier / Component Provider | Exploitation notice for integrated component | Can trigger review across many downstream products | SBOM / dependency mapping plus rapid escalation | Affected downstream products cannot be identified |
Separate ordinary vulnerability management from Article 14 reporting
| Situation | Evidence Condition | Presumptive Article 14 Treatment | Required Corporate Action |
|---|---|---|---|
| Internal code-review vulnerability | No malicious exploitation evidence | Not automatically AEV-reportable | Remediate and monitor exploitation intelligence |
| Researcher proof-of-concept | Technical exploitability only | Not automatically an AEV | Validate, preserve chronology, investigate real-world exploitation |
| Customer provides credible exploitation logs | Evidence plausibly shows malicious unauthorised use | Immediate Article 14 assessment | Begin awareness-clock analysis and escalate |
| CSIRT warns of exploitation in the wild | Competent external source | Strong Article 14 trigger | Priority reportability review |
| Third-party component exploited elsewhere | Exploitation proven but product inclusion uncertain | Dependency analysis required | Map component to product/version through SBOM records |
| Software-update pipeline compromise | Trusted distribution or customer environment at risk | Potential severe incident | Immediate Article 14 severe-incident assessment |
| Malicious code reaches users through trusted channel | Integrity / trust function compromised | Strong severe-incident indicator | Do not wait for complete attribution |
Internal severity does not equal CRA severity
Internal loss measures manufacturer impact, not necessarily product-security consequences.
Manufacturer downtime can remain low while compromised code reaches users.
Actor attribution may remain unknown for weeks or months.
Publication status is not the legal reporting trigger.
Recommended internal decision-time budget
Analytical operating model only — this does not redefine the statutory 24-hour requirement. Its purpose is to preserve contingency inside the legal deadline.
| Elapsed Time | Control Objective | Responsible Function | Required Output |
|---|---|---|---|
| 0–1h | Preserve evidence and establish possible product connection | SOC / PSIRT / IR | Incident record + first timestamp |
| 1–3h | Confirm product/version/dependency relevance | Product security + engineering | Product impact map |
| 1–4h | AEV / severe-incident analysis | PSIRT + cyber legal | Preliminary reportability decision |
| 2–6h | Establish manufacturer entity and CSIRT | Legal / compliance | Jurisdiction determination |
| 3–8h | Identify Member States where product is available | Operations / sales / compliance | Distribution geography |
| 4–10h | Prepare early-warning content | Assigned Representative + legal + PSIRT | Draft SRP submission |
| 6–12h | Approve and submit if threshold met | Delegated Article 14 authority | Submitted early warning |
| 12–24h reserve | Contingency and evidence refinement | Incident command | Deadline protection |
The reporting platform itself becomes a resilience control
| Control | Current ENISA Position | Corporate Implication |
|---|---|---|
| Authentication | EU Login + MFA | Accounts must remain accessible during crisis conditions |
| Primary Assigned Representative | One Primary AR | Do not create dependence on one person for actual submission |
| Secondary Representatives | Up to 20 | Create geographic and time-zone redundancy |
| Pending verification | Does not initially prevent reporting within ENISA limits | Registration status should never justify a missed deadline |
| Unverified reporting ceiling | 20 notifications | Verification should nevertheless be completed proactively |
| API | No API at initial release | Machine-assisted preparation + controlled human submission |
| Wrong CSIRT | Notification may be invalidated | Jurisdiction must be solved before an incident |
| Draft visibility | Individual AR account | Personal drafts cannot be the corporate system of record |
The correct authority must be determined before the crisis
Member State where cybersecurity decisions concerning products are predominantly taken.
If first test cannot determine location: EU establishment with the highest employee count.
Member State where authorised representative acts for the highest number of products.
Member State where importer places highest number of products on the EU market.
Member State where distributor makes the highest number of products available.
Where earlier criteria fail, use Member State containing the highest number of users.
Reporting authorities and warning users are two separate information problems
Supplier contracts must move faster than the statutory clock
| Contractual Element | Governance Objective | Control Logic |
|---|---|---|
| Security incident notification | Prevent supplier delay | Immediate notice on credible product-security impact |
| Evidence preservation | Support reportability analysis | Preserve logs, binaries, indicators and timestamps |
| Exploitation intelligence | Detect active exploitation quickly | Transfer verified indicators and victim evidence |
| Dependency identification | Map issue to downstream products | Version- and build-level dependency data |
| Investigation cooperation | Populate later reports | Defined technical contact and escalation path |
| Continuous availability | Avoid business-hours latency | 24/7 security contact for CRA-critical suppliers |
| Subcontractor flow-down | Prevent lower-tier blind spots | Equivalent requirements for critical subcontractors |
Sensitivity affects dissemination, not the reporting obligation
Article 16 allows delayed dissemination in exceptional cybersecurity-related circumstances, including coordinated vulnerability-disclosure scenarios. Sensitivity should therefore be a controlled, evidence-based decision rather than a generic confidentiality label.
- Is a patch already publicly available?
- Would disclosure materially improve attacker capability?
- Is coordinated disclosure active?
- Are critical systems disproportionately exposed?
- Which exact fields are sensitive?
- When should sensitivity be reassessed?
Preserve what was known at each reporting stage
The 24-hour early warning, 72-hour notification and final report intentionally reflect different levels of evidentiary maturity. Later discoveries should not overwrite the historical record.
One control chain rather than four departments
| Function | Detection | Reportability | CSIRT | SRP | Users | Remediation | Evidence |
|---|---|---|---|---|---|---|---|
| SOC / IR | R | C | I | I | I | C | R |
| PSIRT | A/R | R | C | C | C | R | A/R |
| Engineering | C | C | I | I | C | A/R | C |
| Cyber / Legal | C | A/R | A/R | C | C | C | A |
| Regulatory Compliance | I | C | R | A/R | C | I | R |
| Assigned Representative | I | I | C | R | I | I | C |
| Customer Operations | C | I | C | I | A/R | C | C |
| Executive Incident Lead | A | A | I | A | A | A | A |
Control maturity must be measurable
CRA Product Security Reporting Control System
Continuous collection from SOC, PSIRT, support, suppliers, researchers and threat intelligence.
Product catalogue, supported versions, SBOM, dependencies and distribution geography.
AEV/severe-incident rules, manufacturer mapping and jurisdiction logic.
Assigned Representatives, EU Login/MFA, SRP procedures and structured submission templates.
Customer mapping, advisories, mitigation and machine-readable communications.
Evidence ledger, audit trail, tabletop testing, KPIs and lessons learned.
Six definitive corporate implications
Technical awareness becomes a governed legal event. Internal procedure cannot reset the time at which sufficiently reliable evidence entered the manufacturer.
Strong cybersecurity does not guarantee reporting readiness. Fragmented product ownership, weak dependency mapping and slow approvals can still create Article 14 failure.
CSIRT jurisdiction must be solved before an incident. Crisis-time authority selection is an avoidable control weakness and an incorrect selection may require resubmission.
Human operational resilience remains material. EU Login, MFA, Assigned Representatives and the absence of an initial API mean submission redundancy must be explicitly engineered.
Supplier and customer data are cyber-regulatory infrastructure. They determine evidence velocity, affected-product mapping and the ability to warn users effectively.
The first regulatory year is a calibration period. Legal interpretations, ENISA fields, CSIRT practice and internal workflows require controlled versioning rather than being frozen at September 2026 assumptions.
- How regulators will evaluate disputed manufacturer-awareness timestamps.
- Frequency of invalidation caused by incorrect coordinator-CSIRT selection.
- Practical evidentiary threshold used in borderline active-exploitation cases.
- Frequency of Article 16 delayed-dissemination requests and approvals.
- Whether national validation practices diverge materially despite the common EU framework.
- Whether recurrent reporting failures become a material factor in wider CRA market-surveillance enforcement.
The CRA reporting regime is best understood as a decision-latency control system. The strongest organisations will not be those that merely possess the best cybersecurity tools, but those capable of converting distributed technical evidence into a documented legal classification, correct jurisdictional routing, timely SRP submission, user protection and auditable evidence trail without allowing organisational complexity to consume the statutory window.
ENISA’s Platform Creates a New European Cybersecurity Information Layer
Principal judgment
The strategic significance of ENISA’s Single Reporting Platform is not that the European Union has created another portal through which manufacturers transmit regulatory forms, but that the Cyber Resilience Act has established an institutional mechanism through which product-level cyber intelligence can move systematically from private manufacturers into national CSIRTs, horizontally between Member States, vertically toward ENISA and market-surveillance authorities and, where the scale of an event justifies escalation, into the European cyber-crisis-management architecture represented by EU-CyCLONe. Article 16 of [Regulation (EU) 2024/2847 — Cyber Resilience Act] establishes ENISA as the operator and maintainer of the SRP, permits Member States and ENISA to maintain their own electronic notification endpoints within the common architecture and requires the CSIRT designated as coordinator that initially receives a notification to disseminate it without delay to coordinator CSIRTs in the Member States where the manufacturer has indicated that the affected product has been made available.
This creates an information architecture fundamentally different from a conventional national incident-reporting system, because the underlying object being monitored is not primarily the attacked organisation but the product with digital elements, which can be simultaneously deployed across thousands of companies, public administrations, critical infrastructures and consumers in several Member States. A vulnerability exploited against one customer in one jurisdiction can therefore represent evidence about the exposure of users elsewhere in the Single Market, meaning that the regulatory value of the notification increases when it is combined with product identity, affected versions, exploitation characteristics, deployment geography and subsequent notifications concerning the same technology.
ENISA described the platform at its operational launch on 11 September 2026 as a mechanism allowing manufacturers to report once while communicating relevant information to the appropriate authorities, and stated that the initial operating capability will continue to be developed on the basis of operational experience and user requirements. This point is institutionally important: the SRP should currently be treated as an operational capability entering its first production phase, not as a mature intelligence environment whose performance has already been demonstrated through several years of reporting data. The public official record available only ten days after launch does not yet establish notification volumes, average dissemination times, national processing differences, false-positive rates or the number of reports that have produced cross-border defensive action.
The architecture is distributed even though the interface is single
The expression “Single Reporting Platform” can create a misleading impression of a central European repository into which manufacturers report directly and from which ENISA alone controls subsequent action. Article 16 establishes a more distributed structure: ENISA creates, manages and maintains the platform, while the architecture permits both Member States and ENISA to establish electronic notification endpoints, and the designated coordinator CSIRT remains the central national operational actor responsible for initially receiving and disseminating the notification.
The resulting system is therefore better understood as a federated European routing and information-sharing layer than as a conventional centralised regulatory inbox.
| Institutional layer | Formal role in the CRA reporting architecture | Information function | Decision significance |
|---|---|---|---|
| Manufacturer | Originates mandatory AEV or severe-incident notification | Supplies product, vulnerability, exploitation, geographic and mitigation information | Primary private-sector intelligence source |
| Assigned Representative | Operates the manufacturer-facing SRP workflow | Submits and updates the manufacturer’s notification | Operational interface, not independent regulatory authority |
| Initially receiving coordinator CSIRT | Receives notification under Article 14 jurisdiction rules | Reviews and routes information | Principal national coordination node |
| Other relevant coordinator CSIRTs | Receive information when the product was made available in their territories | Develop national awareness and response | Converts one report into multinational visibility |
| ENISA | Establishes, manages and maintains SRP | Union-level information access, platform security, analysis and escalation | Creates EU-level analytical layer |
| National market-surveillance authority | Receives information needed for CRA supervisory tasks | Connects cyber-event evidence to product compliance | Bridges incident intelligence and product enforcement |
| CSIRTs Network | Technical cooperation architecture under NIS2 | Supports technical analysis and coordination | Enables cross-state operational interpretation |
| EU-CyCLONe | Operational management of large-scale cyber incidents and crises | Receives relevant CRA-derived information from ENISA | Escalates product-security intelligence into crisis-management domain |
| NIS Cooperation Group | Receives ENISA’s periodic trend analysis | Strategic and policy-level coordination | Converts accumulated reporting into policy learning |
| European Vulnerability Database | Can receive publicly known corrected vulnerabilities with manufacturer agreement | Longer-term vulnerability knowledge | Converts incident reporting into reusable vulnerability intelligence |
This institutional chain demonstrates why the platform’s value does not arise from the act of submission itself. Its value arises from what happens after submission: whether information reaches the correct national authorities, whether affected jurisdictions are identified accurately, whether national CSIRTs can interpret and correlate the reports, whether ENISA can detect broader patterns and whether those patterns are translated into defensive action before exploitation expands.
The SRP establishes cross-border dissemination as the default rule
Article 16 creates an important presumption in favour of circulation. After receiving a notification, the coordinator CSIRT initially receiving it must disseminate it without delay through the SRP to the coordinator CSIRTs in Member States where the manufacturer has indicated that the affected product has been made available. The resulting dissemination universe therefore depends partly upon the manufacturer’s own geographic information, making product-distribution data an input not merely into corporate compliance but into European governmental situational awareness.
The mechanism can be represented as follows:
| Information stage | Origin | Default destination | Legal/operational effect |
|---|---|---|---|
| Initial CRA submission | Manufacturer | Coordinator CSIRT + ENISA through SRP | Creates official product-security record |
| Cross-border routing | Initially receiving coordinator CSIRT | Relevant coordinator CSIRTs | Extends visibility across affected Member States |
| Supervisory transfer | National coordinator CSIRT | National market-surveillance authority | Connects incident information with CRA enforcement |
| Technical assessment | CSIRT ecosystem / ENISA | Relevant EU cyber structures | Supports interpretation and correlation |
| Crisis escalation | ENISA | EU-CyCLONe where relevance threshold is met | Integrates CRA intelligence into large-scale operational coordination |
| Strategic analysis | ENISA | NIS Cooperation Group | Converts accumulated notifications into trend assessment |
| Vulnerability knowledge | ENISA, with manufacturer agreement and after remediation availability | European Vulnerability Database | Converts corrected public vulnerability into persistent EU vulnerability record |
The immediate policy consequence is that manufacturer geography becomes threat-intelligence geography. If the same router, operating system, identity product, industrial control component or enterprise application is marketed in 20 Member States, evidence of malicious exploitation discovered initially in one jurisdiction is potentially relevant to defensive authorities in all 20. The CRA therefore introduces a legal mechanism designed to prevent the initial discovery location from determining the geographical limits of the response.
This matters particularly for vulnerabilities in widely distributed horizontal technologies because their systemic significance cannot reliably be inferred from the first victim. A vulnerability initially exploited against one organisation may become strategically important because the same software component is embedded across several sectors, governments or critical-service providers. The SRP’s architecture allows national evidence to acquire European relevance before every Member State independently observes successful exploitation.
The system depends critically on the manufacturer’s geographic data
The cross-border dissemination rule contains an operational dependency that deserves more attention than it has generally received: the receiving CSIRT distributes the report according to the Member States in which the manufacturer indicates that the product has been made available. The geographic accuracy of the European warning network therefore depends partly upon commercial and distribution information maintained by the reporting company.
For policymakers, this creates a potential information-quality problem because product distribution is not always synonymous with observed deployment. Manufacturers may distribute through intermediaries, online marketplaces, channel partners, multinational procurement contracts or software-download models that make the ultimate location of users harder to determine than a conventional shipment record would suggest.
Geographic intelligence quality hierarchy
| Manufacturer data | Information quality for SRP routing | Principal limitation |
|---|---|---|
| Verified installed-base data by Member State | Very high | May raise data-governance/privacy constraints depending on implementation |
| Active subscription/customer data | High | Does not necessarily represent secondary deployment locations |
| Distributor shipment data | Moderate-high | Product can move after first distribution |
| Importer records | Moderate | Shows market-entry point rather than final use |
| Online sales records | Variable | Location may reflect purchaser rather than actual installation |
| Download telemetry | Potentially high | Depends on product architecture, consent and telemetry quality |
| Historical sales data | Moderate-low | Does not establish whether product remains operational |
| “Available across EU” assumption | Low analytical precision | Creates overbroad routing without deployment intelligence |
The policy implication is not that manufacturers should collect unlimited customer telemetry, but that the effectiveness of the statutory dissemination system depends upon transparent definitions of what constitutes sufficient evidence that a product “has been made available” in a Member State. If manufacturers adopt materially different methodologies, the same cross-border exposure pattern could produce different dissemination footprints.
The platform creates a new intelligence source, but not automatically an intelligence picture
The CRA can generate a dataset that Europe did not previously possess in the same systematic form: mandatory reports concerning known active exploitation of products with digital elements, combined with severe product-security incidents and, in later stages, voluntary reporting. ENISA’s current SRP guidance confirms that mandatory Article 14 reporting is operational, while voluntary reporting under Article 15 is planned for a future phase of the platform.
That distinction is analytically important. The initial SRP dataset will not constitute a representative census of European cyber threats because mandatory reporting is restricted to particular legally defined product-security events. It will systematically exclude many threat categories that remain outside those definitions, while the voluntary channel is not yet operational in the first platform phase.
What SRP data can and cannot establish
| Analytical question | Potential contribution of SRP | Limitation |
|---|---|---|
| Which products are being actively exploited? | Strong where manufacturers detect and correctly report exploitation | Detection capability varies between manufacturers |
| Which vulnerabilities recur across Member States? | Potentially strong after cross-report correlation | Depends on consistent product/vulnerability identifiers |
| Which product categories produce severe incidents? | Potentially strong over time | Reporting threshold and product population differ |
| Which countries experience exploitation? | Useful where geography is known | Product availability is not equivalent to confirmed exploitation |
| Which threat actor is responsible? | Sometimes available in final reports | Attribution is frequently incomplete or uncertain |
| Which sectors are most targeted? | Indirectly inferable when deployment context is known | CRA reporting is product-focused, not a complete sector incident dataset |
| How common are non-exploited vulnerabilities? | Weak | Mandatory AEV channel does not capture ordinary vulnerabilities comprehensively |
| Total number of EU cyber incidents | Cannot establish | CRA covers only a subset of cyber events |
| Attack prevalence across manufacturers | Cannot safely establish from raw report counts alone | Detection and reporting capacity varies |
| Relative security quality of products | Cannot infer directly | More reports can reflect better detection rather than worse security |
| Cross-border campaign activity | Potentially strong when technical indicators correlate | Requires analysis beyond simple notification counting |
| Supply-chain concentration | Potentially strong when common components are identified | Depends upon dependency and SBOM information |
This distinction is essential for government analysts. A large number of reports associated with a particular manufacturer cannot automatically be interpreted as evidence that its products are less secure than those of competitors, because high detection maturity, extensive deployment and stronger reporting compliance can themselves increase reporting frequency. Conversely, a low reporting volume cannot be treated as evidence of superior security.
The SRP should therefore be interpreted as an observational cyber-intelligence system affected by detection and reporting biases, not as an unbiased statistical sample of the European technology market.
Cross-report correlation is where the strategic value begins
The major intelligence opportunity emerges when individual reports are analysed as components of a broader system rather than processed as independent compliance cases. The same vulnerability identifier, software library, cryptographic component, signing infrastructure, cloud dependency or distribution mechanism can appear across multiple manufacturers, while different vulnerabilities can also reveal common adversary techniques.
A mature European analytical layer could therefore examine relationships across at least six dimensions.
| Correlation dimension | Illustrative analytical question | Potential policy value |
|---|---|---|
| Product correlation | Is the same product being exploited in several Member States? | Early multinational warning |
| Vulnerability correlation | Does the same exploited flaw appear in several incidents? | Exploitation prioritisation |
| Component correlation | Do apparently unrelated products depend on the same vulnerable component? | Supply-chain concentration analysis |
| Infrastructure correlation | Are attacks using common command-and-control, delivery or hosting infrastructure? | Campaign identification |
| Temporal correlation | Are reports clustering within hours or days? | Detect coordinated exploitation waves |
| Sector correlation | Are affected products concentrated in health, energy, finance or government? | Critical-infrastructure prioritisation |
| Geographic correlation | Is exploitation moving between Member States? | Anticipatory national warning |
| Technique correlation | Are identical exploitation techniques appearing across products? | Adversary methodology assessment |
| Update-channel correlation | Are multiple incidents connected to trusted update mechanisms? | Supply-chain crisis identification |
| Remediation correlation | Are mitigations proving effective across environments? | Response optimisation |
The CRA itself creates the basis for such analysis by requiring ENISA to prepare every 24 months a technical report on emerging trends regarding cybersecurity risks in products with digital elements, using notifications received under Articles 14 and 15, and to submit that report to the NIS Cooperation Group. The first report must be submitted within 24 months after Article 14(1) and Article 14(3) became applicable, placing the first statutory reporting horizon no later than 11 September 2028. Relevant information must also feed into ENISA’s broader report on the state of cybersecurity in the Union.
That statutory requirement confirms that the European legislature does not view the reporting system purely as an event-processing mechanism. It explicitly anticipates secondary analytical use of accumulated notifications for understanding emerging product-security risk.
Market surveillance receives a new stream of operational cyber evidence
One of the most consequential but less visible elements of Article 16 is the connection between national CSIRTs and market-surveillance authorities. After receiving a notification concerning an actively exploited vulnerability or severe incident, coordinator CSIRTs must provide their national market-surveillance authorities with the notified information necessary for those authorities to perform their duties under the CRA.
This creates a direct bridge between two institutional systems that historically served different functions: incident-response authorities focused on immediate cyber defence, and product-surveillance authorities focused on regulatory compliance and market controls.
Information-to-enforcement transmission
| Stage | Cybersecurity function | Market-regulatory significance |
|---|---|---|
| Active exploitation detected | Establish immediate threat | Indicates possible weakness in product-security lifecycle |
| Manufacturer reports through SRP | Creates formal regulatory record | Establishes documented awareness and response chronology |
| CSIRT analyses notification | Evaluates operational cyber risk | Generates evidence potentially relevant to surveillance |
| Necessary information transferred to MSA | Cyber intelligence leaves purely technical channel | Enables conformity and compliance assessment |
| MSA evaluates product | Determines CRA compliance status | Can request information and corrective action |
| Cross-border non-compliance identified | National issue becomes Single Market issue | Triggers Commission/Member-State coordination |
| Corrective measure insufficient | Security risk persists | Restriction, withdrawal or recall mechanisms can become relevant under CRA market-surveillance provisions |
The importance of this bridge will increase considerably after the CRA becomes generally applicable on 11 December 2027, because incident information will then coexist with the Regulation’s wider requirements concerning secure-by-design development, vulnerability handling, conformity assessment, technical documentation and lifecycle support. A report about an exploited vulnerability can therefore become one element of a much broader supervisory assessment concerning whether the manufacturer’s security processes were adequate.
For policymakers, this implies that the SRP will generate dual-use regulatory information: it supports immediate cyber defence while also creating evidence capable of informing product-market supervision.
ENISA is an analytical node, not the sole operational authority
ENISA’s role in the system should be understood precisely. The Agency establishes, manages and maintains the platform, receives information within the statutory architecture, protects the platform and its data, develops technical analysis and can transmit relevant information into wider Union mechanisms; however, the national coordinator CSIRT remains indispensable to reception, dissemination and several disclosure decisions.
Article 16 specifically requires ENISA to implement appropriate and proportionate technical, operational and organisational measures to manage security risks affecting both the SRP and information transmitted through it, and requires ENISA to notify the CSIRTs Network and the Commission without undue delay if a cybersecurity incident affects the platform itself. ENISA and the CSIRTs Network must also develop specifications for secure platform operation, including strict protocols and need-to-know handling where a notified vulnerability has no corrective or mitigating measure available.
This is more than an ordinary information-security requirement, because the platform can contain exceptionally valuable offensive intelligence. A database describing actively exploited vulnerabilities before remediation is available could itself become a high-value target for state actors, criminal groups and exploit brokers.
SRP threat model from a governmental perspective
| Threat against SRP ecosystem | Potential consequence | Relevant institutional safeguard |
|---|---|---|
| Unauthorized access to unpatched vulnerability details | Accelerated exploitation across EU | Confidentiality controls and need-to-know handling |
| Compromise of national endpoint | Exposure of reports routed to that Member State | Article 16 security architecture and delegated delay mechanism |
| Compromise of SRP itself | Systemic confidentiality risk | ENISA incident notification and ability to delay dissemination |
| Credential compromise of reporter | False or manipulated submissions | EU Login, MFA and representative validation |
| Malicious data poisoning | Distorted situational awareness | CSIRT review and cross-source analysis |
| Excessive internal access | Leakage of exploit details | Access control and handling protocols |
| Premature dissemination | Weaponisation of technical details | Article 16 delay safeguards |
| Excessive withholding | Other Member States remain unnecessarily exposed | Strict-necessity condition and ENISA systemic-risk role |
| Platform outage during major exploitation campaign | Reporting and dissemination degradation | Operational resilience procedures required from ENISA |
| Correlation failure | Multiple reports treated as isolated incidents | Union-level analytical capability |
ENISA’s official registration guidance confirms that SRP access currently requires an EU Login account with multi-factor authentication, while authorisation of Assigned Representatives is validated by the relevant coordinator CSIRT. These controls address the manufacturer-facing access layer, but the systemic security problem extends much further because the value of the information increases as multiple reports are aggregated.
Confidentiality is not an exception to the architecture; it is part of the architecture
The CRA reporting system is built around an inherent tension. Fast dissemination can allow another Member State to defend its infrastructure before exploitation spreads, while the same dissemination can expose detailed technical information concerning a vulnerability for which no security update exists.
The legislature therefore did not choose between complete secrecy and automatic transparency. It created a graduated dissemination architecture in which the default is rapid sharing but restricted handling is possible where defined cybersecurity risks justify it.
Commission Delegated Regulation (EU) 2026/881, adopted on 11 December 2025 and published in the Official Journal on 20 April 2026, gives operational content to the Article 16 exception by specifying when the initially receiving coordinator CSIRT may temporarily delay dissemination. The central test is demanding: considering the sensitivity of the information, the cybersecurity risks created by dissemination must outweigh its security benefits, those risks must not be adequately mitigable through handling restrictions such as the Traffic Light Protocol (TLP) or Permissible Actions Protocol (PAP), and one of the specific regulatory conditions must also be satisfied.
Delegated Regulation 2026/881: grounds related to the information itself
| Condition | Regulatory logic | Dissemination consequence |
|---|---|---|
| Effective mitigation expected within 72 hours | Short delay can reduce exposure while patch is imminent | Dissemination may be delayed; if mitigation is not available in time, dissemination must proceed |
| Information is sufficient to create an exploitation technique | Sharing itself can materially increase offensive capability | Delay until effective mitigation is available |
| Sufficient reduced information can be shared for defensive action | Relevant CSIRTs can protect systems without receiving full exploit details | Partial information can circulate before complete notification |
| Vulnerability is under coordinated vulnerability disclosure with coordinator CSIRT as trusted intermediary | Premature disclosure can disrupt CVD | Delay can continue while strictly necessary and subject to disclosure conditions |
The first condition is particularly precise and should not be diluted into a general “patch coming soon” exception: where a manufacturer indicates that an effective risk-mitigation measure is expected within 72 hours, delayed dissemination can be considered, but if the mitigation does not become available in that period the initially receiving CSIRT must disseminate the notification to the relevant CSIRTs.
The second condition recognises that some vulnerability reports contain sufficient technical information for an attacker to construct an exploit, particularly when the flaw can be identified and weaponised by actors with limited skills or resources. The regulatory response is therefore not to suppress the information permanently, but to delay wider dissemination until an effective mitigation such as a security update or user guidance becomes available.
The third condition is analytically sophisticated because it introduces the possibility of information minimisation rather than binary disclosure. If the initially receiving CSIRT can provide enough information for other CSIRTs to implement adequate mitigations without transmitting the most dangerous technical detail, the system can preserve defensive utility while reducing exploitation risk. Once effective mitigation becomes available, the full notification is then disseminated.
A recipient CSIRT can itself become the security risk
Delegated Regulation 2026/881 goes further by recognising that the danger can arise not from the content of the report but from the security condition of the authority that would receive it. Dissemination to a particular relevant CSIRT may be delayed when that CSIRT has suffered a cybersecurity incident casting doubt on its ability to protect the information or where sufficient reason exists to believe its capabilities are inadequate to guarantee confidentiality.
This is an unusually important institutional safeguard because it rejects the assumption that governmental recipients are automatically trusted merely because they possess formal authority.
| Recipient-side condition | Permitted response | Termination condition |
|---|---|---|
| Relevant CSIRT has suffered security incident affecting confidentiality | Delay dissemination to that CSIRT | Capability restored and CSIRTs Network informed |
| Serious capability deficiencies undermine confidentiality | Delay dissemination | CSIRT provides evidence deficiencies were addressed |
| Other relevant CSIRTs remain secure | Delay can be targeted rather than system-wide | Secure recipients need not automatically be deprived of information |
| SRP itself suffers confidentiality-threatening incident | Dissemination through platform may be delayed | ENISA confirms platform confidentiality is restored |
The rule has a broader governance implication: European cyber-information sharing is becoming capability-conditioned rather than status-conditioned. The right institution to receive sensitive information still needs the practical capability to protect it.
The platform itself has a legally recognised failure mode
Article 5 of Delegated Regulation 2026/881 addresses an especially important scenario: compromise of the SRP itself. Where ENISA informs the CSIRTs Network that a cybersecurity incident has affected the platform in a way that casts doubt on the confidentiality of the submitted information, the initially receiving CSIRT can delay dissemination through the platform until ENISA confirms that confidentiality has been restored.
This provision demonstrates that the EU has formally acknowledged a paradox inherent in central cyber-reporting infrastructure: the mechanism established to reduce systemic cybersecurity risk can itself become a concentration point for highly sensitive vulnerability intelligence.
For governments, the appropriate resilience standard should therefore include not only platform availability but at least four separate dimensions:
| SRP resilience dimension | Core question |
|---|---|
| Availability | Can reports still be submitted and routed during a major cyber campaign? |
| Confidentiality | Can unpatched vulnerability information be protected against unauthorised access? |
| Integrity | Can authorities trust that notification content has not been altered? |
| Authentication | Can the platform reliably establish who is acting for the manufacturer? |
| Segmentation | Can compromise of one national endpoint be prevented from exposing wider platform data? |
| Recovery | Can trusted operation be restored rapidly after an incident? |
| Auditability | Can authorities reconstruct access, routing and modification history? |
| Alternative communication | Can critical information still move when normal SRP dissemination is suspended? |
The public official record currently establishes the legal security requirements but does not publish enough architectural detail to permit an external assessment of the platform’s technical resilience against sophisticated attack. That absence should not be filled with speculation.
Particularly Exceptional Circumstances create an even narrower information channel
Separate from the ordinary exceptional delay mechanism, Article 16 contains a more restrictive mechanism for particularly exceptional circumstances, and ENISA has implemented a specific operational process for it within the SRP. According to ENISA’s guidance updated on 9 September 2026, the mechanism applies only in connection with the 72-hour notification of an actively exploited vulnerability, not as a general confidentiality switch for all CRA reports.
ENISA’s implementation guidance states that the reporter assesses during the initial 72-hour period whether the conditions apply and flags the relevant indicator in the 72-hour AEV notification. The coordinator CSIRT—not the manufacturer—then retains responsibility for deciding whether restricted dissemination is justified. Where the mechanism is accepted, the complete notification is not initially made available to ENISA; ENISA instead receives only the limited information prescribed in Article 16(2), while the coordinator determines subsequent dissemination.
This is a significant legal distinction because it establishes that even ENISA’s information access is not absolute under the most sensitive conditions.
Normal, exceptional and particularly exceptional information flows
| Regime | Information to relevant CSIRTs | Information to ENISA | Decision authority | Typical security rationale |
|---|---|---|---|---|
| Normal dissemination | Full notification without delay | Full information according to SRP architecture | Statutory default | Defensive value exceeds disclosure risk |
| Exceptional delayed dissemination | Delayed or partially restricted where justified | ENISA remains within Article 16 framework | Initially receiving coordinator CSIRT | Sensitive exploit information, imminent mitigation, CVD or recipient risk |
| Particularly exceptional circumstances | Full dissemination restricted under Article 16 conditions | Only limited statutory information initially | Initially receiving coordinator CSIRT | Very high sensitivity under narrowly specified AEV conditions |
| Platform-compromise condition | Dissemination via affected SRP may be delayed | ENISA is itself platform operator managing incident | Initially receiving coordinator CSIRT following ENISA notice | SRP confidentiality cannot currently be assured |
The distinction matters because corporate requests for confidentiality do not control the ultimate dissemination decision. A manufacturer can identify sensitivity and invoke the relevant mechanism, but the coordinator CSIRT remains responsible for deciding whether the legal conditions actually justify delayed dissemination.
ENISA has a systemic-risk override function
The most important counterweight to restricted dissemination appears in Article 16 itself. Where only limited information has initially been made available to ENISA under the particularly exceptional mechanism, and ENISA concludes from that information that the case presents a systemic risk affecting security in the internal market, the Agency can recommend that the recipient CSIRT disseminate the full notification to the other coordinator CSIRTs and to ENISA.
This creates a carefully structured institutional tension between national control over an exceptionally sensitive notification and Union-level concern about systemic exposure.
The decision problem can be represented as follows:
| Consideration favouring restriction | Countervailing European consideration |
|---|---|
| Exploit can be reproduced from technical details | Other Member States may already contain exposed systems |
| Patch will be available imminently | Exploitation may spread before patch deployment |
| Disclosure could undermine active CVD | Cross-border victims may require immediate defensive action |
| Sensitive national-security exposure | Product may underpin critical services elsewhere |
| Recipient authority confidentiality concerns | Excluding that authority may itself leave national systems exposed |
| Geographic exploitation currently appears limited | Market distribution may indicate much broader latent exposure |
The CRA therefore does not assume that confidentiality and collective security always point in the same direction. It establishes institutions responsible for managing that trade-off.
EU-CyCLONe provides the escalation path from product incident to European cyber crisis
Article 17 allows ENISA to transmit information received under mandatory and voluntary CRA reporting to EU-CyCLONe where that information is relevant to the coordinated management of large-scale cybersecurity incidents and crises at operational level. In deciding relevance, ENISA can consider technical analysis performed by the CSIRTs Network.
This provision creates a formal escalation bridge:
manufacturer → coordinator CSIRT → affected CSIRTs/ENISA → technical correlation → EU-CyCLONe where large-scale operational relevance emerges.
EU-CyCLONe’s function under NIS2 is operational coordination of large-scale cybersecurity incidents and crises rather than routine handling of every cybersecurity report. Current EU cyber-crisis guidance similarly describes EU-CyCLONe as the network for coordinated operational management of major cross-sectoral cyber incidents and stresses the need for information exchange between technical, operational and political layers.
Escalation ladder
| Level | Typical condition | Principal actors | Objective |
|---|---|---|---|
| Product event | AEV or severe incident detected | Manufacturer | Identify and report |
| National cyber event | National users or infrastructure exposed | Coordinator CSIRT | Technical response |
| Cross-border product event | Same product exposed in several states | Multiple coordinator CSIRTs + ENISA | Shared situational awareness |
| Systemic EU concern | Broad market/security consequences | ENISA + CSIRTs Network | Union-level technical assessment |
| Large-scale cyber incident/crisis | Significant cross-border operational consequences | EU-CyCLONe | Coordinated operational management |
| Political/crisis-management relevance | Effects extend beyond technical response | EU institutions and Member States through wider crisis architecture | Strategic coordination |
Not every widely deployed vulnerability should therefore become a cyber-crisis case. The relevant threshold is whether the information becomes significant for the coordinated management of a large-scale cybersecurity incident or crisis, not merely whether the product is popular.
Public disclosure sits above manufacturer preference when defensive necessity requires it
Article 17 adds another important information pathway: where public awareness is necessary to prevent or mitigate a severe incident, to manage an ongoing incident or otherwise serves the public interest, the coordinator CSIRT may, after consulting the manufacturer and where appropriate cooperating with ENISA, inform the public or require the manufacturer to do so.
The legal architecture therefore contains multiple layers of information release:
| Disclosure level | Recipient | Default status |
|---|---|---|
| Restricted manufacturer case data | Coordinator CSIRT / ENISA | Regulatory |
| Cross-border authority dissemination | Relevant coordinator CSIRTs | Default where product is available |
| Market-surveillance disclosure | National MSA | Necessary regulatory information |
| EU-CyCLONe escalation | Operational crisis network | Conditional on large-scale relevance |
| Public disclosure | Users/general public | Conditional on prevention, mitigation or public interest |
| European Vulnerability Database | Public vulnerability ecosystem | After corrective measure and with manufacturer agreement |
This progression confirms that confidentiality under the CRA is managed rather than absolute. Manufacturer sensitivity is an important factor, but it does not provide unilateral control over information whose disclosure authorities consider necessary for preventing or mitigating significant harm.
The European Vulnerability Database creates a bridge from confidential reporting to public knowledge
Article 17 also provides that, after a security update or other corrective or mitigating measure becomes available, ENISA must, in agreement with the manufacturer, add a publicly known vulnerability notified under the CRA to the European Vulnerability Database established under NIS2.
This creates a lifecycle in which information can move through fundamentally different confidentiality states:
| Vulnerability stage | Principal information status |
|---|---|
| Initial private discovery | Manufacturer/researcher information |
| Confirmed active exploitation | Mandatory regulatory information |
| Unpatched high-sensitivity stage | Restricted/need-to-know handling possible |
| Cross-border defensive stage | Relevant CSIRT sharing |
| Remediation available | Wider technical dissemination becomes safer |
| Publicly known corrected vulnerability | Potential European Vulnerability Database entry |
| Long-term analytical stage | Aggregated ENISA trend assessment |
This sequence is strategically important because it allows the European system to preserve secrecy when secrecy has defensive value while eventually converting remediated vulnerability information into a public knowledge resource.
The first 24-month dataset will be more important than raw launch statistics
Article 17 requires ENISA’s first technical report on emerging product cybersecurity risks within 24 months of the reporting obligations becoming applicable, which places September 2028 as the critical first analytical benchmark.
The most useful governmental indicators should therefore go considerably beyond the number of submissions.
Decision-useful indicators for the first 24 months
| Indicator | What it would reveal | Why policymakers should monitor it |
|---|---|---|
| Total mandatory AEV reports | Scale of observed active exploitation | Baseline platform workload |
| Total severe-incident reports | Product-security incident burden | Distinguishes vulnerability exploitation from broader incidents |
| Unique products affected | Concentration of risk | Prevents report-count distortion |
| Unique manufacturers reporting | Breadth of compliance participation | Detects reporting concentration |
| Reports affecting >1 Member State | Cross-border significance | Measures value of common platform |
| Median number of affected Member States per report | Geographic propagation | Indicates transnational exposure |
| Median CSIRT dissemination latency | Operational information speed | Tests system against rapid exploitation |
| Percentage under exceptional delay | Sensitivity-management frequency | Shows use of confidentiality safeguard |
| Percentage using PEC | Frequency of highest-sensitivity cases | Tests whether exceptional mechanism remains exceptional |
| Median duration of delayed dissemination | Defensive cost of confidentiality | Reveals exposure created by withholding |
| Reports escalated to EU-CyCLONe | Crisis relevance | Measures intersection with large-scale incidents |
| Reports transferred to market-surveillance action | Regulatory consequence | Connects cyber events to CRA enforcement |
| Public warnings issued by CSIRTs | Protective intervention | Measures authority override use |
| Vulnerabilities later added to EUVD | Knowledge conversion | Shows transition into public vulnerability ecosystem |
| Cross-report correlations identified | Intelligence yield | Measures analytical rather than administrative value |
| Reports involving shared components | Supply-chain concentration | Identifies systemic dependency risk |
| Platform security incidents | Trustworthiness of infrastructure | Tests SRP resilience |
| Notifications submitted to wrong CSIRT | Jurisdictional friction | Measures usability and manufacturer preparedness |
The public official record currently provides none of these outcome statistics at a mature scale, because the platform became operational only on 11 September 2026. Any numerical claim about current annual reporting volume, average dissemination latency, percentage of reports involving cross-border exploitation or rate of EU-CyCLONe escalation would therefore be premature unless and until ENISA or national authorities publish verified operational data.
Data quality will determine whether SRP becomes intelligence infrastructure or merely compliance infrastructure
The central analytical vulnerability of the system is not necessarily platform technology but semantic inconsistency. If manufacturers describe products differently, classify affected versions inconsistently, use different vulnerability identifiers, provide different geographic granularity or apply different evidentiary standards when describing exploitation, the resulting information may be legally sufficient for individual reports while remaining difficult to aggregate reliably.
The most valuable long-term improvement would therefore be increased machine-readable standardisation around several core fields.
| Data field | Intelligence value | Standardisation requirement |
|---|---|---|
| Manufacturer identifier | Entity correlation | Stable legal-entity identity |
| Product identifier | Cross-report matching | Persistent product/version taxonomy |
| Vulnerability identifier | Technical correlation | CVE/EUVD or equivalent where available |
| Component identifier | Supply-chain correlation | SBOM-compatible component naming |
| Affected version range | Exposure mapping | Structured version syntax |
| Exploitation evidence type | Confidence assessment | Controlled evidence categories |
| First known exploitation date | Campaign chronology | Standard timestamps |
| Member States where product available | Geographic analysis | Defined territorial coding |
| Known affected users | Impact assessment | Structured but privacy-compatible format |
| Threat technique | Campaign correlation | Standard cyber-threat taxonomy where appropriate |
| Mitigation availability | Defensive prioritisation | Structured remediation status |
| Security-update publication | Closure analysis | Time-stamped patch state |
| Severity/impact characteristics | Cross-case comparison | CRA-aligned categories |
The regulatory architecture already anticipates secure technical and organisational specifications, while ENISA’s implementation materials demonstrate that the platform itself is expected to evolve. The question for the next implementation phase will therefore be whether the Union optimises SRP merely for successful submission or for high-quality cross-report analytics.
A European product-security sensor network is emerging, but its blind spots must remain visible
The strongest interpretation supported by the current official record is that the CRA has created the legal and technical foundations of a European product-security sensor network in which manufacturers function as distributed sources of exploitation intelligence and the SRP serves as the routing layer connecting that intelligence to national and Union institutions.
However, several blind spots remain structurally unavoidable.
First, the system sees only what manufacturers and other reporters detect. A vendor with limited telemetry can remain unaware of exploitation occurring against its products, meaning that silence in the SRP cannot be interpreted as evidence of absence.
Second, reporting quality will vary with manufacturer capability. Large technology companies with mature PSIRTs may detect weak signals faster than smaller suppliers, producing an apparent concentration of incidents in companies that are simply better at observing them.
Third, the mandatory regime is threshold-based. Ordinary unexploited vulnerabilities do not enter the mandatory AEV stream merely because they exist.
Fourth, product availability does not equal compromise. A vulnerability affecting a product marketed in 27 Member States does not establish that exploitation occurred in all 27.
Fifth, national processing capacity will matter. A common European platform cannot by itself eliminate differences in staffing, expertise, prioritisation or operational maturity between Member-State authorities.
Sixth, confidentiality creates a deliberate information-friction mechanism. In certain cases, slowing dissemination is itself a cybersecurity protection rather than a failure, but the effectiveness of that trade-off can be assessed only after operational evidence accumulates.
Governmental decision matrix
| Policy objective | Benefit of SRP architecture | Principal risk | Appropriate governmental response |
|---|---|---|---|
| Faster cross-border warning | One report can reach multiple relevant CSIRTs | Poor geographic data produces incomplete routing | Define data-quality expectations |
| Better systemic-risk identification | ENISA can compare product-level intelligence | Inconsistent identifiers impair correlation | Standardise core reporting fields |
| Protect unpatched vulnerabilities | Delay mechanisms reduce weaponisation risk | Excessive restriction leaves states exposed | Monitor frequency and duration of delays |
| Strengthen product enforcement | CSIRTs feed relevant information to MSAs | Technical evidence may be misunderstood outside cyber context | Build joint CSIRT–MSA expertise |
| Improve crisis preparedness | Relevant data can reach EU-CyCLONe | Over-escalation creates noise | Maintain strict large-scale relevance threshold |
| Improve public protection | Authorities can compel/publicise warnings | Premature disclosure can increase exploitation | Integrate technical risk assessment with disclosure decision |
| Build EU vulnerability intelligence | Remediated public vulnerabilities can feed EUVD | Database completeness may remain uneven | Align identifiers and reporting standards |
| Support SMEs | Coordinator CSIRTs must provide helpdesk support | Capacity unevenness among Member States | Measure support volume and response quality |
| Generate strategic risk analysis | ENISA must produce biennial trend report | Raw counts can be analytically misleading | Publish methodologies and denominators |
| Protect SRP itself | Legal security duties imposed on ENISA | Central intelligence concentration attracts sophisticated attackers | Treat SRP as high-value critical cyber infrastructure |
The inclusion of SME support is explicit rather than discretionary: Article 17 requires coordinator CSIRTs to provide helpdesk assistance regarding Article 14 reporting, particularly for microenterprises and small and medium-sized enterprises. This is important because unequal reporting capability would otherwise distort the European dataset toward manufacturers possessing sophisticated regulatory and product-security teams.
The critical institutional test will be time-to-defence, not time-to-collection
The most useful measure of the platform will ultimately be whether information entering the system causes exposed systems elsewhere to become safer before exploitation reaches them.
A decision-useful performance chain is therefore:
manufacturer detection → CRA notification → coordinator CSIRT validation → cross-border dissemination → technical correlation → national defensive action → user mitigation → crisis escalation where necessary.
Every step introduces latency, and every additional hour can matter when an exploit is being industrialised rapidly.
The strategic KPI should consequently not be simply “percentage of reports processed”, because administrative throughput does not demonstrate resilience. A better hierarchy would distinguish:
| Performance layer | Core measurement |
|---|---|
| Collection | Time from manufacturer awareness to submission |
| Routing | Time from submission to relevant CSIRT availability |
| Interpretation | Time from receipt to validated technical assessment |
| Correlation | Time to identify related reports or shared components |
| Warning | Time to notify exposed national actors where appropriate |
| Mitigation | Time to deployment of protective measures |
| Escalation | Time to EU-CyCLONe where large-scale conditions exist |
| Resolution | Time to effective corrective measure |
| Learning | Time to integrate findings into EU threat and policy analysis |
Only the first element is principally controlled by manufacturers. The remainder tests the European institutional machinery itself.
The 2028 Commission review will be the first major accountability point
The CRA requires the Commission, after consulting ENISA and the CSIRTs Network, to assess the functioning of the Single Reporting Platform by 11 September 2028, including the effect of the mechanism allowing delayed dissemination of sensitive notifications. The timing creates an unusually important two-year empirical window during which the Union can evaluate whether the architecture is producing useful cross-border warning without generating unacceptable disclosure risk.
That assessment should be judged against measurable operational evidence rather than implementation completion alone.
Questions the 2028 review should be capable of answering
| Strategic question | Evidence required |
|---|---|
| Does SRP reduce duplicate manufacturer reporting? | Comparison with parallel national reporting demands |
| Does it accelerate cross-border warning? | Submission-to-dissemination latency |
| Are relevant Member States consistently identified? | Geographic routing accuracy |
| Are sensitive vulnerability details adequately protected? | Security incidents, access breaches and disclosure events |
| Is exceptional delay used narrowly? | Number, duration and rationale of delay cases |
| Does delayed sharing create defensive harm? | Cases where withheld information affected response capability |
| Is PEC genuinely exceptional? | Frequency relative to total AEV reports |
| Does ENISA identify systemic patterns? | Documented cross-report analytical outputs |
| Is information reaching market surveillance effectively? | Transfer and enforcement metrics |
| Does SRP contribute to crisis management? | Relevant EU-CyCLONe escalations |
| Are SMEs able to comply effectively? | Helpdesk utilisation and reporting-quality indicators |
| Is the platform itself resilient? | Availability, confidentiality and security-incident metrics |
| Does the system improve vulnerability intelligence? | Integration with EUVD and trend reporting |
| Are national implementation differences material? | Comparative CSIRT processing data |
A review unable to answer these questions would measure deployment rather than effectiveness.
Key judgments
The first judgment is that the SRP should be understood as European cybersecurity information infrastructure, because Article 16 creates structured movement of operational product-security evidence between manufacturers, national CSIRTs, ENISA and market-surveillance authorities, while Article 17 provides explicit routes into EU-CyCLONe, strategic ENISA reporting, public warning and the European Vulnerability Database.
The second judgment is that the system’s intelligence value will come primarily from correlation rather than collection. A single notification is useful for responding to one event; hundreds or thousands of standardised notifications could reveal recurring exploitation, common components, systemic technology dependencies, cross-border campaigns and product categories associated with emerging cybersecurity risk, but only if the information is sufficiently structured and comparable.
The third judgment is that the CRA deliberately creates a controlled-disclosure architecture rather than an unrestricted information-sharing architecture. Regulation 2026/881 establishes concrete situations in which the cybersecurity danger of dissemination can outweigh its immediate benefits, including imminent mitigation, exploitability of the disclosed information, coordinated vulnerability disclosure, compromised recipient CSIRTs and compromise of the SRP itself.
The fourth judgment is that the confidentiality safeguard has its own counterweight because ENISA can identify systemic internal-market risk and recommend wider dissemination, while information can also be escalated to EU-CyCLONe when it becomes relevant to the operational management of a large-scale cybersecurity incident or crisis.
The fifth judgment is that the connection between coordinator CSIRTs and market-surveillance authorities is likely to become increasingly consequential after December 2027, because SRP notifications can evolve from immediate incident intelligence into evidence informing broader supervision of manufacturers’ product-security processes.
The sixth judgment is that the system cannot yet be judged quantitatively. As of 21 September 2026, the SRP has been operational for only ten days, while ENISA explicitly characterises the current deployment as an initial operating capability that will continue to evolve. No mature official dataset presently establishes notification volumes, cross-border dissemination performance, delay frequency, EU-CyCLONe escalation rates or enforcement outcomes.
What would change the assessment
The assessment would strengthen materially if ENISA begins publishing sufficiently granular but anonymised operational statistics demonstrating that reports are consistently correlated across products, components and Member States and that this correlation produces defensive action faster than separate national reporting would have achieved.
It would weaken if Member-State processing practices diverge materially, if geographic routing proves unreliable, if manufacturers routinely provide data that cannot be correlated, if exceptional confidentiality mechanisms become common rather than genuinely exceptional or if significant differences emerge in national CSIRT capacity to protect and process sensitive information.
A major SRP security breach exposing unpatched vulnerability information would also materially alter the assessment because the platform’s greatest strategic advantage—concentration of high-value product-security intelligence—would simultaneously be demonstrated to constitute a systemic vulnerability.
Conversely, documented cases in which SRP-derived correlation allows Member States to mitigate exploitation before national victims emerge would provide the strongest evidence that the platform has moved beyond regulatory administration and become genuine European defensive intelligence infrastructure.
Open official record
The current official record does not yet disclose the number of mandatory reports submitted since 11 September 2026, their distribution between actively exploited vulnerabilities and severe incidents, the number involving multiple Member States, the average or median dissemination time between coordinator CSIRTs, the number of Article 16 delayed-dissemination decisions, the number of PEC cases, the number of reports transferred to EU-CyCLONe, the number producing market-surveillance action, the number leading to public warnings or the number subsequently incorporated into the European Vulnerability Database.
Those figures should become central to any serious evaluation of the SRP because the existence of the information architecture has now been established by law, while its operational effectiveness, analytical yield and institutional speed remain empirical questions that the first two years of implementation must answer.
The most important policy question for 2026–2028 is therefore no longer whether Europe possesses a common reporting portal, but whether the Union can convert thousands of potentially fragmented manufacturer observations into a protected, interoperable and sufficiently rapid intelligence system capable of recognising systemic cyber risk before that risk becomes a continental cyber crisis.
ENISA’s Platform Creates a New European Cybersecurity Information Layer
The strategic significance of the Single Reporting Platform is not the creation of another compliance portal. The Cyber Resilience Act establishes a mechanism through which product-level cyber intelligence can move from manufacturers into national CSIRTs, horizontally across Member States, vertically toward ENISA and market-surveillance authorities and, where large-scale operational relevance emerges, into EU-CyCLONe. The system is therefore best understood as a federated European routing, correlation and warning layer whose effectiveness will depend on information quality, dissemination speed, confidentiality control and the ability to convert fragmented product observations into defensive action.
A single interface sits above a distributed institutional architecture
ENISA establishes and maintains the common infrastructure, but the initially receiving coordinator CSIRT remains a central national node. The architecture is therefore federated: one manufacturer notification can become multinational information without converting the SRP into a purely centralised European inbox.
Institutional architecture of the SRP
| Institutional Layer | Formal Role | Information Function | Decision Significance |
|---|---|---|---|
| Manufacturer | Originates mandatory AEV / severe-incident notification | Product, vulnerability, exploitation, geography, mitigation | Primary private-sector intelligence source |
| Assigned Representative | Operates manufacturer-facing SRP workflow | Submits and updates manufacturer notifications | Operational interface, not regulatory authority |
| Initially Receiving Coordinator CSIRT | Receives notification under Article 14 jurisdiction rules | Reviews, validates and routes information | Principal national coordination node |
| Other Relevant CSIRTs | Receive reports for products available in their territories | Develop national awareness and response | Transforms one case into multinational visibility |
| ENISA | Establishes, manages and maintains SRP | Union-level access, platform protection, analysis and escalation | Creates EU-level analytical layer |
| Market-Surveillance Authority | Receives information needed for CRA supervision | Connects incident evidence to product compliance | Bridges cyber response and enforcement |
| CSIRTs Network | Technical cooperation under NIS2 | Technical analysis and coordination | Cross-state operational interpretation |
| EU-CyCLONe | Large-scale cyber-incident operational management | Receives relevant CRA-derived intelligence | Escalates product risk into crisis-management domain |
| NIS Cooperation Group | Receives ENISA trend analysis | Strategic and policy coordination | Transforms accumulated data into policy learning |
| European Vulnerability Database | Receives corrected public vulnerabilities in defined conditions | Persistent vulnerability knowledge | Converts incident reporting into reusable intelligence |
From private observation to European defensive action
| Information Stage | Origin | Default Destination | Operational Effect |
|---|---|---|---|
| Initial CRA submission | Manufacturer | Coordinator CSIRT + ENISA | Creates formal product-security record |
| Cross-border routing | Initially receiving CSIRT | Relevant coordinator CSIRTs | Extends visibility across affected Member States |
| Supervisory transfer | National coordinator CSIRT | Market-surveillance authority | Connects incident evidence with CRA enforcement |
| Technical assessment | CSIRT ecosystem / ENISA | Relevant EU cyber structures | Supports correlation and shared analysis |
| Crisis escalation | ENISA | EU-CyCLONe | Integrates product intelligence into large-scale crisis coordination |
| Strategic analysis | ENISA | NIS Cooperation Group | Turns notifications into trend assessment |
| Vulnerability knowledge | ENISA | European Vulnerability Database | Creates persistent public vulnerability intelligence after remediation conditions are met |
Manufacturer geography becomes threat-intelligence geography
| Manufacturer Data | Routing Quality | Principal Limitation |
|---|---|---|
| Verified installed-base by Member State | VERY HIGH | Data-governance and privacy constraints may apply |
| Active subscription / customer data | HIGH | May not represent secondary deployment locations |
| Distributor shipment data | MODERATE-HIGH | Product may move after first distribution |
| Importer records | MODERATE | Shows market entry, not final deployment |
| Online sales records | VARIABLE | Purchaser location can differ from installation |
| Download telemetry | POTENTIALLY HIGH | Depends on architecture, consent and telemetry quality |
| Historical sales records | MODERATE-LOW | Does not prove continued operation |
| “Available across EU” assumption | LOW PRECISION | Overbroad routing with weak deployment intelligence |
What SRP data can and cannot establish
Active exploitation by product
Strong where manufacturers detect exploitation and classify it consistently.
Cross-border campaign correlation
Potentially strong when product, infrastructure, timing and technical indicators can be correlated.
Supply-chain concentration
Useful only when common dependencies and component identifiers are available.
Sector attack prevalence
CRA is product-focused and does not represent a complete sector incident dataset.
Relative product security quality
More reports may reflect better detection, larger deployment or stronger compliance rather than weaker security.
Total EU cyber incidents
Mandatory CRA reporting captures only a legally defined subset of cyber events.
Strategic value begins when individual cases are connected
Market surveillance receives operational cyber evidence
| Stage | Cybersecurity Function | Market-Regulatory Significance |
|---|---|---|
| Active exploitation detected | Establish immediate threat | Possible evidence of lifecycle-security weakness |
| Manufacturer reports through SRP | Create formal regulatory record | Documented awareness and response chronology |
| CSIRT analysis | Evaluate operational cyber risk | Can generate evidence relevant to supervision |
| Transfer to MSA | Cyber intelligence leaves technical channel | Enables conformity and compliance assessment |
| MSA evaluates product | CRA compliance assessment | Information requests and corrective action become possible |
| Cross-border non-compliance | Single-market security issue | Commission / Member-State coordination |
The intelligence platform itself becomes a high-value target
Confidentiality is part of the system, not an exception to it
| Condition | Regulatory Logic | Dissemination Consequence |
|---|---|---|
| Effective mitigation expected within 72 hours | Short delay can reduce exposure while patch is imminent | Delay possible; if mitigation misses the period, dissemination proceeds |
| Information sufficient to construct exploit technique | Sharing itself can increase offensive capability | Delay until effective mitigation is available |
| Reduced information is enough for defence | Defensive utility can survive without full exploit detail | Partial information can circulate first |
| Coordinated vulnerability disclosure active | Premature disclosure could undermine remediation process | Delay possible while strictly necessary |
A CSIRT can itself become the confidentiality problem
Dissemination can be delayed to a particular recipient when a cybersecurity incident or serious capability deficiency casts doubt on its ability to protect the information.
The SRP itself can become a concentration risk
Where a platform incident casts doubt on confidentiality, dissemination through the affected infrastructure can be delayed until ENISA confirms restoration of trusted operation.
Normal, exceptional and particularly exceptional flows
| Regime | Relevant CSIRTs | ENISA | Decision Authority | Security Rationale |
|---|---|---|---|---|
| Normal | Full notification without delay | Full SRP information | Statutory default | Defensive value exceeds disclosure risk |
| Exceptional Delay | Delayed or partially restricted | Within Article 16 framework | Initially receiving CSIRT | Exploit sensitivity, imminent mitigation, CVD or recipient risk |
| Particularly Exceptional | Full dissemination restricted | Only limited statutory information initially | Initially receiving CSIRT | Very high-sensitivity AEV conditions |
| Platform Compromise | SRP dissemination may pause | Platform operator managing incident | CSIRT following ENISA notice | Platform confidentiality cannot be assured |
National confidentiality control is balanced by Union-level systemic concern
- Technical detail makes exploitation reproducible
- Patch expected imminently
- Disclosure may undermine coordinated disclosure
- Sensitive national-security exposure
- Recipient confidentiality capability is doubtful
- Other Member States may already contain exposed systems
- Exploitation may spread before patch deployment
- Critical services elsewhere may depend on product
- Withholding can impair defensive preparation
- Market distribution may indicate broader latent systemic exposure
From product event to European cyber crisis
From confidential discovery to public European vulnerability knowledge
Metrics that matter before the September 2028 review
Semantic consistency will determine analytical value
| Data Field | Intelligence Value | Standardisation Requirement |
|---|---|---|
| Manufacturer identifier | Entity correlation | Stable legal-entity identity |
| Product identifier | Cross-report matching | Persistent product / version taxonomy |
| Vulnerability identifier | Technical correlation | CVE / EUVD or equivalent where available |
| Component identifier | Supply-chain correlation | SBOM-compatible naming |
| Affected version range | Exposure mapping | Structured version syntax |
| Evidence type | Confidence assessment | Controlled evidence categories |
| First known exploitation date | Campaign chronology | Standard timestamps |
| Member-State geography | Geographic analysis | Defined territorial coding |
| Threat technique | Campaign correlation | Standard threat taxonomy where appropriate |
| Mitigation availability | Defensive prioritisation | Structured remediation status |
Policy objective, risk and institutional response
| Policy Objective | Benefit | Principal Risk | Governmental Response |
|---|---|---|---|
| Faster cross-border warning | One report reaches several CSIRTs | Poor geography → incomplete routing | Define data-quality expectations |
| Systemic-risk identification | ENISA compares product intelligence | Weak identifiers impair correlation | Standardise core reporting fields |
| Protect unpatched vulnerabilities | Delay reduces weaponisation risk | Over-restriction leaves states exposed | Monitor frequency and duration of delays |
| Strengthen product enforcement | CSIRTs feed MSAs | Technical evidence misunderstood outside cyber context | Build joint CSIRT–MSA expertise |
| Crisis preparedness | Relevant data reaches EU-CyCLONe | Over-escalation generates noise | Maintain strict large-scale relevance threshold |
| Support SMEs | CSIRT helpdesk assistance | Uneven national support capacity | Measure response volume and quality |
| Protect SRP | Centralised secure handling | High-value intelligence concentration | Treat platform as critical cyber infrastructure |
Collection alone is not resilience
| Performance Layer | Core Measurement |
|---|---|
| Collection | Manufacturer awareness → submission |
| Routing | Submission → relevant CSIRT availability |
| Interpretation | Receipt → validated technical assessment |
| Correlation | Receipt → related report / component identification |
| Warning | Validated risk → exposed national actor notification |
| Mitigation | Warning → protective measure deployment |
| Escalation | Systemic conditions → EU-CyCLONe |
| Learning | Incident closure → integration into EU analysis |
Six decision-grade judgments
The SRP is cybersecurity information infrastructure. Its strategic value lies in structured information movement between private-sector manufacturers, CSIRTs, ENISA, surveillance authorities and crisis-management institutions.
Correlation matters more than collection. Standardised multi-report analysis is what can reveal recurring exploitation, common dependencies, coordinated campaigns and systemic product risk.
The CRA creates controlled disclosure, not unrestricted sharing. Delay and minimisation mechanisms exist where dissemination itself would materially increase cybersecurity risk.
Confidentiality has a systemic counterweight. ENISA can identify internal-market systemic risk and wider EU crisis structures can receive relevant information where large-scale consequences emerge.
Cyber intelligence can become enforcement evidence. The CSIRT–market-surveillance bridge will grow in significance once the wider CRA product-security regime becomes applicable in December 2027.
The platform cannot yet be judged quantitatively. As of 21 September 2026, the first ten days of production do not provide a mature evidence base for volumes, latency, correlation yield or enforcement outcomes.
- Number of mandatory reports submitted since 11 September 2026.
- Distribution between actively exploited vulnerabilities and severe incidents.
- Median cross-CSIRT dissemination latency.
- Number and duration of exceptional delayed-dissemination decisions.
- Frequency of particularly exceptional circumstances.
- Number of EU-CyCLONe escalations.
- Number of cases producing market-surveillance action.
- Number of notified vulnerabilities later incorporated into EUVD.
The decisive test for 2026–2028 is not whether Europe can collect manufacturer notifications, but whether the Union can convert thousands of fragmented product-security observations into a protected, interoperable and sufficiently rapid intelligence system that identifies common exposure, distributes actionable warning, preserves sensitive vulnerability information, supports market supervision and recognises systemic cyber risk before local exploitation becomes a continental crisis.
Regulatory Convergence Remains Incomplete Despite Centralised Reporting
Principal judgment
The emergence of ENISA’s Single Reporting Platform does not create a unified European cyber-incident reporting regime, because the Cyber Resilience Act, NIS2, DORA and the GDPR regulate different legal objects, different actors, different harms and different institutional relationships, even when they are activated by the same underlying cyber event. The CRA is fundamentally product-centred and asks whether an actively exploited vulnerability or severe incident affects the security of a product with digital elements; NIS2 is entity- and service-centred and asks whether an incident has a significant impact on the provision of services by an essential or important entity; DORA is sector-specific and asks whether an ICT-related incident affecting a financial entity crosses the regulatory threshold for classification as major; the GDPR is data-protection-centred and asks whether a personal-data breach creates a risk to the rights and freedoms of natural persons. These frameworks therefore overlap operationally without becoming legally interchangeable. Regulation (EU) 2024/2847 — Cyber Resilience Act, Directive (EU) 2022/2555 — NIS2, Regulation (EU) 2022/2554 — DORA and Regulation (EU) 2016/679 — GDPR establish separate statutory tests and reporting relationships.
For companies, the result is a compliance environment in which one technical incident can generate several legal clocks running simultaneously, potentially involving different legal entities within the same corporate group, several competent authorities and materially different information requirements. For governments, the structural problem is the reverse: several regulatory channels can receive overlapping fragments of the same event, but no single authority is necessarily entitled to assume that a report submitted under one regime satisfies another unless the applicable legislation or national implementation explicitly provides for such consolidation.
The central policy question is therefore not whether Europe should abolish specialised incident-reporting regimes, because their substantive purposes differ too substantially for full legal merger to be realistic, but whether the Union can develop a common intake and routing architecture capable of allowing organisations to submit core incident information once, after which legally authorised systems distribute the relevant elements to the appropriate authorities while preserving each regime’s threshold, confidentiality requirements, supervisory competence and sector-specific data needs.
This distinction between single legal obligation and single reporting infrastructure is critical. The former is neither legally justified nor presently realistic; the latter is technically and institutionally plausible and would address a substantial proportion of the duplication burden without erasing the regulatory differences that justify the separate regimes.
The four principal EU regimes regulate different dimensions of the same cyber event
The superficial similarity of their reporting clocks can obscure the much larger differences between CRA, NIS2, DORA and GDPR. Both CRA and NIS2 employ 24-hour and 72-hour stages, while DORA’s detailed regulatory technical standards similarly establish an initial notification architecture anchored in a 24-hour outer limit and a subsequent 72-hour stage; GDPR uses a 72-hour supervisory-authority deadline. Those numerical similarities do not mean that the underlying reporting triggers are harmonised.
Core EU cyber-reporting architecture
| Regime | Primary regulated object | Principal reporting entity | Core mandatory trigger | First reporting stage | Subsequent reporting | Principal recipient |
|---|---|---|---|---|---|---|
| CRA | Product with digital elements | Manufacturer | Actively exploited vulnerability or severe incident affecting product security | Early warning without undue delay, ≤24h from awareness | 72h notification; final report according to AEV/severe-incident timetable | Coordinator CSIRT + ENISA through SRP |
| NIS2 | Security of network/information systems supporting regulated services | Essential or important entity | Significant incident affecting provision of services | Early warning without undue delay, ≤24h | 72h incident notification; final report ≤1 month after notification | CSIRT or competent authority |
| DORA | ICT resilience of financial entity | Financial entity | Major ICT-related incident | ≤4h after classification as major and ≤24h after awareness | Intermediate report ≤72h after initial report; final ≤1 month | Financial-sector competent authority |
| GDPR | Personal data | Controller | Personal-data breach unless unlikely to create risk to rights/freedoms | Supervisory-authority notification where feasible ≤72h | Additional information can follow in phases where necessary | Data-protection supervisory authority |
| GDPR processor layer | Processing on behalf of controller | Processor | Awareness of personal-data breach | Without undue delay to controller | Controller determines regulatory notification | Controller |
The NIS2 timetable is expressly defined in Article 23 of Directive (EU) 2022/2555: essential and important entities must provide an early warning within 24 hours of becoming aware of a significant incident, an incident notification within 72 hours, intermediate reporting when requested and a final report no later than one month after the 72-hour notification. The NIS2 threshold is linked to significant impact on service provision and is met where the incident has caused or is capable of causing severe operational disruption or financial loss, or has affected or is capable of affecting other persons through considerable material or non-material damage.
DORA uses a separate classification architecture. Under Article 19 of Regulation (EU) 2022/2554, financial entities report major ICT-related incidents to their competent financial authority, while Commission Delegated Regulation (EU) 2025/301 establishes the detailed time limits: the initial notification must be submitted as early as possible, within four hours after classification of the ICT incident as major and no later than 24 hours after awareness; the intermediate report is due no later than 72 hours after the initial notification; and the final report is due no later than one month after the intermediate or latest updated intermediate report.
GDPR follows a fundamentally different legal logic. Article 33 of Regulation (EU) 2016/679 requires a controller to notify the competent supervisory authority without undue delay and, where feasible, within 72 hours after becoming aware of a personal-data breach unless the breach is unlikely to result in a risk to the rights and freedoms of natural persons. The GDPR therefore does not ask whether a product was actively exploited or whether an essential service suffered significant disruption; it asks whether confidentiality, integrity or availability of personal data was breached and whether that breach creates the relevant risk.
Similar deadlines conceal different legal clocks
A significant operational error would be to assume that the phrase “24-hour report” means the same thing across European cybersecurity law. The clocks differ not merely in duration but in the legal event that starts them.
Clock comparison
| Regime | Event starting relevant clock | Key legal distinction |
|---|---|---|
| CRA | Manufacturer becomes aware of qualifying AEV or severe incident | Requires product-security classification |
| NIS2 | Entity becomes aware of significant incident | Requires service-impact classification |
| DORA | Awareness plus classification as major | Initial report must also be within 4h of major classification |
| GDPR | Controller becomes aware of personal-data breach | Risk assessment determines whether notification exemption applies |
| UK PSTI | Not structured as CRA-style mandatory exploited-vulnerability incident clock | Product-security duties focus on baseline requirements and vulnerability reporting arrangements |
This produces a practical scenario in which the same company can reach the reporting threshold under one law several hours before it reaches the threshold under another.
A vulnerability may be actively exploited against a manufacturer’s software and therefore trigger CRA reporting before any NIS2-regulated customer experiences significant service disruption. Conversely, a NIS2 entity can suffer a significant availability incident caused by configuration failure without any vulnerability in the product being actively exploited, meaning that NIS2 reporting becomes mandatory while CRA reporting may not.
A cyberattack can also create a GDPR notification requirement before a manufacturer has established the evidence needed to classify an exploited product vulnerability under the CRA, because the controller may already know that personal data was unlawfully accessed while the precise exploitation path remains under investigation.
DORA creates another variation because a financial entity must first determine whether an ICT incident meets the major-incident classification criteria, but once that classification occurs the initial report must be transmitted within four hours, subject to the separate outer limit of 24 hours from awareness. Commission Delegated Regulation (EU) 2025/301, Article 5 confirms that if a financial entity does not classify the incident as major within the first 24 hours but later reaches that classification, it must submit the initial notification within four hours from classification.
The consequence is that a unified internal corporate incident record is essential, but a unified legal trigger is impossible under the current framework.
The same cyberattack can create several legally different incidents
Consider a compromised enterprise software update delivered to a European bank that introduces malicious code, exposes personal data and disrupts online banking services. The technical event may be singular, but the legal analysis fractures into several regulatory perspectives.
Multi-regime attack decomposition
| Factual element | CRA | NIS2 | DORA | GDPR |
|---|---|---|---|---|
| Malicious code introduced through software update | Potential severe product-security incident | Relevant if service impact significant | Relevant ICT incident | Relevant only if personal data affected |
| Vulnerability actively exploited | Direct CRA trigger if statutory definition met | Relevant cause, but not itself sufficient | Relevant to classification | Relevant security cause, but not reporting trigger by itself |
| Banking service unavailable | Indirect product consequence | Potential significant incident | Potential major ICT incident | Relevant only insofar as personal-data availability constitutes breach |
| Customer credentials exfiltrated | Product-security consequence | Potential material/non-material damage | ICT consequence | Personal-data breach |
| Manufacturer knows before bank | Manufacturer clock can start first | Bank’s NIS2 clock has not necessarily started | Bank clock has not necessarily started | Controller awareness determines GDPR clock |
| Bank knows before manufacturer | CRA manufacturer may not yet be aware | NIS2 clock can start | DORA clock can start | GDPR clock can start |
| Patch issued | Relevant CRA remediation/final reporting | Mitigation information | Relevant incident resolution | Security remediation |
| Bank has customers in several EU states | Product distribution relevant to CRA routing | Cross-border impact relevant | Cross-border financial impact relevant | Lead/supervisory authority issues may arise |
The practical consequence is that organisations should abandon the concept of a single binary “reportable cyber incident” status. The appropriate model is a regulatory trigger matrix in which each incident is evaluated independently against every potentially applicable legal regime.
The reporting burden is multiplicative because the regulated entity is not always the same legal person
Complexity increases significantly in multinational groups because the entity responsible under each regime may differ.
A parent technology company can be the CRA manufacturer, a banking subsidiary can be the DORA financial entity, another European group company can be the NIS2 essential or important entity, and a customer-facing subsidiary can be the GDPR controller. Those legal persons may share technology and security operations but retain separate statutory duties.
Entity-mapping problem
| Corporate role | Possible relevant regime | Compliance consequence |
|---|---|---|
| Software manufacturer | CRA | Must analyse AEV/severe product incident |
| Cloud-service subsidiary | NIS2 | Can be essential/important entity depending on scope |
| Bank or insurer | DORA | Sectoral major ICT reporting |
| Group data controller | GDPR | Personal-data breach analysis |
| Processor | GDPR | Must notify controller without undue delay |
| Importer/distributor | CRA product-market obligations | Separate duties from manufacturer |
| UK distributor | PSTI | UK product-security obligations |
| Parent company | Potentially none directly for specific incident | Cannot assume group reporting automatically discharges subsidiary duties |
For boards of multinational corporations, this means that incident reporting cannot be assigned solely by technology platform. It must also be mapped by legal entity, regulatory role and jurisdiction.
CRA and NIS2 are deliberately complementary, not duplicates
The strongest apparent overlap exists between CRA and NIS2 because both use 24-hour and 72-hour notification stages and both involve CSIRTs. Their substantive functions are nevertheless distinct.
The CRA regulates manufacturers and products with digital elements, whereas NIS2 regulates entities providing services across sectors such as energy, transport, banking, financial-market infrastructure, health, drinking water, wastewater, digital infrastructure, ICT service management, public administration and manufacturing categories identified by the Directive. Directive (EU) 2022/2555 explicitly defines a significant incident through effects on service provision rather than product exploitation.
CRA–NIS2 boundary
| Question | CRA | NIS2 |
|---|---|---|
| What is protected? | Security of products with digital elements | Continuity and security of regulated entities/services |
| Who usually reports? | Manufacturer | Essential or important entity |
| Is active vulnerability exploitation itself reportable? | Yes, when statutory AEV definition met | Not automatically |
| Is service disruption required? | No for AEV reporting | Significant service impact central to trigger |
| Can product compromise without service outage trigger reporting? | Yes | Possibly not |
| Can service outage without exploited product vulnerability trigger reporting? | Not necessarily | Yes |
| Primary EU information architecture | SRP/ENISA/coordinator CSIRT | National CSIRT/competent authority + EU NIS cooperation structures |
| Final policy purpose | Product lifecycle cybersecurity and market resilience | Entity/service cyber resilience |
This distinction is particularly important where a manufacturer is itself a NIS2 entity. A cloud provider producing proprietary software, for example, could potentially encounter one event that requires a CRA analysis in its capacity as manufacturer and a NIS2 analysis in its capacity as provider of a regulated digital service.
The fact that the same organisation carries both roles does not collapse the statutory tests.
NIS2 itself recognises the problem of overlapping sectoral rules
NIS2 contains a built-in mechanism intended to prevent unnecessary duplication where equivalent sector-specific Union legislation already imposes cybersecurity risk-management or incident-reporting requirements. Article 4 provides that where sector-specific Union legal acts require essential or important entities to adopt cybersecurity risk-management measures or notify significant incidents and those requirements are at least equivalent in effect to NIS2, the corresponding NIS2 provisions do not apply to those entities in relation to those sector-specific requirements. Directive (EU) 2022/2555, Article 4.
This lex-specialis mechanism is central to understanding the relationship with DORA.
For financial entities covered by DORA, the EU intentionally constructed DORA as the specialised operational-resilience framework rather than requiring full duplicative NIS2 incident reporting. The policy objective is therefore already regulatory specialisation with information interoperability, not universal duplication.
The challenge is that this logic does not automatically solve overlaps with every other framework, particularly the CRA and GDPR, because they regulate substantively different interests.
DORA demonstrates that technical harmonisation is possible without abolishing sectoral supervision
DORA provides the clearest example of how Europe can preserve a specialised supervisory regime while still aligning its reporting structure with horizontal cybersecurity legislation.
The European Supervisory Authorities stated when developing the joint technical standards that DORA’s incident-reporting timelines were designed to align with NIS2 where possible. The final Commission Delegated Regulation (EU) 2025/301 confirms a timetable built around 24-hour, 72-hour and one-month horizons, although DORA retains its distinctive four-hour requirement following classification of an incident as major.
DORA versus NIS2
| Feature | DORA | NIS2 |
|---|---|---|
| Sector | Financial services | Broad critical and important sectors |
| First outer deadline | ≤24h from awareness | ≤24h from awareness |
| Additional trigger | ≤4h from classification as major | None equivalent |
| Intermediate stage | ≤72h after initial notification | ≤72h from awareness |
| Final stage | ≤1 month after intermediate/latest update | ≤1 month after incident notification |
| Recipient | Financial competent authority | CSIRT or competent authority |
| Supervisory logic | Prudential/financial operational resilience | Cybersecurity/service resilience |
| Cross-sector substitution | Operates as specialised regime for covered entities | Article 4 lex-specialis mechanism |
| Information flow to cyber authority | Depends on applicable institutional architecture | Native NIS framework |
The distinction between 72 hours after awareness under NIS2 and 72 hours after submission of the initial notification under DORA also demonstrates why companies should not implement one generic timer labelled “72-hour EU cyber deadline”. The actual legal reference point differs.
GDPR remains the least substitutable reporting regime
GDPR notification is often operationally bundled with cyber reporting, but legally it is the most difficult regime to absorb into a generic cybersecurity portal because its supervisory purpose concerns fundamental rights and personal-data protection rather than cybersecurity alone.
A security incident can activate Article 33 even where no CRA, NIS2 or DORA threshold is met. Conversely, an actively exploited product vulnerability can require CRA reporting without any personal-data breach whatsoever.
GDPR divergence
| Variable | GDPR position | Why it resists full consolidation |
|---|---|---|
| Legal interest | Rights and freedoms of individuals | Different from product/service cybersecurity |
| Trigger | Personal-data breach with relevant risk | Not based on technical incident severity |
| Authority | Data-protection supervisory authority | Institutionally independent from cyber regulators |
| Deadline | Where feasible ≤72h after awareness | No 24h early warning |
| Processor relationship | Processor reports to controller without undue delay | Creates private reporting chain before regulator |
| Data-subject communication | Required in high-risk cases under Article 34, subject to conditions | Distinct from CRA user-warning duties |
| Evidence | Categories/volume of personal data, consequences, mitigation | Different factual dataset from cyber incident report |
| Confidentiality/legal basis | Data-protection law | Separate institutional safeguards |
The correct objective should therefore not be to replace GDPR breach notification with CRA or NIS2 reporting, but to enable structured reuse of overlapping factual information while preserving the independent legal assessment that the GDPR requires.
The real duplication lies in common facts rather than common law
Although the legal tests differ, a large proportion of the underlying incident information is reusable.
Common factual core that can potentially be reported once
| Data field | CRA | NIS2 | DORA | GDPR |
|---|---|---|---|---|
| Incident identifier | ✓ | ✓ | ✓ | ✓ |
| Date/time first detected | ✓ | ✓ | ✓ | ✓ |
| Date/time awareness established | ✓ | ✓ | ✓ | ✓ |
| Reporting entity | ✓ | ✓ | ✓ | ✓ |
| Contact person | ✓ | ✓ | ✓ | ✓ |
| Technical description | ✓ | ✓ | ✓ | ✓ |
| Malicious activity suspected | ✓ | ✓ | ✓ | Potentially |
| Indicators of compromise | Relevant | Explicitly relevant | Relevant | Relevant where available |
| Product/version | Central | Sometimes | Sometimes | Sometimes |
| Service affected | Sometimes | Central | Central | Sometimes |
| Personal data affected | Sometimes | Sometimes | Sometimes | Central |
| Geographic impact | Central to CRA routing | Cross-border relevance | Cross-border relevance | Supervisory relevance |
| Mitigation measures | ✓ | ✓ | ✓ | ✓ |
| Root cause | Later stage | Final report | Final report | Relevant where known |
| Threat actor | Where available | Relevant | Relevant | Usually secondary |
| Financial impact | Secondary | Significant-impact criterion | Important | Usually secondary |
| Data-subject impact | Secondary | Possible material/non-material damage | Possible | Central |
The duplication problem is therefore predominantly a data architecture problem rather than a legislative identity problem.
A single structured incident record can support four different legal assessments and generate four regulator-specific outputs without pretending that the obligations themselves are identical.
A “report once, route many” model is legally more realistic than a single European cyber notification
The most credible future architecture would separate three layers that are currently often conflated.
The first layer would be a Common Incident Data Layer, containing neutral factual information concerning the event.
The second would be a Regulatory Decision Layer, in which CRA, NIS2, DORA, GDPR and national rules apply their own legal triggers.
The third would be an Authority Routing Layer, through which the relevant information is transmitted to the legally competent authority.
Possible future architecture
| Layer | Function | Legal effect |
|---|---|---|
| Common incident record | Stores technical and chronological facts once | No automatic legal conclusion |
| CRA rules engine | Determines product-security reporting fields | Generates SRP notification |
| NIS2 rules engine | Determines significant-service-impact requirements | Generates national NIS notification |
| DORA rules engine | Applies major ICT classification/reporting data | Generates financial-sector report |
| GDPR rules engine | Applies personal-data breach/risk assessment | Generates DPA notification |
| National-law modules | Add country-specific requirements | Preserves national competence |
| Secure routing gateway | Routes each authorised dataset | Avoids manual repeated submission |
| Authority feedback layer | Returns requests/acknowledgements | Maintains separate supervisory processes |
This approach would achieve meaningful simplification without requiring a legally implausible merger of the European Data Protection Board, financial supervisors, national CSIRTs, product-market authorities and ENISA into one regulator.
Italy currently provides one of the clearest examples of national institutional consolidation
Italy completed NIS2 transposition through Legislative Decree No. 138 of 4 September 2024, published in the Gazzetta Ufficiale on 1 October 2024 and entering into force on 16 October 2024. The official Gazzetta Ufficiale text establishes the national framework, while the European Commission currently records Italy’s NIS2 status as “Transposed” and identifies the Agenzia per la Cybersicurezza Nazionale, ACN, as the national single point of contact. (European Commission — NIS2 Directive implementation in Italy)
Italy is particularly relevant to regulatory convergence because ACN simultaneously occupies a central national cybersecurity role while CSIRT Italia operates within the Agency. The subsequent Italian DORA implementation framework also expressly identifies ACN as the national NIS authority and CSIRT Italia as the national incident-response team. Legislative Decree implementing DORA-related national provisions, Gazzetta Ufficiale, March 2025.
This produces an institutional environment in which several cybersecurity functions are already organisationally proximate even though the substantive legislation remains separate.
Italy: regulatory interfaces
| Regime | Primary national institutional interface | Structural characteristic |
|---|---|---|
| NIS2 | ACN / CSIRT Italia | National cyber authority centrally positioned |
| CRA reporting | CRA coordinator-CSIRT architecture through SRP | EU regulation directly applicable |
| DORA | Financial authorities with statutory relationship to national cyber architecture | Sector supervision retained |
| GDPR | Garante per la protezione dei dati personali | Independent data-protection supervision |
| National cyber framework | ACN and sector NIS authorities | Central coordination with sector participation |
The Italian model therefore demonstrates that institutional proximity can reduce friction without abolishing regulatory separation.
Its principal policy challenge is now interoperability: ensuring that information already submitted through one legally valid channel can move lawfully and accurately to another competent authority when legislation permits, rather than requiring the reporting organisation repeatedly to reproduce the same factual chronology.
Germany illustrates how national portal design can already reduce duplication
Germany’s NIS2 implementation entered into force on 6 December 2025, and the BSI now directs regulated organisations to use the BSI Portal for NIS2 registration and incident reporting. The official BSI information page states that, following entry into force of the NIS2 implementation law, registration and reporting obligations are handled through that portal and that organisations can also voluntarily report incidents and anonymously report vulnerabilities. BSI — Information on NIS2 registration.
Particularly instructive is Germany’s treatment of operators that already use established reporting infrastructure: the BSI states that operators of critical installations and federal authorities may continue using the existing MIP mechanism during transition and do not need to submit the same notification additionally through the BSI Portal. BSI — NIS2 information and registration.
That principle—one valid submission should not have to be manually duplicated inside the same administrative ecosystem—is precisely the design logic that could eventually be extended across European reporting frameworks.
Germany also provides an important DORA precedent. BSI guidance developed before the final NIS2 implementation stated that DORA reports received by BaFin would be forwarded automatically and without substantive alteration to BSI, allowing relevant financial institutions to avoid duplicate cyber-incident notification under the pre-existing German BSI framework where DORA supplied equivalent reporting requirements. BSI — archived sector-specific NIS2 FAQ.
This is a significant example because it shows that regulator-to-regulator forwarding can replace company-to-regulator duplication where legal equivalence and information-sharing authority are sufficiently clear.
German model: useful design principles
| Existing practice | Broader European lesson |
|---|---|
| BSI Portal centralises NIS2 registration/reporting | Common national cyber gateway reduces administrative fragmentation |
| Existing MIP reporters need not duplicate identical submission | Legacy channels can coexist without double reporting |
| DORA data can be forwarded from financial supervisor to cyber authority | Authority-to-authority transmission can replace entity duplication |
| BSI also develops CRA technical guidance | Product and entity cyber expertise can be institutionally connected |
| Separate legal regimes remain intact | Integration need not require regulatory merger |
Germany’s administrative model therefore provides one of the strongest practical arguments for a European architecture based on authoritative forwarding rather than repeated filing.
France demonstrates the opposite problem: European harmonisation can be weakened by incomplete national transposition
France remains the most significant divergence among the major continental economies examined here because, as of the Commission’s 8 July 2026 enforcement decision, France had still not notified complete transposition of NIS2. The European Commission consequently decided to refer France, together with Ireland, Spain and the Netherlands, to the Court of Justice of the European Union, requesting financial sanctions for continued failure to notify full national transposition. European Commission — “Commission refers Ireland, Spain, France and the Netherlands to the Court of Justice for failing to transpose the rules on cybersecurity”, 8 July 2026.
The Commission noted that Member States were required to transpose NIS2 by 17 October 2024, that France had first received a formal notice in November 2024 and a reasoned opinion in May 2025, and that the failure remained unresolved sufficiently long for referral to the Court in July 2026. The Commission’s France implementation page identifies ANSSI as the single point of contact and CERT-FR as the national CSIRT, but the July 2026 infringement decision establishes that the full national transposition framework remained incomplete. European Commission — NIS2 implementation in France.
France had nevertheless developed a substantial legislative proposal combining the transposition of three interconnected EU frameworks: the Critical Entities Resilience Directive, NIS2 and the DORA-related amending directive. The French Conseil d’État opinion of 16 October 2024 explicitly described the bill as integrating physical resilience, cybersecurity and digital operational resilience in a common legislative package, while the Senate adopted the proposal in first reading on 12 March 2025 and the National Assembly’s special commission continued examining it subsequently. French Senate legislative dossier.
The French case therefore illustrates a crucial distinction: strategic integration at legislative-design level does not guarantee timely operational convergence. A country can conceptually align NIS2, critical-infrastructure resilience and DORA while still lagging in formal transposition and thereby creating uncertainty for regulated entities.
France: convergence strengths and weaknesses
| Variable | Position |
|---|---|
| Central cybersecurity authority | ANSSI |
| National CSIRT | CERT-FR |
| NIS2 conceptual integration | Strong within proposed resilience legislation |
| DORA/critical-resilience coordination | Included in same legislative project |
| Full NIS2 transposition by July 2026 | Not completed |
| EU enforcement status | Referred to CJEU on 8 July 2026 |
| CRA applicability | Direct as EU Regulation irrespective of NIS2 transposition delay |
| Principal corporate risk | Different maturity between directly applicable CRA and unfinished domestic NIS2 framework |
For multinational companies, France therefore demonstrates why European compliance mapping cannot rely solely on the assumption that EU directives produce uniform national operating environments on the date set by Brussels.
The CRA creates more uniformity than NIS2 because it is a Regulation, but national enforcement still matters
The CRA’s legal form reduces one source of divergence because Regulation (EU) 2024/2847 applies directly and does not require the Member States to recreate its substantive reporting obligation through national transposition. Germany’s BSI explicitly notes this distinction in its official CRA guidance, explaining that unlike NIS2, the CRA is a directly applicable EU Regulation.
Direct applicability does not, however, produce complete operational uniformity. Member States still designate coordinator CSIRTs, market-surveillance authorities operate nationally, enforcement resources differ, product markets differ and interactions with domestic cybersecurity legislation remain jurisdiction-specific.
This creates a two-level convergence model:
| Layer | Degree of harmonisation |
|---|---|
| CRA substantive reporting duty | High — directly applicable EU Regulation |
| SRP technical infrastructure | High — common ENISA platform |
| CSIRT routing architecture | Harmonised framework, national nodes |
| Market surveillance | National enforcement within EU framework |
| Administrative practice | Potentially variable |
| Interaction with national NIS2 rules | Variable |
| Interaction with sector regulators | Variable |
| Penalty application and enforcement intensity | Potentially variable |
The CRA therefore solves the problem of divergent national statutory wording more effectively than a directive can, but it does not eliminate differences in administrative capacity or supervisory practice.
The United Kingdom is moving on a structurally different track
The UK’s Product Security and Telecommunications Infrastructure product-security regime has been in force since 29 April 2024 and applies to consumer connectable products placed on the UK market. The official UK Government guidance on consumer connectable product security confirms that manufacturers, importers and distributors must comply with the regime and that the baseline security requirements include prohibition of universal default or easily guessable passwords, publication of information explaining how security issues can be reported and transparency regarding minimum security-update periods.
The UK’s framework therefore overlaps with the CRA in its policy objective of improving product security, but it is neither equivalent in scope nor structured around the same mandatory incident-reporting architecture.
CRA versus UK PSTI
| Variable | EU CRA | UK PSTI product-security regime |
|---|---|---|
| Core product concept | Products with digital elements | Relevant consumer connectable products |
| Geographic trigger | Product placed/made available on EU market | Relevant product supplied in UK |
| Security model | Broad lifecycle cybersecurity | Defined baseline consumer-product security requirements |
| Active-exploitation reporting | Mandatory under Article 14 | No equivalent CRA-style SRP reporting structure |
| Severe product incident reporting | Mandatory | No equivalent general CRA 24h/72h structure |
| Vulnerability-reporting policy | Part of wider vulnerability-handling framework | Manufacturer must publish security-issue reporting information |
| Update support transparency | CRA lifecycle obligations | Minimum security-update period must be published |
| Primary enforcement | National EU market-surveillance authorities | OPSS |
| Common supranational portal | ENISA SRP | None equivalent |
| Maximum headline administrative penalty | CRA penalty framework | Greater of £10m or 4% qualifying worldwide revenue |
The UK’s enforcement framework is financially significant. OPSS enforcement guidance confirms that the maximum fixed monetary penalty under the PSTI Act is the greater of £10 million or 4% of qualifying worldwide revenue, with a potential additional daily penalty of up to £20,000 per day for continuing non-compliance. OPSS can also issue compliance notices, stop notices and recall notices, seek forfeiture orders and publish details of compliance failures where appropriate.
This means that manufacturers operating across both markets face regulatory divergence rather than deregulation after Brexit. The relevant compliance question is not whether the UK or EU is more stringent in the abstract, but which products, duties and incident processes each system captures.
UK enforcement data already provides a useful warning for CRA policymakers
The UK’s enforcement experience also offers one of the few available quantitative indicators of product-security compliance maturity before the CRA’s broader requirements become fully applicable.
In its 2024–2025 Delivery Report, OPSS reported that it had assessed 82 connected-home, consumer-lifestyle and child-related connected devices, and that 75% of the in-scope products showed varying levels of non-compliance with the three UK security requirements assessed. OPSS also reported responding to 91 business enquiries and participating in outreach that reached more than 7,000 businesses.
Those figures cannot be extrapolated directly to the European CRA population, because the UK sample, regulatory obligations and product scope differ substantially, but they provide a useful policy signal: formal adoption of product-security law does not imply rapid market-wide compliance, even where the requirements are narrower than those created by the CRA.
UK evidence relevant to EU implementation
| OPSS 2024–2025 indicator | Official value | European analytical significance |
|---|---|---|
| Devices assessed | 82 | Demonstrates active product-level market surveillance |
| In-scope devices with varying levels of non-compliance | 75% | Suggests implementation friction can remain substantial after law enters force |
| Business enquiries handled | 91 | Indicates continuing need for regulator guidance |
| Businesses reached through events/webinars | >7,000 | Demonstrates importance of large-scale compliance outreach |
| PSTI maximum fixed penalty | £10m or 4% worldwide qualifying revenue | Shows strong enforcement leverage outside EU |
| Possible continuing daily penalty | £20,000/day | Adds persistent compliance incentive |
The principal lesson for European policymakers is that enforcement data should eventually distinguish documentation failures, technical-security failures, reporting failures and supply-chain failures, rather than publishing only aggregate non-compliance statistics.
Multinational manufacturers now need a jurisdiction-by-regime matrix
For companies selling products across Europe, regulatory planning should operate across at least three dimensions simultaneously: product, corporate entity and jurisdiction.
Example multinational matrix
| Scenario | EU CRA | EU NIS2 | EU DORA | EU GDPR | UK PSTI |
|---|---|---|---|---|---|
| US software vendor sells enterprise application in EU | Yes if product in scope | Only if vendor/entity independently in NIS2 scope | Usually no unless financial entity | Yes where controller/processor obligations arise | Possibly if relevant UK consumer product, otherwise no |
| German cloud provider develops proprietary digital product | Potential CRA manufacturer | Potential NIS2 entity | Could be ICT third-party provider to finance but not necessarily DORA financial entity | GDPR likely relevant | Depends on UK product scope |
| Italian bank suffers attack through third-party software | Manufacturer may have CRA duty | Bank treatment depends on sectoral lex specialis | DORA central | GDPR if personal data breach | UK PSTI not relevant unless UK connectable product involved |
| UK smart-device manufacturer sells in EU and UK | CRA for EU market | Possibly NIS2 only if separate service role | Usually not | GDPR if processing personal data | PSTI for UK market |
| French IoT producer sells consumer devices in EU | CRA | NIS2 only if independently covered | Usually not | GDPR depending on processing | PSTI if UK market supplied |
No multinational manufacturer should therefore maintain a compliance model based only on the country of headquarters.
Enforcement risk also fragments across regulators
A single incident can attract different supervisory questions from several authorities, each assessing a separate legal failure.
Regulatory inquiry matrix
| Authority type | Core question after incident |
|---|---|
| CRA market-surveillance authority | Did manufacturer comply with product cybersecurity and reporting obligations? |
| Coordinator CSIRT | Was Article 14 notification timely and technically sufficient? |
| NIS2 competent authority | Did regulated entity adequately manage risk and report significant incident? |
| Financial supervisor | Was DORA classification/reporting and ICT risk management adequate? |
| Data-protection authority | Was personal data protected and was breach notification compliant? |
| UK OPSS | Did connectable product comply with PSTI duties? |
| Consumer/product regulator | Were unsafe/non-compliant products appropriately restricted or recalled? |
The compliance exposure is therefore cumulative in institutional terms even where financial sanctions cannot simply be added mechanically without regard to applicable legal principles.
This creates a new requirement for regulatory narrative consistency. Where the same technical event is described differently to ENISA, a national CSIRT, financial supervisor and data-protection authority, differences need to be explainable by the distinct legal questions being answered rather than by uncontrolled factual inconsistency.
The largest corporate risk is inconsistent facts across parallel reports
Regulators can legitimately receive different legal analyses of the same incident; they should not receive incompatible factual chronologies.
Facts that should remain identical across all filings
| Fact | Why consistency matters |
|---|---|
| Detection timestamp | Establishes chronology |
| Awareness timestamp | Determines several statutory clocks |
| Incident start/end | Affects severity and duration |
| Systems/products involved | Determines regulatory scope |
| Versions affected | Supports technical analysis |
| Root cause when known | Core forensic fact |
| Indicators of compromise | Cross-authority technical evidence |
| Geographic footprint | Cross-border relevance |
| Number/type of affected users | Impact evaluation |
| Service downtime | NIS2/DORA materiality |
| Personal data affected | GDPR analysis |
| Remediation timeline | Demonstrates incident handling |
| External notifications already made | Supports authority coordination |
Elements that can legitimately differ
| Element | Reason |
|---|---|
| CRA classification | Product-security legal test |
| NIS2 classification | Service-impact legal test |
| DORA classification | Financial ICT major-incident test |
| GDPR risk conclusion | Rights-and-freedoms test |
| Confidentiality designation | Regime-specific disclosure rules |
| Authority-specific mitigation request | Different statutory competence |
The ideal corporate architecture therefore maintains one authoritative factual record with several regulatory interpretation layers.
A common European reporting taxonomy is more urgent than a common European reporting law
The technical path toward convergence should begin with shared data structures rather than attempting to legislate away substantive regulatory differences.
The common taxonomy should include stable fields for:
| Domain | Candidate common field |
|---|---|
| Entity identity | LEI/company registration/European identifier |
| Product identity | Product family, version, model |
| Incident identity | Unique European incident reference |
| Vulnerability identity | CVE/EUVD identifier where available |
| Time | Detection, awareness, classification, reporting timestamps |
| Geography | Member States affected/exposed |
| Threat | Malicious activity, technique, indicators |
| Impact | Availability, integrity, confidentiality, authenticity |
| Service effect | Disruption duration and severity |
| Personal-data effect | Categories and scale |
| Financial effect | Direct and indirect loss |
| Mitigation | Temporary control, patch, recovery |
| Reporting map | Authorities/regimes already notified |
| Confidentiality | Handling classification |
| Evidence maturity | Preliminary/confirmed/final |
If the same structured record could populate the CRA SRP, a NIS2 national portal, DORA supervisory forms and a GDPR notification template, reporting burden would fall substantially even while the legal obligations remained formally separate.
The Commission is already acknowledging the broader regulatory-complexity problem
The European Commission stated in July 2026 that it was pursuing further simplification of the cybersecurity regulatory framework, while its updated NIS2 materials refer to targeted amendments proposed on 20 January 2026 intended to improve legal clarity and simplify compliance with cybersecurity risk-management requirements for companies operating in the Union. The Commission estimates that the proposed changes would facilitate compliance for approximately 28,700 companies, including 6,200 micro and small enterprises. European Commission — NIS2 Directive.
These figures are important because they demonstrate that the regulatory-complexity problem has moved beyond industry complaints and into formal Commission policy design.
The future of cyber reporting should therefore be assessed against three objectives simultaneously:
| Objective | Risk if pursued alone |
|---|---|
| Maximum regulatory specificity | Excessive duplicate compliance processes |
| Maximum reporting simplification | Loss of legally important sector distinctions |
| Maximum centralisation | Concentration of highly sensitive incident data |
The appropriate architecture is consequently federated convergence, not complete centralisation.
Centralising all cyber reports in the SRP would create significant legal and security problems
The fact that ENISA now operates a common reporting platform does not mean that the SRP should simply become the intake point for GDPR, DORA and every national cyber regime.
Doing so would create at least six major problems.
First, institutional competence would become blurred. Data-protection authorities and financial supervisors possess legal functions that ENISA and national CSIRTs do not.
Second, confidentiality requirements differ between vulnerability intelligence, prudential financial information and personal-data breach information.
Third, the resulting platform would become an extraordinary concentration point for sensitive data concerning zero-day vulnerabilities, financial-system incidents, personal-data breaches, essential-service weaknesses and national critical infrastructure.
Fourth, the scope of authorised access would become difficult to reconcile with purpose-limitation principles.
Fifth, the value of a single platform would increase its attractiveness as an intelligence target.
Sixth, a common outage or compromise could degrade several major European reporting regimes simultaneously.
The safer model is therefore interoperable portals with controlled authority-to-authority exchange, potentially supported by a common technical gateway but without requiring all underlying data to exist in one undifferentiated repository.
A European “report once” system needs strict legal safeguards
A credible future architecture would require at least the following safeguards.
Minimum safeguards for cross-regime incident exchange
| Safeguard | Reason |
|---|---|
| Explicit legal basis for each onward transfer | Prevent unlawful secondary use |
| Data minimisation by recipient | Authority receives only necessary fields |
| Purpose limitation | Prevents unrestricted regulatory reuse |
| Strong authentication | Protects reporting integrity |
| Role-based access | Limits cross-regulator exposure |
| Immutable audit trail | Records who accessed or transmitted data |
| Source attribution | Authority knows whether fact came from company or another regulator |
| Version control | Prevents inconsistent incident states |
| Confidentiality marking | Preserves vulnerability sensitivity |
| Automated deadline calculation | Prevents cross-regime timing errors |
| Human legal override | Avoids automated misclassification |
| National-routing logic | Preserves jurisdictional competence |
| Incident reference interoperability | Allows cross-regulator correlation |
| Separate supervisory case files | Preserves legal independence |
| Platform-segmentation architecture | Limits compromise propagation |
The system should therefore automate data reuse and routing, not legal judgment.
The political choice is between administrative convergence and institutional centralisation
For policymakers, two different reform agendas need to be distinguished.
Administrative convergence would standardise factual data, identifiers, secure transport, acknowledgement formats and regulator-to-regulator forwarding while preserving existing legal authorities.
Institutional centralisation would transfer substantive reporting and supervisory competence toward a single European authority or platform.
The first is achievable incrementally and already has national precedents; the second would require substantially greater legislative redesign and create major questions regarding competence, data protection, financial supervision, national-security information and subsidiarity.
Reform-path comparison
| Reform path | Feasibility | Benefit | Principal downside |
|---|---|---|---|
| Common incident taxonomy | High | Reduces repeated data preparation | Requires standards alignment |
| Shared unique incident identifier | High | Improves regulator correlation | Governance rules required |
| Authority-to-authority forwarding | High-medium | Removes duplicate filing | Requires legal transfer basis |
| Pre-population across portals | Medium-high | Reduces administrative burden | Strong access controls required |
| Common authentication | Medium | Simplifies reporter access | Identity-management concentration |
| Common technical gateway | Medium | Enables report-once architecture | Cybersecurity concentration risk |
| One universal EU cyber form | Low-medium | Superficial simplicity | Cannot capture different legal tests adequately |
| One universal reporting authority | Low | Maximum centralisation | Major competence and governance problems |
| Full merger of CRA/NIS2/DORA/GDPR incident duties | Very low | Theoretical simplification | Destroys distinct regulatory purposes |
The most effective near-term model is regulatory orchestration
For companies, the operational solution should be a regulatory orchestration layer positioned above existing incident-management systems.
The orchestration process would work as follows:
technical incident → unified factual record → parallel CRA/NIS2/DORA/GDPR trigger analysis → automated deadline register → regulator-specific forms → controlled submission → acknowledgement tracking → subsequent updates from one evidence base.
Enterprise regulatory-orchestration dashboard
| Control | Required capability |
|---|---|
| Incident master ID | One identifier across all regulatory assessments |
| Legal entity mapping | Associates each obligation with correct corporate entity |
| Jurisdiction mapping | Determines competent national authority |
| Trigger engine | Applies CRA/NIS2/DORA/GDPR tests independently |
| Deadline engine | Calculates clocks from correct legal trigger |
| Submission register | Records every authority notified |
| Evidence versioning | Preserves what was known at each reporting point |
| Cross-form consistency check | Detects contradictory factual fields |
| Confidentiality engine | Restricts information by legal recipient |
| Executive view | Shows remaining deadlines and unresolved determinations |
| Regulator-response tracker | Captures information requests |
| Final-report closure control | Prevents early notification from remaining permanently unresolved |
The purpose of such a system is not to replace legal analysis but to eliminate avoidable administrative error.
Country comparison: operational convergence as of September 2026
| Variable | Italy | France | Germany | United Kingdom |
|---|---|---|---|---|
| EU CRA | Directly applicable | Directly applicable | Directly applicable | Not applicable domestically; applies to UK manufacturers placing covered products on EU market |
| NIS2 national status | Transposed | Full transposition still unnotified; referred to CJEU July 2026 | National implementation in force from 6 Dec 2025 | Not applicable as EU law |
| Central cyber authority | ACN | ANSSI | BSI | NCSC has cyber-security role; separate product regulator OPSS |
| National CSIRT | CSIRT Italia | CERT-FR | BSI national structures | NCSC/CERT functions outside EU NIS2 system |
| DORA | Applicable | Applicable | Applicable | Not applicable as EU Regulation domestically |
| GDPR | EU GDPR | EU GDPR | EU GDPR | UK GDPR/data-protection regime |
| Product-security domestic layer | CRA | CRA | CRA | PSTI |
| Product regulator architecture | National CRA market surveillance | National CRA market surveillance | National CRA market surveillance | OPSS |
| Incident portal convergence | Developing around ACN architecture | Fragmented by delayed NIS2 transposition | Strong BSI portal model | Separate sector/product frameworks |
| Principal convergence risk | Multi-authority information exchange | Legislative/transposition delay | Complex federal/sector interfaces despite strong portal architecture | EU–UK regulatory divergence |
The table illustrates that European regulatory convergence is not a single-speed process even among four major markets.
Italy demonstrates relatively complete NIS2 institutional implementation; Germany demonstrates portal-oriented administrative integration; France still carries the consequences of delayed transposition; and the United Kingdom has deliberately developed a separate product-security model outside the EU architecture.
Corporate exposure is highest at the interfaces between regimes
The most serious compliance failures are increasingly likely to occur not because companies are unaware that regulations exist, but because one team assumes another reporting process has satisfied an obligation that legally remains separate.
High-risk interface failures
| Failure | Consequence |
|---|---|
| CRA report assumed to satisfy NIS2 | Significant service incident potentially unreported |
| NIS2 report assumed to satisfy CRA | Product exploitation not reported through SRP |
| DORA report assumed automatically to satisfy GDPR | Personal-data breach deadline missed |
| GDPR notification used as substitute for cyber report | Technical/operational information insufficient |
| Parent-company report assumed to cover subsidiary | Wrong legal entity may remain non-compliant |
| National CSIRT notification assumed to satisfy another Member State obligation | Jurisdiction error |
| UK PSTI compliance assumed equivalent to CRA | EU manufacturer duties remain unmet |
| One “awareness” timestamp applied to every regime | Incorrect deadline calculations |
| One severity classification reused everywhere | Legal threshold mismatch |
| Inconsistent facts submitted to different regulators | Credibility and enforcement risk |
The correct compliance doctrine should therefore be “one incident, one factual record, multiple independent legal determinations.”
Policy options for the European Union
Common European Cyber Incident Data Standard
The Union could establish a common machine-readable schema defining core factual incident fields used across CRA, NIS2, DORA and other cybersecurity regimes, while allowing sector-specific extensions.
Expected effect: substantial reduction in repeated data preparation and improved interoperability.
Implementation burden: moderate, because regulators would need to align schemas and legacy systems.
Time-to-effect: relatively short compared with legislative merger.
Reversibility: high.
Principal risk: standardisation becoming excessively complex if every regulator attempts to place all specialised data into the common core.
European Incident Reference Number
Every regulated event could receive a unique reference identifier capable of being cited in subsequent notifications to other authorities.
Expected effect: authorities could recognise that several filings concern the same underlying event without requiring one shared case file.
Implementation burden: relatively low.
Time-to-effect: short-medium.
Reversibility: high.
Principal risk: identity correlation could itself reveal sensitive relationships unless access controls are strong.
Authority-to-authority forwarding
Where legal thresholds overlap and legislation permits, the first competent authority receiving a notification could transmit defined fields automatically to another authority, subject to confirmation by the reporting entity where necessary.
Germany’s DORA-to-BSI model demonstrates the practical feasibility of this principle. BSI archived NIS2 sector FAQ.
Expected effect: major reduction in duplicate filing.
Implementation burden: medium because legal transfer gateways and data mappings are required.
Time-to-effect: medium.
Reversibility: high.
Principal risk: the reporting organisation may incorrectly assume onward transmission discharged an obligation unless acknowledgements are explicit.
Federated European reporting gateway
A common front-end could authenticate the reporter, collect the shared factual core and then distribute separate legally compliant reports to the relevant CRA, NIS2, DORA and national endpoints.
Expected effect: closest practical approximation to “report once”.
Implementation burden: high.
Time-to-effect: medium-long.
Reversibility: medium.
Principal risk: cybersecurity concentration and complex access governance.
Full legal consolidation
Europe could theoretically attempt to create a single horizontal incident-reporting law superseding CRA, NIS2, DORA and related reporting obligations.
Expected effect: superficial reduction in legal multiplicity.
Implementation burden: extremely high.
Time-to-effect: long.
Reversibility: low.
Principal risk: loss of product, sector, financial and fundamental-rights distinctions that exist for substantive reasons.
The evidence therefore supports administrative integration much more strongly than full legal consolidation.
Data governments should publish to measure duplication
The present debate suffers from a lack of reliable public quantitative evidence concerning the true cost of overlapping reporting.
The Commission, ENISA and national authorities should eventually publish anonymised statistics capable of answering:
| Indicator | Decision value |
|---|---|
| Percentage of CRA reports linked to NIS2 incidents | Measures actual overlap |
| Percentage linked to GDPR breaches | Measures privacy intersection |
| Percentage linked to DORA incidents | Measures financial-sector intersection |
| Average number of authorities notified per qualifying incident | Direct duplication indicator |
| Median staff hours spent on regulatory reporting | Compliance-cost measure |
| Percentage of identical fields repeated across filings | Technical integration opportunity |
| Number of authority-to-authority forwarded reports | Measures interoperability |
| Duplicate reports avoided through national single-entry systems | Quantifies benefit |
| Percentage of filings containing inconsistent factual data | Measures fragmentation risk |
| Number of late reports attributable to multi-regime complexity | Measures regulatory cost |
| Number of incidents requiring reporting in ≥3 regimes | Identifies highest-burden cases |
| Average number of national jurisdictions involved | Cross-border complexity measure |
Without this evidence, policy debate risks relying excessively on anecdotal claims from regulators or industry.
The 2026–2028 period will determine whether Europe builds a regulatory system or a regulatory stack
The crucial issue is whether CRA implementation simply adds another layer above an already complex European cyber-regulatory landscape or becomes the catalyst for better integration.
Three developments should be monitored particularly closely.
The first is whether the Commission’s 2026 NIS2 simplification initiative develops into concrete mechanisms for cross-regime reporting interoperability rather than merely adjusting entity thresholds or definitions. European Commission — NIS2 Directive.
The second is whether ENISA’s SRP architecture develops reusable technical standards that can interact with national NIS2 portals and sectoral systems without converting ENISA into the universal supervisory authority.
The third is whether national models such as Germany’s BSI portal and regulator-to-regulator DORA forwarding demonstrate measurable reductions in duplicate reporting that can be replicated across the Union.
If these developments converge, the EU could move toward a federated reporting ecosystem in which the company provides a common factual core once and authorities exchange authorised information between themselves. If they do not, the CRA risks becoming another efficient portal inside an inefficient overall architecture.
Key judgments
The first judgment is that centralised CRA reporting does not amount to regulatory convergence, because CRA, NIS2, DORA and GDPR continue to apply different substantive tests to different regulated interests, and the same event can legitimately produce different notification outcomes under each framework.
The second judgment is that the greatest opportunity for simplification lies not in rewriting those legal tests but in eliminating repetitive transmission of identical technical facts. A common incident taxonomy, shared identifiers, pre-populated forms and regulator-to-regulator forwarding could remove significant administrative burden without altering supervisory competence.
The third judgment is that DORA already demonstrates a workable model of specialised regulation combined with reporting alignment, because the EU deliberately aligned much of its reporting timetable with NIS2 while preserving financial-sector supervision, and Germany has gone further by building practical information-forwarding arrangements between financial and cyber authorities.
The fourth judgment is that national implementation remains an important source of divergence. Italy has completed NIS2 transposition and concentrated major cyber functions around ACN; Germany brought its implementation law into force on 6 December 2025 and has developed a central BSI portal; France had still not notified complete NIS2 transposition by July 2026 and was referred by the Commission to the Court of Justice; the United Kingdom operates a separate PSTI product-security regime with different scope, obligations and enforcement mechanisms.
The fifth judgment is that UK experience provides a useful cautionary benchmark: OPSS found varying levels of non-compliance in 75% of 82 in-scope connected products assessed in 2024–2025, despite the UK regime containing only three principal product-security requirements at that stage. OPSS Delivery Report 2024–2025. The figure should not be extrapolated mechanically to the CRA population, but it demonstrates that enforcement and implementation capacity matter as much as statutory adoption.
The sixth judgment is that a universal European cyber-reporting portal containing complete CRA, NIS2, DORA and GDPR datasets would create excessive institutional and cybersecurity concentration risk. The more defensible architecture is federated interoperability: common data standards, controlled routing, explicit legal gateways, separate authority permissions and regulator-specific case management.
The seventh judgment is that corporate governance must consequently treat cyber reporting as a portfolio of legal obligations managed from one authoritative incident record, rather than allowing each regulatory department to build independent factual accounts of the same attack.
What would change the assessment
The assessment would change materially if the EU legislator creates an explicit cross-regime “once-only” reporting principle under which submission to one authorised gateway legally discharges specified notification obligations in other frameworks. No such general principle currently replaces the independent CRA, NIS2, DORA and GDPR tests.
The assessment would also change if ENISA’s SRP evolves into an interoperable gateway capable of authorised machine-to-machine routing toward national NIS2, financial-sector and data-protection systems, because the practical distinction between multiple reporting regimes and multiple manual submissions would then become substantially smaller.
France’s position should be reassessed immediately when complete NIS2 transposition is formally notified and accepted into the Commission’s implementation record, because the 8 July 2026 CJEU referral is a current legal-status fact rather than a permanent structural characteristic. European Commission — 8 July 2026 infringement decision.
The assessment would likewise need revision if the United Kingdom substantially expands the PSTI regime toward an EU-style mandatory exploited-vulnerability or incident-reporting architecture, because the present analysis rests on the significant structural difference between the UK’s baseline consumer-connectable-product requirements and the CRA’s lifecycle and incident-reporting system.
Open official record
The official record does not yet provide a Union-wide dataset showing how many CRA incidents simultaneously satisfy NIS2, DORA or GDPR thresholds, how many separate regulatory submissions companies make per underlying cyber event, how many staff hours those parallel processes consume, how frequently regulators forward notifications between themselves, how often one authority’s report is accepted as satisfying another regime, or how often inconsistent reporting timelines create late or contradictory filings.
No mature official evidence yet establishes whether the SRP is reducing total regulatory burden at enterprise level, because its success in centralising CRA reporting should not be confused with reduction of cross-regime duplication.
The critical measurement for the next phase should therefore be not simply the number of CRA reports processed successfully, but the number of redundant regulatory interactions eliminated without degrading the independent legal purposes of NIS2, DORA, GDPR or national cybersecurity law.
The strategic objective for Europe should consequently be understood with precision: not one cyber law, not one cyber regulator and not necessarily one central database, but one coherent information architecture capable of supporting several legitimate regulatory regimes without forcing companies to reconstruct the same incident repeatedly for every authority.
Regulatory Convergence Remains Incomplete Despite Centralised Reporting
ENISA’s Single Reporting Platform centralises CRA product-security reporting, but it does not create a unified European cyber-incident regime. CRA, NIS2, DORA and GDPR regulate different legal objects, different actors and different harms. The same technical event can therefore launch several legal clocks at once, involve different corporate entities and produce parallel filings to cyber, financial, product and data-protection authorities. The strategic objective is consequently not legal merger, but federated convergence: one authoritative factual record, multiple independent legal determinations and controlled routing toward the correct authority.
One cyber event can create several legally distinct reporting obligations
CRA, NIS2, DORA and GDPR can all be activated by the same underlying attack, but each asks a different legal question. Operational overlap therefore does not create legal interchangeability.
Core EU cyber-reporting architecture
| Regime | Regulated Object | Reporting Entity | Core Trigger | First Stage | Subsequent Reporting | Principal Recipient |
|---|---|---|---|---|---|---|
| CRA | Product with digital elements | Manufacturer | AEV or severe product-security incident | ≤24h from awareness | 72h notification + final-report timetable | Coordinator CSIRT + ENISA via SRP |
| NIS2 | Security of systems supporting regulated services | Essential / important entity | Significant impact on service provision | ≤24h | 72h notification + final ≤1 month | CSIRT / competent authority |
| DORA | ICT resilience of financial entity | Financial entity | Major ICT-related incident | ≤4h after major classification and ≤24h after awareness | Intermediate ≤72h after initial; final ≤1 month | Financial competent authority |
| GDPR | Personal data | Controller | Personal-data breach unless unlikely to create rights/freedoms risk | Where feasible ≤72h | Additional information can follow in phases | Data-protection supervisory authority |
| GDPR Processor Layer | Processing on behalf of controller | Processor | Awareness of personal-data breach | Without undue delay to controller | Controller decides supervisory notification | Controller |
Similar deadlines conceal different legal starting points
| Regime | Clock-Starting Event | Key Distinction |
|---|---|---|
| CRA | Manufacturer becomes aware of qualifying AEV / severe incident | Product-security classification required |
| NIS2 | Entity becomes aware of significant incident | Service-impact classification required |
| DORA | Awareness plus classification as major | Additional ≤4h rule after major classification |
| GDPR | Controller becomes aware of personal-data breach | Risk analysis determines whether notification exemption applies |
| UK PSTI | No equivalent CRA-style AEV clock | Focuses on baseline product-security requirements and vulnerability-reporting arrangements |
One compromised software update, four legal perspectives
| Factual Element | CRA | NIS2 | DORA | GDPR |
|---|---|---|---|---|
| Malicious code via software update | Potential severe product-security incident | Relevant if service impact significant | Relevant ICT incident | Relevant only if personal data affected |
| Vulnerability actively exploited | Direct trigger if statutory AEV test met | Relevant cause, not sufficient alone | Relevant to classification | Not reporting trigger by itself |
| Banking service unavailable | Indirect product consequence | Potential significant incident | Potential major ICT incident | Relevant if availability of personal data constitutes breach |
| Customer credentials exfiltrated | Product-security consequence | Potential material/non-material damage | ICT consequence | Personal-data breach |
| Manufacturer aware before bank | CRA clock can start first | Bank clock may not yet start | Bank clock may not yet start | Controller awareness governs GDPR clock |
| Bank aware before manufacturer | CRA manufacturer may not yet be aware | NIS2 clock can start | DORA clock can start | GDPR clock can start |
The reporting entity may differ across the same corporate group
Complementary frameworks, not duplicates
| Question | CRA | NIS2 |
|---|---|---|
| What is protected? | Security of products with digital elements | Continuity/security of regulated entities and services |
| Who reports? | Manufacturer | Essential or important entity |
| Active exploitation itself reportable? | YES, if AEV test met | Not automatically |
| Service disruption required? | No for AEV reporting | Significant service impact central |
| Product compromise without outage? | Can trigger | May not trigger |
| Outage without exploited product vulnerability? | Not necessarily | Can trigger |
Specialised supervision can coexist with aligned reporting architecture
| Feature | DORA | NIS2 |
|---|---|---|
| Sector | Financial services | Broad critical / important sectors |
| Outer initial deadline | ≤24h from awareness | ≤24h from awareness |
| Additional trigger | ≤4h from major classification | No equivalent |
| Intermediate stage | ≤72h after initial report | ≤72h from awareness |
| Final stage | ≤1 month after intermediate/latest update | ≤1 month after incident notification |
| Supervisory logic | Financial operational resilience | Cyber/service resilience |
The least substitutable reporting regime
The duplication problem is primarily a data-architecture problem
| Common Field | CRA | NIS2 | DORA | GDPR |
|---|---|---|---|---|
| Incident identifier | ✓ | ✓ | ✓ | ✓ |
| Detection timestamp | ✓ | ✓ | ✓ | ✓ |
| Awareness timestamp | ✓ | ✓ | ✓ | ✓ |
| Technical description | ✓ | ✓ | ✓ | ✓ |
| Product / version | CENTRAL | Sometimes | Sometimes | Sometimes |
| Service affected | Sometimes | CENTRAL | CENTRAL | Sometimes |
| Personal data affected | Sometimes | Sometimes | Sometimes | CENTRAL |
| Geographic impact | Routing-critical | Relevant | Relevant | Supervisory relevance |
| Mitigation measures | ✓ | ✓ | ✓ | ✓ |
“Report once, route many” is more realistic than one universal cyber notification
Stores neutral technical, chronological, entity and impact facts once.
Applies product-security trigger and generates SRP-ready fields.
Apply service, financial and data-protection legal tests independently.
Add jurisdiction-specific requirements without rewriting the shared factual core.
Sends only legally authorised fields to each competent authority.
Returns acknowledgements, information requests and update requirements into the common case record.
Italy, France, Germany and the United Kingdom
Institutional proximity
NIS2 was transposed through Legislative Decree No. 138/2024. ACN is the national single point of contact and CSIRT Italia operates inside the Agency. The Italian model demonstrates how institutional proximity can reduce friction without abolishing sectoral or data-protection supervision.
Portal-oriented convergence
Germany’s NIS2 implementation entered into force on 6 December 2025. The BSI Portal and existing MIP arrangements show that a valid submission does not need to be manually duplicated inside the same administrative ecosystem. DORA-to-BSI forwarding provides a further precedent.
Transposition lag
As of the Commission’s 8 July 2026 decision, France had not notified complete NIS2 transposition and was referred to the Court of Justice. ANSSI and CERT-FR remain central cyber institutions, but legal-operational maturity is uneven relative to the directly applicable CRA.
Regulatory divergence
The UK PSTI product-security regime has applied since 29 April 2024 and follows a different architecture from the CRA. UK manufacturers selling covered products into the EU can therefore face CRA duties while complying separately with UK product-security requirements enforced by OPSS.
Product-security law does not produce immediate market-wide compliance
Different legal conclusions, identical factual chronology
- Detection timestamp
- Awareness timestamp
- Incident start / end
- Systems and products involved
- Affected versions
- Root cause when known
- Indicators of compromise
- Geographic footprint
- Service downtime
- Personal data affected
- Remediation timeline
- CRA legal classification
- NIS2 significant-incident classification
- DORA major-incident classification
- GDPR rights-and-freedoms risk conclusion
- Regime-specific confidentiality designation
- Authority-specific mitigation or information request
Shared data structures are more urgent than a single reporting law
Administrative convergence must not become uncontrolled institutional centralisation
What a credible “report once” system would require
Administrative convergence versus institutional centralisation
| Reform Path | Feasibility | Benefit | Principal Downside |
|---|---|---|---|
| Common incident taxonomy | HIGH | Reduces repeated data preparation | Requires standards alignment |
| Shared incident identifier | HIGH | Improves regulator correlation | Governance rules needed |
| Authority-to-authority forwarding | HIGH-MEDIUM | Removes duplicate filing | Requires legal transfer basis |
| Pre-population across portals | MEDIUM-HIGH | Reduces manual burden | Strong access control required |
| Common technical gateway | MEDIUM | Closest to report-once model | Cybersecurity concentration risk |
| Universal EU cyber form | LOW-MEDIUM | Surface simplicity | Cannot capture distinct legal tests well |
| Universal reporting authority | LOW | Maximum centralisation | Major competence / governance problems |
| Full legal merger | VERY LOW | Theoretical simplification | Destroys distinct regulatory purposes |
One incident, one factual record, multiple legal determinations
Operational convergence is not moving at one speed
| Variable | Italy | France | Germany | United Kingdom |
|---|---|---|---|---|
| EU CRA | Directly applicable | Directly applicable | Directly applicable | Applies to covered products placed on EU market |
| NIS2 status | Transposed | Full transposition unnotified; CJEU referral July 2026 | In force from 6 Dec 2025 | Not applicable as EU law |
| Central cyber authority | ACN | ANSSI | BSI | NCSC cyber role; OPSS product enforcement |
| Product-security layer | CRA | CRA | CRA | PSTI |
| Portal convergence | Developing around ACN ecosystem | Affected by transposition delay | Strong BSI portal model | Separate sector/product frameworks |
| Principal risk | Multi-authority exchange | Legislative/transposition delay | Federal / sector interfaces | EU–UK divergence |
Where compliance breakdown is most likely to occur
Six definitive judgments
Centralised CRA reporting is not regulatory convergence. Different legal tests remain valid because the regimes protect different interests.
The major simplification opportunity lies in factual reuse. Common identifiers, shared incident records and pre-populated forms can remove repeated work without erasing legal differences.
DORA demonstrates the viability of specialised regulation with aligned reporting. Sector supervision can remain intact while information structures become interoperable.
National implementation remains a major source of operational divergence. Italy, France and Germany illustrate different institutional and legislative maturity levels.
UK evidence shows that statutory adoption does not equal compliance maturity. Enforcement capacity, guidance and market surveillance remain decisive.
Federated interoperability is more defensible than universal centralisation. Europe needs shared standards and controlled routing, not one undifferentiated repository containing every cyber, financial and privacy incident.
- How many CRA incidents also satisfy NIS2, DORA or GDPR thresholds.
- Average number of authorities notified per underlying incident.
- Median staff hours consumed by parallel regulatory reporting.
- Frequency of regulator-to-regulator forwarding.
- Number of duplicate reports avoided through national gateways.
- Rate of factual inconsistency across parallel filings.
- Number of late reports attributable to multi-regime complexity.
Europe does not need one cyber law, one cyber regulator or one undifferentiated database. The more defensible objective is a coherent information architecture capable of supporting several legitimate regulatory regimes: one factual core, independent legal tests, interoperable identifiers, secure authority-to-authority routing, strict purpose limitation and separate supervisory case management. If that architecture emerges, CRA implementation can become a catalyst for administrative convergence. If it does not, the SRP risks becoming another efficient portal inside an inefficient regulatory stack.