



Scope — This assessment examines Deutsche Bank’s Russia-to-Berlin technology transfer, the alleged assignment to a corporate banking platform identified as sDDA, and the reach of the bank’s public response, using the official record from 2011 through 18 November 2026 across Germany, Russia, the EU, the United Kingdom and the United States, with implications for Italy, France, Luxembourg and Switzerland.
Executive Summary / BLUF
The transfer to Berlin is confirmed. Whether the transferred staff could see live transactions remains unresolved. An ECB supervisory interview and a Deutsche Bank filing substantiate the transfer. The official records reviewed do not identify a specific sDDA assignment, its production responsibilities or the staff’s effective data permissions. bankingsupervision.europa.eu
On 17 November, Deutsche Bank said testing with a security firm found no indication that its current IT environment had been compromised or that account information, credentials or payment data had been accessed. The bank said its analysis was continuing and that it had informed relevant authorities, including the data protection authority. db.com
The bank’s statement addresses evidence of an incident. Whether engineers had standing or temporary permission to view live transaction fields is a separate, unanswered question. Back-end engineering can be performed with synthetic data and no production access. It can also include tightly controlled production support. Effective permissions and audit records would establish which arrangement applied. eur-lex.europa.eu
The Russian technology centre had approximately 1,500 employees on 31 January 2022. That figure describes the source centre’s workforce. The Berlin transfer count and any platform-specific headcount remain unverified in the official record. annualreport.deutsche-bank.com
The public record supports a precise request for a written, system-specific account of access. It currently supplies no substantiated basis to allege transaction exposure, unauthorised access, sanctions evasion or state-directed activity by the Berlin team.
Deutsche Bank’s Berlin Test Is What Its Staff Could See
Deutsche Bank’s statement of 17 November 2026 addresses what its forensic tests detected. The question raised by the transfer of technology staff from Russia to Berlin concerns what those employees were permitted to see. The bank says testing with a security firm found no indication that its current IT environment had been compromised or that account information, credentials or payment data had been accessed. That is a substantive finding within the scope of the tests. The bank has yet to disclose whether the review covered the transferred staff’s permissions on sDDA, a corporate banking system that holds accounts and positions. The distinction matters to companies relying on Deutsche Bank for cash management, to supervisors assessing the bank’s controls, and to a management team that says it invested €7 billion in those controls between 2019 and 2025.
The account core makes permissions the decisive fact
The European Central Bank’s banking supervisors and Deutsche Bank’s 2022 filings establish that the bank moved technology resources from Russia to Berlin to maintain services. The Russian technology centre had approximately 1,500 employees on 31 January 2022. The number who moved to Berlin, and how many subsequently worked on sDDA, remain unverified. Archived Berlin recruitment notices attributed to the bank advertise back-end engineering and production-facing responsibilities for sDDA and related applications. They show what the bank sought to staff in Berlin. They give no basis for assigning those roles to particular transferees.
Deutsche Bank’s July 2020 description of its Australian corporate banking architecture explains why the distinction matters. It identifies sDDA as the component holding accounts and positions, alongside a separate payment engine and payment data store. The billing platform drew data from both. An engineer can deploy an approved release or monitor a service while seeing only operational metrics. A support engineer with temporary read permission could, depending on the role, see an identifiable debit or credit without access to the full payment instruction or authority to release it. The published Australian example establishes the distinction between the account and payment functions. The evidence that would settle the Berlin question is the dated record of what the relevant roles could read, including during authorised support and testing.
The Epstein figures expose the cost of delayed scrutiny
The November 2026 investigation reports US$581.9 million across approximately 3,000 transactions involving Jeffrey Epstein or his companies from October 2013 through May 2019, drawing on an internal bank summary of 21 suspicious activity reports. That is the most precisely documented basis in the reporting for the shorthand “about US$600 million”. A consortium overview uses “more than US$600 million” without publishing a reconciliation. Separately, Senate Finance Committee investigative staff documented more than US$250 million in retrospectively flagged wires in the filings they examined, including 1,140 wires worth US$147 million in a single 2019 filing. The amounts describe different documentary populations whose overlap is unresolved. Suspicious activity reporting identifies transactions warranting scrutiny. The dollar value of those transactions does not establish how much was criminal proceeds.
The New York State Department of Financial Services identified a more consequential failure in its 2020 consent order. Deutsche Bank took Epstein on in August 2013 after an internal memorandum had documented his prior plea and sentence. In 2015, a reputational-risk committee allowed the relationship to continue subject to conditions that did not reach all responsible relationship and monitoring staff as intended. By March 2017, a monitoring employee could treat certain payments as ordinary because similar activity was already familiar for that client. A history that called for enhanced scrutiny had become the basis for accepting the transactions as routine. The regulator imposed US$150 million under a single order that also covered separate correspondent relationships involving Danske Bank Estonia and FBME. The US$75 million civil class settlement was a different proceeding. The governance finding lies in the failure to carry a committee decision into daily monitoring.
The Trump records test three different controls
The New York civil record documents Deutsche Bank’s lending to entities associated with Donald Trump, the U.S. president, including financing connected with Doral, Trump Chicago and the Old Post Office in Washington. It describes the weight the bank gave to Trump’s personal guarantee and financial statements, as well as adjustments its credit staff made to collateral values. The trial court’s US$168,040,168 disgorgement component represented estimated interest savings on four loans considered in the case. The Appellate Division vacated the disgorgement awards in August 2025. The U.S. Supreme Court’s July 2020 decision in Trump v. Mazars addressed another question: the constitutional limits of congressional subpoenas, including one sent to Deutsche Bank in April 2019. Neither proceeding decided the allegations about how the bank handled a confidential disclosure or reviewed a particular payment.
Those allegations turn on two different records. ZDF reports that on 30 March 2017 a bank employee mistakenly sent an external accountant financial material covering 1,586 accounts, including three attributed to Trump. The documents reviewed by ZDF indicated that U.S. authorities were informed and Trump was not. The transmission record, the recipient’s actual access and the bank’s notification decision are the relevant evidence. Consortium reporters separately matched an entry in a May 2020 internal financial-crime memorandum to a US$141,261.82 transfer on 28 April 2015 from Faberlex to THC Baku Services LLC, a Trump-owned company. That reported match warrants scrutiny of the payment and the bank’s disposition of the review. It establishes neither the payment’s illegality nor Trump’s personal knowledge of its origin. The distinction between a documented lending relationship, a reported disclosure and an internally reviewed transfer is what makes the Trump material probative.
Russian client concentration put revenue behind the risk decision
The reported November 2020 Russia Strategy Review presents the sharpest commercial tension. According to the published account, 17 of 160 major Russian clients appeared in the U.S. Treasury’s 2018 report under Section 241 of the Countering America’s Adversaries Through Sanctions Act. Those 17 reportedly accounted for 47% of the reviewed Russian client portfolio’s revenue in 2020. Treasury’s Office of Foreign Assets Control made clear that inclusion in the Section 241 report did not impose sanctions. The figures therefore show, if the reported review is accurate, that portfolio revenue was concentrated among a small number of politically exposed relationships. Any claim that banking activity violated sanctions requires a separate check of the client or beneficial owner, the operative designation, the transaction date and the applicable jurisdiction. The reported concentration of wealthy Russian clients in Switzerland and Luxembourg raises a further question about where records were held and what the bank could disclose to U.S. investigators. Deutsche Bank reportedly explained the concentration as part of its wealth-management operating model. The booking records and the bank’s actual replies to authorities would allow that explanation to be tested.
The 2010 hiring of Alexey Storchak illustrates the danger of reading more into those records than they say. Reporting on Deutsche Bank’s internal hiring inquiry identified him as a former Credit Suisse employee and the son of Sergei Storchak, then a Russian deputy finance minister. Separately, Le Monde reported that an unnamed banker hired in June 2010 communicated Deutsche Bank’s selection for a €2 billion Eurobond issue before its public announcement. The public material reviewed does not identify Storchak as the sender. The Securities and Exchange Commission’s August 2019 resolution, which totalled US$16,178,850 including disgorgement and interest, covered corporate referral-hiring controls in Russia and Asia-Pacific. The SEC’s €2 billion Eurobond example concerns an anonymised deputy minister’s daughter and a request for proposals. A matching denomination cannot identify the banker or equate a request for proposals with an announcement of selection.
Moscow put a price on the limits of a wind-down
Deutsche Bank announced in March 2022 that it would wind down remaining business in Russia and enter into no new business there. The Bank of Russia still listed its Moscow banking subsidiary as active on 18 November 2026. The registry entry establishes legal status and leaves current business volumes unanswered. The RusChemAlliance litigation gives a clearer measure of the exposure that remained. An English court granted an anti-suit injunction in 2023 under a guarantee governed by English law that provided for Paris arbitration. A Russian court nevertheless awarded €238,126,196.10 in principal in May 2024. Deutsche Bank says €244 million, including interest, was enforced that November against assets it maintained in Russia. It subsequently derecognised an asset representing expected reimbursement under an indemnity, which it says it continues to pursue. The case illustrates the limits of a commercial exit when legacy obligations and assets remain within another court’s reach. It also explains why a bank can reduce new business while its exposure to local enforcement remains material.
Over the next 12–24 months, the cost of ambiguity falls on clients and the bank
The Digital Operational Resilience Act, applicable since 17 January 2025, gives EU supervisors a basis to examine access governance, segregation of duties and logging across the entities that support a shared banking service. The adequacy of safeguards is also the subject of an inquiry that Alexander Roßnagel, the Hessian data protection commissioner, was reported on 18 November 2026 to be conducting. The public record reviewed through that date contains no conclusion from the inquiry about the Berlin team. Nor does it identify the Berlin systems, personnel or audit period covered by the bank’s forensic statement. A review of whether safeguards were adequate and a forensic test for evidence of compromise can reach findings on different questions, even when both start from the same disclosure.
Over the next 12–24 months, the cost will depend on whether Deutsche Bank supplements its 17 November statement with evidence specific to Berlin. A dated account of standing, temporary and emergency permissions, paired with an audit summary that states what activity can be reconstructed, would allow supervisors and corporate treasurers to judge the assurance on its merits. If the bank leaves the statement at group level, clients that rely on its cash-management services will bear the cost of additional due diligence, supervisors will have to establish the facts through their own inquiries, and Deutsche Bank will have to defend its controls without a public answer to the simplest question in the case.
Could the transferred sDDA staff see identifiable transactions, and what record proves the answer?
Navigational Index
| Thematic pillar | Chapter allocation |
|---|---|
| I. The transfer and the technology | Chapter 1. Moscow and Saint Petersburg to Berlin, staffing, entities and the 2022–2026 chronology. Chapter 2. Corporate banking technology, the alleged sDDA assignment and the evidence needed to establish live access. |
| II. Enforcement, sanctions and jurisdiction | Chapter 3. Russia-linked mirror trading, referral hiring, U.S. and UK enforcement, and remediation. Chapter 4. Russia sanctions, the residual Moscow entity and the RusChemAlliance dispute. Chapter 5. Digital resilience, bank supervision and data protection in Germany, Italy, France, the United Kingdom and the EU. |
| III. Verification and institutional decisions | Chapter 6. Deutsche Bank’s assertions, the scope of the forensic investigations, and the documentation that could resolve the dispute. Chapter 7. Evidence thresholds, institutional options and final net assessment. |
Master Abstract
The 2022 transfer is documented by both the bank and its supervisor
Deutsche Bank’s communications distinguish three developments that occurred within months of Russia’s full-scale invasion of Ukraine. On 3 March 2022, the bank said it housed neither code nor data at its Russian technology centre. On 11 March, it announced a wind-down of its remaining Russian business while helping non-Russian multinational clients reduce their local operations, and said it would enter into no new business in Russia. On 7 June, it announced a Berlin technology centre primarily developing applications and integrating technologies for the Corporate Bank and Investment Bank. Its interim report as of 30 June, filed with the SEC, separately recorded a transfer of resources from the Russian technology centre to Berlin and accrued committed relocation costs. The report described the Russian unit’s work as technology development and change. In November 2022, an ECB Banking Supervision interview independently described the Saint Petersburg centre as providing services within the group and confirmed that the bank moved staff from that centre to Berlin to maintain service continuity. Taken together, the records establish a transfer of people and technology work. The statement about where data and code were housed addresses physical or logical hosting in Russia. Remote visibility and later Berlin permissions require separate evidence. Deutsche Bank statements on war in Ukraine — Deutsche Bank — Mar 2022 · Statement on business activities in Russia — Deutsche Bank — Mar 2022 · Deutsche Bank eröffnet neues Technologiezentrum in Berlin — Deutsche Bank — Jun 2022 · Interim Report as of June 30, 2022, pp. 52–53 — Deutsche Bank, filed with the SEC — Jul 2022 · Interview at the DNB Banking Seminar — ECB Banking Supervision — Nov 2022. db.com
“Back end” does not define a person’s access
Deutsche Bank publicly offers corporate clients real-time debit and credit notifications at transaction level, optional updated balances, and intraday and end-of-day account statements. It also describes virtual accounts that support payment reconciliation and liquidity pooling. These disclosures demonstrate that the bank’s corporate cash-management services handle transaction-level information. The public product descriptions do not identify sDDA as the system providing each service or establish which personnel could access the underlying data. The technical question turns on four distinct facts: which application the personnel supported, which environments they worked in, which data fields their effective permissions exposed, and whether they exercised those permissions. An engineer can develop a service with synthetic records, view production service-health metrics without seeing customer records, or have an approved support role that exposes identifiable data for a limited time. A separate question concerns power to approve or release payments. A person can have read-only visibility into a transaction without having authority to initiate, amend or release it. Each proposition requires its own evidence. API Connectivity — Deutsche Bank Corporate Bank — undated · Virtual Accounts — Deutsche Bank Corporate Bank — undated · Commission Delegated Regulation (EU) 2024/1774, Arts. 12, 20–21 — European Commission — Mar 2024. Corporates and Institutions
The November statement answers a narrower question than the access allegation
The bank’s German statement says testing conducted with a security firm found no indications of compromise of the current IT environment or access to account information, credentials or payment data. It describes the documents behind the reporting as purported internal materials from several years earlier, acknowledges that they include confidential information, and says the bank contacted clients or staff where it identified potentially relevant effects. It does not publish the test dates, system inventory, identities or roles examined, data categories mapped, evidence-retention period, or security firm’s report. Consequently, the public statement cannot establish whether the tests assessed the effective permissions of the transferred staff, whether historical access records were available, or whether the review examined authorised support access as well as potential unauthorised activity. The stated €7 billion in direct control investment from 2019 to 2025 is a group-level figure reported by the bank. Its evidentiary value for Berlin depends on whether a specific control can be shown to have operated on the relevant systems at the relevant time. Stellungnahme der Deutschen Bank zu aktuellen Medienberichten — Deutsche Bank — Nov 2026. db.com
Key Evidence Table
Financial figures are nominal in the original currency. Dates refer to the event or measurement unless the row identifies a publication date. The FCA and NYDFS reviewed overlapping historical trading activity, so their transaction estimates are not additive.
| Indicator | Value/status | Reference date | Definition/scope | Issuer | Exact source |
|---|---|---|---|---|---|
| Russian technology centre workforce | Approximately 1,500 employees, around 5% of the group’s internal and external technology workforce | 31 Jan 2022 | Source-centre employment. A relocation count, citizenship breakdown and sDDA roster remain unverified. | Deutsche Bank | Second Supplement Dated 23 September 2022, Russia risk discussion — Deutsche Bank — Sep 2022. annualreport.deutsche-bank.com |
| Transfer of technology resources | Confirmed by the filing and ECB account | By 30 Jun 2022. ECB account published Nov 2022. | Resources transferred from the Russian technology centre to Berlin. The ECB specifically identified Saint Petersburg. The filing recorded accrued relocation costs and task reassignment to technology centres worldwide. | Deutsche Bank and ECB Banking Supervision | Interim Report as of June 30, 2022, pp. 52–53 — Deutsche Bank, filed with the SEC — Jul 2022 · Interview at the DNB Banking Seminar — ECB Banking Supervision — Nov 2022. sec.gov |
| 2022 loan exposure to Russia | €1.3bn gross, €0.5bn net, €0.4bn additional undrawn commitments | 30 Jun 2022 | Group loan exposure. Net exposure reflects risk mitigants. Undrawn commitments are a separately reported category. These figures measure financial exposure, not transaction flow or technology access. | Deutsche Bank | Interim Report as of June 30, 2022, Russia credit risk — Deutsche Bank, filed with the SEC — Jul 2022. sec.gov |
| Moscow banking entity | Active entry for OOO Deutsche Bank, registration No. 3328, OGRN 1027739369041 | 18 Nov 2026, 00:00 Moscow time | Russian register status of the banking subsidiary. Its listing leaves the status of the separately identified technology company and the scale of current banking activity open. | Bank of Russia | List of Credit Institutions Registered in the Russian Federation — Bank of Russia — Nov 2026 · OOO Deutsche Bank — Bank of Russia — current register entry. Банк России |
| UK mirror-trading enforcement | £163,076,224 penalty. More than 2,400 matched trade pairs and US$6bn transferred through them. US$3.8bn in further suspicious one-sided trades. | Failings during 2012–2015. Final notice 30 Jan 2017. | FCA’s approximately US$10bn estimate assumes most or all of the one-sided trades formed part of additional mirror trades. The FCA found serious AML failings, described the transfers as highly suggestive of financial crime, and reported no evidence that senior management or UK employees knew of or participated in the suspicious trading. | UK Financial Conduct Authority | Final Notice to Deutsche Bank AG, §§2.7–2.18 and 4.16–4.43 — FCA — Jan 2017. fca.org.uk |
| New York mirror-trading enforcement | US$425m penalty and independent monitor | 30 Jan 2017 | NYDFS documented extensive AML failures involving operations in Moscow, London and New York and adopted its own findings in a consent order. | New York State Department of Financial Services | Consent Order, Deutsche Bank AG and Deutsche Bank AG New York Branch — NYDFS — Jan 2017. dfs.ny.gov |
| Russia and Asia-Pacific referral hiring | US$16,178,850 total, calculated from US$10,785,900 disgorgement, US$2,392,950 prejudgment interest and US$3m civil penalty | Russian conduct dated 2009–2012. Order 22 Aug 2019. | The SEC found books-and-records and internal-accounting-controls violations. The bank settled without admitting or denying the findings. The regulator anonymised individual hires. The total covers the order’s combined scope. | U.S. Securities and Exchange Commission | In the Matter of Deutsche Bank AG, Exchange Act Release No. 86740, file 3-19373 — SEC — Aug 2019. sec.gov |
| U.S. criminal resolution | More than US$130m under a deferred prosecution agreement | 8 Jan 2021 | DOJ resolution covering foreign bribery and commodities fraud. This is a distinct case. The public agreement supplies no finding about the later Berlin team or its permissions. | U.S. Department of Justice | Deutsche Bank Agrees to Pay Over $130 Million to Resolve Foreign Corrupt Practices Act and Fraud Case — DOJ — Jan 2021. United States Department of Justice |
| U.S. remediation enforcement | US$186m penalty and consent order. An earlier order was later terminated. | 19 Jul 2023. Earlier order terminated 13 Aug 2026. | The 2023 action concerns insufficient progress in U.S. sanctions and AML remediation, including transaction data, monitoring and filtering. The August 2026 termination expressly identifies the 20 April 2017 order. | Federal Reserve Board | Consent Order, Deutsche Bank — Federal Reserve Board — Jul 2023 · Announcement of Termination of Enforcement Action — Federal Reserve Board — Aug 2026. federalreserve.gov |
| RusChemAlliance guarantee dispute | Approximately €238m plus interest claimed. €244m including interest enforced against assets in Russia, per the bank. €240m was the threatened penalty for violating a separate anti-suit order. | Guarantee issued 2021. Enforcement Nov 2024. Disclosure 5 Nov 2026. | The bank says it refused payment because of EU sanctions, the Russian court granted the claim, and the bank continues to pursue indemnification. The €260m initial provision was a separate accounting amount. | Deutsche Bank, securities disclosure | Global Supplement, “RusChemAlliance Litigation” — Deutsche Bank — Nov 2026. deutsche-bank.it |
| November 2026 data-access response | No indication found, according to bank testing. Analysis ongoing. €7bn in direct control investment reported for 2019–2025. | 17 Nov 2026 | Public group statement. It gives no system-specific finding on sDDA or the Berlin cohort’s entitlements. No public determination by a competent authority resolving those questions was identified by the cut-off. | Deutsche Bank | Stellungnahme der Deutschen Bank zu aktuellen Medienberichten — Deutsche Bank — Nov 2026. db.com |
What the historical record establishes about the broader Russia allegations
The mirror-trading findings demonstrate why this case warrants close examination of cross-border controls. The FCA reconstructed an operation in which Moscow personnel executed orders on both sides of paired trades, with the London side booked remotely. NYDFS independently documented weaknesses in escalation and oversight across the relevant entities. In the referral-hiring case, the SEC described Russian government officials’ requests for employment of relatives and recorded a case involving a Russian deputy finance minister’s relative and a €2 billion Eurobond request for proposals. The order anonymises that relative. It also establishes the size of the proposed issue as part of the chronology, rather than bank revenue or an illicit payment. In a further case, NYDFS imposed a US$150 million penalty in 2020 covering the Epstein relationship and separate correspondent-banking relationships with Danske Bank Estonia and FBME. That is a combined enforcement amount. Each record establishes a specific historical matter, with its own dates, entities and findings. None puts the Berlin cohort in those transactions. Final Notice to Deutsche Bank AG — FCA — Jan 2017 · Consent Order, Deutsche Bank AG and Deutsche Bank AG New York Branch — NYDFS — Jan 2017 · In the Matter of Deutsche Bank AG, Exchange Act Release No. 86740 — SEC — Aug 2019 · Consent Order, Deutsche Bank — NYDFS — Jul 2020. fca.org.uk
The allegation that wealthy Russian clients were moved into Swiss or Luxembourg booking entities, including clients allegedly subject to U.S. restrictions, remains unresolved at transaction level. No official record reviewed establishes the asserted client list, the actual transfers, or the legal rationale for each booking decision. A defensible finding would require the booking entity, beneficial owner and controlling persons, designation and effective date, transaction date, jurisdictional nexus and any applicable licence or exemption. Oleg Deripaska’s case illustrates the distinction. OFAC designated him in April 2018. In January 2019, it delisted En+, Rusal and EuroSibEnergo while retaining its sanctions on Deripaska. DOJ subsequently announced a 2022 indictment alleging sanctions evasion. Those records establish the official actions against the relevant person and entities. Proof about a particular bank transaction would require a further evidentiary link. Treasury Designates Russian Oligarchs, Officials, and Entities in Response to Worldwide Malign Activity — U.S. Treasury — Apr 2018 · OFAC Delists En+, Rusal, and EuroSibEnergo — U.S. Treasury — Jan 2019 · Russian Oligarch Oleg Vladimirovich Deripaska and Associates Indicted for Sanctions Evasion and Obstruction of Justice — DOJ — Sep 2022. U.S. Department of the Treasury
Where authority sits in Europe
| Jurisdiction | Material relevance to this case |
|---|---|
| Germany | Berlin is the documented receiving location. Deutsche Bank AG is identified as a significant institution in the ECB’s supervised-entities list. The material supervisory questions are who owned the application, which production functions were supported from Germany, and what the permissions and audit evidence show. The Deutsche Bundesbank also publishes the German financial-sanctions framework for Russia and Ukraine. List of Supervised Entities, cut-off 1 September 2026 — ECB Banking Supervision — Oct 2026 · Russland / Ukraine — Deutsche Bundesbank — current guidance. Cut-off date 1 September 2026 |
| Italy | Banca d’Italia’s published DORA framework covers major ICT incidents and relevant operational or security incidents affecting payments for entities within its remit. Italian relevance would depend on an affected entity or payment service, its reliance on the shared application, and the relevant reporting threshold. The official records reviewed do not identify such an impact in Italy. Comunicazione di gravi incidenti ICT e delle minacce informatiche significative — Banca d’Italia — current guidance. bancaditalia.it |
| France | The ACPR sets out reporting for major ICT incidents and the submission of registers of ICT service arrangements for entities within scope. A French case would turn on the affected regulated entity or service, its dependency on the system and any actual data or service impact. The official records reviewed do not identify such an impact in France. Guide Formalités, reportings et notifications – domaine bancaire et des paiements — ACPR — current guidance. acpr.banque-france.fr |
| United Kingdom | London was a documented booking location in the historical mirror-trading case. A present UK question would require a UK-regulated business service, entity or sanctions nexus. The FCA’s operational resilience framework and OFSI’s Russia financial-sanctions guidance provide separate bases for assessment. Final Notice to Deutsche Bank AG — FCA — Jan 2017 · PS21/3 Building Operational Resilience — FCA — Mar 2021 · Financial Sanctions Guidance for Russia — HM Treasury/OFSI — current guidance. fca.org.uk |
| European Union | DORA has applied since 17 January 2025. It addresses ICT governance, access controls, incident classification and reporting. Article 21 of the delegated technical standard specifies need-to-know, least privilege, separation of duties and controls over privileged and emergency access. GDPR Articles 4(12), 32 and 33 separately govern personal-data breaches, security and notification. The bank’s statement that it informed authorities as a precaution does not establish either a formal DORA incident classification or a GDPR breach determination. The Council extended sectoral Russia sanctions until 31 July 2027, a separate legal inquiry from the Berlin access question. Regulation (EU) 2022/2554 — European Parliament and Council — Dec 2022 · Commission Delegated Regulation (EU) 2024/1774 — European Commission — Mar 2024 · Regulation (EU) 2016/679 — European Parliament and Council — Apr 2016 · Council Extends Economic Sanctions for Another Year — Council of the EU — Jun 2026. eur-lex.europa.eu |
| Luxembourg and Switzerland | The booking allegations would engage separate authorities and legal frameworks. Luxembourg’s CSSF publishes guidance on international financial sanctions within the EU regime. Switzerland’s SECO publishes the Swiss measures relating to Ukraine. Each allegation requires the account or asset, booking entity, date and applicable restrictions in that jurisdiction. Sanctions financières internationales — CSSF — current guidance · Mesures en lien avec la situation en Ukraine — SECO — current guidance. CSSF |
Competing Explanations or Pathways
The public evidence substantiates application development as a function of the Berlin centre. It is too coarse to rank the possible access arrangements for the alleged sDDA team. Three patterns illustrate the difference that the missing evidence would make.
| Access arrangement | Evidence that would support it | Evidence that would weaken it |
|---|---|---|
| Development without live transaction visibility | Synthetic or irreversibly masked test data, role records excluding production access, and an audit covering any exceptions during the relevant period. | Read permission for an identifiable transaction store, production support records containing customer data, or approved temporary access that exposed live fields. |
| Back-end support with restricted operational visibility | Records showing access solely to service health, processing status or approved non-identifying operational metadata. | A link available to the same role between operational records and identifiable customers, accounts, amounts or counterparties. |
| Back-end support with authorised live visibility | A dated entitlement or approved temporary role permitting named transaction fields to be viewed. Logs would establish whether staff used it. | Evidence that effective rights excluded transaction fields across the relevant production and support environments, with sufficient coverage to test exceptions. |
A confirmed entitlement would establish capability. A corresponding audit event would establish use within the event’s documented scope. Evidence that the use exceeded authorisation, or that information was disclosed to an unauthorised recipient, would raise a separate incident question. The published testing statement does not identify which of these propositions the bank tested. Commission Delegated Regulation (EU) 2024/1774, Arts. 12 and 21 — European Commission — Mar 2024 · Stellungnahme der Deutschen Bank zu aktuellen Medienberichten — Deutsche Bank — Nov 2026. eur-lex.europa.eu
Principal Gaps and Watch Indicators
| Open question | Record that could resolve it | Effect on the assessment |
|---|---|---|
| Was the relocated cohort assigned to sDDA, and in what capacity? | A dated application register, ownership and support matrix, and aggregate staffing confirmation identifying the employing entity, start dates and responsibilities. Individual names are unnecessary. | Would establish whether the allegation concerns a defined application and team. A title, reporting line or location alone cannot establish data visibility. |
| Could any member of that cohort view identifiable transaction records after relocation? | A signed response from the application owner and control function giving the relevant dates, environment and data categories, supported by historical role attestations covering standing, temporary and emergency access. | An explicit entitlement would substantiate the narrow capability claim. An evidenced absence of entitlement across the defined scope would support the bank’s explanation. |
| Did any member of the cohort actually view those records? | An audit summary stating the period covered, what activity was logged, the completeness and retention of those logs, and whether the review tested authorised access alongside potential unauthorised access. | A recorded read and a dated entitlement would answer different questions. Incomplete logging would limit the force of a negative result. |
| Did the November testing cover sDDA and Berlin? | A publishable scope statement from the bank or security firm covering dates, environments, assessed data classes and exceptions, or a competent authority’s public finding. | An explicit scope match would make the November result probative for this dispute. A review confined to present compromise would leave historical role permissions unresolved. |
| Were any Russia-linked client transfers or sanctions breaches formally established? | A competent authority’s order, court filing or authenticated transaction record establishing the specific booking entity, beneficial ownership, date, legal nexus and applicable restriction. | Would allow a documented sanctions analysis for each transaction. A client relationship or a designation alone leaves that analysis incomplete. |
The decisive written question is narrow enough to answer without disclosing customer data or security-sensitive architecture: “At any point after the transfer to Berlin, did any member of the transferred cohort working on sDDA have standing, temporary or emergency permission to view identifiable production account or payment-transaction data, including through support systems? If so, which categories of data could be viewed, during what period, and did the November review test whether those permissions were used?”
Pending a documented answer, the defensible publication position is that the transfer is confirmed, the bank reports finding no indication of compromise or access in its testing, and the effective data permissions of the Berlin cohort remain unverified.
Deutsche Bank Berlin · What the record can prove
Public record through 18 November 2026. Read left to right or in list order. The sequence shows the evidence needed to reach a finding about access. It does not depict the bank’s system architecture.
1. Transfer
The ECB described staff moving from the Saint Petersburg IT centre to Berlin. A June 2022 bank filing also documents a transfer from the Russian technology centre. ECB interview2. Assignment
The bank announced development work for the Corporate and Investment Banks. A dated application ownership and staffing record would establish the alleged sDDA assignment. Berlin announcement3. Permission
Effective entitlements and data classifications would establish who could see live account or payment records, including under approved temporary access. EU access-control standard, Art. 214. Use
Retained logs and an audit of coverage would establish whether access occurred within a defined period. The bank reports finding no indication of access in its tests. Bank statement, 17 November 20265. Incident
An incident determination needs dated evidence of an event and its effects on confidentiality, integrity, availability or authenticity, assessed against the applicable rule. DORA, Arts. 3 and 17–19
Published evidence and numerical scope
| Measure | Published value and date | Scope and source |
|---|---|---|
| Russian technology centre staff | About 1,500 employees, 31 January 2022 | Source-centre workforce. Berlin transfer count unavailable in this record. Deutsche Bank registration supplement, p. 49 |
| Transfer and relocation costs | Transfer recorded by 30 June 2022 | Bank reports a transfer of resources and accrual of committed relocation costs. No team entitlement information. Deutsche Bank interim report, pp. 52–53 |
| Control investment | €7 billion, 2019–2025 | Bank-reported direct investment in its control environment. No application-level breakdown. Deutsche Bank statement, 17 November 2026 |
| Historical mirror-trading penalties | £163,076,224 and US$425 million, January 2017 | Separate FCA and NYDFS actions on overlapping historical activity. FCA Final Notice · NYDFS Consent Order |
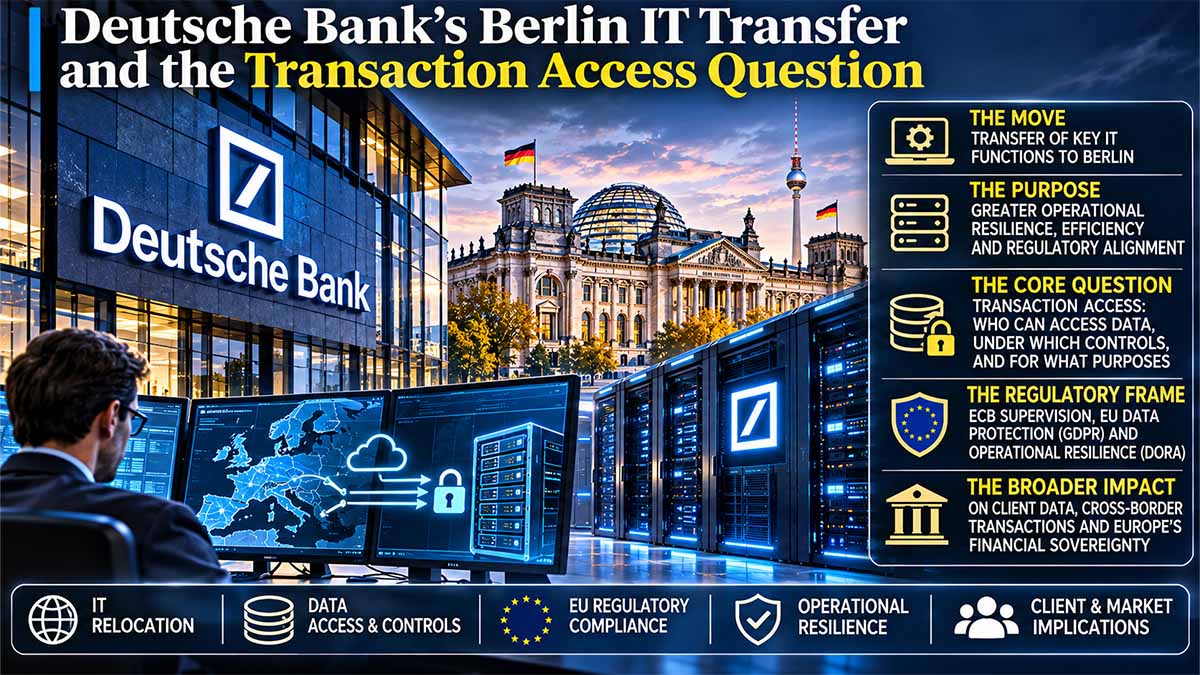
Deutsche Bank’s Berlin IT Transfer and the Transaction Access Question
Public record through 18 November 2026. The technology transfer to Berlin is documented. The specific sDDA assignment and the transferred staff’s permissions to view identifiable live transactions remain unverified. Deutsche Bank says testing with a security firm found no indication of compromise of its current IT environment or access to account information, credentials or payment data. The bank said its analysis was continuing.
| Measure | 31 December 2021 | 30 June 2022 |
|---|---|---|
| Gross loans | 1.4 | 1.3 |
| Net loans | 0.6 | 0.5 |
| Additional undrawn commitments | 1.0 | 0.4 |
These are financial exposures. The figures do not measure transaction volume or staff access.
Deutsche Bank interim report, filed with the SEC · ECB Banking Supervision interview · Deutsche Bank statement, 17 November 2026
Pillar I — Deutsche Bank’s Berlin Transfer, sDDA and Access to Live Transactions
Assessment date: 18 November 2026
Verdict. The back-end explanation is credible as a description of engineering work. The claim that the transferred staff could never see identifiable live transactions remains unverified. Deutsche Bank’s own technical publication identifies sDDA as a core component that holds accounts and positions. It identifies a separate payment engine and payment data store in the architecture it describes. Archived Berlin recruitment notices attributed to Deutsche Bank name sDDA and describe back-end development, production release management and production-facing engineering. Those notices materially strengthen the connection between sDDA and Berlin. They do not establish which employees transferred from Russia joined the team or which fields any of them could view. The bank’s public statement of 17 November reports that its tests found no indication of compromise of the current IT environment or access to account information, credentials or payment data. The statement contains no team-specific finding about ordinary, temporary or emergency permissions. The bank’s explanation could be accurate for the personnel in question. A job description and a forensic statement about what testing found are insufficient to verify it. Tomorrow’s Technology Today — Deutsche Bank, July 2020 · Lead Java/Kotlin Developer, sDDA — archived recruitment notice · IT Application Owner / Release Manager, sDDA Data — archived recruitment notice · Public Statement of 17 November 2026 — Deutsche Bank. Deutsche Bank
Chapter 1 — Moscow and Saint Petersburg to Berlin
The transfer moved people and technology work. Its public record does not identify individual system assignments.
The June and September 2022 filings are more informative together than the Berlin launch announcement alone. On 7 June, Deutsche Bank announced a centre led by Gerrit Einhoff, then CIO for the Corporate Bank and Investment Bank in Germany, with a remit centred on application development and technology integration. In its June interim report, the bank recorded that resources had already transferred to Berlin and that it had accrued committed relocation costs. By September, it reported that the Berlin centre had been established, explicitly identified local hiring as part of its growth, and continued to describe the Russian technology unit’s work as development and change for the Corporate Bank and Investment Bank, with tasks also being reassigned to technology centres elsewhere. These statements document three movements with different evidentiary implications: people transferring to Berlin, tasks being redistributed across the group, and new people being hired in Berlin. Interviewed in November 2022, ECB Banking Supervision separately described Saint Petersburg as the site of an important intragroup IT centre and said staff were moved to Berlin to preserve service continuity. That is independent institutional corroboration for the transfer from Saint Petersburg. Neither the ECB account nor the filings reviewed provide a city-by-city roster, a department-by-department allocation or the proportion of any Berlin team made up of transferred employees. Berlin Technology Centre Announcement — Deutsche Bank, June 2022 · June 2022 Interim Report — Deutsche Bank, filed with the SEC · September 2022 Earnings Report — Deutsche Bank, filed with the SEC · Interview at the DNB Banking Seminar — ECB Banking Supervision, November 2022. db.com
The legal and organisational boundary matters as much as the geographic one. Deutsche Bank’s annual report identifies OOO Deutsche Bank TechCentre, the Russian technology service company, separately from OOO Deutsche Bank, the Moscow banking subsidiary that provided corporate banking services to local subsidiaries of international companies. As of December 2022, the bank still described the technology unit and the ongoing reassignment of its work. It also reaffirmed that no data or code were maintained in the Russian technology centre. That statement directly bears on where material was maintained. It leaves remote access, the use of data hosted elsewhere and subsequent Berlin permissions as separate questions. Likewise, the bank’s public materials distinguish the Berlin Technology Centre from the Corporate Bank’s EMEA Centre of Excellence in Berlin, which the bank says supports more than 25,000 clients in over 30 countries across trade finance, securities services, cash management and operations. Those client and country figures describe the Centre of Excellence’s published remit. They cannot be assigned to sDDA, the technology centre as a whole, or a cohort of relocated staff. A source that identifies a Berlin office, a source that identifies a banking service and a source that identifies a technology team answer different questions even when all three records name the same city. Annual Report 2022, “Russian Operations,” p. 91 — Deutsche Bank · Technology Centre Berlin — Deutsche Bank Careers · Corporate Bank EMEA Centre of Excellence — Deutsche Bank Careers. db.com
| Date | Public record | What it establishes for this investigation | What remains open |
|---|---|---|---|
| 31 January 2022 | Approximately 1,500 employees at the Russian technology centre, about 5% of the group’s internal and external technology workforce. | The scale of the source operation and the definition of the workforce denominator. | Headcount by city, citizenship, transfers accepted and completed, and later application assignments. Registration Document Supplement — Deutsche Bank. investor-relations.db.com |
| 7 June 2022 | Berlin technology centre announced for application development and technology integration, primarily for the Corporate Bank and Investment Bank. | A formal Berlin remit broad enough to include corporate banking technology. | A named sDDA team, a production-support mandate or a transfer roster. Berlin Technology Centre Announcement — Deutsche Bank. db.com |
| 30 June and 30 September 2022 | Transfer of resources to Berlin recorded. Committed relocation costs accrued. The September report identifies local hiring and task reassignment to other technology centres. | The move was underway, and the group used several routes to maintain technology capacity. | The scale of the Berlin move and the assignments of individual transferees. June Interim Report · September Earnings Report. sec.gov |
| November 2022 | ECB Banking Supervision described the Saint Petersburg operation as intragroup outsourcing and documented the move of staff to Berlin for service continuity. | An official source outside the bank confirms the Saint Petersburg–Berlin link and explains its operational purpose. | A precise Moscow-to-Berlin count, the employing entity of each transferee and any sDDA assignment. DNB Banking Seminar Interview — ECB Banking Supervision. bankingsupervision.europa.eu |
| 2025–2026 archive dates | Berlin postings attributed to the bank identify sDDA Data engineering, application ownership, production release and DevOps functions. | A specific operational link between Berlin recruitment and the named platform family. | Whether the vacancies were filled, by whom, or whether any role holder came from the 2022 transfer. Archive removal dates establish neither hiring nor the start of a role. Senior Engineer, sDDA Data · Application Owner / Release Manager, sDDA Data · Senior DevOps Engineer, sDDA Data. Built In |
What the Berlin recruitment evidence adds
The archived postings support a more precise conclusion than the opening assessment. One Berlin lead developer posting explicitly identifies back-end engineering in sDDA and situates it within Cash Management. A separate application owner and release manager posting describes responsibility for production releases and technology compliance for a critical Cash Management application stack. A third posting describes an sDDA infrastructure role working with production support and responsible for monitoring and operating production assets. Another, for an sDDA Data engineer, describes a data platform consolidating inputs from more than 50 systems, with both end-of-day and near-real-time processing. That figure is the scope described in a vacancy. It does not establish the precise live footprint of the application, the number of connected systems on a given date or the access rights of the vacancy’s eventual holder. These are archived third-party copies of recruitment notices attributed to Deutsche Bank. Their strength lies in the consistency of the named function and location across distinct advertised roles, and in the bank’s own independent description of sDDA. Their limit is equally important: an advertised production responsibility establishes neither a completed hire nor the result of a permission check on a particular person. The record supports “Berlin recruited for sDDA, including production-facing roles.” It does not support “the 2022 transferees held those roles” or “members of that cohort read live transactions.” Lead Java/Kotlin Developer, sDDA · IT Application Owner / Release Manager, sDDA Data · Senior Software Engineer, Infrastructure/sDDA · Senior Engineer, sDDA Data. Built In
Chapter 2 — What sDDA Does and When Back-End Staff Could See Transactions
The bank’s own architecture describes an account core and a separate payment layer
In its July 2020 description of the Australian branch build-out, Deutsche Bank spells out sDDA as strategic Demand Deposit Account and identifies it as the core component holding accounts and positions, with an account-opening process. The same description identifies a separate payment engine, a payment data store, and a billing platform that consumes data from both the account core and the payment data store. The Australian example matters because it establishes a real distinction inside the bank’s published architecture. Someone assigned to the account core could work with account and position functions without holding access to the payment engine or the full payment message. The reverse inference also fails. A role can sit outside the payment engine and still have visibility into sensitive account data, production-derived information or a related support record if its permissions allow it. The 2020 publication does not enumerate the fields each component exposes, identify a single present-day implementation across all markets, or provide Berlin’s permissions. Deutsche Bank’s separate corporate product documentation shows how much detail can exist in the wider environment: transaction-level credit and debit notifications, real-time balance information, and ISO 20022 statements with transaction references and extended remittance information. Those products establish that such fields exist in Deutsche Bank’s corporate banking services. An application inventory and a dated access review would establish whether any of those fields were available to a particular sDDA role. Tomorrow’s Technology Today, Australian Branch Build-out — Deutsche Bank, July 2020 · Corporate API Connectivity — Deutsche Bank · ISO Changes on Account Information Messages — Deutsche Bank. Deutsche Bank
Deutsche Bank’s published account and payment components
Australian branch example, July 2020. The two components below had distinct functions.
sDDA · Account core
Holds accounts and positions and supports account opening.
Payment engine and payment data store
The engine processes high- and low-value payments. The data store provides payment data for uses including anti-money-laundering and billing processes.
Documented billing inputs: sDDA data and payment data store data.
sBilling · Billing platform
Consumes data from both sources in the bank’s published example.
The published architecture leaves Berlin staffing and staff permissions unverified.
What “they don’t see the transactions” would have to mean
The expression can refer to several different factual claims. It could mean that the engineers did not initiate, approve or release payments, which concerns authority to act on transactions. It could mean that they lacked routine visibility of complete payment messages, while limited fields remained available to authorised support roles. It could mean no individual-level customer information could be read anywhere within their role, including during an authorised incident or in a production-derived support case. Or it could mean that a review found no recorded use of whatever permissions existed during a defined interval. The distinction matters because a bank can give an engineer permission to deploy an approved release or inspect the health of a service while excluding the ability to read customer data. A bank can also give a designated support engineer temporary, read-only access to a limited set of identifiable records to diagnose a specific incident, with authorisation and monitoring appropriate to the risk. Neither deployment authority nor involvement in a support call settles which arrangement applied. The strongest reading of the denial requires evidence of every relevant permission path for a named cohort, including temporary access and access to records presented through support, reporting or other approved interfaces. It also requires a clear definition of transaction. A complete payment instruction, a posted debit or credit, a booking reference, a balance and an aggregate processing count are different objects. Commission Delegated Regulation (EU) 2024/1774, Arts. 12, 15–17 and 21 · Corporate API Connectivity — Deutsche Bank. eur-lex.europa.eu
| Meaning of “see the transactions” | What would count as visibility | Consequence for the bank’s explanation |
|---|---|---|
| See an original payment message | Read an individual instruction, including the fields available in that message, such as parties, amount and remittance reference. | An engineer can work on sDDA while the payment layer’s data permissions exclude that engineer. |
| See an identifiable booked transaction | View an individual debit or credit and link it to a specific account or customer. A full payment message is unnecessary for this form of visibility. | A role can lack access to the payment engine and still fall within this definition of seeing transactions. |
| See account or position information | View an identifiable account, balance or position without a list of individual movements. | This is sensitive banking information. A narrow denial limited to individual payment transactions could remain accurate. |
| See masked or aggregated data | View service metrics, synthetic records or data with identifying fields removed. Assess whether supplementary information can re-identify a person or account. | Aggregates and synthetic records support the narrow claim. Reversible pseudonymisation requires a separate assessment. |
| See a production-derived support record | Read a historical transaction extract or a case record containing identifiable fields, where an approved support role permits it. | A statement limited to access to the live platform can be accurate even when the role has encountered identifiable records outside that platform. |
| Approve or release a payment | Exercise authority to approve, release or otherwise act on a payment instruction. | This concerns control of payments. Read-only transaction visibility can exist independently. |
Sources for the distinctions in the matrix are Deutsche Bank’s Australian architecture description and Corporate API documentation, as well as the EU technical standard on access control and segregation of duties, Art. 21 and the GDPR definition of pseudonymisation, Art. 4(5). The matrix describes verification criteria. Berlin’s actual configuration remains outside the public record reviewed. Deutsche Bank
Deutsche Bank’s published procedures and the rules that applied in 2022 and 2026
Deutsche Bank’s public Code of Conduct establishes a need-to-know rule for sharing confidential information, including internally. Its 2025 Annual Report describes an information security management system with role responsibilities, identity and access management, data classification, prevention of unauthorised data disclosure, and incident response. These are relevant bank-specific disclosures. They establish the existence of group-level expectations and controls against which the explanation can be tested. The public documents do not disclose the sDDA role catalogue, the employing entity and role membership of the transferred cohort, the approval chain for exceptional access or the specific logs examined by the security firm. For 2022, the applicable historical analysis starts with German banking organisational requirements and the then-current supervisory framework. Section 25a KWG addresses proper business organisation and risk management. The 2021 MaRisk, AT 7.2, addressed testing, approval and separation of production and test environments. BaFin’s 2021 BAIT, sections 6 and 7, addressed need-to-know and least-privilege entitlement design, recertification, monitoring of privileged activity, application development and test documentation. A group policy or supervisory requirement establishes what a bank should design and operate. An entitlement record or control test establishes whether it did so for a specific user, application and period. The 2022 transfer should therefore be examined under the framework in force when relevant permissions were granted, changed or removed. Deutsche Bank Group Code of Conduct, “Protecting and Handling Confidential Information” · Deutsche Bank Annual Report 2025, “Information Security” · Section 25a KWG — German Federal Law Portal · MaRisk, 16 August 2021, AT 7.2 — Deutsche Bundesbank · BAIT, 16 August 2021, Sections 6–7 — BaFin. db.com
For the current position, DORA has applied since 17 January 2025. Article 9(4)(c) requires policies limiting physical and logical access to information and ICT assets to what legitimate and approved functions require. Article 21 of Delegated Regulation (EU) 2024/1774 makes that operational through need-to-know, need-to-use, least privilege, segregation of duties and individual accountability. It expressly contemplates privileged, emergency and administrator access on a need-to-use or ad hoc basis, requires withdrawal of unnecessary access without undue delay and sets access-right update intervals of at least once a year generally and every six months for ICT systems supporting critical or important functions. The term “critical” in a vacancy is not enough to establish formal DORA classification. The same delegated regulation addresses segregation of production and non-production environments and allows defined testing exceptions, subject to conditions, including justification, limited duration and approval. Article 12 requires an event-logging policy with a risk-based retention period and level of detail aligned with its purpose. It does not establish that every business-data read necessarily appears in a single log, or that a 2026 review can reconstruct every relevant event since 2022. EU law permits restricted, justified access by technical personnel when the work requires it. The question for Berlin is whether any members of the defined cohort held or exercised such access and, if so, within what limits. DORA, Arts. 9 and 64 — EUR-Lex · Delegated Regulation (EU) 2024/1774, Arts. 8, 12, 16 and 21 — EUR-Lex · BAIT, December 2024 version, scope and DORA transition — BaFin. EUR-Lex
Confidentiality, personal data and the legal threshold for a breach
Where transaction data identify a natural person, viewing them is itself processing under GDPR Article 4(2). A corporate payment can contain personal data about a signatory, employee, individual beneficiary or sole trader even when the account holder is a company. Articles 5 and 25 require purpose limitation, data minimisation and appropriate safeguards by design and default. Articles 29 and 32 regulate processing under the controller’s or processor’s authority and require safeguards appropriate to risk. An employee’s authorised consultation for a necessary, properly governed purpose can therefore be lawful. Unnecessary or excessive permissions can present a control or data-protection problem even where there is no evidence that they were exercised. Unauthorised access or disclosure involving personal data can be a personal-data breach under Article 4(12). Article 33 generally requires supervisory notification without undue delay and, where feasible, within 72 hours of awareness, unless the breach is unlikely to present a risk to individuals’ rights and freedoms. A DORA major-incident classification is a separate assessment under its own rules. The bank’s statement says it informed the relevant authorities as a precaution. That statement supplies neither a formal breach determination nor the scope of the security firm’s work. GDPR, Arts. 4, 5, 25, 29, 32 and 33 — EUR-Lex · DORA, Arts. 17–19 — EUR-Lex · Public Statement of 17 November 2026 — Deutsche Bank. eur-lex.europa.eu
The cross-border analysis also requires the employing entity, the capacity in which the person acted and the recipient of any data made available. Under the European Data Protection Board’s guidance, remote access from a third country by an employee acting as part of the same EU controller can fall outside the definition of a Chapter V transfer, while remaining subject to GDPR security and accountability requirements. Making the same data available to a distinct controller or processor in that third country can constitute a transfer, including between entities in the same corporate group. This distinction is directly relevant to the period before relocation, to any support work that stayed in Russia, and to the legal form under which work continued after relocation. It is also why location, nationality and prior employment cannot answer the data-transfer question. The records reviewed do not establish that the Russian technology company received live account or payment data. They also do not establish which legal entity employed every engineer or whether the applicable role ever involved remote access before the move. Guidelines 05/2021 on Article 3 and GDPR Chapter V, paras. 20–21 and 31, and Example 8 — European Data Protection Board. edpb.europa.eu
The records that would verify or qualify the bank’s answer
The bank could resolve the issue with a dated written attestation from the application owner and the relevant control function, supported by historical entitlement evidence and a summary of the review scope. The attestation should identify the cohort by role and period without naming individuals, and define which of the account core, related data platforms and support processes it covers. It should answer separately whether the cohort had standing read access, whether anyone could receive temporary or emergency access, whether identifiable production-derived records were visible through approved support or testing processes, and whether the logs show those capabilities were used. For the last question, the relevant checks are what the logs capture, how far back they reach, whether controlled exceptions are included, and whether the event shows data retrieval or merely the opening of a session. A complete negative entitlement review would substantiate the bank’s strongest claim. A documented temporary read entitlement would qualify it even if nobody exercised that entitlement. An evidenced read could be consistent with a properly approved support case. An unauthorised read or disclosure would require its own legal and incident assessment. Delegated Regulation (EU) 2024/1774, Arts. 12, 20 and 21 — EUR-Lex · Public Statement of 17 November 2026 — Deutsche Bank. eur-lex.europa.eu
What would verify the Berlin transaction-access claim?
| Question | Bank record | What it establishes |
|---|---|---|
| Who worked on sDDA? | Dated application ownership, role and cohort attestation. | The assignment, relevant entities and time window. |
| Who could read identifiable data? | Historical role entitlements and temporary or emergency approvals, mapped to data categories. | Effective read capability and its limits. |
| Could staff see records outside the live platform? | Controls for production-derived test data and approved support records. | Whether identifiable information was available in those workflows. |
| Did access occur? | Audit events and a statement of log scope, coverage and retention. | Recorded use within the documented review period. |
| Was an incident identified? | Forensic scope and findings, together with the applicable incident determination. | The event tested, the result and the authority for that determination. |
EU technical standard on logging and access control · Deutsche Bank’s public statement
The precise question for Deutsche Bank
Can Deutsche Bank confirm in writing whether any employee transferred from its Russian technology operations to Berlin and assigned to sDDA or sDDA Data ever held standing, temporary or emergency permission to view identifiable production account entries or payment-transaction data, including in approved support workflows or production-derived test records? Please specify the dates, applications and data categories covered. If the bank’s answer concerns actual use rather than permissions, did the testing announced on 17 November 2026 cover this cohort and these systems, and what was its historical review period?
The answer can be assessed against a clear standard. “They did back-end work” is supported at the level of the advertised Berlin roles. “They had no authority to execute payments” is a separate proposition. “They could never see identifiable transactions” remains unverified. Deutsche Bank’s published architecture makes the narrow explanation technically plausible, because the account core and payment layer had distinct functions. Its published policies and applicable law also allow appropriately restricted and justified access in defined circumstances. The unanswered factual question is therefore whether the specific people, in the specific roles, at the relevant time had that access. The public record presently supports neither a categorical assurance of zero visibility nor an allegation that the transferred staff viewed live transactions. Deutsche Bank’s Published Architecture · Deutsche Bank’s Public Statement · EU Access-Control Standard, Art. 21. Deutsche Bank
Pillar II — Deutsche Bank, Russian Sanctions and the Limits of Cross-Border Supervision
Assessment date: 18 November 2026
Three findings matter for publication. First, U.S. and UK authorities documented serious control failures in defined historical cases, and the Federal Reserve imposed a further penalty in 2023 after finding insufficient progress in U.S. sanctions and anti-money-laundering remediation. Second, Deutsche Bank retained assets exposed to Russian enforcement after announcing its wind-down. In the RusChemAlliance case, Russian courts awarded €238.126 million in guarantee principal, and the bank subsequently reported €244 million, including interest, enforced against assets maintained in Russia. Third, the bank’s reported precautionary contact with authorities in November 2026 is evidence of notification as described by the bank. The public statement supplies no supervisory ruling on the Berlin team, no published DORA incident classification and no formal data-breach determination. The enforcement history justifies scrutiny of the bank’s controls. The Berlin question still requires evidence about the particular system, personnel and period. FCA Final Notice · Federal Reserve 2023 Consent Order · Russian Cassation Judgment, А56-60809/2023 · Deutsche Bank Global Supplement, 5 November 2026 · Deutsche Bank Statement, 17 November 2026. fca.org.uk
Chapter 3 — Mirror Trading, Referral Hiring and the Record of Remediation
What the UK and New York authorities established
The FCA’s final notice is valuable because it shows where responsibility for cross-border controls broke down. Deutsche Bank’s Moscow front office could arrange trades for connected customers, with one side involving the purchase of Russian securities for roubles and the corresponding side involving the sale of the same securities for dollars, booked through Deutsche Bank in London. The FCA identified more than 2,400 matched pairs between April 2012 and October 2014, transferring more than US$6 billion out of Russia through the UK. It also identified more than 3,400 suspicious one-sided trades representing US$3.8 billion. The roughly US$10 billion headline estimate depends on the FCA’s inference that most or all of those trades formed part of further mirror transactions. That distinction matters for publication because the matched cases and the inferred cases carry different evidentiary weight. The authorities identified weaknesses in client due diligence, country and customer risk assessment, ownership of controls over remotely booked trading, and monitoring. The FCA also stated that it had found no evidence that Deutsche Bank’s senior management or UK employees knew of or participated in the suspicious trading. It recorded that Deutsche Bank notified it in early 2015 and cooperated with the investigation. NYDFS reached its own findings under New York law concerning overlapping conduct across Moscow, London and New York, imposed US$425 million and required independent monitoring. The cross-border lesson is specific. When execution, booking, clearing and compliance review sit in different places, the bank must be able to show who owns the control and whether the responsible function receives enough information to exercise it. That is also the right standard for evaluating a distributed technology function, even though the transactions and personnel in the mirror-trading case are historically distinct from the Berlin matter. FCA Final Notice, §§1.1–1.2, 2.2–2.18 and 4.16–4.43 · NYDFS Consent Order, 30 January 2017. fca.org.uk
| FCA measure | Figure | How to read it |
|---|---|---|
| Matched mirror trades | More than 2,400 pairs, representing more than US$6bn | Transactions the FCA identified through matched sides. |
| Suspicious one-sided trades | More than 3,400 trades, representing US$3.8bn | Further suspicious activity. The missing side was not identified. |
| Estimated funds transferred | Approximately US$10bn | The FCA’s estimate assumes most or all of the one-sided trades belonged to additional mirror transactions. The NYDFS figure covers overlapping activity. |
| Final UK penalty | £163,076,224 | £9,076,224 disgorgement plus a £154m penal element. |
| UK penalty before early-settlement discount | £229,076,224 | £9,076,224 disgorgement plus £220m penal element. The 30% discount applied to the penal element. |
FCA Final Notice, §§1.1–1.2 and 2.4–2.11. fca.org.uk
Referral hiring and financial-crime remediation were different proceedings
The SEC’s 2019 referral-hiring order concerned how employees were recruited at the request of foreign officials and how those decisions were recorded and controlled. The Russia-related conduct identified by the SEC dated from 2009 to 2012. Its order recounts how the relative of a Russian deputy finance minister was placed in London and how Deutsche Bank subsequently received a request for proposals for a €2 billion Eurobond signed by the official. The €2 billion is the proposed bond issuance. The order uses it to explain the business context surrounding the hiring decision. The SEC anonymised the individuals in that account and found books-and-records and internal-accounting-controls violations. Deutsche Bank settled without admitting or denying those findings, agreeing to US$10,785,900 in disgorgement, US$2,392,950 in prejudgment interest and a US$3 million civil penalty, totalling US$16,178,850 across the order’s Russia and Asia-Pacific scope. The 2021 DOJ deferred prosecution agreement involved different conduct, including business-development-consultant payments and precious-metals trading fraud. DOJ identified US$79,561,206 as the FCPA criminal penalty, US$43,329,622 in a related SEC resolution, and US$7,530,218 for the commodities matter. A US$5.625 million component of the commodities penalty was credited against a prior CFTC penalty for substantially the same conduct. That credit matters if figures are aggregated. The Russia referral-hiring order cannot identify a 2022 Berlin transferee, and the later DOJ resolution cannot establish the operating permissions of a corporate banking technology team. SEC Administrative Order, Exchange Act Release No. 86740 · SEC Summary of the 2019 Proceeding · DOJ Deferred Prosecution Resolution, 8 January 2021. www.sec.gov
The Federal Reserve’s orders provide the strongest documentary basis for questioning a broad assurance that all historical weaknesses had been resolved. The 2015 Federal Reserve sanctions order and coordinated NYDFS action imposed US$258 million in total, split between US$58 million for the Federal Reserve and US$200 million for NYDFS. That action concerned earlier U.S. sanctions conduct involving other jurisdictions. In 2017, the Federal Reserve announced a separate US$41 million penalty for anti-money-laundering deficiencies in the bank’s U.S. operations. In 2023, it imposed US$186 million and found insufficient progress under the earlier sanctions and AML orders. Its consent order identified work still required in compliance oversight, customer due diligence, transaction data, transaction monitoring and filtering, suspicious activity reporting, and arrangements for independent review. On 20 August 2026, the Federal Reserve announced that the order dated 20 April 2017 had terminated on 13 August 2026. The scope of that notice is precise. It establishes the termination of the identified 2017 order. The notice supplies no basis for a conclusion about the status of the separate 2023 order or any assessment of Berlin’s technology controls. Conversely, the 2023 findings concern the U.S. operations and the obligations specified in that order. They do not establish that the same deficiencies existed in sDDA. Federal Reserve 2015 Sanctions Action · NYDFS 2015 Allocation of the Joint Penalty · Federal Reserve 2017 AML Action · Federal Reserve 2023 Consent Order · Federal Reserve Termination Notice, August 2026. federalreserve.gov
Enforcement and remediation record
| Action | Amount or status | Scope | Source |
|---|---|---|---|
| 2015 U.S. sanctions | US$258m combined | US$58m Federal Reserve and US$200m NYDFS. | NYDFS announcement |
| 2017 UK mirror trading | £163,076,224 | Disgorgement and penal element for AML control failings. | FCA final notice |
| 2017 New York mirror trading | US$425m | NYDFS penalty and independent monitor. | NYDFS order |
| 2023 U.S. remediation | US$186m | Federal Reserve action over insufficient progress under earlier U.S. orders. | 2023 consent order |
| 2026 termination | 13 August 2026 | The notice identifies the Federal Reserve order dated 20 April 2017. | Termination notice |
Chapter 4 — Russia Sanctions, the Moscow Entity and RusChemAlliance
What the Moscow register and the sanctions instruments establish
At 00:00 Moscow time on 18 November 2026, the Bank of Russia register listed OOO Deutsche Bank as active, with registration number 3328 and OGRN 1027739369041. The register establishes the status of the Russian banking entity at that time. Deutsche Bank’s March 2022 commitment to wind down its remaining business while assisting non-Russian multinational clients with their local wind-downs was an announcement about its business activity. A banking entity can remain active in the register while it manages legacy positions, litigation and residual obligations. The register does not disclose turnover, new customers, current systems, transaction volumes or links to Berlin. The appropriate inquiry is therefore specific to the alleged activity and date. Regulation (EU) No 269/2014 requires the freezing of funds and economic resources belonging to, owned, held or controlled by persons and entities listed in Annex I, and restricts making funds or economic resources available to or for their benefit. Regulation (EU) No 833/2014 imposes separate sectoral and transaction restrictions, including an Article 11 rule concerning specified claims affected by sanctions. The Council extended the sectoral measures to 31 July 2027. In October 2026 it separately announced a listings package targeting almost 1,600 persons and entities connected to Russia’s military-industrial complex. Those updates reinforce the need to check the operative rules and lists on the date of the transaction. For a client-booking or payment allegation, the record must establish the entity, beneficial ownership or control, transaction and booking dates, jurisdictional nexus, type of restriction, and any applicable authorisation. A present-day designation or an active Russian banking registration cannot reconstruct those facts. Bank of Russia Credit Institutions Register · Deutsche Bank Russia Business Statement, 11 March 2022 · Regulation 269/2014, Consolidated Text · Regulation 833/2014, Consolidated Text · Council Sectoral Renewal, June 2026 · Council Listings Package, October 2026. Банк России
One guarantee generated three distinct legal proceedings
RusChemAlliance brought its claim against Deutsche Bank AG under an advance-payment guarantee issued on 24 September 2021, related to Linde’s obligation to repay an unearned advance. The Russian cassation judgment reproduces the guarantee ceiling of €238,126,196.10 and records RusChemAlliance’s demand of 27 April 2023. Deutsche Bank says it refused that demand on EU sanctions grounds. The guarantee was governed by English law and provided for Paris arbitration. In September 2023 the English Court of Appeal granted an anti-suit injunction to restrain the Russian proceedings, publishing fuller reasons in October. The injunction concerned the arbitration agreement and the proper forum. The Russian commercial court subsequently awarded the principal on 29 May 2024, and the Russian appellate and cassation records document the ensuing challenges. The Russian Supreme Court refused to refer the merits complaint to its Economic Disputes Chamber in May 2025. In a separate development, the bank reports that a Russian court granted an anti-suit order against Deutsche Bank in October 2024, backed by a threatened €240 million penalty for non-compliance. The bank says it complied in November. The English order protected the agreed dispute forum, the Russian merits judgment awarded money, and the Russian anti-suit order constrained the bank’s conduct in proceedings abroad. The legal conflict became financially consequential because assets within Russia were available for local enforcement. The UK Supreme Court’s judgment in UniCredit v RusChemAlliance discusses the parallel cases and the English injunctions, while deciding UniCredit’s own appeal. Deutsche Bank AG v RusChemAlliance LLC [2023] EWCA Civ 1144 — UK National Archives · North-West District Cassation Judgment, А56-60809/2023, Russian Court Text · Russian Supreme Court Order, 15 May 2025, Russian Court Text · UniCredit v RusChemAlliance [2024] UKSC 30 · Deutsche Bank Global Supplement, 5 November 2026, “RusChemAlliance Litigation”. The National Archives
What was awarded, enforced and recognised in the accounts
The Russian judgment described below concerns a claim against the German parent. The Russian bank and technology companies were joined as third parties, and RusChemAlliance also sought execution against the parent’s 100% holdings in those two entities. A later Russian appellate decision expressly recites that the court granted the monetary claim and rejected the requests to execute against those shareholdings. The bank’s November 2026 disclosure describes interim freezing measures and reports that RusChemAlliance ultimately enforced €244 million including interest against assets Deutsche Bank maintained in Russia. Read together, the records establish an award against the parent, a claim over specified shareholdings that was rejected, and a reported recovery against assets in Russia. The disclosure also shows how the accounting changed. Deutsche Bank initially recognised a €260 million provision with a corresponding reimbursement asset under an indemnification agreement. After the enforcement, subsequent developments led it to derecognise that asset. Deutsche Bank says it still considers the indemnity claim valid and is pursuing it in court. The outstanding question is whether the bank will recover under the indemnity and on what terms. The bank’s separate disclosure of a provision, an enforced amount and a derecognised reimbursement asset does not support adding the three figures as if each were a new payment. An April 2026 Russian appeal concerned a separate costs order. It left the RUB 2,137,666.30 award in that costs proceeding unchanged. North-West District Cassation Judgment, А56-60809/2023 · Thirteenth Commercial Court of Appeal, September 2025 Costs Decision · Thirteenth Commercial Court of Appeal, April 2026 Costs Decision · Deutsche Bank Global Supplement, November 2026. sudact.ru
| Amount | What the record identifies | Legal or accounting status |
|---|---|---|
| €238,126,196.10 | Guarantee ceiling and principal awarded against Deutsche Bank AG | Russian court award. |
| €479,514.39 | Late-payment amount accrued to 27 June 2023 | The court also ordered continued accrual from 28 June 2023, calculated at 1.5% per annum on principal until performance. |
| €244 million including interest | Amount enforced in November 2024, according to Deutsche Bank | Reported enforcement against assets maintained in Russia. |
| €240 million | Penalty threatened under the Russian anti-suit order if the bank failed to comply | Contingent sanction described in the bank’s disclosure. The bank reports that it complied. |
| €260 million | Initial provision recognised in 2023 | Accounting provision initially offset by a reimbursement asset, subsequently derecognised. |
| RUB 2,137,666.30 | Costs awarded in a separate 2026 ruling and left unchanged on appeal | Procedural cost award in roubles. |
Russian Cassation Judgment, Award and Accrual Terms · Russian Appellate Costs Decision, April 2026 · Deutsche Bank Global Supplement, November 2026. sudact.ru
RusChemAlliance guarantee and enforcement
Common origin · The 2021 guarantee was governed by English law and provided for Paris arbitration. A 2023 payment demand led to proceedings in England and Russia.
English Court of Appeal
Granted an injunction restraining Russian proceedings on the basis of the arbitration agreement.
English judgmentRussian proceedings
The commercial court awarded €238,126,196.10 in principal. A separate Russian anti-suit order carried a threatened €240 million non-compliance penalty.
Russian cassation judgmentEnforcement and recovery
The bank reports €244 million enforced in Russia and says it continues to pursue recovery under its indemnity.
November 2026 bank disclosureChapter 5 — Digital Resilience, Supervisory Jurisdiction and Data Protection
A governance weakness, a reportable ICT incident and a personal-data breach have different thresholds
The first supervisory question is whether the management of the shared banking service met applicable controls for classification, responsibility, access and oversight. A weakness in any of those controls can justify supervisory scrutiny even if the bank finds no specific incident. The second question is whether an ICT-related incident occurred and met the criteria for a major incident under DORA. Delegated Regulation 2024/1772 requires impact on critical services as defined in Article 6 and either the specific threshold in Article 9(5)(b) or at least two of the other materiality thresholds. The specific threshold concerns successful, malicious and unauthorised access of the kind described in the provision that may result in data loss. Other thresholds address such matters as affected clients or transactions, duration and downtime, geographic spread, data loss, reputational impact and economic impact. These rules can capture a serious confidentiality event even if payment services keep operating. They cannot classify an incident from a job title, press report or general control concern alone. The third question is whether a breach of security caused unauthorised access, disclosure, loss, alteration or destruction of personal data. That triggers a separate GDPR assessment, including risk to individuals and the applicable notification threshold. The same event may trigger both regimes. In the November case, the bank reported the results of testing and said it contacted the relevant authorities as a precaution. The public record therefore establishes the bank’s account of its actions, while the formal classification, notification route and supervisory conclusions remain unresolved. DORA, Arts. 17–19 — EUR-Lex · Delegated Regulation 2024/1772, Arts. 5–9 · GDPR, Arts. 4(12), 33 and 34 · Deutsche Bank Statement, 17 November 2026. eur-lex.europa.eu
| Reporting track | Clock or threshold | Relevance to the case |
|---|---|---|
| DORA initial report | As early as possible and within 4 hours of major classification, normally no later than 24 hours after awareness of the incident. If classified as major after those 24 hours, Article 5(2) requires reporting within 4 hours of classification. | Requires the incident facts and the classification timestamp. A statement about precautionary contact does not give either timestamp. |
| DORA intermediate report | Within 72 hours of submission of the initial notification. An updated intermediate report follows without undue delay and in any case when regular activities resume. | The clock begins with submission of the initial notification. Credit institutions cannot use the weekend or bank-holiday extension for initial and intermediate reports. |
| DORA final report | Within one month of the intermediate report, or of the latest updated intermediate report where applicable. | The prescribed final report addresses root cause, remediation and impact. |
| GDPR supervisory notification | Without undue delay and, where feasible, within 72 hours of awareness of the personal-data breach, unless risk to individuals is unlikely. | The GDPR clock and legal test are distinct from DORA’s intermediate reporting clock. |
| GDPR communication to individuals | Without undue delay where the breach is likely to result in high risk, subject to Article 34’s exceptions. | Direct client or staff contact can serve several purposes. The public statement gives no Article 34 determination. |
Delegated Regulation (EU) 2025/301, Art. 5 — Official Journal Text via IVASS · GDPR, Arts. 33–34 — EUR-Lex. ivass.it
Germany and the EU — who receives a report and who supervises the group
Germany is the primary location for establishing the facts because the bank’s parent and the documented Berlin technology function are there. Deutsche Bank AG is identified as a significant institution under ECB banking supervision. The Bundesbank’s DORA guidance identifies BaFin as the German reporting authority and explains that it forwards reports to the Bundesbank and other relevant authorities. At EU level, DORA Article 19 sets out how the national competent authority transmits a major-incident report from a significant credit institution to the ECB. This gives the group’s prudential supervisor a route to the relevant information without making every notice to a national authority a published ECB finding. Data protection follows a separate competence analysis under GDPR Articles 55 and 56. The responsible controller, its main establishment for the relevant processing and any cross-border effects matter. The bank’s statement identifies a data protection authority by function, without publicly naming the authority or giving the basis and scope of the notification. For a Berlin-specific assessment, the relevant supervisory record would identify the regulated legal entity, the affected service, the application owner, the operational impact, the data involved and the jurisdictions affected. None of those fields can be inferred from the word “back end.” ECB List of Supervised Entities, September 2026 Cut-off · Deutsche Bundesbank DORA Reporting Guidance · DORA, Art. 19 · GDPR, Arts. 55–56. www.bankingsupervision.europa.eu
Italy and France — a shared platform can create local obligations when services are affected
In Italy, Banca d’Italia directs entities within its remit to submit major ICT incident reports through INFOSTAT and explains that the relevant requirements also cover operational or security incidents involving payments for entities in scope. The Italian Garante publishes the separate GDPR breach-notification rules. The domestic data show why the distinction between an event and a report is material. In a 5 November 2026 speech, Banca d’Italia reported 101 events and 137 reports in 2025 and 68 events and 92 reports in the first nine months of 2026. The periods differ and a single event can generate multiple reports. These are Italian supervisory figures, with no attribution to this Deutsche Bank matter. In France, the ACPR’s DORA guidance states that financial entities within its remit and significant credit institutions report relevant incidents to the ACPR on an individual basis. The CNIL provides the personal-data breach notification route where it is competent. A shared German platform could have legal relevance in Italy or France if it supported a locally regulated service that was affected, or if the affected data processing fell within the respective data protection authority’s competence. The practical evidence would be a mapping from the application to the local service and entity, followed by evidence of actual service or data impact. Merely showing that a corporate client does business in Italy or France does not establish that an incident occurred there or identify a notification duty for a particular local entity. Banca d’Italia DORA Incident Reporting · Banca d’Italia Supervisory Speech, 5 November 2026 · Garante Data Breach Guidance · ACPR DORA FAQ · CNIL Breach Notification. bancaditalia.it
United Kingdom — the applicable November 2026 rules and the March 2027 change
For a UK-regulated operation, the starting point as of the assessment date is the UK’s existing notification framework. The FCA’s operational-incident guidance directs firms to consider Principle 11, which requires open and cooperative dealings with the regulator and disclosure of matters the FCA would reasonably expect notice of, alongside the applicable Handbook requirements. A dual-regulated bank must separately assess its obligations to the PRA. A qualifying personal-data breach engages the ICO route under UK GDPR. Separately, the FCA’s PS26/2 and the PRA’s PS7/26 set out the new UK operational incident and third-party reporting regimes, due to apply from 18 March 2027. That effective date prevents a retrospective application of the new regime to November 2026. London’s role in the historical remote-booking case is firmly documented. UK competence in the present matter would depend on a current UK entity, regulated service or data-processing connection and the facts that trigger the relevant duty. In particular, an English-law guarantee and an English court’s anti-suit injunction establish a legal nexus for the RusChemAlliance dispute. They do not establish the UK supervisory nexus for a different question about a Berlin-hosted technology function. FCA Current Operational-Incident Guidance · FCA PS26/2 · PRA PS7/26 · ICO Personal Data Breach Guidance. FCA
Which authority may need to be notified?
Identify the event, the affected legal entity and service, the data involved, and the time of awareness. One event can engage more than one route.
EU financial supervision
Apply DORA’s major-incident criteria. Report through the competent national channel when required. For significant institutions, Article 19 provides for transmission to the ECB.
DORA incident criteriaEU data protection
Determine whether personal data were breached and assess risk to individuals. Identify the competent authority and any duty to inform affected people.
GDPR Articles 33–34United Kingdom
Apply the relevant UK rules to the affected UK entity or service. The new FCA and PRA reporting regimes take effect on 18 March 2027.
Current FCA reporting guidancePillar II judgment. The documentary record establishes historical enforcement failures, a later U.S. remediation action and material exposure to Russian judicial enforcement. It also shows exactly where the evidence stops. An active Moscow bank registration, a Russian guarantee award, a U.S. AML order and a precautionary data-protection notification each concern a different legal proposition. The evidence that could change the Berlin assessment is a case-specific regulatory finding or a documented incident review identifying the affected legal entity, service, system, time interval and data categories, with a clear statement of whether the review addressed standing permissions, temporary access, recorded use or unauthorised disclosure. The public record reviewed through 18 November 2026 supplies no such finding. Federal Reserve 2023 Consent Order · Deutsche Bank Global Supplement, November 2026 · Deutsche Bank Statement, 17 November 2026. federalreserve.gov
Pillar III — Deutsche Bank’s Assurances, the Epstein and Trump Records, and the Evidence Still Missing in Berlin
Assessment date: 18 November 2026
The earlier chapters left out material evidence. The detailed Inside Deutsche Bank investigation reports US$581.9 million across approximately 3,000 Epstein-linked transactions covered by 21 suspicious activity reports. Senate Finance Committee investigative staff separately documented more than US$250 million in retrospectively flagged wires from the records they reviewed. The Trump material involves documented lending, a congressional subpoena dispute, a reported 2017 disclosure of financial records and later internal reviews of transfers involving Trump-owned companies. The Russia material includes a reported 2020 strategy review, internal compliance warnings and questions about referral hiring and access to sovereign-bond information. Each strand bears on the credibility of Deutsche Bank’s governance assurances. The Berlin finding remains narrower: the public record establishes back-end work associated with sDDA in Berlin, but it has yet to establish whether the transferred engineers could read identifiable live transactions. The bank’s 17 November statement did not publish a finding on those staff permissions. Detailed Epstein Investigation — Himal Southasian · Looking the Other Way, Section X — Senate Finance Committee investigative staff · Inside Deutsche Bank — Investigative Journalism Bureau · Deutsche Bank’s Public Statement, 17 November 2026. finance.senate.gov
Chapter 6 — What the Leaked Records Add and What the Bank’s Tests Can Establish
Epstein — what the approximately US$600 million figure actually measures
The most precisely defined figure in the detailed November reporting is US$581.9 million. Reporters attribute it to an internal document from Deutsche Bank’s U.S. Financial Crimes Intelligence Unit that summarised 21 suspicious activity reports, covering approximately 3,000 transactions from October 2013 through May 2019 involving Jeffrey Epstein or his companies. The Financial Times headline rounds this to US$582 million. The Investigative Journalism Bureau’s overview uses more than US$600 million for transactions involving Epstein and his network. The published accounts do not supply a reconciliation between those figures or a transaction-level schedule that would identify any difference in scope, overlapping filings, or the treatment of incoming and outgoing movements. For publication, the defensible formulation is “about US$600 million, including a precisely reported US$581.9 million across approximately 3,000 transactions in a review attributed to the bank’s U.S. financial-crime unit.” The figure measures the reported value of suspicious activity within that review. It does not establish the amount of criminal proceeds, the bank’s revenue, the balance of Epstein’s accounts, or the amount tied to any specific offence. The independent point of comparison is the Senate staff review of records examined in camera, which documented more than US$250 million in retrospectively flagged wires. One 2019 filing cited in that report covered 1,140 wires worth US$147 million. The US$147 million example sits within the Senate staff discussion. The Senate figure and the consortium’s figure cannot be added or reconciled from the published material. Detailed Epstein Investigation — Himal Southasian · US$582 Million Headline — Financial Times · Consortium Overview — Investigative Journalism Bureau · Senate Finance Committee Staff Report, Section X, pp. 43–44. ft.com
The 2020 New York State Department of Financial Services consent order supplies the strongest official evidence about how the relationship was handled. The regulator records that Deutsche Bank took Epstein on in August 2013, after an onboarding memorandum had set out his earlier plea and sentence, and decided to end the relationship in December 2018. The bank told the consortium that the transfer of assets out of the bank continued in the following months. The NYDFS order describes an early commercial projection of US$100–300 million in flows and US$2–4 million in possible annual revenue. Those figures were forecasts in a relationship manager’s email. They did not measure realised earnings. In 2015, the bank’s reputational-risk committee allowed the relationship to continue subject to conditions. NYDFS found that the conditions were not communicated to all relevant relationship staff or to the transaction-monitoring team in their intended form. A March 2017 exchange cited by the regulator illustrates the failure. A monitoring employee treated payments as unremarkable because similar activity was normal for this client, even though the client’s history was the reason enhanced scrutiny mattered. NYDFS also records more than 120 wires totalling US$2.65 million from several accounts to Butterfly Trust beneficiaries. Senate staff separately discussed more than US$800,000 in cash withdrawals over four years and more than US$7 million in private settlements with potential victims. These examples explain the concerns about monitoring and escalation. They cannot be added to the consortium aggregate without knowing which transactions it already includes. NYDFS Consent Order, §§17–23, 31 and 38–46 · Senate Finance Committee Staff Report, Section X · Deutsche Bank’s Response to the Epstein Reporting, published by The News Minute. dfs.ny.gov
The US$150 million NYDFS penalty was imposed under one consent order covering Epstein and separate correspondent-banking relationships involving Danske Bank Estonia and FBME. Quoting it as a US$150 million Epstein-only fine misstates the order’s reach. The US$75 million federal class settlement approved in Doe v. Deutsche Bank was a separate civil resolution. The legal question raised by the retrospective reporting is distinct from either amount. Under 31 CFR §1020.320, the ordinary filing clock runs from initial detection of facts that may provide a basis for filing, generally 30 calendar days, with up to 60 days in the specified circumstance where no suspect was identified at initial detection. The transaction date and the date on which the bank first detected a reportable basis can differ. A filing-timeliness assessment therefore needs the alerts, escalation dates, case determinations and filing records. The regulation also protects suspicious activity reports and information revealing their existence. A publishable request to the bank should seek a lawful, aggregate explanation of the reported totals and reporting chronology, supported where possible by public findings from the competent authorities. NYDFS Consent Order, §§114–117 · Doe v. Deutsche Bank, Settlement Approval, S.D.N.Y. · 31 CFR §1020.320 — GovInfo. dfs.ny.gov
Jeffrey Epstein · What each dollar figure measures
| Amount | Scope | Source |
|---|---|---|
| US$581.9m | Approximately 3,000 transactions across 21 reports, October 2013–May 2019, according to the consortium’s account of an internal bank review. | Detailed consortium reporting |
| More than US$600m | Broader wording in the consortium overview. No published reconciliation to US$581.9m was identified. | Consortium overview |
| More than US$250m | Retrospectively flagged wires identified by Senate Finance investigative staff in the material they examined. | Senate staff report, section X |
| US$147m | 1,140 wires cited in one 2019 filing within the Senate staff discussion. | Senate staff report, pp. 43–44 |
| US$150m | State regulatory penalty covering Epstein, Danske Bank Estonia and FBME. | NYDFS consent order |
| US$75m | Separate court-approved civil class settlement. | Federal court judgment |
Donald Trump — lending, subpoenas, disclosure of records and payment reviews
The strongest primary evidence of Deutsche Bank’s relationship with Donald Trump is the New York civil record. The 2024 trial decision describes Deutsche Bank Private Wealth Management’s handling of credit facilities connected with Doral, Trump Chicago and the Old Post Office in Washington, including the importance the bank assigned to Donald Trump’s personal guarantee and financial statements. It also records that the bank’s credit staff made their own adjustments to collateral values and that different Deutsche Bank divisions could propose different terms. The US$168,040,168 figure was a trial-level disgorgement component based on estimated interest-rate savings associated with four loans considered in the case, including the 40 Wall Street loan. The figure does not represent Deutsche Bank’s loan principal, a bank payment to Trump, or an enforcement penalty against Deutsche Bank. In August 2025, the Appellate Division vacated the disgorgement awards in their entirety and otherwise affirmed the judgment subject to the modifications in its order. A separate primary record, Trump v. Mazars USA, LLP, confirms that the House Financial Services Committee subpoenaed Deutsche Bank in April 2019 for categories of financial information concerning Trump, family members and affiliated entities. In July 2020, the U.S. Supreme Court vacated and remanded the lower-court judgments for reconsideration under a separation-of-powers analysis. That ruling concerned Congress’s compulsory process and cannot establish what any underlying transaction showed. New York Trial Decision, February 2024 · New York Appellate Division, People v. Trump, August 2025 · U.S. Supreme Court, Trump v. Mazars USA, LLP, July 2020. nycourts.gov
The leaked records add two separate lines of inquiry. First, ZDF reports that on 30 March 2017 a Deutsche Bank employee sent an external accountant financial material covering 1,586 accounts, including three attributed to Trump. The Investigative Journalism Bureau describes an externally sent link and the bank’s internal deliberations over notification. ZDF reports that the recipient initially told the bank he had deleted the material, that executives questioned whether deletion could be established, and that the documents it reviewed indicated notice to U.S. authorities but no notice to Trump. Those are attributed findings about a 2017 incident. The underlying transmission record, actual access scope, notification file and any regulatory disposition remain material to a legal conclusion. Second, consortium reporters describe a separate May 2020 internal financial-crime memorandum discussing transactions involving Trump-owned companies. They matched one entry to a US$141,261.82 transfer dated 28 April 2015 from Faberlex to THC Baku Services LLC. The same reporting describes an April 2019 internal draft concerning the bank’s knowledge of Trump–Russia links in relation to his business with the bank. A draft’s wording and an internal memo prepared a year later can show how the questions asked and the information available changed. The public record does not establish that the draft was sent in that form, that the Baku transfer was unlawful, or that Trump personally knew its origin. The proper comparison is between the original transaction record, the May 2020 memorandum, any actual communication to authorities, and the bank’s resulting disposition. ZDF, Report on the 2017 Disclosure · Investigative Journalism Bureau, Inside Deutsche Bank · Himal Southasian, Trump-Owned Companies and the 2020 Memorandum · Le Monde, The Azerbaijan Transaction. zdfheute.de
Russian oligarch exposure — the chronology and the misreading of the “Kremlin list”
The dates 2015, 2017, 2019 and 2020 matter because they define what the bank could have known at different points and what action it could then have taken. The November reporting draws on internal correspondence, compliance material and governance records. The public extracts available for this assessment do not authenticate a complete set of particular letters for each of those four years. The official 2017 enforcement record independently establishes the findings concerning earlier Russia-linked mirror trading. It cannot authenticate any specific oligarch memorandum from the same year. For 2019, Le Monde reports that internal risk-committee discussions questioned the profitability of the Russian business given the control weaknesses and expressed concern about Russian state-owned clients. For 2020, the reporting describes compliance concerns around plans to expand parts of the Russian business and a November 2020 Russia Strategy Review, reported by Meduza as 172 pages. It says the review identified 17 of 160 major Russian clients appearing in the U.S. Treasury’s 2018 Section 241 report and attributed 47% of revenue from the reviewed Russian client portfolio to those 17 clients in 2020. Seventeen out of 160 is 10.6% of the reviewed client population. That figure says nothing by itself about the share of assets, the share of payments, or who was legally sanctioned. Treasury’s Office of Foreign Assets Control expressly states that the Section 241 report did not impose sanctions. Each of the 17 would need to be checked against a separate operative designation as of the relevant date, with the ownership and control facts for any client entity. FCA Final Notice · Le Monde, Russian Client and Governance Reporting · Meduza, Reported Russia Strategy Review Figures · OFAC FAQ 552, Legal Status of the Section 241 Report. www.fca.org.uk
The same distinction applies to the allegation that Deutsche Bank concentrated wealthy Russian relationships in Switzerland and Luxembourg, making some information harder for U.S. investigators to obtain. Meduza, drawing on the consortium reporting, says the shift began in 2018, describes later requests by U.S. authorities and reports that the bank cited local banking secrecy in limiting disclosure of certain client data. The bank’s reported explanation was that the hubs formed part of its wealth-management operating model and that clients underwent the required checks. Both accounts can be tested against dated booking records, beneficial-ownership files, the requests made by the authorities, the bank’s actual replies, and the specific legal restrictions it invoked. The scale and purpose of any movement remain distinct questions. In another strand, Le Monde reports that an internal investigation called Project Wingman calculated at least €1.7 billion in flows through a network of nearly 800 companies, some of which reporters linked to people or entities associated with Oleg Deripaska. The investigation also describes a separate €1.1 billion correspondent-banking transfer considered in a report involving Fren Global, in which Deutsche Bank reportedly questioned who ultimately benefited and received differing explanations from Russian banks. These are reported findings about different populations, entities and banking functions. Neither amount belongs in a total for assets held by the 160 reviewed clients. OFAC’s separate April 2018 designation of Deripaska is official. It can be matched to an identified transaction only once the beneficiary, ownership or control, date and jurisdictional nexus are established. Meduza, Swiss and Luxembourg Booking Allegations and Bank Response · Le Monde, Project Wingman · Le Monde, Fren Global and Russian Correspondent Banking · U.S. Treasury, April 2018 Designations. Meduza
Alexey Storchak — the hiring inquiry, the bond allegation and the SEC order
Alexey Storchak’s 2010 hiring is a material part of the Russia story. In 2018, Bloomberg reported from former Deutsche Bank executive Nizar Al-Bassam’s London High Court claim that an internal inquiry called Project Dastan examined the hires of relatives of Russian officials, including Storchak. It identified his father, Sergei Storchak, as a deputy finance minister, and described Alexey’s prior work at Credit Suisse and in the Russian finance ministry’s foreign-assets division. Al-Bassam disputed wrongdoing in the hiring. Bloomberg later reported that the employment dispute settled. The November 2026 Financial Times reporting identifies Storchak in the bank’s Russia business and describes compliance monitors’ concerns about political exposure. A source familiar with the inquiry told the newspaper that the bank had closely examined his hiring and found no violation of its internal anti-bribery, conflicts or hiring rules. Separately, Le Monde reported from leaked records that a banker hired in June 2010, described as the son of a senior Russian ministry official, communicated Deutsche Bank’s selection for a €2 billion Eurobond issue before the information became public. The article describes a September communication preceding public announcement by about a month. Its account does not name the banker. The public material reviewed therefore supports reporting Storchak’s named hiring inquiry and the early-access allegation in parallel. A signed finding or authenticated contemporaneous record linking him to the specific communication would be needed to state that he obtained non-public information improperly. Bloomberg, Project Dastan and the Storchak Hiring · Bloomberg, Settlement of the Al-Bassam Employment Dispute · Financial Times, How Deutsche Bank Lost Its Bet on Putin’s Russia · Le Monde, Russian Hiring and the Eurobond Chronology. news.bloomberglaw.com
The SEC record makes identification especially important. The 22 August 2019 order establishes a corporate accounting-controls and books-and-records case covering Russia and Asia-Pacific. The US$16,178,850 overall resolution included US$3 million in civil penalty plus disgorgement and interest. The order’s Russian sovereign Eurobond example concerns Referral Hire D, expressly described as the daughter of a deputy finance minister. The order records that the bank received a request for proposals signed by her father about ten days after her approved transfer to London. It separately describes Referral Hire E as the son of a senior executive at a Russian state-owned enterprise. These are anonymised examples with distinct personal descriptions and chronologies. The SEC example involving a request for proposals also describes a different event from the selection announcement in the leaked account. The shared €2 billion denomination cannot identify the individuals or prove that the two reports describe the same step in the same mandate. The SEC order supports a firm conclusion about the corporate referral-hiring controls. It supplies no named misconduct finding against Storchak. SEC Administrative Order, Release No. 86740, §§32–40 · SEC Summary of the Settlement and Monetary Components. www.sec.gov
The November forensic statement and the reported German inquiry
Deutsche Bank said on 17 November that, following testing with a security firm, it had found no indication that its current IT environment had been compromised or that account information, credentials or payment data had been accessed. It acknowledged that the material described in the reporting included confidential information, said it had contacted relevant authorities as a precaution and stated that its analysis was continuing. On 18 November, Reuters reported that Alexander Roßnagel, the Hessian data protection commissioner, told Handelsblatt he was investigating whether Deutsche Bank had implemented technical and organisational measures appropriate to the risk. This is a material update to the earlier assessment. There is a publicly attributed account of a regulator’s inquiry, while a published determination on the merits or a finding about Berlin’s sDDA permissions remains unavailable. The bank’s statement and the reported inquiry can coexist because they address different propositions. The bank describes what its testing detected. The commissioner’s reported inquiry concerns the adequacy of safeguards. There is also a difference between a present environment compromise, an older disclosure of documents, the extraction of internal files and authorised staff access to live records. A meaningful forensic response needs to state which of those possibilities was tested, over what dates, in which systems, against which categories of data and with what audit coverage. The published statement provides none of those details for the Berlin cohort. The bank’s reported €7 billion invested in controls from 2019 to 2025 establishes what management says it spent. The performance of a particular permission control requires its own dated evidence. Deutsche Bank Statement, 17 November 2026 · Reuters, Hessian Commissioner’s Reported Inquiry, 18 November 2026 · GDPR, Art. 32 — Security of Processing. www.db.com
Chapter 7 — Evidence Thresholds, Institutional Decisions and Final Net Assessment
What would justify changing the published conclusion
The next decision is how strongly to phrase the Berlin finding. “The transferred personnel could never see identifiable transactions” is a claim about effective capability, including temporary permissions and any support process in which individual transaction records could be displayed. A reliable bank answer would define the cohort, employing entity, application and period and then distinguish full payment messages, individually identifiable booked debits or credits, account positions, non-identifying operational data and identifiable records used in support or approved testing. It would cover ordinary, temporary and emergency permissions. If the bank instead answers that it found no recorded reads, the strength of that assurance depends on the historical audit window, the completeness of the records and whether the retained events can distinguish a session from the actual retrieval of data. A bank can answer these questions through a signed aggregate attestation, a redacted independent assurance summary, or a competent authority’s published finding. Customer names, raw transaction data and sensitive implementation details are unnecessary to substantiate the conclusion publicly. EU technical standards provide the benchmarks for access control, segregation of duties and logging. They cannot substitute for evidence that the bank applied those controls to the personnel and system in question. Commission Delegated Regulation (EU) 2024/1774, Arts. 12, 20 and 21 · Deutsche Bank Annual Report 2025, “Information Security” · Deutsche Bank Public Statement, 17 November 2026. eur-lex.europa.eu
| Evidence obtained | What it would establish | Publication consequence |
|---|---|---|
| Dated cohort and application attestation | Which transferred personnel, described by role or aggregate group, were assigned to sDDA or sDDA Data and when. | Strengthens or narrows the staffing allegation. Visibility remains a separate finding. |
| Complete effective-permissions review | Whether any cohort member had standing, temporary or emergency read capability for the specified data categories and period. | An evidenced absence supports the bank’s claim for that scope. A verified entitlement requires the claim to be qualified, even if no use is documented. |
| A attributable audit record of retrieval or display | That a user viewed or retrieved the specified category of data during the recorded interval, where the evidence can support that inference. | Establishes a particular instance of use. Its authorisation and purpose still need to be checked. |
| Evidence of access or disclosure beyond authorisation | A specific control event with a defined actor or recipient, data category, time and authorisation boundary. | Supports assessment under the applicable incident and data-protection rules. |
| Forensic report with a narrower or incomplete scope | The systems, users and dates the review can address, including any retention gaps. | Preserves the bank’s negative result within the documented scope. Historical or team-specific questions outside that scope remain open. |
| Published regulator decision | What the competent authority actually investigated and concluded. | Supersedes inference only on the matters the decision expressly resolves. |
EU Technical Standards on Logging and Access Control · GDPR, Arts. 4(12), 32 and 33. eur-lex.europa.eu
Berlin transaction access · Four questions, four records
1. Assignment
Confirm the transferred cohort, named application, role and dates through a dated application-owner attestation.
3. Recorded use
Check whether retained audit events establish retrieval or display, and disclose any gaps in coverage.
4. Incident determination
Establish whether access or disclosure exceeded authorisation. Apply the relevant supervisory and privacy tests to the event.
EU technical standards on access and logging · Deutsche Bank’s public forensic statement
Institutional decisions and the questions to put on the record
| Decision | Who can act and what to request | What the result would change |
|---|---|---|
| Obtain a publishable bank answer | Ask the application owner and bank control function to attest to the sDDA cohort, dates, ordinary and exceptional read permissions, and the scope of the November testing. Seek an aggregate answer with no client identifiers. | The fastest route to distinguish a denial of permissions from a negative finding about actual use. |
| Reconcile the Epstein amounts | Ask the bank for a lawful explanation of what the US$581.9 million covers, including the transaction population, direction of flows and any overlap in the aggregate. Ask competent authorities whether they can publish a reconciliation. | Establishes whether the detailed figure and the consortium’s broader more than US$600 million wording measure different populations or reflect a discrepancy. |
| Verify Trump-related reporting independently of the credit record | Ask separately for a publishable account of the 2017 disclosure, the notification decision and the disposition of the 2020 review. Use the official court record to describe lending and procedural outcomes. | Could substantiate the historical disclosure or the bank’s handling of it without implying a finding on the Baku payment or on Trump’s knowledge. |
| Audit the Russian client and Storchak claims | Seek dated versions of the strategy and committee records, confirmation of what “17” measured, and the legal status of each relevant connected client on the transaction date. Obtain the actual bond communication and inquiry finding before assigning the reported advance information to a named individual. | Resolves the difference between a risk classification, a designation, an actual banking transaction and individual misconduct. |
| Track the Hessian inquiry on its stated terms | Seek the authority’s public description of scope and any published determination. Attribute the inquiry to the commissioner’s reported statement while that is the available source. | Could establish a finding about the adequacy of safeguards. A finding on Berlin’s team would still require an explicit match to that cohort and system. |
The central question for Deutsche Bank can be put on the record in one request:
Can Deutsche Bank confirm whether any employee transferred from its Russian technology operations to Berlin and assigned to sDDA or sDDA Data ever had standing, temporary or emergency permission to view identifiable production payment messages, individual booked debits or credits, or identifiable transaction records in approved support or testing workflows? Please identify the period and data categories covered. If the bank’s assurance is based on recorded activity, please confirm whether the tests announced on 17 November assessed this cohort and these applications, and what historical period they covered.
Final net assessment
The Epstein record establishes a serious historical failure in the implementation of the bank’s own risk conditions, with the precise US$581.9 million figure attributable to the consortium’s reporting and the more than US$250 million figure attributable to Senate investigators’ review. The Trump record establishes a documented lending relationship and a subpoena dispute, alongside separately reported evidence of a historical data disclosure and transactions examined in an internal review. The Russian record supports scrutiny of how Deutsche Bank booked and monitored high-risk relationships, balanced commercial incentives against compliance warnings and handled politically exposed referral hiring. The 17 of 160 figure concerns the Section 241 list as reported in the strategy review. The SEC order establishes corporate violations and does not name Storchak. These findings justify asking for more than a general assurance about reform or back-end work. They do not establish that the Berlin transferees saw live transactions. Deutsche Bank’s public statement also does not establish that those employees lacked the ability to see them. The most accurate formulation is that the back-end explanation is plausible, the cohort’s effective permissions remain unverified, and the bank has publicly described a negative testing result without publishing a Berlin- and sDDA-specific scope. A dated permissions review and a separately defined audit of actual use would settle the two questions. NYDFS Consent Order · Senate Finance Committee Staff Report · SEC Referral-Hiring Order · Deutsche Bank Public Statement. dfs.ny.gov


